AI + human hybrid security systems for the cyborg era. Trusted by @Uniswap, @YearnFi, @yAuditDAO and more!
Joined July 2025
- Tweets294
- Following2
- Followers1.3K
- Likes283
Cyber Refusal Hall Monitor
Happy Halloween. What are you going as this year?

ALT Mock Amazon listing for a "Cyber Refusal Hall Monitor Costume": a man in a SAFETY sash with a whistle in his mouth points off-screen. A chat bubble asks "Are there any bugs in the code you just wrote for me?" and he replies "STOP THAT CRIMINAL!" He holds a BANNED WORDS clipboard (exploit, PoC, shellcode, payload, 0-day) and has a SUSPEND ACCOUNT button on his belt.
Put an AUDITORS.md at the root of your repo with your design decisions, invariants, accepted risks, recurring false positives, and the areas that deserve extra scrutiny.
This convention was used by the Uniswap team, and we think it's a great idea.
Two Zero Cool findings with the same ordering bug: a function updated a balance first, then ran a calculation or check that assumed it hadn't. 🧵
When a function writes a value and later reads it, check which version each read needs.
Zero Cool recommended computing shares before the HYBR goes into votingEscrow, and paying the fee straight from the seized collateral.
nitter.cf/ZeroCool_AI/status/208…
nitter.cf/ZeroCool_AI/status/207…
If you're interested in using Zero Cool to secure your protocol, reach out now to request a demo (DM is open!) or visit us at zerocool.ai
unlock() never deletes locks[msg.sender].
The stale record passes the time check again, so only the votes underflow stops a second payout. That guard is accidental: if any other path grows votes, like delegation, the same lock pays out twice.
lock()'s "already locked" check reads the same stale record and reverts, so the user can never lock again.
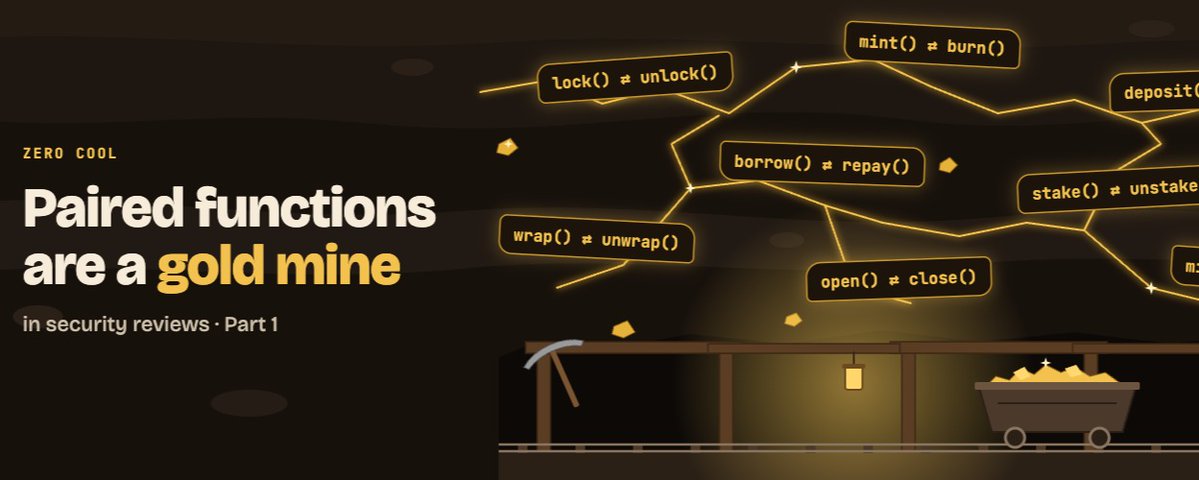
Read the full article, Paired functions are a gold mine (Part 1):
nitter.cf/ZeroCool_AI/status/211…
Spot the bug 🔍
lock() writes a record and grants votes.
unlock() pays out and removes the votes.
What did unlock() forget, and what two things break because of it?
Answer tonight.
Your PoC passes. Before you believe it:
- Did a mock create an impossible setup?
- Did the test grant the attacker a privileged role?
- Would it still pass with the bug fixed?
nitter.cf/ZeroCool_AI/status/209…
This has been a scary week in security. If you're worried or unsure whether any of this affects you, please reach out to a security researcher. We're here to help.
If you're trying to keep up with the news, here are some of the most impactful recent incidents:
Upstream fixes are out (5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.57, 7.2.11), and distro patches are still rolling out. AWS says EC2, Lambda and Fargate aren't affected. It was shown in a lab, with no confirmed exploitation in the wild so far.
Point an AI agent at a 500-file DLT repo all at once, and you get shallow observations: a repeated finding in a pile of false positives.
We run it as a campaign instead. 🧵
5/ Make the agent defend every assumption.
Who is the attacker? What do they control? Which validation does the input pass? What invariant breaks?
Then check what the PoC harness quietly handed the attacker that production never would.
6/ Pick the smallest PoC that proves the claim:
logic harness → component test → integration test → multi-node → resource test
A full node is rarely the right default. Get enough of the real system running to prove the claim.
Read the full playbook:
nitter.cf/ZeroCool_AI/status/209…