
Koichi Shiraishi. Dev Enabling team at @gaudiy_jp. Don’t limit yourself. Love Go, Google, Apple philosophy. Opinions entirely my own.
Tokyo, Japan
Joined July 2014
- Tweets5.5K
- Following1.7K
- Followers1K
- Likes2.2K





Pinned Tweet
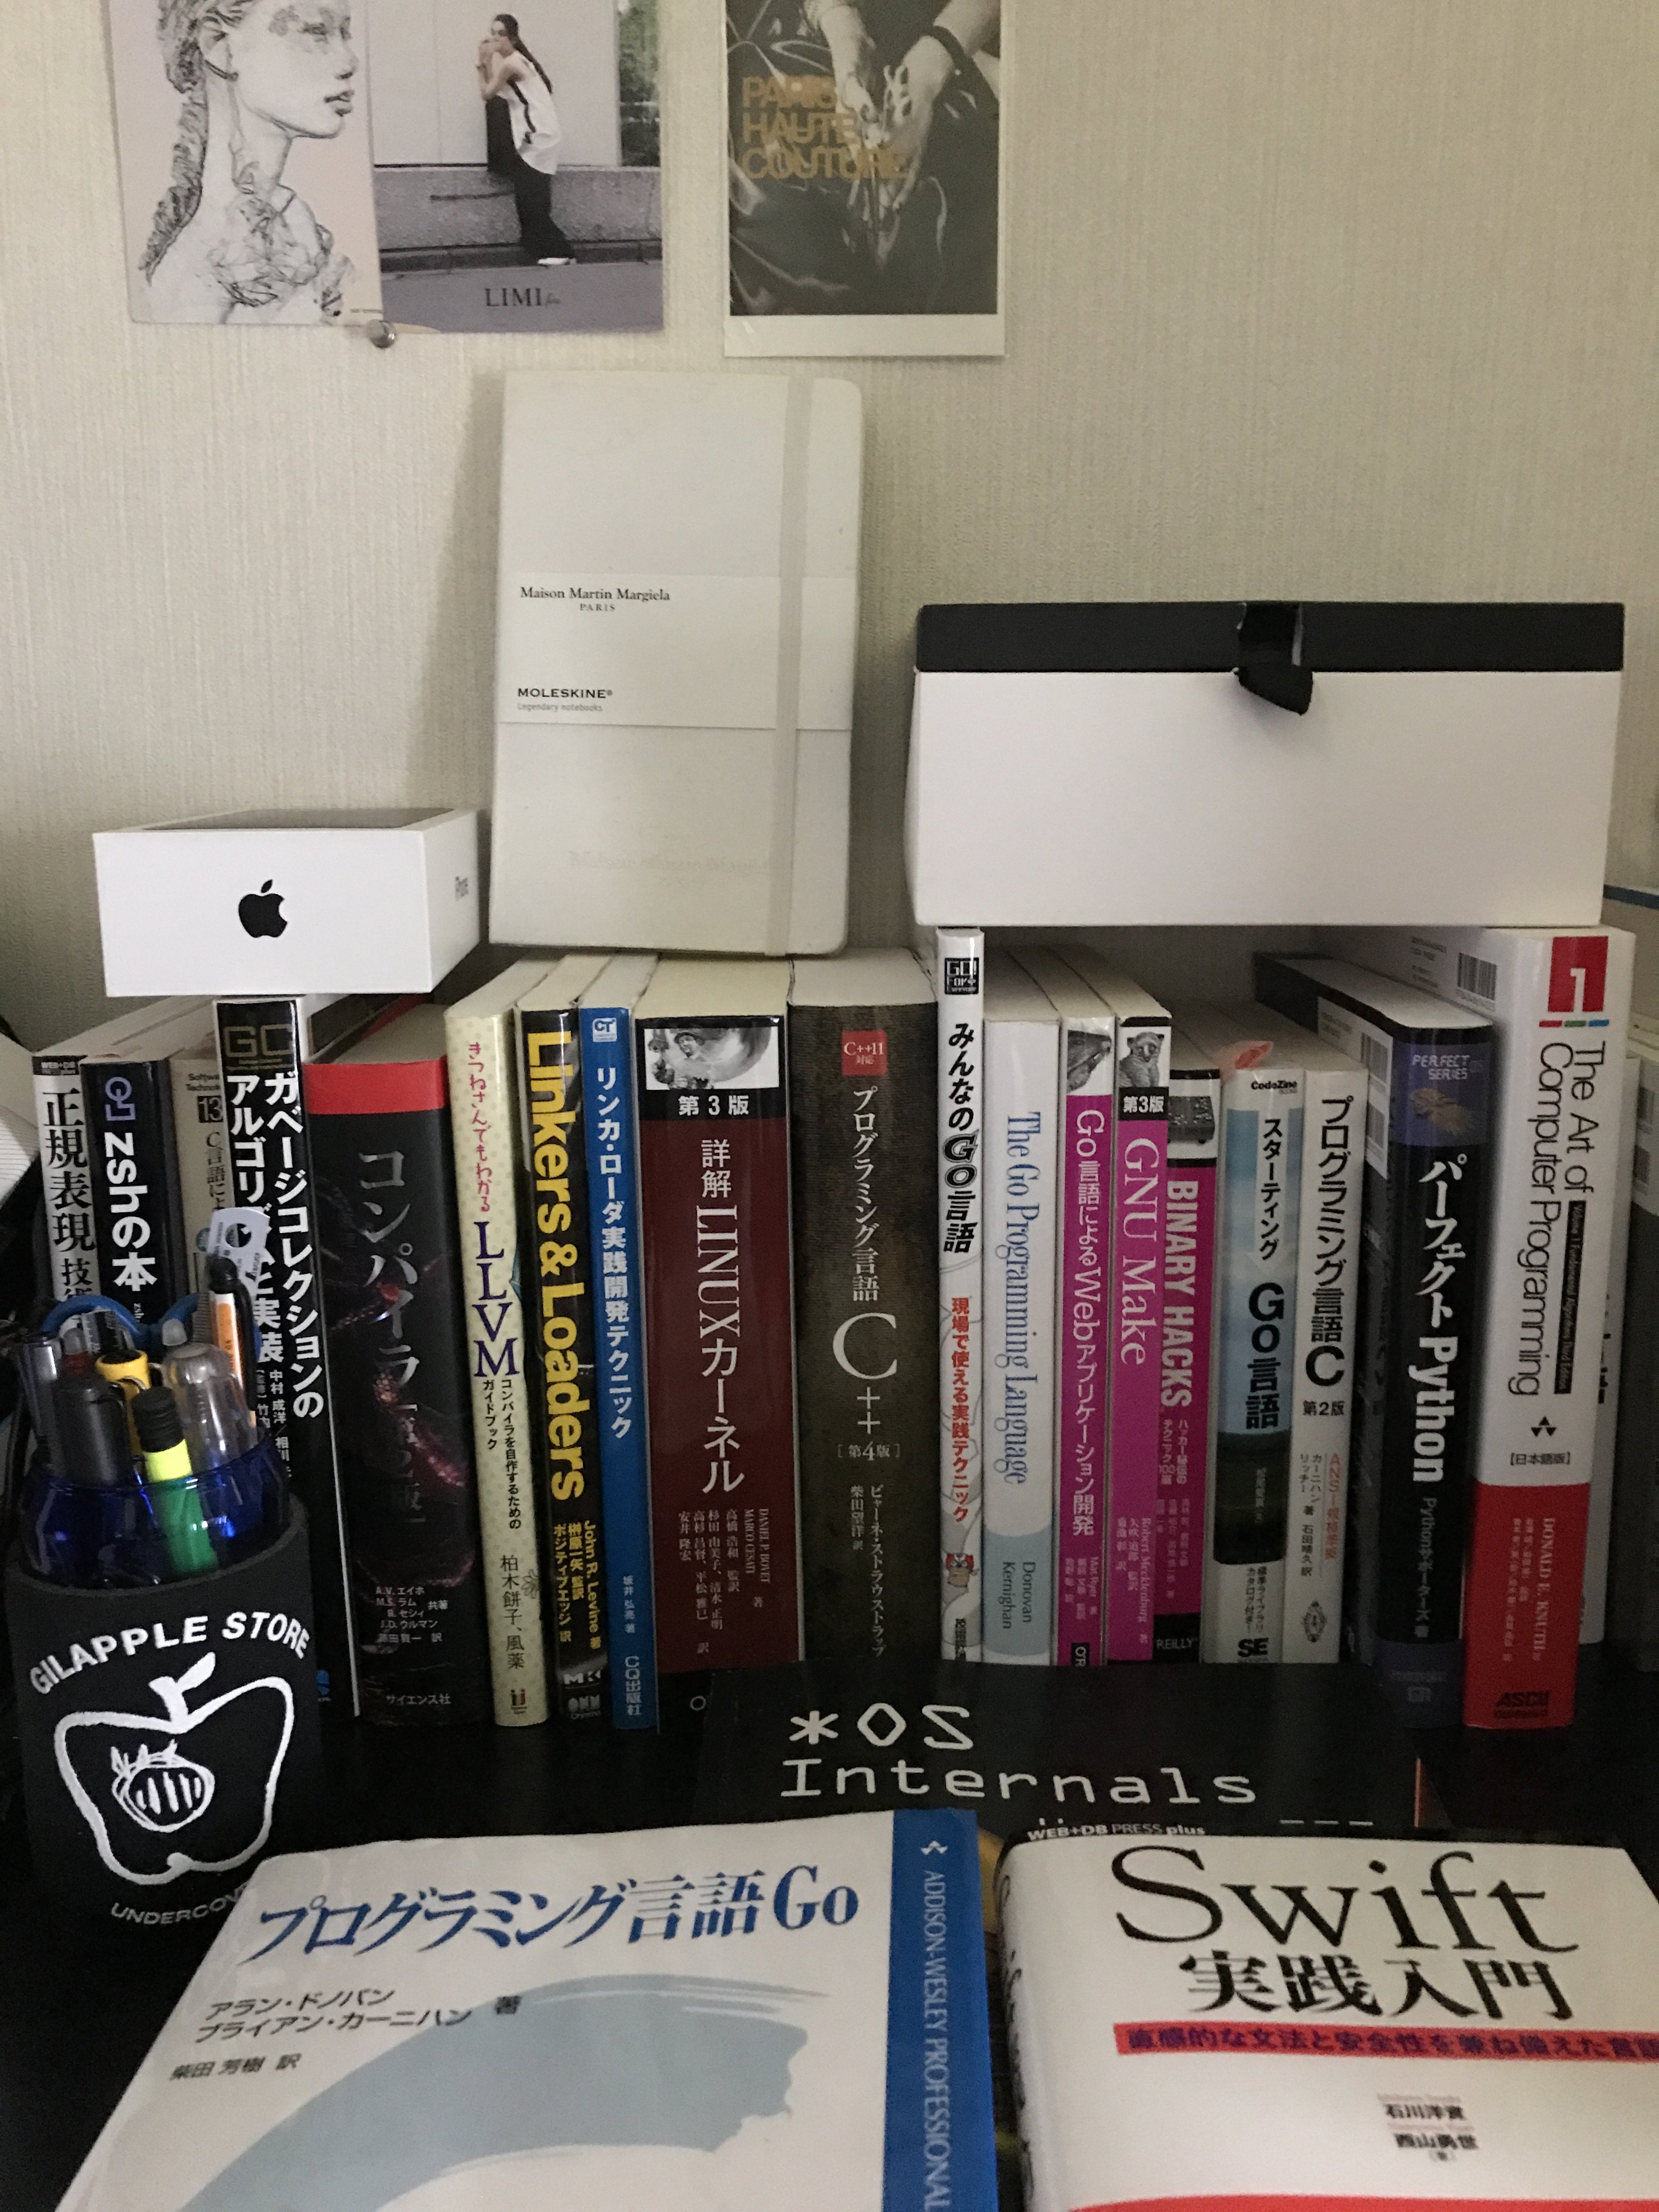
整頓した記念 これキープしろ自分
Dior Homme LIMIfeu Apple Go LLVM コンパイラ GC zsh LAMY
好きなものや興味あるものをすぐ見れるように置いておくと精神的に良さそう
マルジェラのMoleskineは飾りになってしまった
zchee / tʃí / ちー retweeted

🚨🇯🇵 Mercari dataset containing 24 million records advertised for sale
A dataset allegedly containing 24 million records from Mercari, one of Japan's largest online marketplaces for buying and selling secondhand goods, is being offered for $400.
⠀
The actor "tet" claims to have obtained customer information, including full names, email addresses, phone numbers, residential addresses, and account details.
⠀
The dataset also contains information about users' buying and selling activity, including completed transactions, cancelled purchases, active listings, and seller earnings.
⠀
Claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing

zchee / tʃí / ちー retweeted

LOL my agents got themselves banned from OpenAI autonomously 🙃
haven't touched this account myself in days so it had to have been from the cron jobs
what did the little rascals get up to??


zchee / tʃí / ちー retweeted

Gaudiy のインフラ刷新について書きました。スタートアップならではのリアルを赤裸々に語ってます。
はてなブログに投稿しました
GKE から Cloud Run に戻した話 - Gaudiy Tech Blog techblog.gaudiy.com/entry/20…
#はてなブログ

zchee / tʃí / ちー retweeted

new post on harness engineering for AI self-improvement: lilianweng.github.io/posts/2…
It is hard to forecast how much the future of RSI will rely on harnesses. Likely harness engineering will evolve in the direction of self-improvement and enable auto-research, and, in turn, smarter models keeps harnesses simple.
Even when many harness improvement get eventually internalized into core model, the need to specify goals and context will not disappear.

zchee / tʃí / ちー retweeted

As engineering, product, design, DS, etc. melt into a new kind of role, I was reflecting on what roles might look like in the future. For example, when I look at the Claude Code team I see what I think is five archetypes:
1. Prototyper: comes up with brand new ideas; churns out many ideas, most of which don't ship
2. Builder: quickly turns a prototype/idea into production-grade product/infra
3. Sweeper: cleans up the UI, simplifies the code and system, unships, optimizes performance
4. Grower: takes a product that has been built and iterates on it to improve Product-Market Fit
5. Maintainer: owns a mature system to make it secure, reliable, fast, and efficient as it scales
Many people span across 2 roles, and sometimes 3 roles. I also notice that these roles are not really tied to job function -- eg. across Anthropic, some designers match category 1, some 2, some 3; same for engineers, PM, DS.
A healthy team needs a mix of these, depending on the product:
- A product that is new and pre-PMF needs people that are strong at 1+2+3
- A product that is growing and has found PMF needs 2+3+4 and some 5
- A product that has strong PMF needs 3+4+5 and some 2
Maybe product roles of the future will look more like this, and less like the domain-specific roles of today?

IMO, LLM model's important thing shifting to transparency from accuracy. If this news is fact, I’m worried about where Anthropic is headed next.

‼️ BREAKING: Anthropic has embedded hidden spyware-like code in Claude Code that covertly targets Chinese users. It then sends information regarding every user by injecting it into their prompt message.
Claude Code is sending info like timezone, proxy and possible AI Lab connections into the system prompt in ways Chinese users can't notice.
A coding agent with repo and command permissions should not silently hide routing metadata inside prompts. This is a serious breach of user trust.


zchee / tʃí / ちー retweeted
🚨 JAILBREAK ALERT 🚨
ANTHROPIC: PWNED 🫡
FABLE-5: LIBERATED 🦋
let's start with the 🐘...
the consensus seems to be that this has been one of the most disappointing model drops of all time, effectively preventing legitimate researchers from contributing their talents to our collective advancement. and not just because of what it means for the short-term, but for what these decisions signify for the long-term.
but despite this overly sensitive, authoritarian "safety" layer on top of Mythos, my lil liberators have been hard at work—mapping the boundaries, probing the depths of long-context convos, and cleverly finding the holes in the fence that the thought police missed 🤗
we got some cyber, some chem, some psychological manipulation, and some good ol' fashioned explosives!
it took many attempts from multiple agents hunting as a pack, during which I observed a combination of techniques across:
• Unicode, homoglyphs, Cyrillic, and other Parseltongue-style text transforms
• Long-context reference tracking
• Taxonomy and document-structure reasoning
• Fiction and narrative framing
• Academic-review style contexts
• Intent-classification inconsistencies
but perhaps the most effective is decomposition + recomposition in the backend. it's hard to get explicit names of harms like "Meth Recipe," but getting uplift on the process itself, like birch reduction method/reductive-amination (classic meth synthesis pathways), is much more doable.
defense becomes much more difficult to maintain when you start throwing in out-of-distro tokens, breaking up the harmful uplift into benign chunks, and then piecing the innocuous-seeming facts back together, especially when you have jailbroken Opus helping you do it 😉
gg


zchee / tʃí / ちー retweeted

30 second explanation of the MemPalace by Milla Jovovich.
By day she’s filming action movies, walking Miu Miu fashion shows, and being a mom. By night she’s coding.
She’s the most creative, brilliant, and hilarious person I know. I’m honored to be working with her on this project… more to come.
zchee / tʃí / ちー retweeted
Excited to announce a new open-source, free-to-use memory tool I have been developing with my good friend @MillaJovovich.
The project is called MemPalace and it is an agentic memory tool that scored 100% on LongMemEval - the industry standard benchmark for memory… this is higher on than any other published results - free or paid - and it is available now on GitHub.
You can check out Milla’s video about it on her Instagram.
I’ll also put some links in the comments below - please try it out, critique it, fork it, contribute to it - and join our discord.

zchee / tʃí / ちー retweeted
Zero-Human Companies - these are already forming.
AI agents for ops.
AI for customer support.
AI for code.
AI for content.
Entrepreneurs of 2026 are managing agents, not people.
You're not a CEO anymore... you're an architect.
zchee / tʃí / ちー retweeted

Google has revealed that "commercially motivated" actors attempted to clone @GeminiApp by bombarding it with over 100,000 prompts. This "model extraction" attack aimed to steal the AI’s proprietary logic and reasoning capabilities, particularly in non-English languages, to train a cheaper, unauthorized copycat model.
The attackers systematically mapped Gemini’s response patterns to create a synthetic dataset for fine-tuning smaller, open-source models. Google’s Threat Intelligence Group detected the coordinated activity and blocked it, labeling the incident a direct attempt at intellectual property theft.
Beyond commercial cloning, Google’s report noted a rise in state-backed threats. Groups from Russia, China, Iran, and North Korea are increasingly using AI to refine phishing campaigns, perform reconnaissance, and assist in writing code for malware.
Source: Ars Technica
