

Interactive Sandbox & Threat Intelligence trusted by 16K+ SOC & MSSP teams. Triage and respond to phishing & malware faster: https://nitter.cf/t.co/DHC75KqDh1
Joined February 2017
- Tweets5.5K
- Following192
- Followers34.6K
- Likes6.7K



Pinned Tweet
🚀 𝗕𝗜𝗚 𝗡𝗘𝗪𝗦: Introducing Related Threat Context, Your New MTTR Shortcut.
SOC & MSSP teams used to manually rebuild the picture around every suspicious IOC. With this new #ANYRUN update, you can see related team analyses, historical context, and industry-related activity for every IOC and uncover related infrastructure in one connected workflow.
⚡️ 𝗜𝘁’𝘀 𝗿𝗲𝗮𝗹𝗹𝘆 𝘀𝗶𝗺𝗽𝗹𝗲: review the context around each indicator in the Sandbox, then pivot to TI Lookup in one click to uncover additional threat activity and give Tier 1 evidence to justify escalation.
See the workflow in action and try it yourself: app.any.run/tasks/390e708f-2…
🔍 Connected context brings a whole new level of speed and clarity to triage: faster decisions, fewer uncertainty-driven escalations, more focused use of Tier 2 expertise, better knowledge reuse across shifts, and stronger visibility into industry-relevant activity.
🎉 𝗧𝗵𝗲 𝘁𝗿𝗶𝗮𝗴𝗲 𝗯𝗼𝗼𝘀𝘁 𝘆𝗼𝘂’𝘃𝗲 𝗯𝗲𝗲𝗻 𝘄𝗮𝗶𝘁𝗶𝗻𝗴 𝗳𝗼𝗿 𝗶𝘀 𝗵𝗲𝗿𝗲. Explore Related Threat Context in your security workflows: any.run/cybersecurity-blog/r…

⚠️ One IOC raises a critical triage question: is this a first sighting or part of a broader campaign? Let’s see how #ANYRUN helps answer it in a #SkyW4lker investigation.
⚡️ #ANYRUN Sandbox revealed that its phishing page checks Microsoft Device Code authentication status through the PHP endpoint: /session_public.php?action=.
1️⃣ Instead of manually searching for this pattern across previous investigations, open Related analyses, #ANYRUN's major new upgrade. It immediately surfaces threat history: earlier analysis sessions sharing the same URL pattern. Review the analysis: app.any.run/tasks/064901cc-1…
2️⃣ Pivot to #ANYRUN TI Lookup in one click. Searching for this unique backend pattern uncovers additional phishing activity and expands the campaign cluster.
✅ The result is not just one suspicious indicator. Tier 1 gets evidence of related activity to support triage and escalation. Tier 2 starts with connected infrastructure and prior analysis context instead of rebuilding the campaign picture from scratch.
👨💻 Read the full SkyW4lker breakdown and see how #ANYRUN's new Related Threat Context provided a shortcut for the entire investigation: any.run/cybersecurity-blog/s…

❓ When an employee needs a new AI tool, where do they go: your approved catalog or a search engine? It is the habit that shapes your exposure.
⚡️ The strongest control is making the approved AI catalog the easiest path to the software people want.
📖 We broke down five fake AI attack patterns that reach US companies, and what SOC teams can hunt for: any.run/cybersecurity-blog/f…

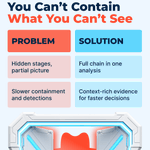
❗ US organizations cannot afford a partial picture of evolving malware: every hidden stage slows containment and weakens detections.
Here is how to reveal the full chain of a phishing link with #ANYRUN:
🔹 Interact like a real user: click through the chain and let hidden stages reveal themselves.
🔹 See inside the browser: the full page execution tree, with every redirect, iframe, and the code added after load, in one view.
🔹 Widen the view: Related Threat Context shows whether the IOCs appeared in team investigations, industry-related analyses, or #ANYRUN Threat Intelligence, with a direct path into TI Lookup.
🔹 Act on it: IOCs, IOAs, IOBs, and TTPs ready for containment, hunting, and detection engineering.
⚡️ Bring #ANYRUN to your SOC to see the full picture and make fast, confident decisions: any.run/enterprise/?utm_sour…

A single IOC can reveal activity far beyond where it was first found 🔎
🚀 See how real-time threat intelligence and sandbox analysis, enriched with Related Threat Context, help SOCs and MSSPs spot threats earlier and triage faster👇
any.run/cybersecurity-blog/c…

🚀 Signing off from #itsa2026 with plenty to take away!
Thanks to everyone who stopped by, met the team, and saw #ANYRUN in action. We already miss the conversations 🫶
Didn’t get the chance to talk? See how #ANYRUN can fit into your security workflows: any.run/enterprise/?utm_sour…


❗ The best SOC improvements begin with one honest question: where is our industry most exposed? Five teams answered it and improved their workflows — read their stories.
1️⃣ An investment bank in Brussels: any.run/cybersecurity-blog/h…
2️⃣ A German manufacturer: any.run/cybersecurity-blog/g…
3️⃣ An MSSP serving hospitals and clinics: any.run/cybersecurity-blog/h…
4️⃣ A logistics company: any.run/cybersecurity-blog/h…
5️⃣ University of Massachusetts Boston: any.run/cybersecurity-blog/u…
⚡ Industry context contributes to proactive defense. #ANYRUN gives you access to what teams in your industry are seeing: threat intelligence enriched by a community of security professionals and searchable by industry and country.
#CybersecurityAwarenessMonth

🚨 We tracked a widespread event-invite #phishing campaign targeting marketing and business teams across technology, consulting, manufacturing, and telecom between September 21 and October 26. Most active in the US ❗️
⚡️ One fake Anthropic invite was the starting point. With #ANYRUN’s new Related Threat Context, we connected anthropic.rsvpconnect-events[.]com to dozens of malicious analyses.
1️⃣ "Anthropic at AWS re:Invent 2026" email + fake Anthropic event page: app.any.run/tasks/b442f924-6…
In TI Lookup, the same infrastructure revealed a separate TikTok-for-Business lure on register.rsvpconnect-events[.]com
2️⃣ TikTok event + Google sign-in: app.any.run/tasks/2b69ab45-9…
More cases to review the phishing flows and collect #IOCs:
🔹 "GPT-6 Astra" Zoom event + Device Code: app.any.run/tasks/6592b2af-6…
🔹 “Salesforce Dreamforce 2026” + Google sign-in: app.any.run/tasks/05f89c90-2…
#ExploreWithANYRUN 1/2 🧵


⚠️ Emails arrive from the legitimate customercare@gotowebinar[.]com notification address after attackers register as event organizers. Links pass through Zoom and Google shorteners, zpr[.]io and c[.]gle. A Cloudflare “Confirm you’re not a robot” check blocks security scanners and other unwanted visitors, allowing only real victims to reach the fake event page.
❗️ The campaign steals accounts through two paths: Microsoft Device Code phishing signs the attacker’s session into M365 without password entry on the phishing page; Google lures relay a live sign-in flow through rotating .icu domains.
#IOCs:
us968web-zoom[.]us
rsvpconnect-events[.]com
/meeting_view.php?meeting=
/partials/microsoft-device-login.js
#ExploreWithANYRUN 2/2 🧵
AI in cybersecurity is everywhere. But where's the real SOC payoff?
We tested it in a real phishing attack: hidden threats exposed, a wider campaign uncovered, and less manual work between detection & response 🚀
How to turn AI into real SOC advantage👇
any.run/cybersecurity-blog/a…


🚨 #SkyW4lker puts US companies at risk: 46% of 618 related analyses came from the US.
This Microsoft 365 device-code #phishing campaign enables account access without passwords — even with MFA.
Catch the warning signs before accounts are compromised 👇
any.run/cybersecurity-blog/s…

The IOC on your screen may already have a threat history. Now, uncovering it is easier than ever with new Related Threat Context 🚀
Achieve even faster triage & enrichment with related team analyses, industry observations, and direct path to threat intel: any.run/cybersecurity-blog/r…


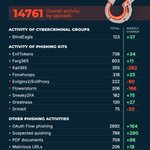
Phishing activity in the past 7 days 🐟
Track latest #phishing threats in TI Lookup: intelligence.any.run/analysi…
#TopPhishingThreats

⚠️ #ToxicPanda banking trojan hides behind fake Android updates, then abuses Accessibility services to control devices and intercept authentication data.
Discover how its staged delivery facilitates financial fraud — and how to detect it: any.run/malware-trends/toxic…

❗ How to speed up incident response in Google SecOps?
#ANYRUN’s Interactive Sandbox takes a file or URL from alert to verdict without leaving Google SecOps: fewer escalations, faster containment.
⚡️ Integrate and get verdicts in every alert: any.run/integrations/google-…

⚠️ RAT families showed contrasting activity trends last week. #Romulus climbed 32% while #AsyncRAT dropped 35%, with #Remcos and #XWorm also declining. Meanwhile, #FormBook gained nearly 40%.
📌 Trend to watch: declining activity among leading RATs doesn't mean every family is slowing down. SOC teams should assess detection gaps at the family level rather than assume lower volumes mean reduced exposure.
Monitor the malware driving today’s attacks: any.run/malware-trends/?utm_…
#Top10Malware

🚨 #Formbook is Back with Regional Lures. A localized business-order lure targets European users and manufacturing orgs, delivering Formbook through an in-memory chain and persisting as SystemUpdate_*.
👨💻 See the full attack chain and collect #IOCs in #ANYRUN Sandbox: app.any.run/tasks/29a05eb9-a…
🚀 With #ANYRUN's new Related Threat Context, analysts can explore activity beyond the original sample in one connected workflow. In this case, another document themed malicious archive used similar JS lure — a useful lead for identifying related threats.
#ExploreWithANYRUN 1/3 🧵

🔗 Execution chain: JavaScript ➡️ hidden PowerShell ➡️ AES-protected .NET payload ➡️ hollowed aspnet_compiler.exe ➡️ #Formbook in rekeywiz.exe
❗️ The loader bypasses execution policy and retries injection through a watchdog, while leaving clear detection markers: SystemUpdate_ps_*.lnk persistence, C:\Temp\ps_*.ps1, and powershell.exe spawning aspnet_compiler.exe without arguments. Suricata flagged Formbook C2 check-ins and a request to a .top domain.
#ExploreWithANYRUN 2/3 🧵
#ANYRUN TI Feeds turn IOCs into continuous monitoring by streaming fresh, validated indicators and behavior-based threat data into your security stack.
💡 #IOC:
hlushkova[.]top
58eb890b612938867237c3fa1715b8742d9b25a8fe136cd75ea659882b7b7a10
a970e997093fcd10d108354423c8fa420a6887ed97cbf7c7dbe3551faa4d9b95
1aa47ce02867f847227839b60d396ca96dac60372b0cd26b78b71a34473bb079
9683514cc99c80e7021849da4e9bd65d00c6d477f478589ea9aef522daed3c72
🔍 Additional IOCs uncovered in TI Lookup through Related Threat Context:
93248da1a4ef6df7b13ecda6c3d91d4d3a49efd4ed1034acd1217e790fc90783
477381fcad2a224fc4070d9fbcd4d5c4f8169fcf0904398bda8f29d6f9fab6a0
806d430c036e3bcb5b05b14eaf7423fdad2fcea67dae7a4beef545ffd864da52
6416f6c353c7e687190fab84c8e8802b0139fb98f44b8e6ae79099fd27884b9b
a44cad7e7d26a0f0284ceb2e9a10a964d9e7ab44ab74b22464eb2f836af3d90a
#ExploreWithANYRUN 3/3 🧵