

Hey @bytecodevm (eleven red pandas 🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼), got any spicy bytecode / VM / language implementation / JIT / music
Bagnes, Switzerland
Joined November 2010
- Tweets46.1K
- Following841
- Followers2K
- Likes39.6K





eleven red pandas retweeted

Обавештење у вези с текућим рачунима клијената Алта банке 👇
nbs.rs/sr_RS/scripts/showcon…

eleven red pandas retweeted

Using the Windows Hypervisor Platform API to execute shellcode in an isolated vCPU, bypassing process memory scanning
WHvCreatePartition → WHvSetupPartition → WHvMapGpaRange → WHvCreateVirtualProcessor → WHvSetVirtualProcessorRegisters → WHvRunVirtualProcessor

eleven red pandas retweeted

👋 ADIÓS TEAMVIEWER
RustDesk hace lo mismo.
Gratis.
Controlas cualquier ordenador como si estuvieras delante.
→ Windows, macOS, Linux, Android e iOS
→ Un ejecutable y listo
→ Cifrado de extremo a extremo
→ Puedes montar tu propio servidor

eleven red pandas retweeted

Speaking of reaching your potential
Here are 124 actionable tips on consistency, skills, discipline, the grind, the journey, the team, the mission, motivation, learning, and expertise.
PDF freely available: justinmath.com/files/advice-…


Ну штош все деньги моем ИП и личные счета в связи отзывом лицензии у банка заблокированы. Из покушать на руках 100$ Остается штурмовать несколько оставшимся банков, где с сербским внж и русским паспортом еще можно что то сделать

eleven red pandas retweeted

AWS Key Finders
- Live Domain
curl -s TARGET | grep -oP 'https?://[^"]+\.js' | xargs -I{} curl -s {} | grep -oP '\bA[KS]IA[0-9A-Z]{16}\b'
- Public Repo
git clone --depth=1 TARGET/repo.git /tmp/r && grep -rP '\bA[KS]IA[0-9A-Z]{16}\b' /tmp/r
Long-term + temp keys, easy critical.

eleven red pandas retweeted

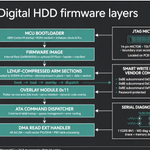
Bypassing Secure Boot using Fault Injection by
@Riscure
【PDF】raelize.com/upload/research/…

eleven red pandas retweeted

You’ve seen REA tear apps apart down to the binary.
Someone built the defense.
BLA : hardens your release so AI reverse-engineering tools chase fake keys, bait APIs, and dead-end logic then run out of budget.
- Poison the artifacts.
- Exhaust the analyzer.
- Force hallucination.
- Verified on 14 benchmarks.
Your runtime stays 100% the same.
- github.com/qybaihe/bla
AI that tries to reverse your app just
wastes its tokens and fails


eleven red pandas retweeted

Jim Manico, one of the best-known names in app security, just released free threat-modeling skills for AI coding agents.
Grim Prompter points Claude Code or Codex at your repo and walks it through a real security review: your architecture, where untrusted data crosses into trusted code, the threats, what's already protecting you, and what to fix. Every finding is traced to your actual code, so you can check it.
It has 36 architecture workflows and 29 analysis prompts.
git clone github.com/jmanico/grim-prom… ~/grim-prompter
ln -s ~/grim-prompter/skills/threat-model ~/.claude/skills/threat-model
Then run /threat-model in your project.

eleven red pandas retweeted

Bug Bounty Tip:
Don't overlook JSON parameters like column.
A simple customerName::int error led to a confirmed SQL Injection. 👀
#BugBounty #SQLi

eleven red pandas retweeted

maldev-academy/whisperhijack: A stealthy process injection PoC combining Thread Name-Calling for payload delivery with Waiting Thread Hijacking for execution, with zero cross-process writes. github.com/Maldev-Academy/Wh…

eleven red pandas retweeted

Released TpDirectCallbackHijack, a process injection PoC where you overwrite one function pointer inside an existing thread pool object (TP_IO / TP_ALPC / TP_JOB), post a single completion packet, and the victim's own worker thread dispatches your shellcode. Restore stub puts the pointer back on the way through, so the thread pool keeps working.
No remote thread, no Get/SetThreadContext. Pool Party adjacent. Based on @_0xDeku's research.
github.com/Maldev-Academy/Tp…


eleven red pandas retweeted

Microsoft trained a language model on 4 TRILLION tokens using just three possible weight values: -1, 0, and +1.
And the GitHub repo behind it has crossed 41,000 stars.
It's called BitNet, and the engineering is fascinating.
Most language models rely on weights stored in formats like FP16 or BF16, requiring 16 bits per weight. BitNet b1.58 uses ternary weights, meaning each quantized weight has only three possible states.
That's where the 1.58-bit name comes from. Three states contain approximately 1.58 bits of information.
Microsoft didn't simply take an existing full-precision model and compress it after training.
Its BitNet b1.58 2B4T model was trained from scratch using ternary weights during the forward pass, with 8-bit activations. The model has roughly 2.4 billion parameters and was pretrained on 4 trillion tokens.
The results are impressive.
In Microsoft's published evaluation, the non-embedding weights occupy approximately 0.4 GB. The model also achieves competitive results against several full-precision language models in the 1B to 2B class.
And Microsoft open-sourced the inference engine needed to exploit this architecture.
It's called bitnet.cpp.
The implementation includes specialized CPU kernels, packed ternary-weight representations, lookup-table computation, and GPU inference support.
In the team's original CPU experiments:
→ Up to 6.17× faster inference on x86
→ Up to 5.07× faster inference on ARM
→ Up to 82.2% lower energy consumption on x86
Those results come from controlled tests using synthetic model configurations, rather than a guarantee for every deployed model.
What makes BitNet particularly interesting is that the efficiency comes from the model architecture, the training method, and the inference implementation working together.
The model weights, research papers, and inference framework are publicly available.
Open source under MIT.
GitHub: github.com/microsoft/BitNet
eleven red pandas retweeted

Simon Tatham, the creator of PuTTY, found a way to fake coroutines in standard C using the same switch/case trick behind Duff's Device.
He combined it with __LINE__ so a function could return a value, remember exactly where it stopped, and resume there on the next call.
no threads & assembly just a few macros. PuTTY still uses versions of this trick in its SSH protocol code.
Here's a minimal example:

eleven red pandas retweeted

对付REA逆向的利器来了!让AI无法逆向你的项目!
有人做了个BLA,专门给REA这类AI逆向工具下套。
假密钥、诱饵接口、干扰逻辑,往发布包里埋。AI拆出一堆看着挺有价值的东西,顺着研究就跑偏,Token还得照烧。
连REA的解析上限也利用上了。作者拿真实REA测过,加固后的JS报预算限制,Electron ASAR报容量错误,WASM接口只能读出一部分。
作者测的14个基准样本,加固后跑出来的结果都和原版一样。
自己有软件项目的,可以在项目目录跑:
1. npx bla-agents setup,接入Claude Code、Codex、Cursor等工具。
2. npx bla-agents harden .,扫描发布文件,执行加固和验证。
BLA项目地址:
github.com/qybaihe/bla
