

Sharing .env files is so 2019.
Vancouver
Joined March 2026
- Tweets69
- Following17
- Followers153
- Likes31


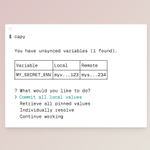
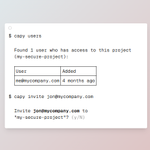
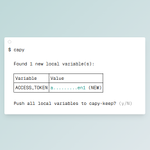
Your teammate shouldn’t need you online to get their app running.
Or your laptop open.
Or that Slack message from three weeks ago.
With Capy, sharing secrets works like sharing code:
capy push
capy pull
Ship without the .env scavenger hunt.
capy.sc

If your app runs PHP, check your version today.
The critical flaws disclosed last week are now on CISA's known-exploited list.
Patch first. Investigate exposure. Rotate credentials if compromise is suspected.
A secrets manager is not a substitute for patching.
Your code is on GitHub.
Your project docs are in Notion.
Your production secrets are in a Slack message from someone who's on vacation.
One of these workflows needs fixing.
Capy brings Git-style sync to secrets. No hunting down whoever has the working .env.
AI helped researchers find critical PHP flaws.
The takeaway isn't "AI code is insecure." This wasn't new AI-generated code.
It's that existing software is getting a new level of scrutiny.
"It’s been running fine for years" is not a security review.
AI can't squint.
The worst part of adding a new environment variable to a project:
Your PR merges, the build passes, and staging instantly crashes because nobody on your team knew you added STRIPE_WEBHOOK_SECRET.
Capy commits a keep.lock manifest to your repo so PR diffs clearly show which secret names changed without ever exposing the values.
Using Capy is simple.
AI changed how software gets built. SecretOps is next.
OAuth based authentication grants your agents and collaborators temporary access to locally encrypted secrets, making them revocable at any time.
Capy is all you need to sync, push, and pull variables for a project.
Setting up Capy in an existing project takes one command:
• Run capy in your project folder.
• It encrypts your .env locally, writes keep.lock, and auto-gitignores raw secrets.
• Your team runs capy pull and starts building.
Done in 10 seconds.
You edit your local .env.
You run capy push.
Your teammate runs capy pull.
That is the entire secrets management workflow.
No dashboards. No copy-pasting API keys across five browser tabs.
When you tell Cursor or Claude Code to build a feature on a new branch, it frequently breaks because your local .env is out of sync with staging.
With Capy, switching secret environments works just like switching code branches.
Sync, push, and pull your environment variables with standard Git primitives.
things .gitignore protects you from:
- git
things .gitignore does not protect you from:
- cursor
- claude code
- copilot
- your own screen share
- the intern
Secrets management tools make a simple mistake: they try to reinvent developer workflows with complex web dashboards.
You should not have to leave your terminal or learn a new paradigm just to share environment variables.
Capy treats secrets the way you already treat code:
👉 capy push to publish updates
👉 capy pull to grab team changes
👉 capy checkout to switch branch environments
No new mental model required.

You open your laptop at a coffee shop, pull down your repository, and immediately hit:
Missing environment variable: DATABASE_URL
Now you are spending 20 minutes texting teammates or remoting into your home desktop just to copy over API keys.
Capy lets you access project secrets securely across every device you own.
capy.sc
A quiet way AI-built apps leak secrets in production:
When an API route fails, default error handlers often dump the entire stack trace straight back to the browser.
Anyone triggering a 500 error can see your database connection string, internal paths, and environment variables sitting right in the response.
Always return generic error messages in production.
Introducing Capy, the world's first secrets manager.
AI changed how software gets built. SecretOps is next.
OAuth based authentication grants your agents and collaborators temporary access to locally encrypted secrets, making them revocable at any time.
Capy is all you need to sync, push, and pull variables for a project.
Comment for an invite at capy [dot] sc.

4/ Capy is a git-native secrets manager with end-to-end encryption, branch-aware syncs, and reviewable metadata.
5/ Why teams pick Capy
- Works through environment variables. Your code keeps reading process.env, os.environ, ENV, or the equivalent in your runtime.
- Secret branches. Capy branches are separate from Git branches. Switch them with capy checkout <branch>.
- Reviewable metadata. Commit keep.lock; it records the project and encrypted-value hashes, not values or keys.
- Local or browser-assisted interaction. Most commands run in the terminal. --web renders supported interactive setup and conflict screens on a local browser page.