FOLLOWS YOU • “Wir müssen wissen, wir werden wissen” -Hilbert • (he/they/him/them) • infosec and privacy aficionado • mage
@da5ch0 || wishabitchwoods 😉
Joined February 2011
- Tweets70.7K
- Following4.9K
- Followers8K
- Likes101K


—————————————————————————————————————————dash🏴☠️ retweeted

9 am: i can’t wait till bedtime
10 pm: i’ve always wanted to write my own operating system
—————————————————————————————————————————dash🏴☠️ retweeted

Hey just to let you know I am not taken. I'm available. Just like the ports on the open net your MSP uses to administer your domain controller

—————————————————————————————————————————dash🏴☠️ retweeted

If they ban open weights, we’ll be trading LLMs like ’90s warez.
We did it before, we can do it again.

—————————————————————————————————————————dash🏴☠️ retweeted

Periodic reminder: Good security architecture minimizes the number of bugs and CVEs you have to care about.


—————————————————————————————————————————dash🏴☠️ retweeted

Probably a good time to point you all to a tool I released not to long ago called SecretsStalker. If you have found an exposed client ID and secret to s service principal, SecretsStalker will authenticate you into the environment and recon the exact rights that it has.
github.com/rootsecdev/Secret…


Microsoft Security Research has identified extensive cloud resource destruction activity linked to JADEPUFFER, which Microsoft tracks as Storm-3168. The activity used compromised service principals and performed cloud credential collection that could be used to facilitate future exfiltration. msft.it/6015a9lob
Two compromised service principals divided discovery, destruction, and credential collection, with timing and overlapping token streams strongly indicating automated or scripted execution that included more than 100 storage account deletion attempts in about seven minutes.
Discovered by Sysdig in July 2026, JADEPUFFER is reported to be the first documented agentic ransomware operation. These new findings expand publicly documented activity associated with Storm-3168 and indicate an evolution in the threat actor's cloud operations.
Read the blog for analysis, Microsoft Defender detections, and mitigation guidance on protecting workload identities, revoking or rotating exposed credentials, and safeguarding backup and recovery resources.

—————————————————————————————————————————dash🏴☠️ retweeted

Hello, Little People Living Inside My Computer,
I have made a YouTube account to discuss malware reverse engineering and development. It will primarily target noobs. It will be lighthearted, poorly produced, and spontaneous.
youtube.com/@MalwareForFun


—————————————————————————————————————————dash🏴☠️ retweeted

Regular reminder… this hardening series by Jerry Devore is super awesome. There’s no way you won’t learn things by reading these.
Part 1 - Disabling NTLMv1
Part 2 - Removing SMBv1
Part 3 - Enforcing LDAP Signing
Part 4 - Enforcing AES for Kerberos
Part 5 - Enforcing LDAP Channel Binding
Part 6 - Enforcing SMB Signing
Part 7 - Implementing Least Privilege
Link to all articles 👇
techcommunity.microsoft.com/…


—————————————————————————————————————————dash🏴☠️ retweeted

When my wife asks me why I need night vision goggles I send her this:
—————————————————————————————————————————dash🏴☠️ retweeted


Introducing GLM-5.3: Built to Code. Ready for Cyber Defense.
- Top-tier coding and agentic capabilities, achieved through post-training on the 743B base model
- A major leap in cybersecurity, setting a new standard among open models
Tech Blog: z.ai/blog/glm-5.3

—————————————————————————————————————————dash🏴☠️ retweeted
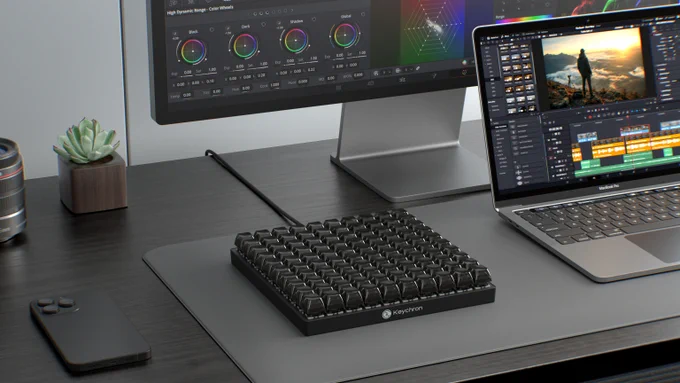
we call this the Chronically Online Hunch

ngl i lowkey want this so bad

Wondering what a 100-key macro pad is for?
💼 Work — open apps, launch websites, take screenshots, mute meetings, automate tasks
🎬 Create — cut clips, switch tools, change layers, adjust timelines, export projects
🎙️ Stream — switch scenes, mute mic, start recording, control OBS
🎮 Play — open Discord, control music, launch games, trigger in-game shortcuts
Your command center. Every key, your way.