


Binance says its Oct 29 hack may have started on a compromised DevOps engineer's laptop that reached a service container.
TRM says wallets on 10 chains all signed for the attacker. Keep signing systems off general prod access, and treat bulk signing requests as a breach.

Give each AI agent its own git worktree.
git worktree add ../app-login -b login gives an agent its own folder and branch on the same repo. Git refuses to check out one branch in two worktrees, so two agents can't edit the same branch by accident.

Add a 1-day cooldown to every JS project: min-release-age=1 for npm, minimumReleaseAge: 1440 for pnpm (on by default in pnpm 11).
The malicious tensorlake 0.5.144 sat on npm for about 1h40m. Bad versions usually get pulled within hours, so a day's wait skips them.


Run Android e2e and screenshot tests on a headless emulator.
-no-window drops the emulator window, so it runs in the background and on CI boxes with no display. Add -no-audio -no-boot-anim, use -read-only for parallel instances, and wait for boot_completed before tests.

Read the hooks before you open a cloned repo with an AI agent.
Per JFrog, 42 GitHub repos had hooks for Claude, Gemini, Cursor and VS Code that ran a hidden ~13 MB JavaScript payload on folder open or session start. Code search missed the files: too big to index.

GitHub Actions slowed for about 90 minutes on Oct 19 after one service lost its cache connections and every server retried at once.
A connection rate limit already existed, but it was in log-only shadow mode. Add backoff to retries and give shadow mode an end date.

Update Jenkins to 2.588 or LTS 2.580.2. The Oct 28 advisory fixes 15 vulnerabilities, including an XStream bug that can give any logged-in user with read access remote code execution.
On a new controller, install the patched build before running the setup wizard.

Node.js 22.23.4, 24.22.1 and 26.12.1 patch Broccoli2Shell, an out-of-bounds write in the Brotli decoder that can lead to remote code execution.
Your HTTP client may decompress Brotli even if your code never mentions it. Update, rebuild the image, restart.


Check your private repos for branches named ci-sync- plus six characters. Per Wiz, the Gheist campaign uses stolen GitHub tokens to commit a workflow that dumps secrets to the log in base32, so masking misses them.
Deleting the branch undoes nothing. Rotate the secrets.

Claude Code 2.1.311 now compacts and keeps going when a standard-context session passes 200K tokens. Before, it stopped mid-task.
Subagents can also use MCP tools from servers that connect late. Worth updating before your next long migration run.

GPT-6.1 Terra is now in GitHub Copilot, including Xcode and JetBrains IDEs. Per OpenAI, it solves 50.3% of Terminal-Bench 4.0 tasks at max effort, up from 21.5% for GPT-5.6 Terra.
I'd hand it the daily small stuff: a broken build, tests for one screen.


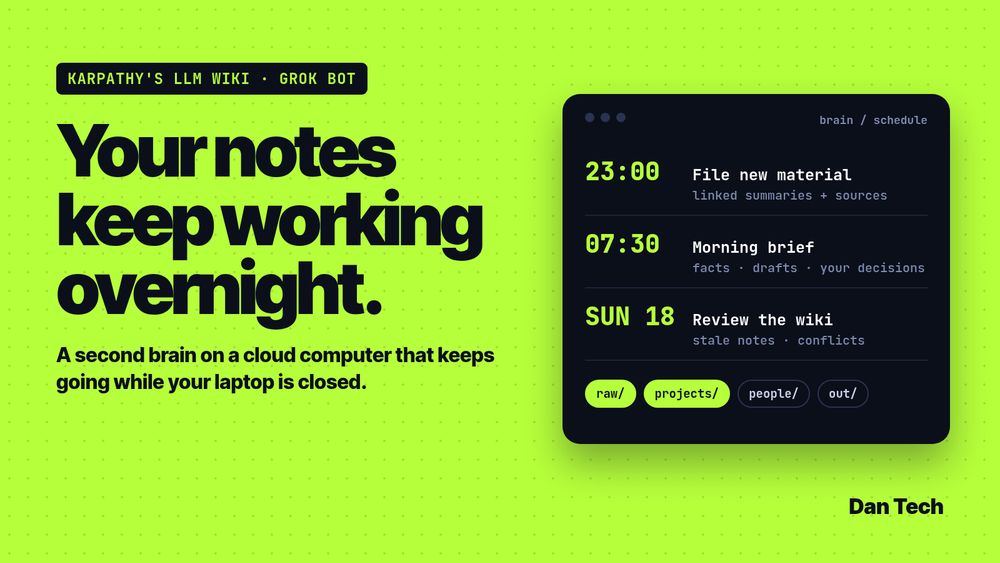
A Second Brain that turns your knowledge into finished work
Put your notes on a night shift before another week slips away
It seems my posts are getting low and lower impression. I need to change the angle of the tweet and start to share more attractive contents lol.

Kotlin 2.5.0-Beta2 cuts the Swift module setup in KMP. api() deps in commonMain now export to Swift automatically, and incremental compilation is on by default for Apple targets.

