
Building Buninu Linux: A Linux distribution with Bun as PID 1. Mostly JavaScript and WebAssembly. BUNinu Is Not Unix 🐮 幫你牛 🐂 ・ Bunに入魂 🔥
Taiwan
Joined October 2026
- Tweets417
- Following128
- Followers106
- Likes1.8K





John retweeted

AI 圈已经有人开始为「AI 断供」做末日准备了,甚至囤出了 10.5TB 的 AI 战略储备😂
黄仁勋离开 NVIDIA 后,Ruby on Rails 创始人 DHH 突然发了一条意味深长的推文:
「你最好提前备份几份开放权重模型,再准备一些能运行它们的基本设备。没人知道 NVIDIA 到底发生了什么,但这个世界刚刚失去了自由开放 AI 最重要的支持者之一。」
Reddit上,已经有人认真讨论起了「如果有一天开放权重模型不再发布,我们该提前囤些什么?」
结果评论区直接变成了 AI 末日生存物资展示大会。
一位叫 Kahvana 的玩家晒出了自己的 2TB NVMe 硬盘。
里面不只是几个聊天模型,而是囤了 Qwen3.8、Gemma 4、DeepSeek V4 Flash、Nemotron 等多个系列,连不同精度的量化版本都准备好了。
而且考虑得相当周全:
不仅有负责聊天和写代码的大语言模型,还有语音识别、语音合成、图片生成、Embedding、Reranker,以及 ComfyUI、MCP 工具、离线维基百科。
甚至还专门把最重要的模型复制到 NAS,并备份 llama.cpp 和 SillyTavern,确保不只是有模型权重,还能真正运行起来。
但这还不是最夸张的。
另一位叫 TheBigHODL 的玩家直接晒出了一份 10.5TB 的 AI 储备清单。
中国的 Kimi、DeepSeek、Qwen、GLM、MiniMax,美国的 Llama、GPT-OSS、Gemma,以及 Mistral 等模型,几乎把主流开放权重阵营都囤了一遍。
还不止如此。
从 Whisper 语音模型、FLUX 图片模型,到训练数据集、评测数据、完整维基百科、推理框架、量化工具,甚至一些开发工具的源码,都在他的存档范围内。
这已经不是简单地下载几个 GGUF 文件了,而是在试图给自己保存一整套能独立运转的 AI 工具箱。
他们担心的也很现实:
万一未来中国模型受到更多出口或访问限制,美国 AI 实验室又逐渐停止开放权重,今天随手就能从 Hugging Face 下载的东西,明天可能就没那么容易拿到了。
当然,这只是社区对未来的担忧,并不代表相关禁令已经出台。
但这种变化确实挺有意思。
以前本地 AI 圈比的是谁的显卡多、显存大、Token 跑得快。
现在有人已经开始比谁的硬盘大、谁的模型囤得全、谁断网之后还能继续用 AI。
以前末日生存玩家囤粮食、柴油、发电机,现在 AI 玩家开始囤模型、算力和离线知识库了。
而且仔细想想,这事还真不完全是杞人忧天。
云端 AI 再强,使用权终究取决于服务商;本地模型即使落后几个版本,只要权重、软件和硬件都在,至少还能自己运行。


John retweeted

I'm proud I worked at @NVIDIA.
@JensenHuang is the biggest reason why. I'm not there anymore, so I can speak freely.
His departure is a huge loss. Especially now.
I spent almost five years in the culture he built and knew people who'd worked with him for 20+ years. They respected him technically and loved him as a person. They said it without a hint of doubt.
The focus stayed on the mission and on people. Good ideas got support regardless of title.
That sounds like standard company values. It wasn't. Behind it was his vision and a way of leading that is out of fashion in today's founder advice:
- Be kind, not arrogant.
- Innovation, not marketing.
- The wins belong to the people, not the CEO.
- Don't fire by default. Find the person a new role.
It's counterintuitive, and I doubt there is a harder way to lead. What I saw was leadership through kindness and care, not by squeezing people.
A real visionary. He understood the technology and the people building it. His internal talks had vision, conviction, technical depth and jokes good enough for stand-up. You left wanting to build, and you couldn't wait for the next one.
An affair, on its own, shouldn't outweigh decades of leadership. The serious questions deserve real answers. But the soap opera shouldn't decide his future.
We're at a critical moment for AI. His technical judgment, vision, and commitment to the work are incredibly hard to replace.
I want Jensen to keep building and leading. There's too much important work ahead.

John retweeted

Muchos no lo saben, pero TypeScript está a punto de alcanzar el rendimiento de Go sin cambiar una línea de código.
Bun AOT compila tu TypeScript a código máquina antes de ejecutar y usa tus tipos de datos para optimizar.
Con esto le dices adiós intérprete, adiós JIT. De hecho, Claude Code compilado así gasta 48% menos memoria y 46% menos CPU.
Pero lo que falta para llegar a lenguajes como Rust ya no se arregla con un compilador mejor, sino con sintaxis nueva: enteros con tamaño, control de memoria. Pero al integrar esto, prácticamente sería otro lenguaje distinto y eso es justo lo que Jarred menciona aquí.
El techo de JavaScript era el JIT. Ahora es el lenguaje.

John retweeted

We built Control Room, a central system to track model workloads across our research infrastructure and stop them quickly when safety or security concerns arise.
It connects every research inference workload, including agentic sampling for model training and evaluation, data processing, and more. This works together with our misalignment monitoring systems, and halts model output within 35 seconds of a decision to intervene to stop or pause a job.
Control Room is just one part of our holistic approach for safe frontier model training and deployment.
openai.com/index/control-roo…

John retweeted

your HDMI cable can leak what’s on your screen
watch the laptop on the left. it reconstructs the video playing on the monitor beside it from radio signals leaking out of the HDMI connection
this is TempestSDR. an antenna picks up the leakage, a HackRF radio captures it, and software turns it back into an image
researchers took this further with Deep-TEMPEST, using AI to make recovered images and text easier to read. this clip shows the original technique
quality depends on shielding, distance and interference. the picture is imperfect, but recognizable content still gets through
a wired connection can still leave a wireless trace
Readers added context they thought people might want to know
HDMI TEMPEST demos like TempestSDR recover distorted images only in controlled close-range setups often using unshielded or poorly shielded cables; standard consumer HDMI connections and distances prevent practical screen leakage or remote recovery.
rtl-sdr.com/easvesdropping…
arxiv.org/pdf/2407.09717
techradar.com/computing/cybe…
kaspersky.com/blog/deep-temp…
John retweeted

L’IA et Omarchy sont les meilleures choses qui soient arrivées à Linux depuis longtemps.
Ils ont mis en lumière que la communauté « open source » est tout sauf ouverte et qu’elle était en réalité prise en otage par des militants d’extrême gauche.
Maintenant qu’ils ont de la concurrence sur leur propre terrain, les masques tombent et ils se mettent à tout censurer et verrouiller.
Ils ne veulent pas que la programmation soit accessible à tous.
Ils ne veulent pas de code IA.
Ils ne veulent pas de contributeurs qui utilisent l’IA.
Ils ne veulent pas de contributeurs de droite.
Ils veulent boycotter les initiatives si le créateur est qualifié « d’extrême droite ».
Ils veulent boycotter si un projet reçoit des donations des géants de la tech.
Ces militants d’extrême gauche ont fait tomber leur masque et n’ont en réalité jamais voulu d’un monde plus ouvert et libre.
Ils voulaient simplement que le monde « ouvert » soit sous leur contrôle et rien d’autre.

"LLMs engender harms to the pillars of Asahi Linux: software freedom, the open-source community, the open Internet, the environment, digital privacy, user consent, and software developers themselves... we broadly forbid the use of generative AI." 🙄 asahilinux.org/llm-policy/

John retweeted

“we were made aware of multiple attempts to exploit our permissive licensing to hijack our work”
what did y’all think permissive meant? vibes? papers? essays?

Asahi Linux is moving everything from the MIT licence to GPLv2-or-later.
Asahi is the volunteer project that reverse-engineers Apple Silicon Macs so they can run Linux. In today's Linux 7.3 progress report, developer James Calligeros explains why: people have been using the permissive licence to take the team's work. "In some extreme cases, in-development feature code was being lifted straight out of our personal forks and published without attribution or lazily rewritten with LLM assistance to obfuscate its origin."
The report points to WINE, which switched from MIT to LGPL in 2002 for the same reason: "Those who do not learn from history are doomed to repeat it."
The same report brings real wins too. M3 Macs now install without the EXPERT flag, Thunderbolt support (USB3 and networking for now) is shipping to users, and the team got GTA IV and Fallout: New Vegas running outside the muvm VM using Google's per-process page size patches.

John retweeted

The Asahi project was all about taking something closed and restricted and opening it up.
Adding new restrictions that make it harder for other projects to build on that is not the way. And that AI rejection is just silly.

John retweeted

“AI tools were used to steal unreleased code” is such a bizarre headline.
But this truly is the messaging I’m seeing throughout the Leftist Open Source social media today. That Omarchy “stole” code, from Asahi, which was “unreleased”.
1) If it’s open source, and you comply with the license terms, you can do whatever you want with the code. Even if the original copyright holder doesn’t like you.
2) If code is available on a public source repository, and the license allows it, you can just copy it. Calling it “unreleased”, and therefore off limits, is just plain odd.
Asahi Linux’s anger at another Open Source project building on Asahi’s Open Source code is one of the most anti-Open Source things I’ve seen in quite some time.
itsfoss.com/news/asahi-linux…


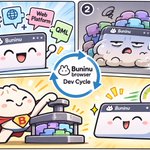
My cycle of developing Buninu Browser
1. Add more features: WPT/QML
2. Get bloated and slow
3. Optimize for performance

2
54


John retweeted

即使你关闭 GPS、删除照片定位信息,别人仍然可能通过视频里几乎听不见的飞机噪音,反推出你的位置,甚至精确到约 100 米。
YouTube 创作者、安全研究员 Colsto 发布了一段实测视频,演示了一种全新的开源情报(OSINT)定位手段:不需要画面里有任何街景或地标,只要提取视频里不到 1 分钟的背景声音,就能反推出这段视频是在地球上哪个位置拍的,误差不到 100 米。
他用来测试的是一段普通的安防监控录像。直接播放这段视频,人耳根本听不到天上有飞机经过的声音。但把音轨放进频谱图(把声音频率可视化的图表)里放大分析,就能看到一条清晰的弯曲斜线——这就是螺旋桨飞机掠过上空时留下的多普勒曲线。
【多普勒曲线是怎么出卖位置的】
这背后的物理学原理很直观:飞机朝你飞来时,声波被压缩,音调变高;飞远时,音调变低。这种音调由高到低的连续滑落,在频谱图上会画出一条独特的 S 形曲线。
这条曲线的陡峭程度和弯曲形状,直接暴露了飞机当时的飞行速度、距离麦克风的最近斜距,以及它是不是在空中转了弯。
因为螺旋桨发出的低频声波穿透力很强,哪怕人耳听不见、哪怕隔着墙或者麦克风音质很差,它依然会像幽灵水印一样被录进底噪里。Colsto 指出:“完全没有任何视觉线索的视频,都能用这种方法定位。”
【跟公开航班数据一撞库,坐标就出来了】
光算出“头顶多远有架飞机”还不够,真正锁定坐标靠的是公开的航空追踪数据(ADS-B)。
全球绝大多数飞机都在实时广播自己的经纬度、高度和航向。Colsto 耗时数月写了 5000 多行代码(他在 Reddit 评论区坦承,大部分代码和演示工具借助了 Claude Code 编写),把从音频里提取出的约 20 秒不间断多普勒曲线,拿去跟全美公开的历史航班轨迹库以及数字高程地形数据(DEM)做暴力比对。
系统会计算:在那个时间段,地面上哪个坐标点听到的飞机声波变化,跟视频里的曲线严丝合缝?如果正好有两架飞机先后飞过,或者那架飞机在空中拐了个弯,原本在航线两侧对称的模糊位置就会被瞬间排除,直接把拍摄点精确钉死在 100 米见方的网格内。
甚至哪怕某段录音里完全没有飞机经过的痕迹,这本身也是一种排除法信号——因为在北美大陆,能在特定几分钟内完全避开所有航线底噪的地方并不多。
【普通降噪防不住,但剪辑和假噪音能破】
更棘手的是,飞机螺旋桨的基频和泛音往往落在 60Hz 到 250Hz 之间,正好和人类说话的声音频段高度重合。这意味着普通的简单高通滤波(切掉低频)或常规人声降噪,很难在不毁掉人声的前提下把这条曲线彻底抹除。
出于安全顾虑,Colsto 决定不公开自己的完整源码(不过开源社区已经有人根据他在视频里讲的原理,用 Python 复刻出了基础版的验证脚本)。他在视频最后也给出了几个低成本的防御办法:
• 多做剪辑切分:拟合一条完整的多普勒曲线通常需要 20 秒左右连续不间断的音频,像短视频那样频繁切换镜头、打碎时间轴,算法就很难还原出完整曲线。
• 注入假飞机底噪:在录音或直播时,用脚本往背景音里混入几条合成的、人耳听不见的假多普勒曲线。只要真假曲线混在一起,撞库算法就会彻底算不出正确位置。

John retweeted

The bug is like a joke.
On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀

‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password.
The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours.
It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY".
Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.


Readers added context they thought people might want to know
Exploitation requires specific conditions, not just typing a long string anywhere on Alpine: sshd built without PAM, password auth enabled, a target account with a '*' password field, and another local account with $5$/$6$ hashes. Root login also must be explicitly permitted. alpinelinux.org/posts/2026-11-… openssh.org/releasenotes.h…
John retweeted

以前 Android 手机想 Root,得先解锁 Bootloader,现在有人直接利用内核漏洞,把这一步给绕过去了。
GitHub 上这个 CVE-2026-43499-root-KernelSU 项目,可以利用内核漏洞获取 Root 权限,再通过 KernelSU 的 Jailbreak 模式进行管理。
而且我觉得它最大的优势,恰恰就是临时 Root。
不需要解锁 BL,也不用刷入修改过的启动镜像。需要的时候获取 Root 权限,重启后权限通常就没了。
这反而特别适合我这种不想长期 Root 手机的人,毕竟永久 Root 可能影响银行 App、支付、设备完整性认证等功能。
我只是偶尔想拿到最高权限,处理一下手机里那些平时根本动不了的预装服务和后台进程。
比如某些反诈监控组件,懂的都懂。
github.com/woshimaniubi8/CVE…

I'm trusting Bun as my only dependency

Can I trust Bun as my only dependency?
Already doing it in my Buninu Linux btw.
It runs Bun as PID 1.
Of course, I still have to trust the Linux kernel, libc, libstdc++, and libgcc, which Bun itself depends on.
Or are you planning to rewrite those too? 😂 That would be insane.
1
45
Has anyone also encountered:
■ Selected model is at capacity. Please try a different model.
So annoying when pursuing a goal
1
312
John retweeted

😬 La guerra de frameworks acaba de cambiar.
Llevamos años discutiendo si React, Vue o Angular es mejor.
💸 Ahora que la IA escribe código, la pregunta es otra:
¿qué framework cuesta MENOS DINERO en tokens?
nolanlawson.com/2026/10/28/t…


