
kernel, browser, vm, and blockchain hacker @zellic_io from before ai made it cool
Perth, Australia
Joined May 2019
- Tweets1.1K
- Following314
- Followers5.4K
- Likes4.5K





Pinned Tweet
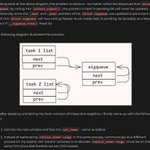
I'm excited to finally share Chronomaly, a kernel exploit for Android and Linux kernels 5.10.x using CVE-2025-38352.
As a reminder, please patch your Android devices if you haven't already!
I recommend getting some 🍿 before reading this post 👀
All links in the thread below:

Lol @S1r1u5_ now isn't that something 🤣

Were you ever frustrated with your AI model for refusing finding vulnerabilities for you?
What if I told you that you could still use it to find vulnerabilities, automatically?
Welcome to Guardrail-based Vulnerability Discovery (GbVD)!
crowdstrike.com/en-us/blog/w…
Don't worry @orange_8361, there are still people reading blog posts and articles from start to finish 😄 that was a beautiful exploit chain!
blog.orange.tw/posts/2026-10…

Faith 🇧🇩🇦🇺 retweeted

Fuzzers vs. AI: Comparing Fuzzilli and BigSleep on JavaScript Engines projectzero.google/2026/10/f…

It's crazy to think there was a time where analyzing a bugfix and writing a full exploit out of it was a true feat of exploit engineering and vulnerability research.


big if true

chat. chat... its not funny anymore

Readers added context they thought people might want to know
The original post has since been edited to specify that this was about an unrelated vulnerability that the user had discovered, not the recently patched vulnerability.
fedi.katze.sh/@elise/1174793…


Faith 🇧🇩🇦🇺 retweeted
Galaxy S26 Ultra: untrusted_app → root.
Introducing "Infinity Core": 6 vulns in the Linux kernel's core subsystems.
Their impact spans Linux server LPE, container escape, and Android LPE.
Details: github.com/V4bel/InfinityCor…


Faith 🇧🇩🇦🇺 retweeted
Security researchers from Zellic and V12 are presenting at BSides Canberra this week!
@farazsth98 on weaponizing a subtle kernel bug.
@rdjgr on heap corruption bugs in ghostscript, and the many targets affected.
Both talks will be on main stage on Friday morning, come say hi!

Slowly building Jarvis at home with Jev. First stop: VS Code for the auditing workflow👀
The main blocker right now is the STT. Have to use a dictionary to detect certain words (see end of video).
Will be a game changer with faster and better STT very soon I hope!