
Security researcher https://nitter.cf/t.co/SHjruAKnnB
iran
Joined September 2010
- Tweets1.3K
- Following477
- Followers421
- Likes1.2K
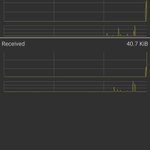

زیاد اهل تویت زدن نیستم و همیشه خواننده بودم اینجا اما وضعیت ما ۱ ماهه شده پینگ گرفتن،نمیشه کار کرد.
فیبر نوری با سرعت ۱۰۰ مگابیت گرفتم اما این سرعت منه ساعت ۲:۳۰ شب
۴۰ کیلوبایت ارسال و دریافت بعد از ۱ دقیقه

faryad rahmani retweeted

We built a full-system iOS fuzzer using QEMU+AFL, dup2() I/O channels, hypercalls, syscall enumeration & __syscall tricks on undocumented architecture. Bridged gap between fuzzing theory & closed-source systems.
Instructions and code
github.com/PacktPublishing/F…
Course and book
fuzzsociety.org/fuzzsociety-…
a.co/d/8AWaczi
The course has an exam and a certification.
#iOSFuzzing
#SecurityResearch #Fuzzing
faryad rahmani retweeted

All credit to @maple3142 but verified this works. Full PoC: gist.github.com/joe-desimone…


faryad rahmani retweeted

pre-auth RCE (CVE-2025-9242) stack buffer overflow vulnerability in WatchGuard Fireware OS
labs.watchtowr.com/yikes-wat…
Credits @watchtowrcyber
#infosec


faryad rahmani retweeted

GitHub - DedSecInside/TorBot: Dark Web OSINT Tool github.com/DedSecInside/TorB…

faryad rahmani retweeted
Analysis and exploitation of a Use-After-Free vulnerability in the Linux network packet schedule (CVE-2025-38001)
syst3mfailure.io/rbtree-fami…
#infosec #Linux

faryad rahmani retweeted

Indirect-Shellcode-Executor | Exploits the misconfiguration/vulnerability present on the API Windows method ReadProcessMemory github.com/mimorep/Indirect-…

faryad rahmani retweeted
We now have a (draft) @metasploit exploit module for the recent Fortinet FortiWeb vulns, chaining CVE-2025-64446 (auth bypass) + CVE-2025-58034 (command injection) to achieve unauthenticated RCE with root privileges: github.com/rapid7/metasploit…


faryad rahmani retweeted
VMware Workstation guest-to-host escape (CVE-2023-20870/CVE-2023-34044 and CVE-2023-20869) by Alexander Zaviyalov (@NCCGroupInfosec)
nccgroup.com/media/b2chcbti/…
#infosec


faryad rahmani retweeted

''GitHub - D4m0n/CVE-2025-50168-pwn2own-berlin-2025: CVE-2025-50168 Exploit PoC — Pwn2Own Berlin 2025 - LPE(Windows 11) winning bug.''
#infosec #pentest #redteam #blueteam
github.com/D4m0n/CVE-2025-50…

faryad rahmani retweeted

A Critical (CVSS 10.0) RCE flaw (CVE-2025-65108) in md-to-pdf allows arbitrary JavaScript code execution via malicious front-matter. Over 47K weekly downloads are affected. Update to v5.2.5.
#mdtopdf #RCE #SupplyChain #Cybersecurity
securityonline.info/critical…

faryad rahmani retweeted

Windows 11 24h-2 Kernel Exploitation
eneio64.sys LPE PoC
Task traversal is one of my favorite techniques. I hope everyone like it as me :)
Reach the blog at the link below ->
lnkd.in/dD6gKV3E
#Windows #Kernel #Exploit #win11 #24h2 #kernelexploit #windowskernel

faryad rahmani retweeted
(ZDI-CAN-25282)[ksmbd]Race condition between smb2 session log off and smb2 session setup -> UAF from session log off -> ... -> RCE(auth is required)
github.com/torvalds/linux/co…
zerodayinitiative.com/adviso…
@FFFVR_


Using AFL++ on bug bounty programs: an example with Gnome libsoup
offsec.almond.consulting/usi…
faryad rahmani retweeted
Exploiting the libwebp Vulnerability, Part 1 : Playing with Huffman Code : darknavy.org/blog/exploiting…
Exploiting the libwebp Vulnerability, Part 2: Diving into Chrome Blink : darknavy.org/blog/exploiting…

faryad rahmani retweeted

Check out the recorded Off By One Security stream with @mrexodia !! The slides and files used for debugging are available in the video description. Thanks again for joining as a guest, Duncan!
youtube.com/watch?v=AKcADaAa…
