

computer dinosaur
Timişoara, România
Joined April 2008
- Tweets3.3K
- Following112
- Followers283
- Likes409





Gupi retweeted

nginx2root / CVE-2026-123007: our take after reading the Xint and Wiz writeups
Two teams independently built working unauthenticated RCE exploits against nginx. F5 confirms the bugs, and fixes are out (1.31.9 / 1.30.7). This is a serious one. Patch.
But the version number alone doesn't tell you whether a server is exposed.
The widely quoted "98.9% of nginx hosts are in the affected range" counts version strings. The two critical bugs (CVE-2026-123007, CVE-2026-123633) sit in the HTTP/2 code. They can only be reached if HTTP/2 is enabled, and nginx doesn't enable it by default.
A server is exposed to them when all of this is true:
- nginx 1.9.5 to 1.31.8 (stable branch: up to 1.30.6), without a vendor backport
- HTTP/2 module compiled in (true for most distro packages)
- HTTP/2 enabled on a listener an attacker can reach
Check from outside:
curl -sI --http2 -o /dev/null -w '%{http_version}\n' https://HOST/
"2" means HTTP/2 is on, "1.1" means it's off. Test the nginx itself, not a CDN in front of it.
Check on the server:
nginx -v
nginx -V 2>&1 | grep -o with-http_v2_module
nginx -T 2>/dev/null | grep -E 'listen.*http2|http2 +on'
No output from the last command means HTTP/2 is not enabled.
How common is HTTP/2 on nginx? We spot-checked a few hundred nginx HTTPS endpoints listed on Shodan: roughly two thirds negotiate it. So not 99%, but still millions of servers.
What to do:
- Update to 1.31.9 / 1.30.7 or your distro's fixed package. Distros backport, so check the advisory, not just nginx -v.
- Can't patch yet? Turn HTTP/2 off until you can.
- The same release fixes three more RCE bugs that need other features (resolver with a variable proxy_pass, HTTP/3, mail proxy). Patching covers those too.
Xint: nginx2root.com/
Wiz: wiz.io/blog/nginx-http2-rce-…
F5: my.f5.com/manage/s/article/K…


Gupi retweeted

The full Identity and Access Administrator (SC-300) course is available from @MicrosoftLearn on YouTube!
Enjoy and don’t forget to share! 🙂
👇
youtube.com/playlist?list=PL…

Atenție la numarul +40 725 032 244, încearcă să vă recruteze pe WhatsApp pentru "activități online". Blocati si raportati numarul!

605
After 25 years of use, it's time to retire. Just a single disk failed during this time, out of 42. So long my reliable friend!
1
329
Dear @lufthansa
You are a great company, here is a free advice: email addresses like [email protected] are perfectly valid. Adding support for them in your booking system would bring a lot more online safety to your customers.
Thanks.
(see
en.wikipedia.org/wiki/Email_…)
1
218
A little piece of history. It worked 24 years without a hiccup. Now retired along with the others în the enclosure.

2
144
@@turboSMTP, do not be surprised if your IPs get listed on RBLs. trustlink.ro is constantly sending #spam through them.
1
1
162
In the era of AI, chat-bots and virtual reality, failing to set a proper default email address at a reputable company is a sign of .... (suggestions, please)
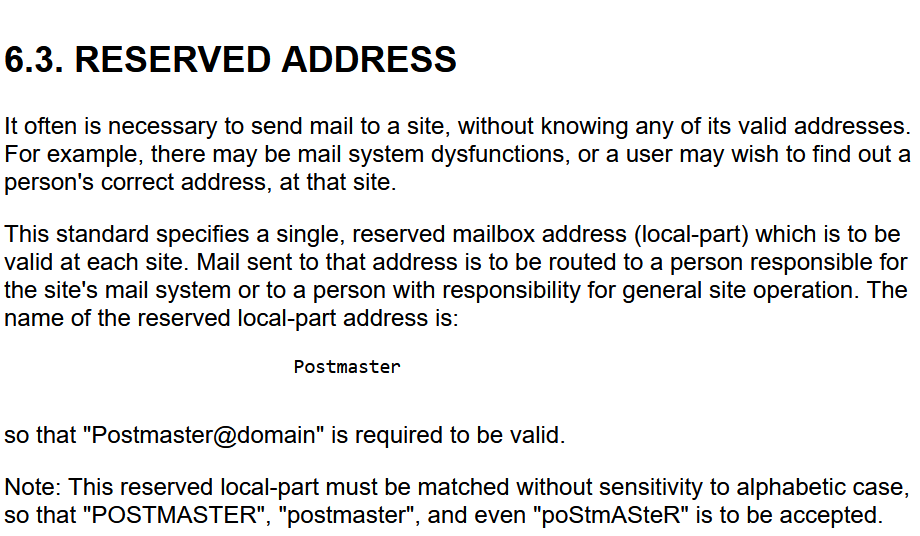
ALT RFC822 https://www.w3.org/Protocols/rfc822/
137


medintern.ro website (or hosting account) seems #compromised, as I have received #phishing from a server with proper DNS records set on bulk.medintern.ro. Tried to phone the owners and explain them what to do, but they seem not to be interested.
79
Hey @FIGC, I have just received a phishing message sent via your SMTP server. You might call the IT guys and ask them to verify smtp1.figc.it (DM me and I will tell you which account seems to be compromised)
127