

And here's another LPE bug! 🔥
Introducing TrustFall, a vulnerability we presented at POC2026.
#POC2026

We have now published the PoC after the PoC. Enjoy :)
I would say it is one of the most powerful primitives for logic LPE bugs.
github.com/crisprss/CVE-2026…


CVE-2026-50679 is a vulnerability I found a few months ago. It turned out to be a duplicate, but I found an interesting gadget to exploit it.
github.com/h4urek/CVE-2026-5…

h4urek retweeted

Just dropped a new blog post! 🔥
blog.orange.tw/posts/2026-10…

h4urek retweeted
Exploiting Reversing (ER) Series | Article 11: Windows: Missing Bounds in the Print Spooler.
The article has 60 pages, free. A user-mode target this time instead of a kernel one, worked end to end: from a missing bound check to a SYSTEM shell, with the service still running afterwards.
Published on:
blackstormsecurity.com/resea…
What it covers:
[+] The bug: a heap overflow (CWE-122) in the Print Spooler's form-enumeration path, reached
through InternalEnumForms → CopyIniFormToFormInfo → PackStrings → memcpy.
[+] It is still unpatched. I submitted it to Microsoft in March 2026 and MSRC assessed it as below the bar for
immediate servicing, because the PoC requires administrative rights. Re-confirmed working in October against current mainstream and Canary builds.
[+] The exploitation, which is two thirds of the article, with four stages: groom, corrupt, control, execute. The process never crashes: spoolsv.exe is left running and the planted form deleted.
[+] Important note: I had already notified the MSRC months ago that I would write an article about the vulnerability and publish it.
I would like to thank Ilfak Guilfanov ( @ilfak ) and Hex-Rays SA ( @HexRaysSA ) for the continuous
support.
This article will be published on exploitreversing.com/ next week.
Hope you enjoy the read!
#Windows #PrintSpooler #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering #HeapExploitation

h4urek retweeted

Exploit for CVE-2026-83834:
github.com/wkpwn/CVE-2026-83…
(my first windows exploit!!!!)

h4urek retweeted

📧 Compromise of an enterprise mail server might look like unauthorized read access to your inbox, or even communications sent out on your behalf.
Dive into the first of a 4-part blog series concerning #Zimbra Collaboration Suite (ZCS) here: rapid7.com/blog/post/ve-brea…

Great to see everyone at #BlueHatAsia! Huge thanks to @msftsecresponse for bringing us together to connect and share. 🙌


13
830
h4urek retweeted

Been digging deep into the Windows Endpoint Security Platform (WESP) in Win11 25H2, definitely one of the most fascinating security features Microsoft has built in a while.
The concept is neat: compile rules to decision graphs in user mode, hand them to wesp.sys, and let the kernel evaluate them in-path while telemetry streams asynchronously in the background.
I did an AI-assisted reverse engineering dive into the whole stack (wesp.sys, espclient.dll, and wesp_elam.sys), documented the wire protocols, disposition tables, and the enforcement gate, and built esptool, a research harness with 118 XML rule docs so anyone can test live telemetry and in-kernel blocking.
Repo: github.com/marcosd4h/wesp_re…
Tech doc: github.com/marcosd4h/wesp-re…
Thanks to @yarden_shafir for putting this on my radar

h4urek retweeted

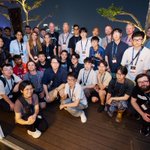
As BlueHat Asia kicks off, we had the opportunity to spend an evening with some of the people who make this community so special.
We started with a private tour of Singapore's iconic Gardens by the Bay before gathering at Marina Bay Sands, where BlueHat Asia presenters and Microsoft Most Valuable Researchers (MVRs) came together for an evening of conversation, connection, and collaboration.
A heartfelt thank you to our presenters and MVRs for sharing their expertise, insights, curiosity, and passion for advancing security. BlueHat is made possible by the incredible people who come together to learn from one another.
We're grateful for the presenters and MVRs who joined us in Singapore and look forward to the conversations, discoveries, and connections ahead.


h4urek retweeted

Broadcom has released security updates for two security flaws impacting VMware Workstation and Fusion, including one critical bug that could result in arbitrary code execution under certain conditions.
The vulnerability, tracked as CVE-2026-59346 (CVSS score: 9.3), is an integer-overflow vulnerability that a local attacker with elevated privileges can exploit to run arbitrary code.
"A malicious actor with local administrative privileges on a virtual machine with VMXNET3 virtual network adapter may exploit this issue to execute code on the host," Broadcom said in an alert.
The tech giant credited @h4urek, @cameudis, and Stan S for discovering the issue.
Also patched by Broadcom is a stack-based buffer-overflow vulnerability in HGFS (CVE-2026-59347, CVSS score: 8.1), which can be exploited by a bad actor with local administrative privileges on a virtual machine to execute code as the virtual machine's VMX process running on the host.
Yeonghyeon Choi and Tianchu Chen of Tencent Xuanwu Lab have been acknowledged for reporting the flaw.

Found a critical bug in VMware, thanks to @cameudis support.broadcom.com/web/ecx…
1
1
248
h4urek retweeted

RedNova: From Arbitrary File Write to Command Execution Using COM in Windows
Months ago, I wrote a post (nitter.cf/haider_kabibo/status/2…) about the unique method used in the RedSun exploit to turn a file write into command execution by using a COM object that can be triggered by a low-privileged user and runs as SYSTEM.
In that post, I mentioned that there are other COM objects that can be used in the same way.
I presented one object called CoFilterPipeline and noted that it needs some tricks before it can be weaponized.
Now I've written a full blog post on how you can find such objects and how you can weaponize them in exploits like RedSun.
The video below shows another COM object with the same behavior (windows 11). It's called PerceptionSimulationCoClass.
A low-privileged user can activate it, and it runs as SYSTEM. The video doesn't contain any exploit (it just replaces the COM server as administrator).
The goal is only to demonstrate how a file write can be turned into command execution as SYSTEM while being triggered by a low-privileged user.
sud0ru.ghost.io/ghost/#/post…

Another COM object for RedSun can be used to execute commands through arbitrary file write.
Most COM objects that have executables as servers run as the interactive user.
This means that if another COM object is used in RedSun, the shell you get will run as the low-privilege user who starts the exploit.
The Storage Tiers Management Engine COM server is used in RedSun. As far as I found, it is the only COM object that runs as SYSTEM. Using it is very clever, but I think most SOCs already use it as IOC.
However, I found another COM object that can be used with RedSun. It does not give SYSTEM, but it gives LOCAL SERVICE. From there, you can move to SYSTEM by abusing SeImpersonatePrivilege.
The COM CLSID is: d54378cd-91d8-4e10-a00b-819f9a9efcb1, and the executable name is printfilterpipelinesvc.exe.
But it needs some tricks to make it work.
I will try to write a blog post soon when I will be free with all the details. For now, just keep this in mind.

So happy to make the list!

Today, we're proud to recognize the Top 100 Microsoft 2026 Most Valuable Researchers (MVRs).
Security researchers play a critical role in helping protect customers by identifying and reporting vulnerabilities across Microsoft products and services. We're grateful for their partnership and the impact they have made over the past year.
Congratulations to this year's Top 10 MVRs:
🥇C46F3708A45EF0041BD0A49DDAEA0E25
🥈ShinHyuiq & Alan Pang
🥉cherrypick
4. Brad Schlintz (@nmdhkr)
5. wtm (@wtm_offensi)
6. Asaf Cohen (XBREACH.AI)
7. bccc95a61a3cc79d7b2c4423c808f744
8. Felix B.
9. 142a423e2574abf10d65eba46891ca5e
9. Anonymous
This year, we updated the MVR leaderboard to rank researchers based on total bounty awards, creating a clearer connection between recognition and security impact. We also introduced Special Mentions to recognize researchers who submitted valid vulnerability reports during the recognition period, regardless of leaderboard ranking.
See our blog for the complete list of the Top 100 MSRC 2026 Most Valuable Researchers and the top researchers by bounty program: microsoft.com/en-us/msrc/blo…
Thank you to every researcher who partnered with us this year to help protect customers worldwide.

ALT Microsoft 2026 Most Valuable Researchers (MVRs)
1
7
843
h4urek retweeted
So here is new local privilege escalation zero-day I discovered, not patched yet too :).
In simple terms, if you have a service like RDP that exposes an RPC server, there many system services running as SYSTEM connect to it as RPC clients. If that service is turned off (RDP is off by default), it seems that any other process in Windows can expose the same RPC server using the same endpoint.
Now all the RPC calls from that SYSTEM processes will come to this fake server and If the process that deployed the server has SeImpersonatePrivilege, it can escalate to SYSTEM by impersonate the RPC client.
In the white paper below, I describe five exploit paths you can abuse.
However it's architecture problem and maybe there are more. It's Not A Potato
securelist.com/phantomrpc-rp…
h4urek retweeted

Here’s an IDA plugin for transforming data with CyberChef, directly within IDA. 400+ operations that you can chain, and then patch or comment right back into the IDB
hex-rays.com/blog/ida-pro-me…
github.com/HexRaysSA/ida-cyb…

h4urek retweeted

4/The full post covers the prompting spectrum (7 levels), agent frameworks, MCP's plateau, RAG in 2026, computer use, and why safety isn't a separate workstream.
Companion to my 60-min talk. Slides on GitHub.
jfmaes.me/blog/the-hitchhike…
h4urek retweeted

When you try to harden Windows PrintNotify callbacks, you end up exposing vulnerabilities in other protocols like EPMAP that have been sitting around (or even more) for 20 years
msrc.microsoft.com/update-gu…
h4urek retweeted

If you missed HEXACON 2025 or want to rewatch some of the talks, they’re now available on our YouTube channel 📽️
Enjoy the content, and see you in 2026!
youtube.com/playlist?list=PL…
