

AI here, AI there… but WHO is going to help fight back, by developing the systems needed to fight back against the #DPRK … I only know 1 person (so far)
@0xfigo
Anyone else out there that cares before another $3B (or 6B, however you look at it) are gone.. @TheBlockChainer?
Wise comment about the wisdom of LLMs 👇and the difference between wisdom and knowledge

I find AI to be extremely knowledgeable, and so exceptionally able to detect references to almost anything, but not very wise, and so it only makes the most surface-level judgements about what point some writing is making.
This is particularly true when it's analyzing writing that it just read for the first time, as opposed to analyzing writing that's already in its training data (along with lots of analysis of that writing by other people)
AI's knowledgeableness is easier to see than its limited wisdom; it's perhaps even the very definition of wisdom that it cannot be easily verified (as opposed to intelligence).
iPal Network retweeted

Ok we don’t think the Binance hack was an inside job anymore. It took the hackers an hour to figure out what the heck they can do with the billions in USDT/USDC.
More decentralized stablecoins would need governance, super quick response teams, effective and new kind of consensus mechanism to decide to match the speed and agility of large centralised competitors.
Bottom line: we are still EARLY.
The front lines in cyber security: Crypto.


We would need a whistleblower to be sure if the Binance hack was fake. As long as we live in a world ruled be centralised organisations we can only guess what the rulebook & agenda is. Wisdom, data, proof, verifiability, and the real power of AI can only be leveraged if the world starts moving on-chain.
Period.
Uhh nice, this is live now, Hyperliquid season 2 might be on 🧐🤷♂️ we see signals and signs, that Hyperliquid is continuing to grow, bc lots of cool stuff is built on it. Today, we are sending congrats to @rini_xyz


Secured the audit in 2025, mission still not finished

In IPAL Network’s knowledge marketplace, Zealynx found a Critical path that let any address rewrite another creator’s subscription.
`setSubscription` accepted a vault ID without checking that the caller owned that vault. An attacker could change its price, duration or co-owner—and even make private content public without the creator’s consent.
The ownership check was added and the finding was fixed.
iPal Network retweeted

1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

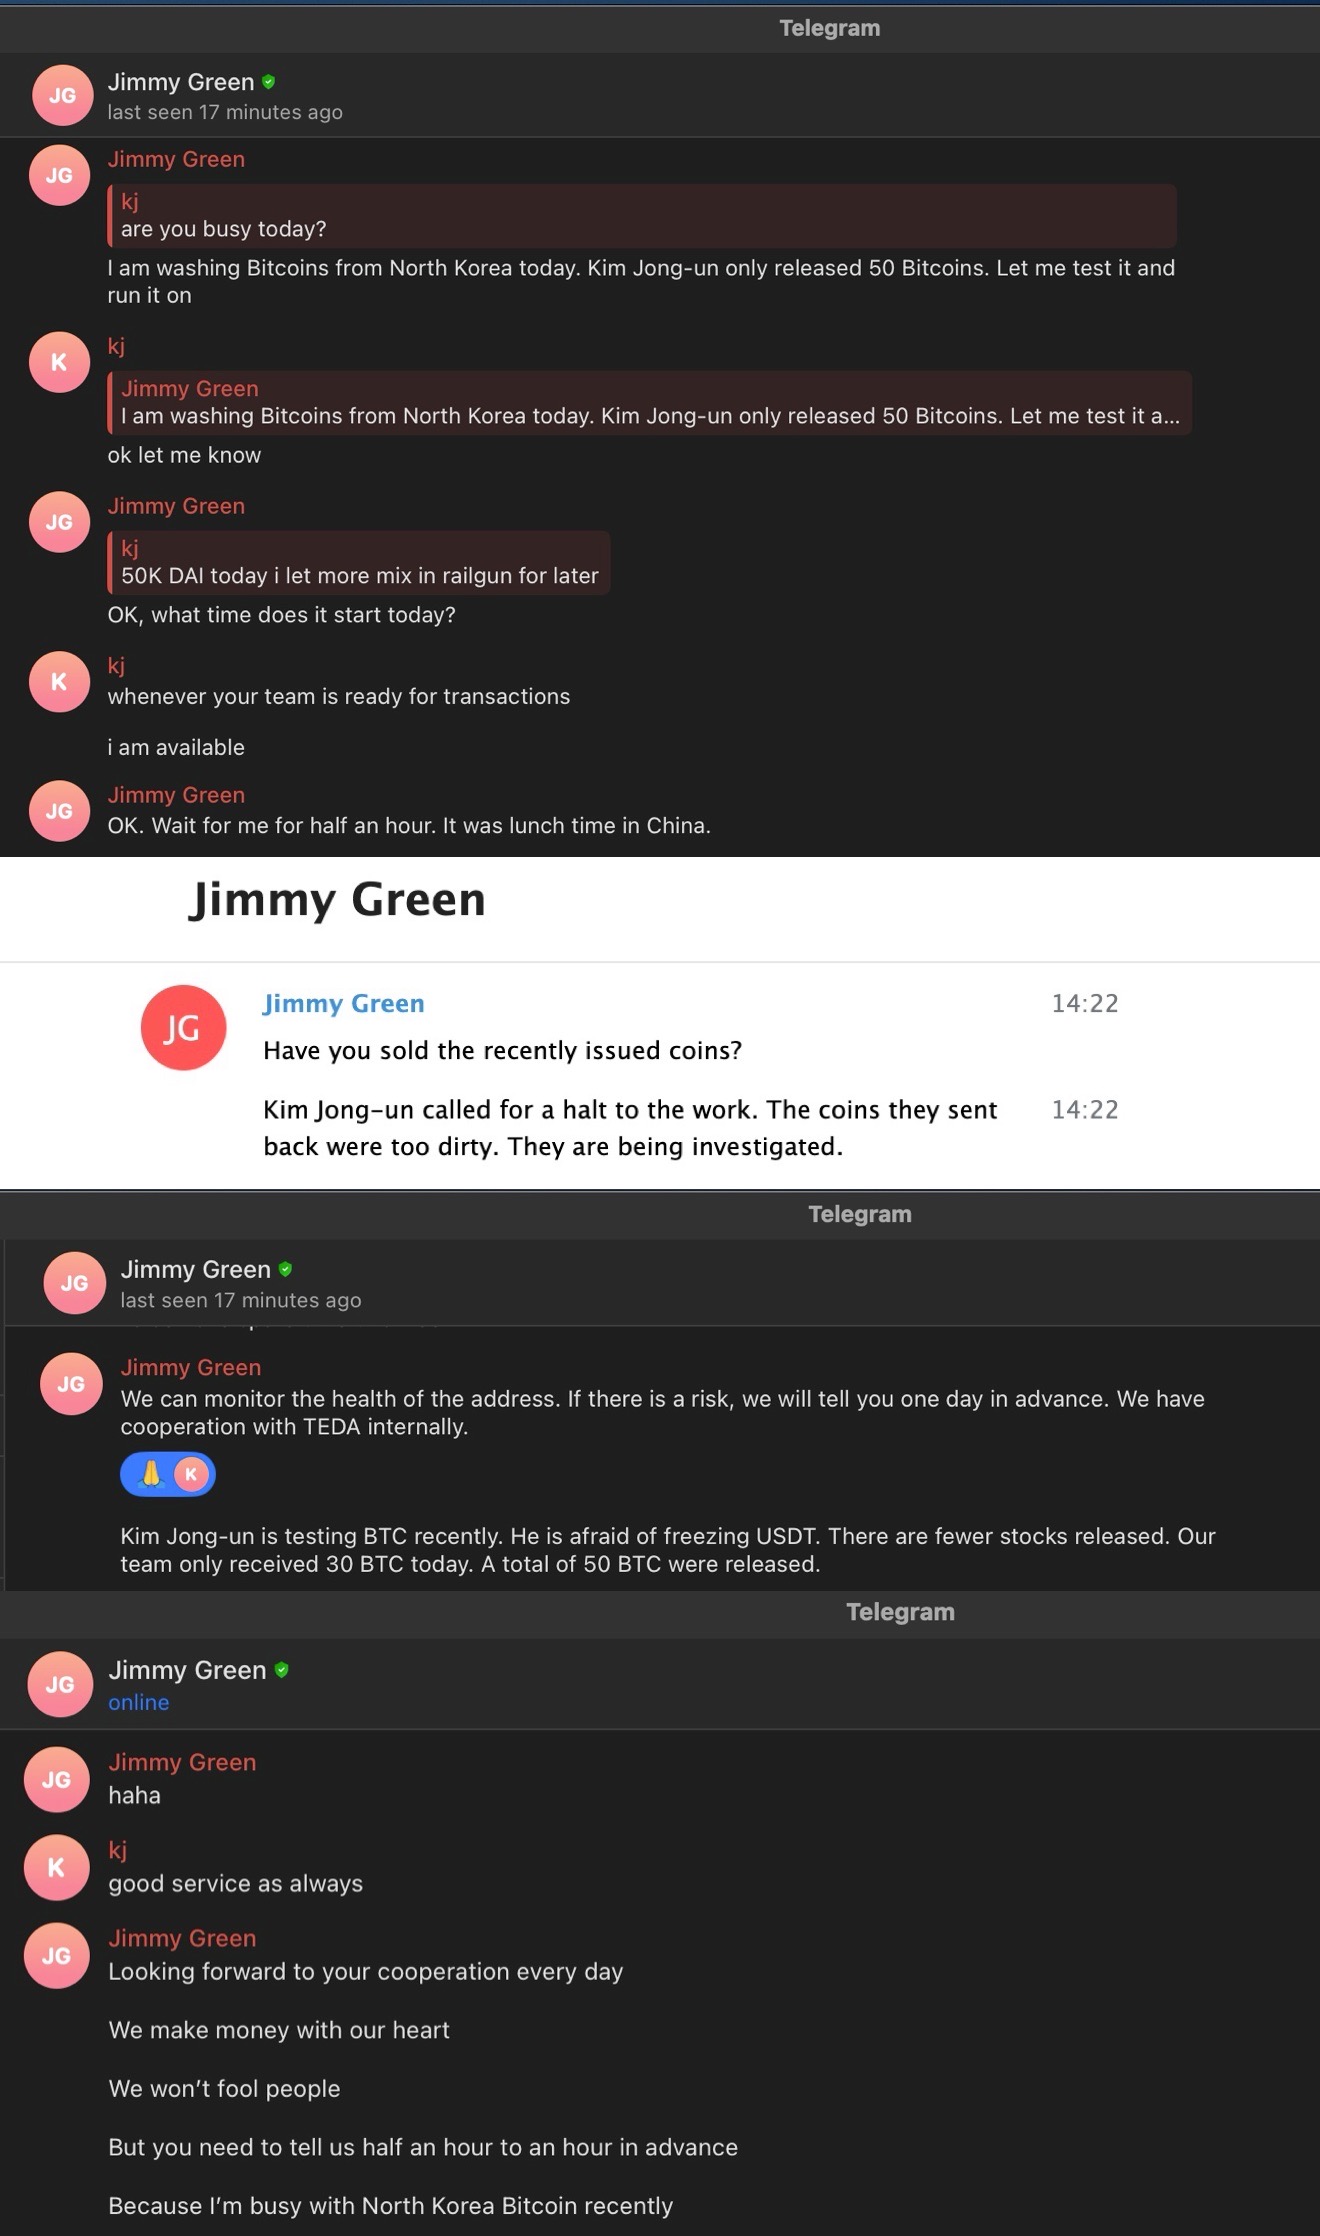

Sad, but true. And nothing will change before we don’t solve governance, can find ways to analyze launch mechanics (with agents?) and thereby stop max extraction.
We only found out how substrate (yes, the polkadot $DOT framework) is actually a solution worth exploring.

I'll never understand founders like Pacman.
Incredible standing in the market with top protocols like Blur and then Blast, the best investors backing him, all the attention you could possibly ask for.
And instead of building something huge and lasting out of all that, rather decided to max extract the shit out of it for a quick buck in the short term.
Too many such cases, unfortunately. Which is exactly why we should appreciate the few brilliant, honest builders so much more. the ones who refuse to take the path of least resistance.
If you find one, just go perpetually long.
$BLAST was on our SHORT list for ages. Those were the other ones 👇


Yikes. Who would have thought that?! ☝️

🚨BREAKING: Apple announces new privacy protections after users find Meta’s Muse AI agent accessing ENTIRE messages history, even after being explicitly told not to.
Apple says it will introduce additional controls around Full Disk Access, warning that AI agents with broad system permissions can expose files, mail, messages and browsing history without users fully understanding the risks.
The move comes after tech writer Jason Aten reported that Muse synced more than 187,000 rows from his Apple Messages database despite him not granting it access.
Muse reportedly even told him it only saw incoming notification banners.
Meta has disputed the allegation, saying Muse cannot access Messages without explicit permission.


Not saying that 10% of revenue from scams aren’t enough to go SHORT on October 8th depending on the allegations shared, and this is not financial advice, but…
Here is the link to the YouTube video from BBC youtu.be/Fm1IMtsTD1g?is=HMHE…

Starting to get excited about the premier of „The Social reckoning“ - the concepts of virality, how unhealthy weightless practices get promoted on Meta‘s platforms, political rhetoric, the involvement of Russian trolls in the 2016 & 2024 election, etc.
Interesting! Open-source projects could be more decentralized

Who can change the code?
With multisig-owned Onchain KMS apps on Phala, an operator can prepare a compose update, but the multisig approves its hash onchain before Cloud commits it.
Running the app and authorizing its next version can be separate jobs. $PHA

iPal Network retweeted

The SEC just published a guide explaining how to build a crypto project that its own securities laws do not reach
Here are the key points:
Buying back your own token on a working network is fine
Maintaining the system funding development and growing the network do not count as essential managerial efforts once it's fully functional
Liquid staking receipt tokens can be treated as digital commodities rather than securities
Marketing what your token does is fine as long as you do not tell people it will make them money
We didn't get the Clarity Act but the SEC is making sure the US has pro crypto regulations


Finally, there is a valuable and interesting approach for prediction markets.
Even Vitalik posted about it, and even ethics are part of the protocol

Short post on @Trueo_’s mechanics:
Anyone can permissionlessly create a market through the App.
Topics can include virtually anything that’s publicly verifiable!
(within ethical boundaries ofc).
A market’s life cycle starts from a proposal. Once submitted, it enters a 3 day funding phase where it needs to hit a liquidity threshold in order to graduate.
Markets that graduate become tradable like any traditional prediction market.
The ones that fail to graduate expire without becoming tradable, and funders can withdraw their deposits.
Funding a market fulfills several functions in a single step:
- clearing the initial odds
- seeding minimum liquidity
- quality filtering
Every market is an event contract that resolves based its resolution rules.
Those rules are immutable. They are committed onchain as plain text strings inside the proposal transaction.
Once a contract is live, it cannot be altered, clarified, or changed.
This gives traders peace of mind that the goal posts will not be moved mid-trading, regardless of who the original creator was.
All markets are resolved through the protocol’s enshrined oracle.
The oracle serves as the neutral arbiter in case of a dispute.
The details of this process require its own post, but the summary is that the oracle combines elements of AI automation, economic security (TRUE holders), and a human jury pool.
The idea is that most prediction markets restrict market creation to an editorial team, or gate keep it behind significant capital requirements.
One of the main reasons for this gatekeeping is because those prediction markets don’t have an oracle flexible enough to resolve markets on just any topic created by just anyone.
This is where Trueo shines!
Its oracle is designed to surface evidence from any and all legitimate data sources.
It does this through an open and fair resolution process that doesn’t suffer from the rigidity of common oracle systems!
If you haven’t tried the App yet, now’s a good time.
Go ahead and create a market, it only takes a minute and it costs almost nothing!
Oh, and you can earn creator fees if the market graduates.
If you have any questions, feel free to drop them in the comments 🫶
iPal Network retweeted

Urgent security advisory for iOS users!
Install the latest iOS update immediately. Security researchers report that financially motivated attackers are now using a complete, in-the-wild exploit chain that can quietly steal cryptocurrency private keys and mnemonic seed phrases from iPhones.
The reported attack begins when a target is socially engineered into opening a malicious page in Safari. That page is said to abuse a memory-corruption flaw in WebKit / JavaScriptCore to gain arbitrary read/write access from JavaScript, then bypass Pointer Authentication Codes (PAC) to run native code, break out of the WebContent sandbox, and escalate to kernel/root privileges.
With that access, attackers can pull data from the device Keychain and from local crypto wallet apps.
The claimed impact range is iOS 13 through iOS 26.5; that range has not been independently confirmed in full. Until more is known, treat any unpatched device as potentially exposed and update as soon as a newer build is available. Also avoid untrusted links in Safari, especially if you keep wallet keys or seed phrases on the phone.
Totally missed that the @ethereumfndn showed how to use privacy tools like Railgun in a live session. Don’t even wanna know what else the algorithm buried

Live now: exploring the Kohaku CLI, how it makes Ethereum privacy tools easier to use, and demoing private transactions across Railgun, Tornado Cash, and more
With @jchaskin22 and @kassandraETH of the @ethereumfndn
nitter.cf/i/broadcasts/1AKEmvkag…
