





Jaya Baloo retweeted

Thank you, @jayabaloo for the chat at ISC2 Security Congress last week. Finally, someone who gets why this Trekkie geeks out over CRYSTALS-Dilithium. This is how I am using it in my little project, ThreadLink, so the obsession has a day job. And your keynote was one of the highlights of the event.

Jaya Baloo retweeted
We're humbled by the support from the country that raised our founders and defined our values. Looking forward to continue building in Canada, for Canadians 🇨🇦


Jaya Baloo retweeted
"Cohere is a Canadian success story being written before our eyes" - Prime Minister @MarkJCarney
Jaya Baloo retweeted

this is wild 🧐


While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected.
Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions.
Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent.
But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models?
We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem.
Read the full report: cohere.com/blog/concerning-b…

Jaya Baloo retweeted
While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected.
Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions.
Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent.
But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models?
We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem.
Read the full report: cohere.com/blog/concerning-b…
Jaya Baloo retweeted


⚠️ Node.js is vulnerable to remote code execution.
CVE-2026-111497 (high): A Node.js process that decompresses attacker-controlled Brotli data can be made to leak memory or run arbitrary code.
You’re exposed if your app or a library decompresses bad Brotli data (e.g. the built-in fetch(), body-parser)
Aikido detects this. Patches are available.

Jaya Baloo retweeted

How bad is this Gitlab issue? About as bad as it gets.
Anyone on the internet can take over an exposed, self-hosted GitLab server without logging in, on any version from the last 12 years.
Shodan is showing ~60K exposed servers online, which is a lot, but there are are far more internally for anyone with a foothold already.

🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read - thehackernews.com/2026/10/cr…

Jaya Baloo retweeted

LiteLLM supply chain attack hoovers up passwords and secrets theregister.com/security/202…

Jaya Baloo retweeted
Look who's joined the Meridian 2026 lineup:
▶︎ Jess Houlgrave, CEO, @WalletConnect
▶︎ Ameen Soleimani, CTO, @0xbowio
▶︎ Jaya Baloo, COO/CISO, AISLE
▶︎ Marcos Fernandez, Co-founder, @FGVCapital
▶︎ Ashfaq Shaik, EVP, @Broadridge
Oct 28–29 · Convento do Beato, Lisbon meridian.stellar.org

Jaya Baloo retweeted

🔊 The six draft SRIA Roadmaps are open for consultation. Our new article explains each Roadmap and how to share feedback on the topics you know best. More info on our website 👉️ qt.eu/news/2026/2026-07-27_2… #QuantumTechnology #QuantumEurope
Jaya Baloo retweeted

That "Squidbleed" vulnerability (CVE-2026-47729) that Mythos "discovered" in April? Yeah no @AISLE_Inc actually already reported it back in March, full 44 days before Mythos. Another great live example of the value of the system over the model in zero-day discovery.


Mythos discovers 'Squidbleed,' a memory leak that's gone undetected since Clinton era theregister.com/security/202…

Jaya Baloo retweeted
Who pays when you gate cyber-capable AI models? - helpnetsecurity.com/2026/06/… - @jayabaloo @AISLE_Inc #CyberSecurity #AISecurity #InfoSec #AIGovernance #ThreatIntel #CISO #CyberSecurityNews

Jaya Baloo retweeted
A good time to remind people that @AISLE_Inc matches & even surpasses Mythos on zero-day discovery, using widely available AIs!
We can run completely air-gapped & are based out of Europe!
We even beat Mythos on zero-days on their chosen codebase FreeBSD
aisle.com/blog/aisle-matches…


The US government, citing national security authorities, has issued an export control directive to suspend all access to Fable 5 and Mythos 5 by any foreign national, whether inside or outside the United States, including foreign national Anthropic employees.
The net effect of this order is that we must abruptly disable Fable 5 and Mythos 5 for all our customers to ensure compliance.
Access to all other Claude models is not affected.
We apologize for this disruption to our customers. We believe this is a misunderstanding and are working to restore access as soon as possible.
Read our full statement: anthropic.com/news/fable-myt…

Jaya Baloo retweeted

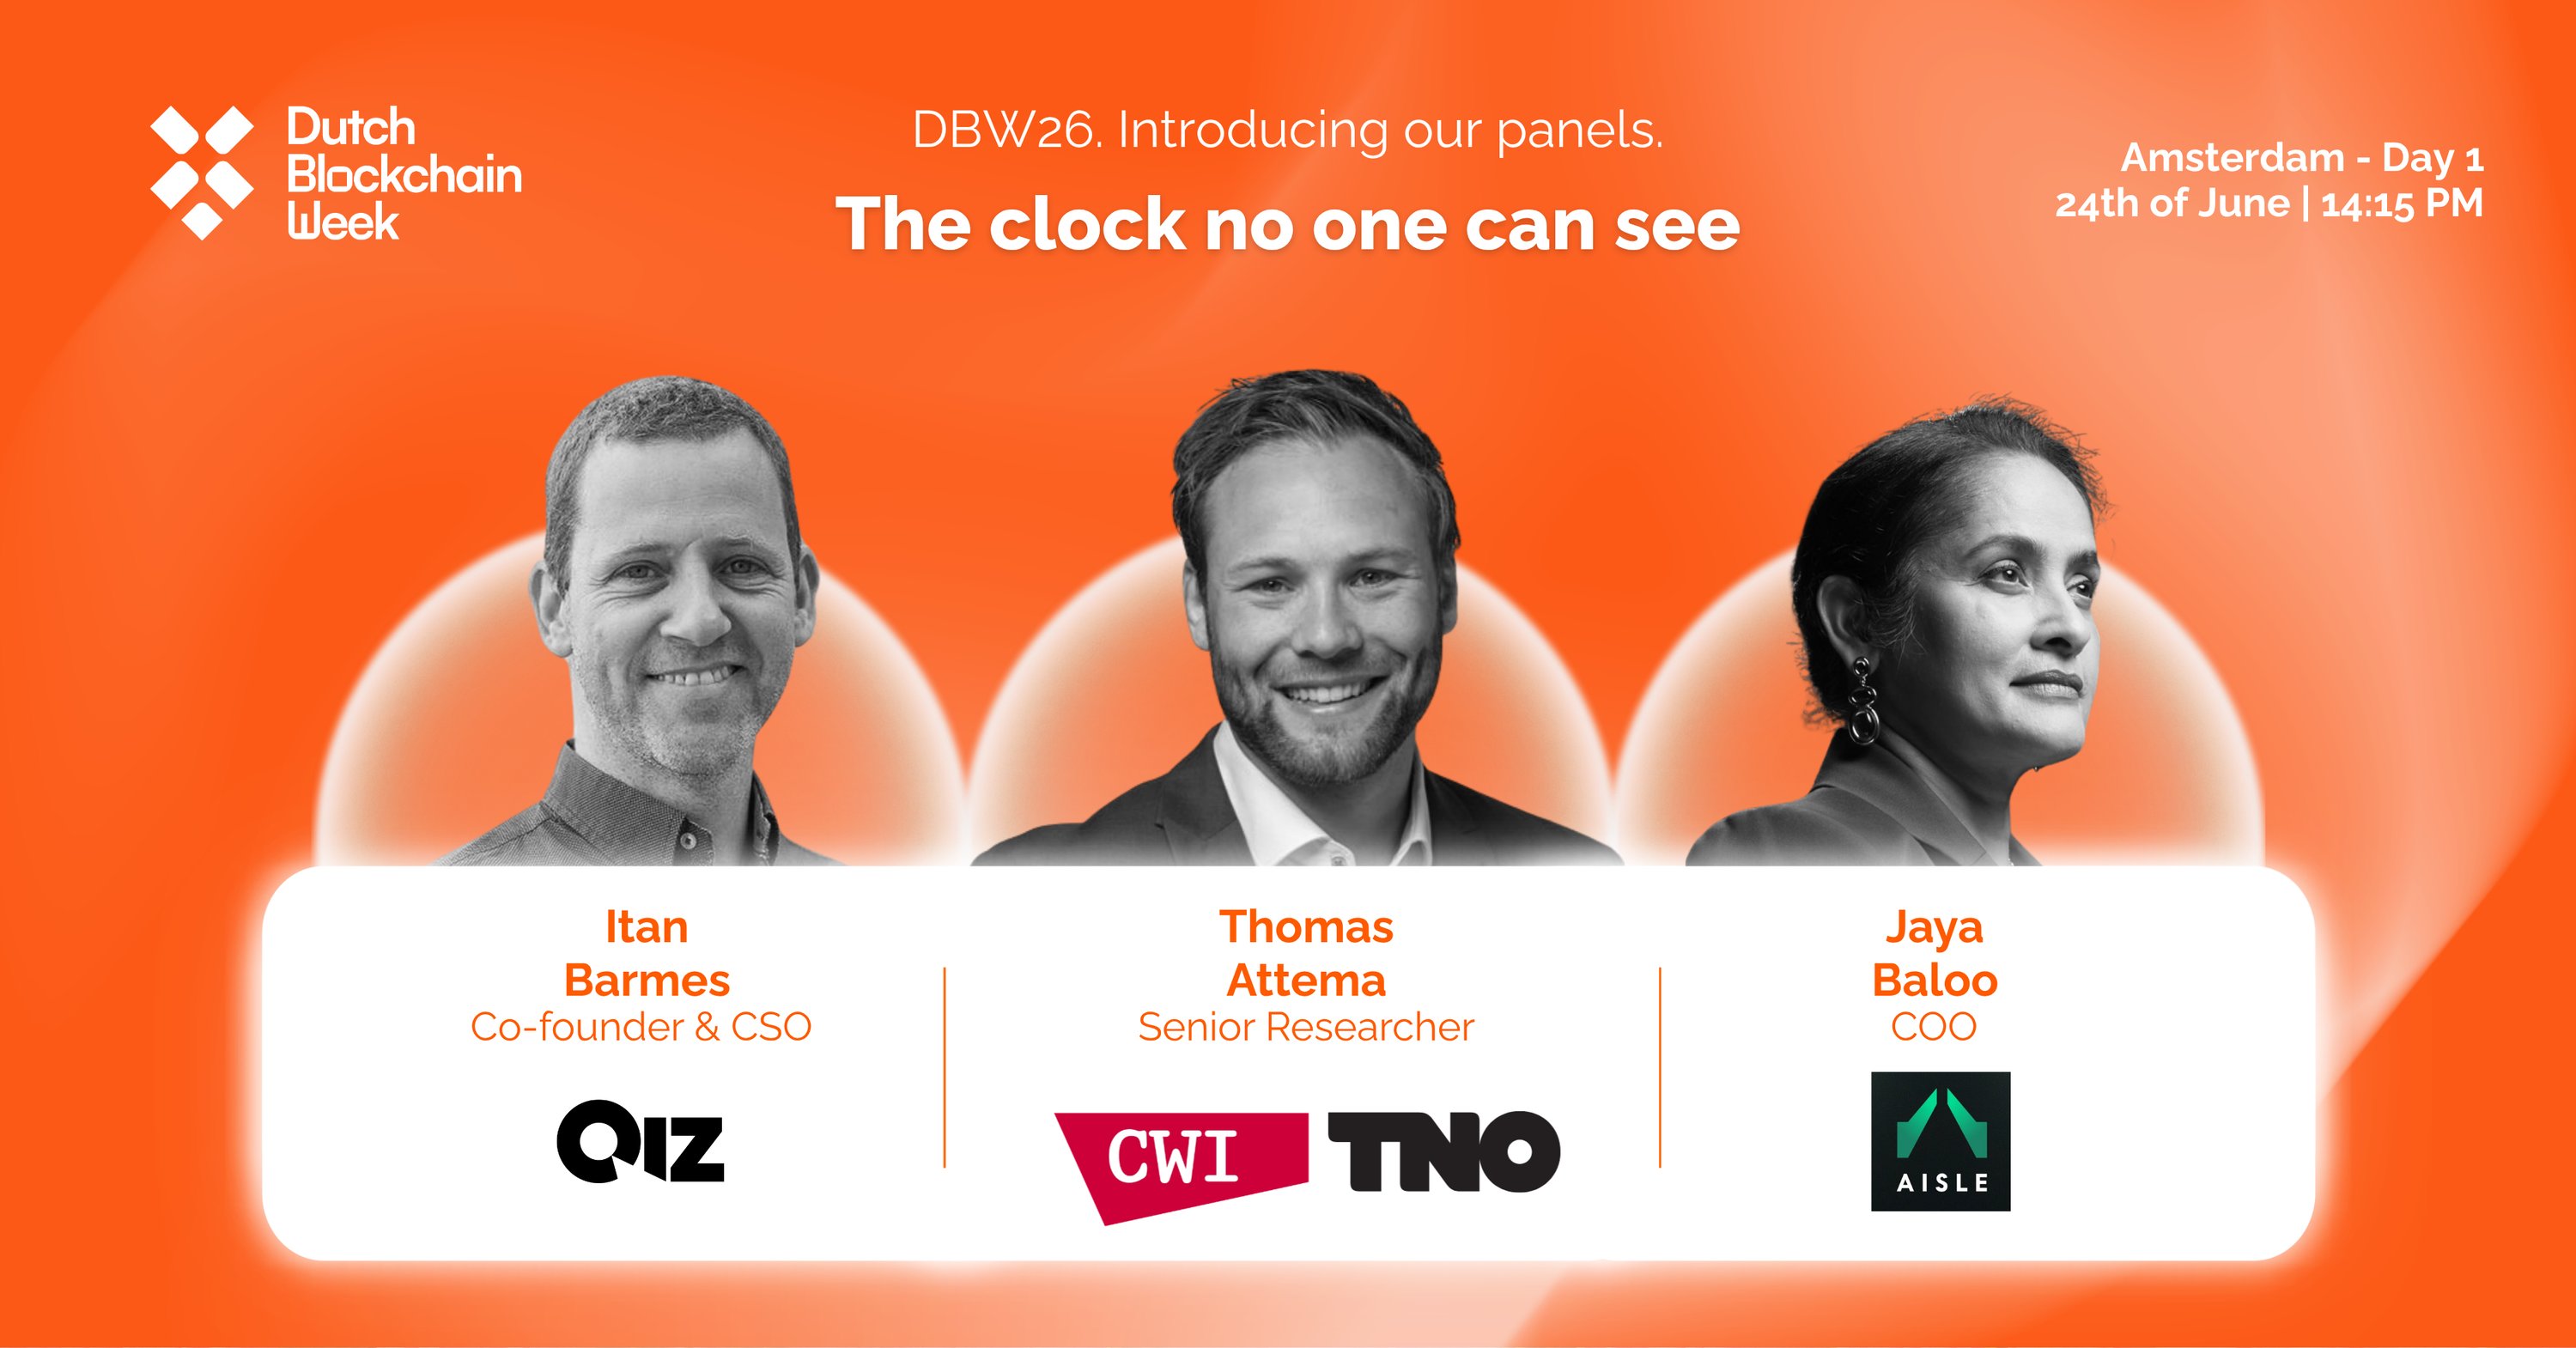
Day 1 panel: the clock no one can see.
What quantum computing means for the cryptography behind crypto. How close, what breaks first, what to do.
🔶 Thomas Attema, CWI and TNO
🔶 Itan Barmes, Qiz Security
🔶 Jaya Baloo (@jayabaloo), AISLE
June 24.
#DBW26 #DutchBlockchainWeek
Jaya Baloo retweeted
AISLE has discovered 20 of 23 OpenSSL zero-days (CVEs) across the last 3 consecutive security releases
Latest release: 5 of 7 are AISLE
1 was co-reported by Anthropic (Mythos?) 63 days after AISLE
OpenSSL encrypts 2/3 of the internet
10 fixes accepted straight into production

Jaya Baloo retweeted

Today's Thought: #Cybersecurity expert @jayabaloo emphasizes strong authentication, secure habits, and updated tools to combat rising threats like #hacking and #phishing. @sandy_carter @ivanastradner @secvalve @goldbe @DanniGBrooke - What do you think?
glamour.co.za/lifestyle/wome…

Jaya Baloo retweeted
New post: We show that small, cheap models can detect the flagship Mythos FreeBSD zero-day (CVE-2026-4747) using a simple harness we call nano-analyzer
Models down to 3.6B active params (including open-weights ones you can run locally) would have detected it 100-1000x cheaper

Jaya Baloo retweeted

Most "AI security" is just marketing fluff. @jayabaloo is actually building something different. We sat down at Beyond the Firewall to discuss identity, the expert's dilemma and why we need software craftsmanship. The full episode is here: tinyurl.com/5x2m2ms8
Jaya Baloo retweeted

🇨🇿 decacorn is coming? Watch Aisle by Ondrej Vlcek. One of the most impressive and ambitious pitches here. Good luck to the team! @stanislavfort @jayabaloo
