

Field CTO @sonatype. Software supply chain management, infosec and devsecops veteran, occasional speaker and dependency hell enthusiast. 🇬🇧 & 🇫🇮
London, England
Joined March 2011
- Tweets2.1K
- Following1.3K
- Followers586
- Likes2.2K




Ilkka Turunen retweeted

🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
Ilkka Turunen retweeted

Aufgrund der aktuellen PHP-Sicherheitslücke hat die Stadt München vorsorglich verschiedene Webseiten und Online-Dienste der Stadtverwaltung vorübergehend vom Netz genommen, bis die erforderlichen Sicherheits-Updates aufgespielt sind.
Ilkka Turunen retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Ilkka Turunen retweeted

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

This seems to be a culmination of the ongoing TeamPCP supply chain rampage

We are investigating unauthorized access to GitHub’s internal repositories. While we currently have no evidence of impact to customer information stored outside of GitHub’s internal repositories (such as our customers’ enterprises, organizations, and repositories), we are closely monitoring our infrastructure for follow-on activity.
3
120
Ilkka Turunen retweeted
Fake npm 2FA reset email led to compromise of popular code packages - helpnetsecurity.com/2025/09/… - @AikidoSecurity @CharlieEriksen @sonatype @llkkaT #npm #AccountHijacking #Cybersecurity

Ilkka Turunen retweeted

Incident Response for Recently Infected Lottie-Player versions 2.05, 2.06, 2.0.7
Comm Date/Time: Oct 31st, 2024 04:00 AM UTC
Incident: On October 30th ~6:20 PM UTC - LottieFiles were notified that our popular open source npm package for the web player @lottiefiles/lottie-player had unauthorized new versions pushed with malicious code. This does not impact our dotlottie player and/or SaaS services. Our incident response plans were activated as a result. We apologize for this inconvenience and are committed to ensuring safety and security of our users, customers, their end-users, developers, and our employees.
Immediate Mitigation Actions
- Published a new safe version (2.0.8)
- Unpublished the compromised package versions from npm
- Removed all access and associated tokens/services accounts of the impacted developer
Impact
- Versions 2.0.5, 2.0.6, 2.0.7 were published directly to npmjs.com over the course of an hour using a compromised access token from a developer with the required privileges.
- The unauthorized versions contained code that prompted for connecting to user’s crypto wallets.
- A large number of users using the library via third-party CDNs without a pinned version were automatically served the compromised version as the latest release. With the publishing of the safe version, those users would have automatically received the fix.
Recommended Steps
- If using 2.0.5, 2.0.6 and 2.0.7 versions please update to the latest version 2.0.8
-- SHA: sha512-PWfm8AFyrijfnvGc2pdu6avIrnC7UAjvvHqURNk0DS748/ilxRmYXGYkgdU1z/BIl3fbHCZJ89Zqjwg/9cx6NQ==
- If you are unable to update the player immediately, it is recommended that you communicate to Lottie-player end-users to NOT accept any attempts to connect their crypto wallets.
Next Steps
- LottieFiles continues to work through its incident response plan and has also engaged an external incident response team to help further investigate the compromise.
- We have confirmed that our other open source libraries, open source code, Github repositories, and our SaaS were not affected.
If you believe you’re affected, don’t hesitate to reach out to us at [email protected]
So many things happening today, including the CRA being adopted by the EU Council. Not long now till the starting gun is fired for implementation consilium.europa.eu/en/press…

1
103
It seems like the vulnerability affects cups, a printer driver found in linux and unix like systems. The good news is the attack only works if the attacker can connect via UDP on port 631. Also requires a print job to start evilsocket.net/2024/09/26/At…
Put it another way - not a huge deal. It's turned off in red hat for example. Good resource here redhat.com/en/blog/red-hat-r…

1
123


This was a great conversation about all the regulation coming up here in Europe

#ICYMI: You can stream the webcast on “Exploring the Future of Software Compliance” for an in-depth discussion on recent EU regulations including #NIS2, #DORA, and the #CyberResilienceAct with Jen Ellis, @alexbotting, and @llkkaT.
brighttalk.com/webcast/19417…
77


When it rains… also it’s likely they’ll see this incident as a blueprint for future campaigns

Cyber criminals quickly exploit CrowdStrike chaos dlvr.it/T9phPb

66
Ilkka Turunen retweeted

CrowdStrike is actively working with customers impacted by a defect found in a single content update for Windows hosts. Mac and Linux hosts are not impacted. This is not a security incident or cyberattack. The issue has been identified, isolated and a fix has been deployed. We refer customers to the support portal for the latest updates and will continue to provide complete and continuous updates on our website. We further recommend organizations ensure they’re communicating with CrowdStrike representatives through official channels. Our team is fully mobilized to ensure the security and stability of CrowdStrike customers.
Ilkka Turunen retweeted

My prays with the CrowdStrike engineers, but this is the best joke I have for this situation


Oof. This is a hairy patch to unpick

BREAKING… Everything: A massive IT outage has knocked hundreds of critical websites offline, including banks, airports and news sites - the bug has been blamed on a rogue Crowdstrike update that seems to have taken vast chunks of the internet down on Friday morning @TelegraphNews @Telegraph
1
105
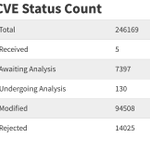
The NVD has stated it is getting new staffing and aims to clear the backlog by the end of the fiscal year (which would be September). Sceptical if that will indeed happen, but if so users of tools relying on it directly will have one busy summer with alerts nist.gov/itl/nvd