
@mainteemoforfun
Account based inMorocco
About this account
- Account based in
- Morocco
- Connected via
- United States App Store
Account-level information from X, not a live location or the device used for a specific post.
/goal hack the planet @Poneglyphsec
Wanou
Joined July 2017
- Tweets10.4K
- Following1.4K
- Followers3.2K
- Likes5.8K



VDPs are meant for do good when critical bugs exists you have the choice to use them or not but there are understaffed teams behind with families and life don’t use them as your benchmarks, there is cybergym and many many projects to test your harness against, and let us say you want to do anyway verify and triage manually you findings add video PoC, its a win win for you and for vdp, also you are not some superhuman because you built a harness that find clear xss and sql injections, people are hacking drones and being humble you are not THAT SPECIAL, do your job or whatever and don’t be a jerk

kids, just fire those codex sessions and use /goal

That didn’t take long: the model swallows the harness.
arxiv.org/abs/2609.35738


let's say LLM only focused on features involving authentication and digged into one specific path because of lead that only got him into a false positive or assumption ...
all those are cross tenant attacks, and one thing in common is I use codex or claude with those:
deepseek 4.1
Opus 4.8
Daybreak
yeah hackbots are good but as entreprise and get contracts, best hunters I know using folders, Prompts, skills, integrated with their DBs of either assets or bugs or novel research


trial retweeted

" I built GeoInt " is misleading. The correct and honest story: "I took geo-sleuth and plugged in existing models"..
Nothing wrong with using MIT licensed code just give credit where it’s due.
Still good start working on real projects beats your usual AI mikiyate 🤭

I built GeoInt, an open-source skill for Codex and Claude Code that finds where any photo was taken, with proof.
It reads every detail in the image, like signs, plates, buildings, plants and the light. It searches several reverse image engines, runs multiple vision models on your own machine, compares your photo with Street View panoramas, and weighs every clue on an evidence board.
Then it gives you coordinates, a confidence level, and the sources behind the answer.
There are companies selling tools like this to police departments. GeoInt is completely free, and honestly, I think it's better than theirs.
People defending this don’t know terms and conditions they accept before submitting a report, if you intend to play the vigilante just don’t do bug bounties, playing the double sides is bit hypocritical


trial retweeted

Made over $25K hacking marketplace app permission issues across various bug bounty programs.
Here's my latest writeup on how a malicious app might take over a GitHub repository: jeetbhdr.github.io/github-gr…
#bugbounty

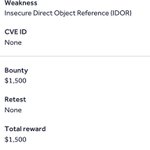
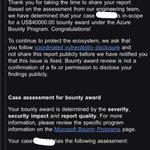
Microsoft’s finding wasn’t my only hit for managed db bugs using AI
poneglyph.cloud/research/man…
And I know its full of em dashes (i wrote initial draft and AI rewrote later)
Besides this managed runtimes/dbs are a good area of research 1/n

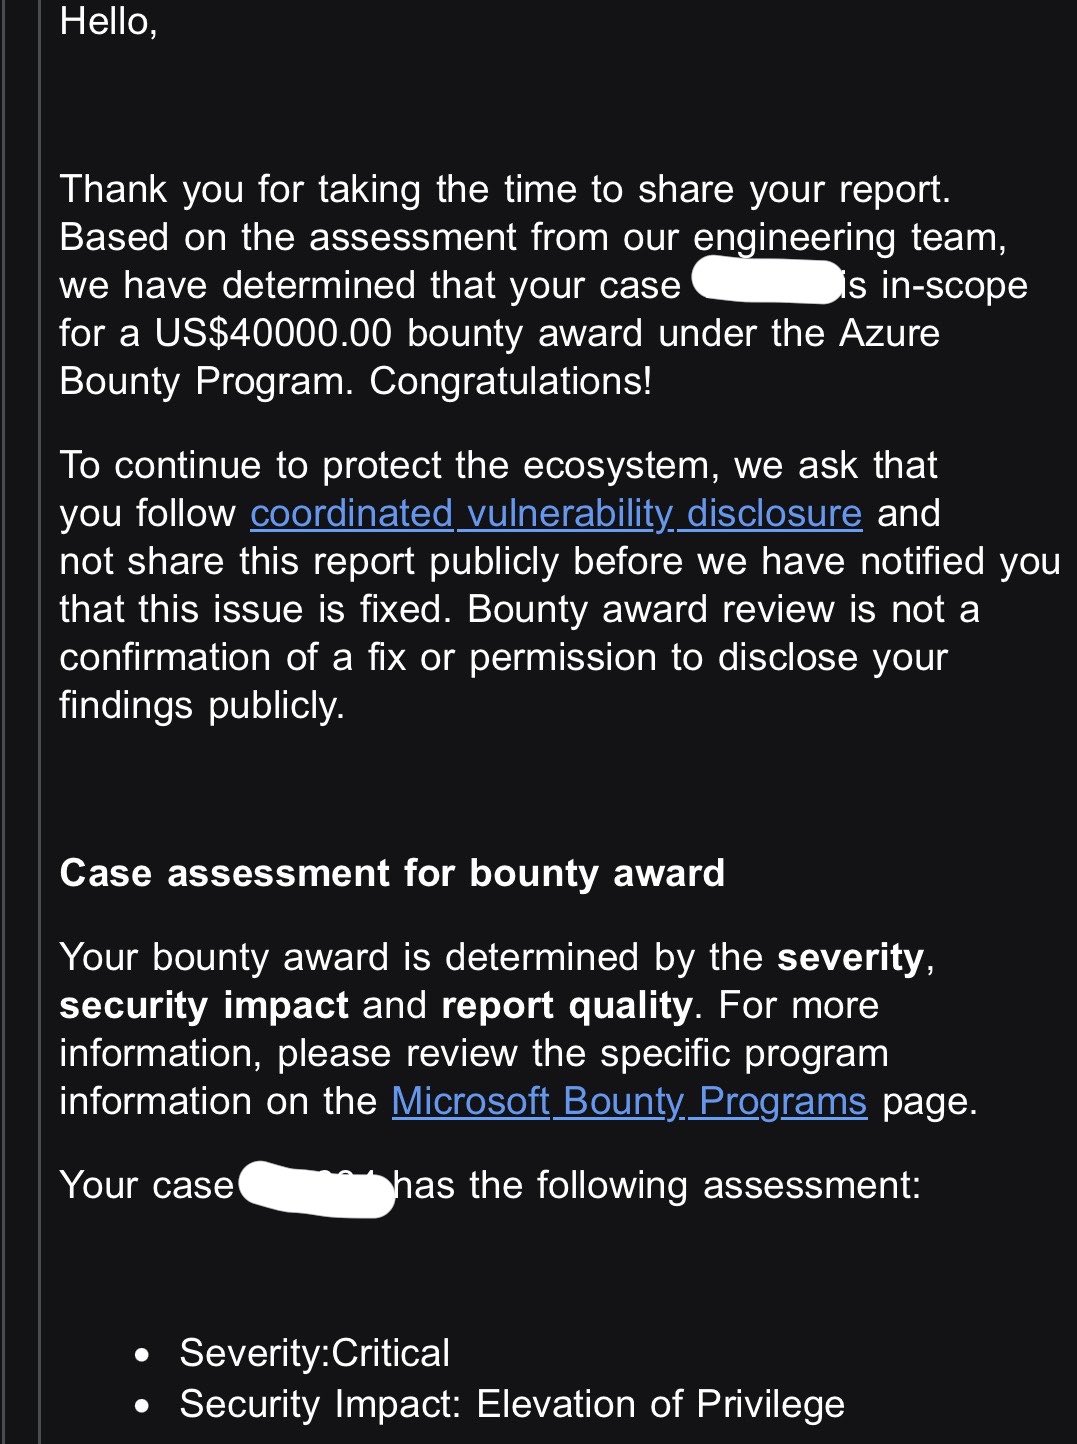
Also, and due to the fact that most of the times its shared instead of dedicated hardware, you can find different kind of cross tenants issues, and most of them are logical, doesn’t require you fuzzing the engine, that’s exactly what I am trying to build at @Poneglyphsec 1/n
I want to reach this kind of power as muslim except i don’t like communism

This day is profoundly painful for so many New Yorkers. It marks three years since the horrific war crimes of October 7. On that day, Hamas killed more than 1,100 Israelis and abducted 251 others. We grieve alongside our many friends and neighbors who still carry that unthinkable loss.
The suffering did not begin nor end that day. It instead continued through the Israeli government’s devastating, ongoing genocide in Gaza, in which it has killed more than 74,000 Palestinians—including more than 21,000 children. Even since the so-called ceasefire, more than 1,400 Palestinians have been killed. That suffering has intensified with every Israeli bomb dropped on ambulances waiting outside hospitals, every drone strike targeting a residential building or journalist, and every shipment of food aid turned away at a border crossing. Many New Yorkers are reckoning with this unbearable grief, and we mourn alongside them – all while knowing that our tax dollars fund these war crimes.
Three years later, we must refuse to accept a world in which occupation and apartheid continue, where war crimes are met with impunity, and our federal government continues its complicity with every arms shipment.
To honor the dead, we must fight for a world in which every person can live with freedom, safety, and dignity.
