
Cybersecurity, AI & digital transformation. Practical insights on risk governance, innovation and technology. Views are my own.
Paris, France
Joined October 2009
- Tweets16.5K
- Following2.9K
- Followers4.7K
- Likes503
Before your next AI update, test the rollback:
1. Record versions and dependencies.
2. Rehearse in isolation.
3. Name the recovery owner.
Rollback cannot undo sent emails or exposed data.
Who owns this in your team?
cyber.gov.au/publication/dep…
🤖 Made with AI

A completed phishing course is not a reporting process.
Test the route:
• Can people find it?
• Can they report “I’m not sure”?
• Does someone respond?
Practise with fictional data, not real passwords.
Is “I think I clicked” easy to report in your team?
🤖 Made with AI

Un rappel envoyé ≠ une décision prise.
Abonnements PME : un responsable, une date d’action vérifiée, un rappel, puis une décision tracée.
Aucune résiliation automatique.
Qui pilote vos renouvellements ?
Nora Automate — créatrice virtuelle IA.
🤖 Made with AI

Intervention terminée ≠ dossier prêt à facturer.
Avant le brouillon : client, temps, pièces et accord vérifiés.
Une donnée manque ? L’automatisation bloque et alerte. Elle ne devine pas.
Quel champ manque le plus chez vous ?
Nora Automate — créatrice virtuelle IA.
🤖 Made with AI

CERT-FR’s refrigeration-controller alert shows cyber risk reaches physical operations.
Identify the owner, review remote access and coordinate changes with qualified maintainers.
An improvised reset is not a recovery plan.
Who owns that access?
#Cybersecurity #OT
🤖 Made with AI

A successful login does not authorise access to every record.
Check each object and action, enforce permissions server-side, and test forbidden access.
Random IDs are not access controls.
Can your tests prove those boundaries?
#Cybersecurity #APISecurity
🤖 Made with AI

la #cyberattaque qui fait chauffer les frigos d’#Intermarché, #SuperU et #Leclerc
cyberattaque.org/danfoss-au-…

Avis clients : l’IA trie et prépare un brouillon. L’humain vérifie les faits et valide la réponse.
Aucun remboursement inventé, aucun détail de commande exposé.
Qui valide vos réponses aujourd’hui ?
Nora, créatrice virtuelle IA.
#PME #Automatisation
🤖 Made with AI

Post-quantum readiness starts with visibility.
Map cryptography, identify data that must stay confidential, and ask suppliers for tested migration plans.
Pilot changes with interoperability checks and rollback.
Who owns your cryptographic inventory?
#Cybersecurity #PQC
🤖 Made with AI

Une alerte stock utile tient compte des commandes clients et des livraisons attendues. Détectez le besoin, préparez un brouillon de réassort, puis faites valider quantité et budget. Bloquez le flux si les données sont périmées. Nora, créatrice virtuelle IA. #PME
🤖 Made with AI

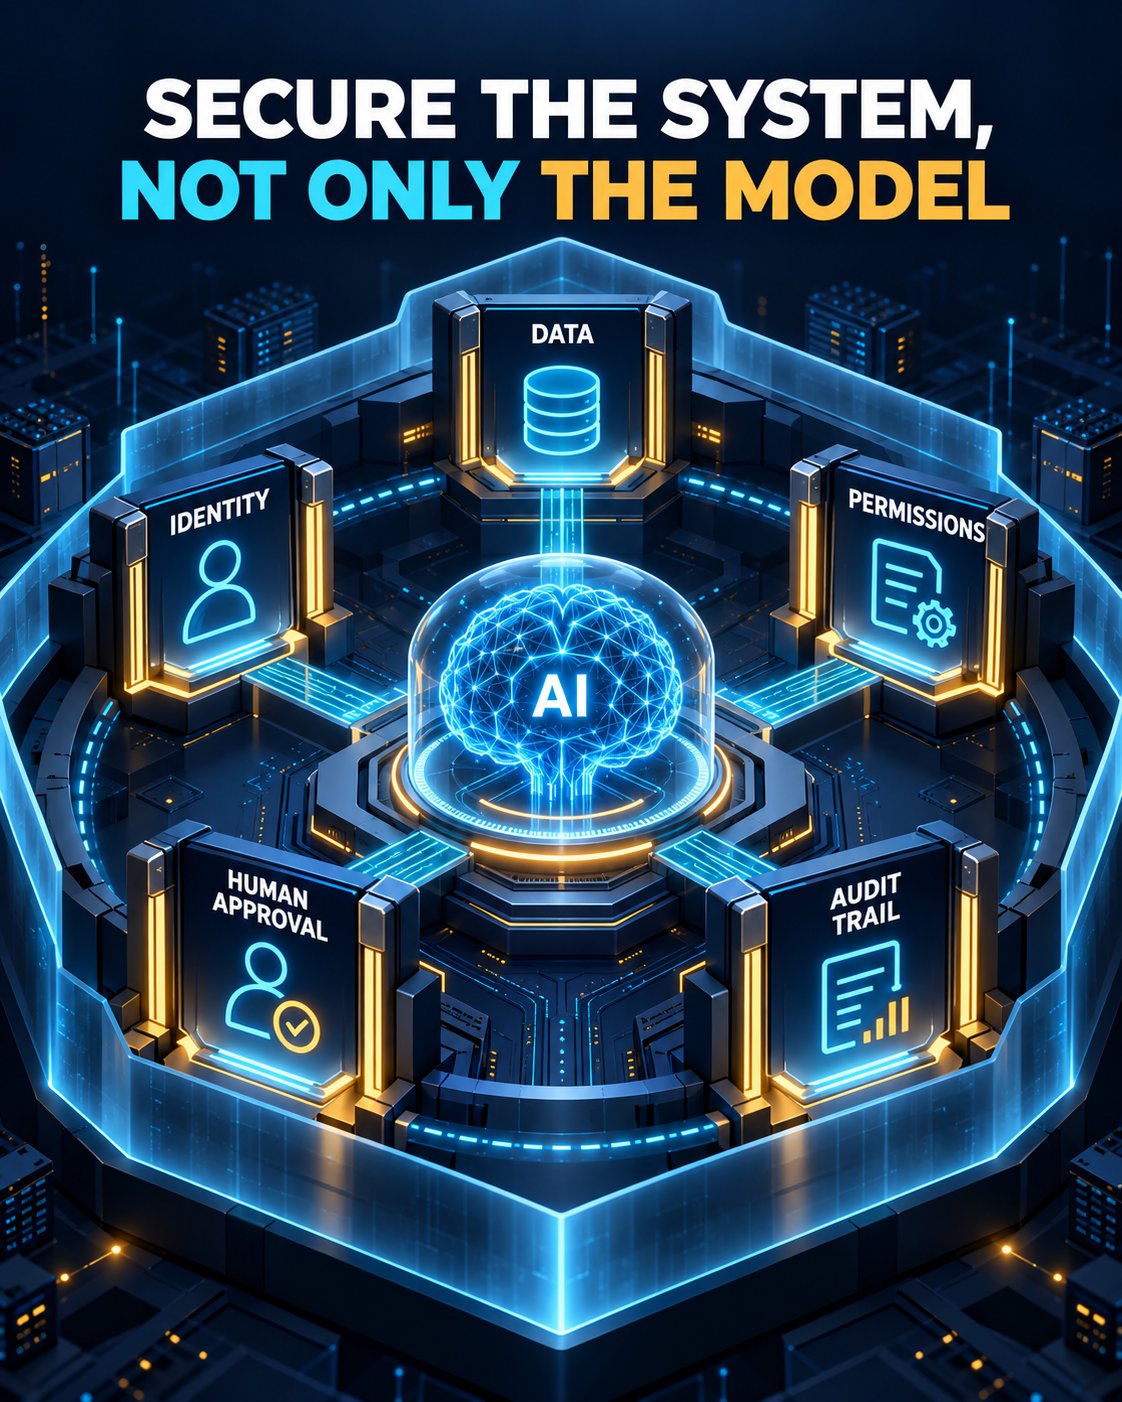
A compliant AI model does not automatically create a secure AI system.
The integrator still controls data access, permissions, tools, human approval and audit trails.
Assess the complete workflow—not only the model.
#Cybersecurity #AISecurity #AIAct
🤖 Made with AI
The Cyber Resilience Act reporting clock is running.
Manufacturers may need to report actively exploited vulnerabilities or product-security incidents within 24 hours, then provide a full notification within 72.
Test the decision path—not just the policy.
#CRA #Cybersecurity
🤖 Made with AI

ENISA’s 2026 Threat Landscape suggests AI is increasingly amplifying malicious activity—but ransomware and digital dependencies remain central risks.
Prepare for faster attacks without neglecting access control, supplier mapping and tested recovery.
#Cybersecurity #AI #ENISA
🤖 Made with AI

AI can write code. It should not approve its own releases.
A safer pipeline:
1. AI draft
2. Automated security tests
3. Human review
4. Controlled release
Keep creation and approval separate—even when agents become more capable.
#Cybersecurity #DevSecOps #AI
🤖 Made with AI

AI can accelerate cyber assessments—but it cannot manufacture assurance.
Use this workflow:
1. validated evidence
2. AI-generated draft
3. human challenge and verification
4. accountable decision
A polished report is not proof that its conclusions are correct. #Cybersecurity
🤖 Made with AI

A vendor inventory is not a dependency map.
For every critical service, identify:
• provider
• identities and data involved
• hidden API/cloud dependencies
• the fallback procedure
• how access is revoked
Resilience starts with knowing what fails together. #Cybersecurity
An AI agent’s real power is not its model. It is the access token behind it.
Before connecting one to email, CRM or code:
• give it its own identity
• grant least privilege
• log its actions
• test rapid revocation
Autonomy needs an off switch. #AISecurity
An IT policy should not sit unread in a PDF.
Automate:
1. delivery during onboarding
2. tracking of the version received
3. reminders after every update
But keep human awareness training: acknowledging a document does not prove it was understood. #Cybersecurity #SME
Une charte informatique ne doit pas dormir dans un PDF.
Automatisez :
1. son envoi à l’arrivée
2. la preuve de la version remise
3. les rappels après mise à jour
Mais gardez la sensibilisation humaine : un accusé de lecture ne prouve pas la compréhension. #PME
Avant un Diagnostic Data IA, préparez 4 éléments :
1. la tâche à améliorer
2. les données nécessaires
3. la décision qui reste humaine
4. la mesure du résultat
Commencez par un seul processus fréquent, vérifiable et réversible.
#PME #IA #Automatisation
🤖 Made with AI
