






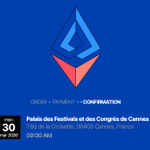


Looks like dates of ETHDenver have been announced ethdenver.com/

Ken Smith retweeted

EVA Symposium III is tomorrow, November 4, in Mumbai.
@jdetychey and @Pol_Lanski join The Great Issuance Debate, hosted by @0xzak.
📍 Event location
Grand Salon Grand Hyatt Mumbai Hotel & Residences Vakola, Mumbai
If you’re coming directly, head to the Grand Hyatt Mumbai and ask for the Grand Salon.
🚌 Shuttle from Devcon
Buses will line up between 4:15 and 4:45 PM at Gate 20 of the Jio World Convention Center (JWCC).
Look for the team holding EVA signs. The shuttle will take you to the Grand Hyatt Mumbai. Return shuttles are also provided.
🕔 Evening schedule
5 PM — Doors open, high tea and refreshments 6–8 PM — Symposium program 8–11 PM — Dinner and networking
All times are Mumbai local time, IST.
Attendance requires approved registration. We’re at capacity, but the waitlist is open.
luma.com/ai6owvhz

I caught a great talk by @d_gusakov on EIP-8148 at Devcon. I highly recommend all home and solo stakers check out eip8148.com/

Ken Smith retweeted

Staking with a decentralised protocol that has a diverse and fully permissionless node operator set means you don’t need to trust any people or companies with your ETH
Rocket Pool is still the only fully permissionless staking protocol
I've spent some time drawing an infographic, "The Anatomy of the Ethereum Block."
Updated in Mumbai ahead of Devcon. PDF attached👇.
Looking at it, I'm growing alarmed by how much isn't post-quantum.

BLS signatures, KZG, and secp256k1 are not post-quantum. They break when a relevant quantum computer exists. Hash roots resist Shor's algorithm. Grover only weakens a 256-bit hash.
If we already know the replacements, I wonder if I* is too late. Should Hegotá be the post-quantum fork, and should the list now considered for inclusion in Hegotá move to I*?
Ken Smith retweeted
Should Ethereum reduce issuance?
How much should the network pay for security? and who keeps staking when rewards fall?
Introducing The Great Issuance Debate at EVA Symposium III hosted by @0xzak.
November 4 · Mumbai · during @EFDevcon
Validators, researchers and staking operators. All in one room.

Ken Smith retweeted

Devcon is where you test the hard questions with the people who rely on the answers. For us, it’s also the best place to talk directly to everyone who runs the Nethermind Client.
Meet Nethermind @EFDevcon in Mumbai - booth on Level 3.
Our talks:
- Ben Adams: Could Ethereum support a billion validators, from phones to home devices?
- Lin Oshitani: Can an AI agent running in secure hardware act as an oracle, so a smart contract can verify where every answer came from?
- Eric Marti Haynes: Can tokenized assets be decentralized?
- Tomasz Stańczak with two talks about robotics and Ethereum.
All talks and our team at Devcon: nethermind.io/nethermind-at-…

Ken Smith retweeted

Mumbai, let’s build! 🦊🔥
Excited for @MetaMask Builder Nights – Agentic Edition on Nov 3, alongside @monad, @arkivnetwork, @ensdomains, @strato_net & @ConsensysAudits.
AI agents, onchain innovation & builder vibes during Devcon week!
luma.com/bnmumbai26

Ken Smith retweeted

1/ The Devcon 8 schedule is officially LIVE!
And the Devcon App is here in Early Access. 📱
Explore sessions, discover speakers, build your schedule with Interests, and keep your ticket handy, even offline.
Mumbai is almost here. Start planning your experience!
Ken Smith retweeted

anyone looking for more information on the issues that delayed the glamsterdam fork on hoodi can find details here:

⚠️ It has just been decided to delay the Glamsterdam hard fork on the Hoodi testnet because of security impacts we identified in this blog post: chainsecurity.com/blog/glams…
We already found 13 real-world examples and are in responsible disclosure with the affected projects.
Please check your contracts as soon as possible, as the EF is determining how many contracts are impacted in which way.
Feel free to reach out to us with questions via [email protected].


Ken Smith retweeted

ROCKET POOL VOTERS BACK $rETH WITHDRAWALS
@Rocket_Pool's proposed queue would let holders recover $ETH through validator exits when liquidity runs short. The full Saturn 2 package still needs ratification.
Read more here:
thedefiant.io/news/defi/rock…

Ken Smith retweeted
EVA Symposium III is coming to Mumbai 🇮🇳
During Devcon, we're bringing together Ethereum validators, staking operators, and researchers for candid conversations about the future of Ethereum. With @0xzak as our emcee.
Previous attendees and speakers have included Ethereum Foundation, Lido, Bitcoin Suisse, and many other individual and institutional stakers.
Special thanks to @ethcforg for helping us coordinate this event.
Request your spot below.

Ken Smith retweeted

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
Ken Smith retweeted

Formal verification of Aztec’s cryptography is underway.
We've completed formal verification of major components of our proving system & our workflow for formally verifying the Aztec stack is quickly accelerating.
Stay tuned for more updates with the upcoming Alpha V6 release

Ken Smith retweeted
Glamsterdam changes how Ethereum scales. Sepolia on October 6, then Hoodi and mainnet. Let’s go!
blog.ethereum.org/2026/09/17…

Ken Smith retweeted

What we're cooking for the tenth anniversary is bigger than a conference or a festival. It stays weird, it's built around the core of Ethereum, and we'll share it in October.
Please DO NOT buy tickets from sites advertising ETHDenver 27. ETHDenver is, and always will be, free.
🤖 Made with AI
