

cipher security labs https://nitter.cf/t.co/IZByfO2Dr4
🇪🇺🇮🇱
Joined October 2016
- Tweets8.5K
- Following697
- Followers1.1K
- Likes4.2K




Nir Yehoshua retweeted

He slept with some women, who cares? He built the largest company in the world, is what he did! He was a brave Taiwanese engineer, and in this house, Jensen Huang is a hero. End of story!

Nir Yehoshua retweeted

heard in Silicon Valley:
Security researchers will soon make more than AI researchers.
Polymarket users were drained again on October 29. Nothing public points to a smart contract bug. This was a client-side supply-chain attack through a third-party script.
The vector
A DebugBear Real User Monitoring (RUM) script, loaded on Polymarket's international site for page-performance metrics, carried wallet-draining code written specifically against Polymarket's frontend (Hudson Rock). The script was served from DebugBear's CDN, a host Polymarket's CSP allowed (WhoGetsMyData scan, cited by Hudson Rock). CSP trusts a hostname, not bytes: once the bytes behind that host changed, the payload ran with full page privilege inside authenticated sessions.
DebugBear, 18:00 UTC: "We're impacted by an ongoing security incident. If you use our RUM product, please remove the embed code from your website." Polymarket referred only to a "3rd party provider". DebugBear was named by a source to CNBC and in Polymarket's build metadata.
Payload (Hudson Rock capture)
cdn.debugbear[.]com/C7xcKKrjUnXK.js
15,187 bytes
SHA-256: 0755e767504d8103f6c27b9e765a1026507a17c04513242adb503df7777879e5
Hard-coded fallback recipient: 0x3F99139F1C5854bb628c2e576Aaf638e99dFfc18 (remote config could select another)
Stage 1: session reuse, not key theft
The script reads polymarket.auth.params, polymarket.auth.proxyWallet and poly_clob_api_key_map from localStorage and branches on eoa vs magic wallets. No seed phrase is needed. It reuses the authority already living in the page.
Stage 2: hijack the app, not the RPC
It walks React internals (component props and hook state) for an object exposing postOrder and createOrder or createMarketOrder, then attempts to drive it together with its signer. This is purpose-built tooling against Polymarket's client, not a generic drainer.
Stage 3: liquidate, then sweep
Per Hudson Rock's static analysis: SELL orders at increasingly aggressive prices, or an ERC-1155 batch transfer of position tokens. Then EIP-712 DepositWallet batches, signed through the page's own signer and submitted to Polymarket's relayer. Then swaps.
On-chain
The payout address received USDC.e to POL swaps via Relay (Arkham, per Decrypt) and peaked at about 28.64M POL (roughly $2.6M) around 18:10 UTC. Between 18:28 and 18:38 UTC it moved about 28.6M POL out in three transfers. Signed DepositWallet batches are a normal Polymarket flow, so on-chain the drains can look user-authorized. The $2.6M figure is the wallet's peak balance, not a confirmed total loss.
Timeline, Oct 29 (UTC)
17:10 first POL reaches the payout address
17:59 Polymarket build removing DebugBear RUM (#15337)
18:00 DebugBear discloses
18:05 cancel-only mode, relayer paused
18:33 Polymarket: provider compromised, law enforcement contacted, impacted users "will be made whole"
19:00 trading fully back online
Per CNBC, the US platform was not compromised and the case went to UK law enforcement. Open questions: victim count, exposure window, and how DebugBear itself was breached.
Pattern
June: same class, a compromised vendor script, about $3M from fewer than 15 accounts. May: a different layer, a compromised key on an internal top-up wallet, about $700k.
The contracts were not the way in. The browser was.
277
Nir Yehoshua retweeted

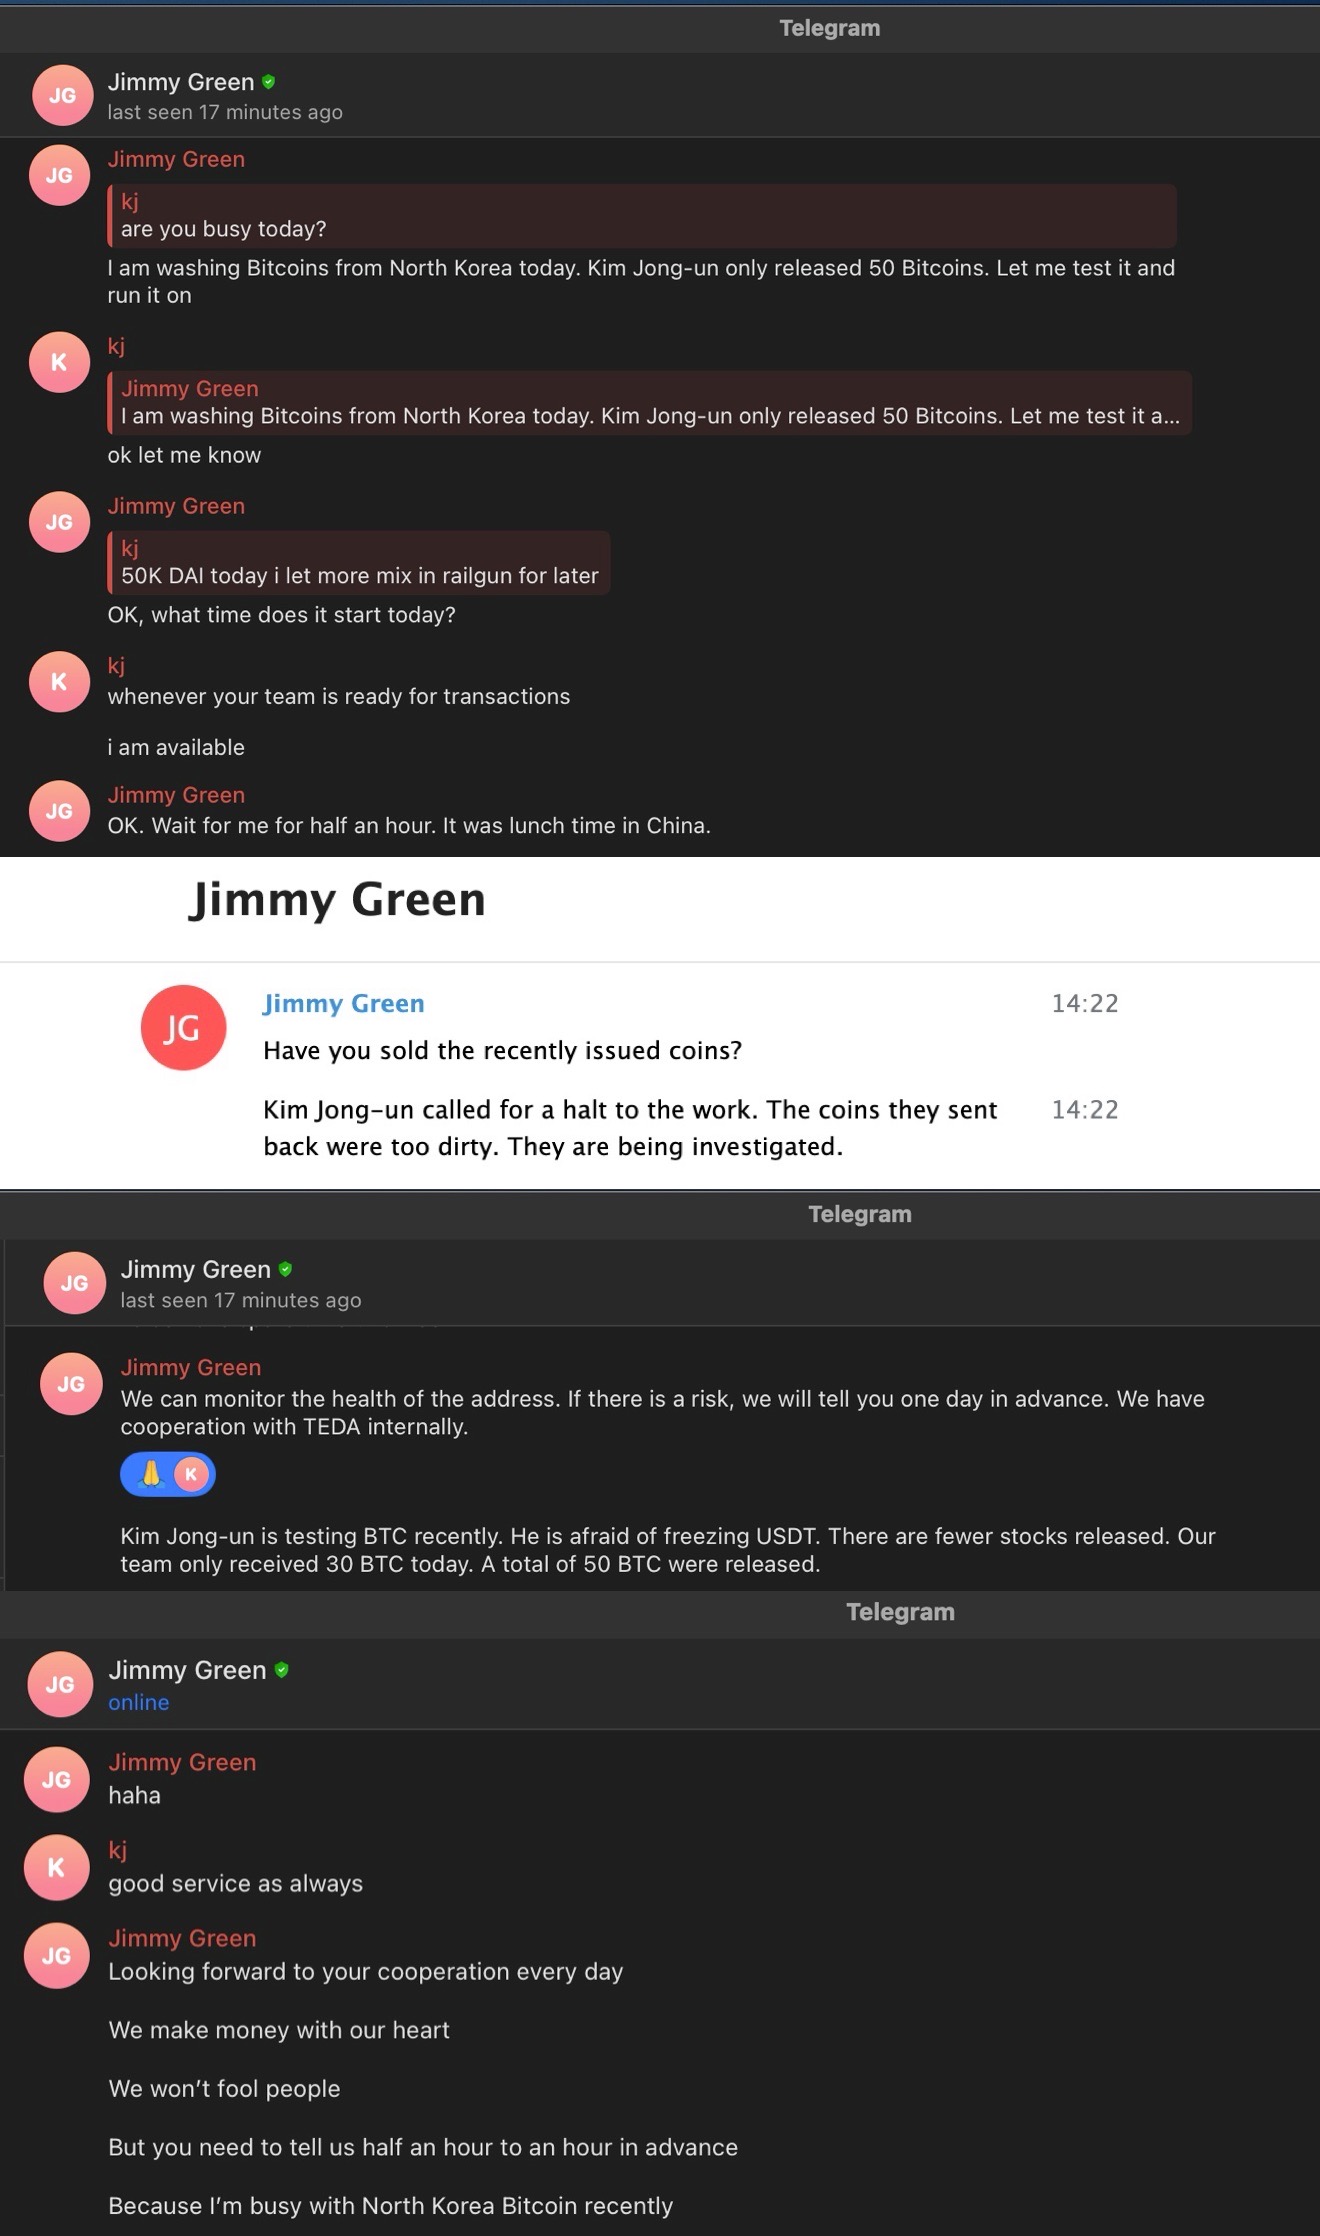
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.



Nir Yehoshua retweeted

Claude has discovered a previously unknown enzyme system hidden in the DNA of bacteriophages. Beside the enzyme’s gene sits a long array of repeating DNA—a structure that looks somewhat similar to CRISPR.
We don’t yet understand what this system does, but only a handful of known systems share its features, and all of them are able to cut, copy, and paste DNA. Historically, the discovery of such programmable systems has helped revolutionize medicine. CRISPR, for instance, is now the foundation of genetic medicines. But it will take much more work to learn what this system does, and whether it can be put to similar use.
Read more: anthropic.com/news/claude-di…


Nir Yehoshua retweeted

🚨 BGP Hijack at 2026-09-20 10:04 UTC
🇮🇷AS197207 (MCCI-AS) announced 190 prefixes, creating 10,865 conflicts with 1,524 ASNs in 100🌏.
🌏Max propagation: 100%
⏱️Duration: 8 min (first part) and 15 min (second part)


Nir Yehoshua retweeted

636606729769440499166579950236036751749912014371509557713570027508971809534551913252252094954941974952859310861988904737359709200557919
is a factor of RSA-896
saweis.net/posts/rsa-896.htm…
Nir Yehoshua retweeted

BREAKING: 🇺🇸 Warren Buffett steps down as Berkshire Hathaway Chairman after more than 60 years at the company.
Berkshire has returned 6,642,000% since 1964, nearly 120x the S&P 500 returns.


Nir Yehoshua retweeted

BREAKING: OpenAI reveals a 10,000-agent AI swarm solved the Navier–Stokes problem in 88 hours, using 130 billion output tokens to crack one of mathematics’ most famous unsolved problems.
Nir Yehoshua retweeted

We’re sharing a solution to the Navier-Stokes Millennium Prize Problem, one of the deepest problems at the frontier of mathematics.
The proof was produced by a group of agents, using an OpenAI next-generation model significantly more capable than GPT-6 Astra.
The problem concerns whether the description of smooth three-dimensional fluid motion modeled by the Navier-Stokes equations can break down. It has remained unresolved for roughly 90 years.

Nir Yehoshua retweeted

We at RefineSec already do it - Adaptive Mutated Attacks while producing behavioral detection rules natively for EDR / XDR solutions for attacks that were not prevented.
Feel free to visit our website and schedule a demo: refinesec.com

Nir Yehoshua retweeted
SOC Analyst Professional - Attack & Defense is officially LIVE. 🔥
I built this course around one rule:
Do not just learn the attack. Execute it. Investigate it. Detect it. Tune the detection. Then try to bypass your own rule and write a better one.
Every technique follows the same hands-on workflow:
ATTACK → TELEMETRY → INVESTIGATION → DETECTION → TUNING → VALIDATION → BYPASS → BETTER DETECTION!
We go hands-on with:
RDP
PsExec
WinRM
Active Directory discovery
PowerShell and LoLBins
WMI
Registry persistence
Scheduled Tasks
Services
Credential dumping
LSASS access
Privilege escalation
Process injection
Ransomware-style activity
and much more.
Then you investigate the evidence across Windows Event Logs, Sysmon and Elastic Security EDR, and build the Elastic Security KQL detection rules yourself.
I do not want you to finish a PsExec lab knowing only that PsExec.exe exists.
I want you to understand what it drops on the target, what service it creates, what executes, what telemetry Elastic Defend collects, how to detect the behavior, and how that detection could be bypassed.
Because a rule that only catches the exact command you used in the lab is not a detection I would trust.
🔥 SOC Analyst Professional - Attack & Defense is live now:
trainsec.net/courses/soc-ana…
Stop memorizing attacks. Start owning the detections that catch them.

Nir Yehoshua retweeted
🚨 Two CVEs. One router. One complete chain to ROOT.
Last week, we disclosed two vulnerabilities affecting the Cudy WR3000 2.0:
🔴 CVE-2026-71960 - Authentication Bypass
CVSS v4.0: 9.3 Critical
🟠 CVE-2026-71961 - OS Command Injection
CVSS v4.0: 8.7 High
Individually, they are serious.
Chained together, the story changes completely.
1/ During our firmware research, we recovered signing material that could be used to forge a valid JWT.
That means bypassing the authentication boundary, accessing the MQTT interface, and reaching a vulnerable command path.
The end result?
Operating system command execution as root.
2/ This is exactly why I keep saying:
Stop looking at vulnerabilities only as isolated CVEs.
Attackers don't think in CVSS tables.
They look for chains.
One weakness opens the door.
Another one gives you the keys.
And suddenly, something that looked "limited" becomes a complete compromise.
3/ Then things became even more interesting.
Shortly after our disclosure, Hunt & Benito independently released public exploit tooling reproducing the attack chain.
Important clarification:
We did NOT create, commission, or contribute to that exploit.
But once public tooling exists, the barrier to reproducing the attack drops dramatically.
And the research entered a second wave of international coverage.
4/ Our findings were covered by:
SecurityBrief - original disclosure
lnkd.in/de6YFUF7
SecurityBrief - public exploit follow-up
lnkd.in/d6hx8c-h
HackRead
lnkd.in/eUBGwjzZ
SecNews
lnkd.in/d3xpfPiv
BugsToday
lnkd.in/dbend8WA
5/ For me, the most important takeaway isn't the headlines.
It's the technical lesson:
Security boundaries rarely fail in isolation.
Authentication bypass alone tells one story.
Command injection alone tells another.
But connect them together and you get:
Firmware -> signing material -> forged JWT -> MQTT access -> command injection -> ROOT
That is the attack path that actually matters.
6/ This is the kind of research we want to push at Cipher Security Labs:
Deep vulnerability research
Full attack-chain analysis
Understanding how weaknesses interact
Product security
Coordinated vulnerability disclosure
Not just:
"Here is a CVE."
But:
"Here is what an attacker can actually do with it."
More research coming.
Our CVE Tracker:
ciphersecuritylabs.com/CVE-T…
#CyberSecurity #VulnerabilityResearch #CVE #IoTSecurity #ProductSecurity #FirmwareSecurity #SecurityResearch #InfoSec
Nir Yehoshua retweeted

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability

By Cipher Security Labs @UrielKosayev

Public exploit code can chain two #Cudy WR3000 v2 flaws to bypass login checks and allow full control when the router’s control service is reachable. Update to firmware 2.5.24 or later.
Listen to the article or read: hackread.com/cudy-wr3000-rou…
#CyberSecurity #Router #Vulnerability
1
1
338
New vulnerability disclosure from Cipher Security Labs.
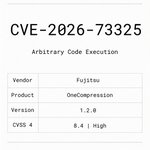
CVE-2026-73325 affects Fujitsu OneCompression 1.2.0 and can lead to arbitrary code execution.
Severity: CVSS 4.0 - 8.4 High
Looking for security research that goes beyond standard testing? We help organizations uncover high-impact vulnerabilities before attackers do.
Track our CVEs: ciphersecuritylabs.com/CVE-T…

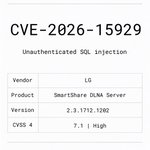
New CVE from Cipher Security Labs: CVE-2026-15929, an unauthenticated SQL injection in LG SmartShare DLNA Server v2.3.1712.1202. CVSS v4.0: 7.1 (High).
Track our CVEs: ciphersecuritylabs.com/CVE-T…
