

Christian. Husband. Father. Bug Bounty Hunter.
Joined February 2016
- Tweets338
- Following246
- Followers687
- Likes1.5K


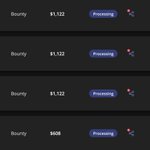


I am feeling fortunate and grateful.
This is my best month in bug bounty.
Thank you, @intigriti

Self closed this one.
I was able to escalate it to ATO but the program thought the delivery was unrealistic. I agree.
Cool gadget, may use it later.

Tip: Indirect prompt injection to XSS
1. Host a .json that contains a malicious payload
2. Ask victim to create a .ppt slide of the data in <hostedJsonUrl>
3. Victim prompts agent and opens .ppt
4. alert() fires
Just reported it. Will keep you guys updated.
2
24
1,468


Wakey wakey eggs and bakey! 🍳🥓
Just scored a reward @intigriti app.intigriti.com/profile/p0… #HackWithIntigriti

2
50
1,221


Just scored a reward @intigriti
Not the highest payout but this was a fun chain discovered in collaboration with @BadAt_Computers.
app.intigriti.com/profile/p0… #HackWithIntigriti

2
12
840

Just scored a reward @intigriti
This private program paid a bonus for an OOS bug. 🙏
I am thanful.
app.intigriti.com/profile/p0… #HackWithIntigriti

2
35
861