

Security Robot Overlord @ Google. Vulnerability Management @paradoxengine.criscio.net @paradoxengine@infosec.exchange
Italy
Joined April 2008
- Tweets5.2K
- Following378
- Followers2.7K
- Likes4.2K



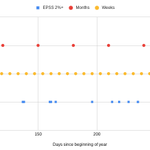
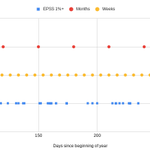
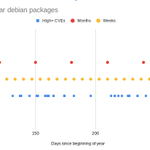
Man the brotli thing really is way more widespread than I had realized. Lots of new detectors coming in the Tsunami scanner.
Claudio Criscione retweeted

Hear me out. Just spin up an agent for each dependency you have and have it be the babysitter for that dependency. It is a surprisingly effective pattern. It only opens PRs when I’m actually vulnerable and can even find vulns before they are lifted from embargo.

Claudio Criscione retweeted

HTTP2Shell (CVE-2026-111497) is exploitable outside Node. Unauth RCE against a pinned vulnerable Docker Official Image for WordPress via /xmlrpc.php. One inbound pingback.ping, ASLR on, no leak or cross-request grooming.
PoC: github.com/caveeroo/cve-2026…
Claudio Criscione retweeted

The danger of HTTP2Shell is very real. The libbrotli 🥦vulnerability affects a wide range of software, patch now (CVE-2026-111497)
We've achieved unauth RCE in Docker's official WordPress image abusing the well known /xmlrpc.php endpoint, we call it the pingback of hell :)

Claudio Criscione retweeted

Apparently tweeting “I have a working PoC” creates a small obligation to explain how the thing works 😅
So here it is: both PHP bugs, the memory leaks, the ASLR bypass, worker pinning, and how I eventually got to execution
andrewmohawk.com/2026/10/26/…


Claudio Criscione retweeted

Interesting post showing the wait times between when a fix comes out, and how long you have to wait for various installers, containers, and other resources make it available for you to use.

Ruby 4.0.9 shipped security fixes last Friday.
Ruby core's Docker image: 8 minutes
Community ruby Docker image: almost 16 hours
Google Cloud: ~3.5 days
AWS Lambda: still waiting
How fast can you actually patch Ruby? 👇
paagman.dev/how-fast-can-you…
Claudio Criscione retweeted

IMHO, the Brotli bug (think zlib 20 years ago) is a bigger deal than PHP2Shell and all the "oooh, AI found it! AI found it!" hype.
Node2Shell is a terrible name.
I’m calling it Broccoli. 🥦
Claudio Criscione retweeted
This is the first time I've ever seen a site do this, the obvious simple response to a disclosure of a vulnerability without a fix: sacrifice availability to preserve safety. This option should be why we do full disclosure.

Claudio Criscione retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Claudio Criscione retweeted
A few of us have been predicting saturation of adversarial contact points for a while, but this is first set of good graphs I’ve seen of it.
Imagine it will take owning agencies a very substantial amount of time to realize what is happening.


Claudio Criscione retweeted

volume does matter
look, i get it. if you were an engineer before agents came along, you're rightfully skeptical about lines of code and number of PRs being used as a metric for any kind of productivity. and i agree! or at least, i used to. for ease of explanation i will talk about this from the perspective as being an engineer on a large team of at least 50.
volume didn't matter before because we focused on impact. you could have high impact even with a few PRs: for example you could make a one line config change and save the company millions of dollars.
but before agents, the times where i saw volume come into the conversation were for the outliers. on the negative end you might have someone who is struggling to perform, on the other end you might have someone who was a "coding machine" archetype. a coding machine was someone who could just lock themselves in a room and emerge with a stack of PRs that solve a huge number of problems. so volume did matter, but only at the tail ends of the distribution, and combined with impact.
if you've ever worked at a large tech company before, you'll get what i mean. the thing about agents is that big tech co problems are now small-medium co problems as well.
how do agents change this calculus? well, everyone now has the ability to become a coding machine. you have incredibly capable frontier models that can write code better than any of us, at a rate much faster than we can. in this world, if you're still producing the same number of PRs as before, why wouldn't you pause to wonder why you're not being more productive? alien intelligence is here, and yet you can't outship a human coding machine?
this brings me back to why i keep talking about trust (nitter.cf/poteto/status/21020504…). if you haven't put in the work to trust your agent's output, it is very difficult to scale up your productivity.
and yes, this approach does require more tokens, but i think about this in terms of cost per intelligence. before agents, this cost was very high - you needed to hire many software engineers with high 6 figure salaries to do the work. tokens are still expensive today, but are likely to get cheaper over time (nitter.cf/theo/status/2107924138…) factoring in the cost of intelligence. what looks exorbitant today will likely be affordable in 6 moths to a year. a single engineer with agents can do the work of tens if not hundreds of engineers, at a fraction of the cost.
the reality that i don't think has hit yet is that job of the software engineer has truly changed. our job is not merely to produce software any longer (well tbh it was never only about the code, but bear with me for the sake of the explanation), but the machine that writes the software. this idea of a software factory, or a Michelin kitchen as i like to call it, is still a topic of research. and it's the type of stuff i like to share, not to flex, but to show you what's possible when you put a lot of rigor into using agents at scale

Claudio Criscione retweeted

Tal attempts to explain why the current vulnpocalypse isn't (yet) a breachpocalypse. while his explanation may not be the correct one (he suggests alternatives too), it still makes an interesting hypothesis. a nice read.

1/ My new blopost on "Why the AI Vulnpocalypse Isn’t the Breachpocalypse (Yet)?"
TL;DR: The vuln surge (‘The Vulnpocalypse’) is real. The breach surge isn’t. YET. Vulns were never the bottleneck; the economics are.
medium.com/@TalBeerySec/why-…


Claudio Criscione retweeted

Introducing PageBreak, an agentic vulnerability discovery tool using deterministic validation to achieve a near-zero false positive rate.
How it works: blog.google/security/agentic…
For real-world vulnerabilities PageBreak has discovered 👇
bughunters.google.com/blog/p…

Claudio Criscione retweeted

We have discovered a massive, ongoing criminal exploitation campaign using Cairn, an autonomous penetration-testing harness, and other AI agents to target hundreds of organizations and successfully breach and impact tens of them (at least). The image below shows just a few days of activity, with up to 25 organizations being attacked simultaneously at the peak.
our intreim report: gambit.security/blog-posts/a…

Yeah. Actually exploitable-at-scale memory corruption vulns are one of the priors that I'm having to re-evaluate unfortunately.
@argvee had told us, but we are only starting to see it now (and I still don't know how frequent this is going to be).
Fun times

Hacktron has a good point here: hacktron.ai/blog/hacking-ope…
"Software has long benefited from a kind of security through complexity. The code and even the vulnerability could be public, but turning a bug into a reliable exploit still required rare expertise, significant time, and knowledge of the target environment. Known memory corruption vulnerabilities were expensive to operationalize, while zero-days were mostly reserved for the highest-value targets."

I love working in Vuln Management.
Over the last week everyone was going crazy about agents swarms collaborating through radio waves and whatnot.
I kept smiling.
And sure enough, they don't patch their stuff, just like everyone else.
Less APT more apt update folks.
Claudio Criscione retweeted

>be me
>discover effective altruism
>apparently normal charity is inefficient
>why donate to random sad thing when spreadsheet can tell you optimal sad thing
>fair enough
>buy mosquito nets
>save lives
>numbers look good
>feel powerful
>couple years later
>someone asks an innocent question
>why only count people alive today
>huh
>future people matter too
>obviously
>my grandchildren shouldn't matter less just because they haven't spawned yet
>reasonable.jpg
>keep following logic
>what about their grandchildren
>also yes
>what about people in 500 years
>sure
>5000 years
>why not
>500 million years
>starting to get weird but morality is morality
>open calculator
>humanity could survive for an astronomically long time
>could colonize galaxy
>could have trillions upon trillions of descendants
>maybe digital people too
>maybe simulated civilizations
>maybe dyson spheres full of happy uploaded minds
>calculator starts smoking
>realize currently living humans are rounding error
>8 billion people suddenly looking extremely beta
>future contains potentially 10^something people
>can't even fit beneficiaries in google sheets
>new moral priority unlocked
>protect the long-term future
>stop thinking in units of "people helped"
>start thinking in "fraction of cosmic endowment preserved"
>malaria?
>terrible
>but only kills existing humans
>AI extinction could delete the entire light cone
>nuclear war could permanently derail civilization
>bad institutions could lock in terrible values for ten million years
>someone invents wrong constitution in 2140
>quadrillions suffer
>better fund governance workshop now
>friend says maybe we should improve hospitals
>explain opportunity cost
>friend says hospitals are full of actual sick people
>explain scope sensitivity
>friend stops inviting me to dinner
>need to decide what to fund
>easy
>expected value
>suppose project has one in a million chance of preventing extinction
>sounds tiny
>but extinction destroys 10^50 future lives
>multiply
>mother of god
>$10 million project has expected value of several galaxies
>charity evaluation complete
>someone asks where the one-in-a-million number came from
>expert judgement
>which expert
>us
>how calibrated
>extremely thoughtfully
>reduce estimate to one in ten million to be conservative
>still beats curing cancer by 38 orders of magnitude
>epistemic robustness achieved
>someone says maybe project doesn't work
>assign 20% chance
>still astronomical
>maybe project makes problem worse
>assign 5% chance
>still astronomical
>why 5
>because 30 felt pessimistic
>publish 46-page report
>contains seventeen sensitivity analyses
>every sensitivity analysis begins after assuming intervention has positive sign
>critic says you're multiplying enormous hypothetical stakes by extremely uncertain probabilities
>yes
>that's literally why it's important
>critic says the uncertainty might be structural rather than numerical
>make probability smaller
>critic says no, I mean maybe your model is wrong
>make probability smaller again
>critic begins rubbing temples
>discover AI safety
>perfect longtermist cause
>AI might kill everyone
>or create utopia
>or seize galaxy
>or tile universe with paperclips
>or create billions of conscious software minds
>finally a problem with numbers big enough for me
>start AI safety nonprofit
>mission: prevent dangerous AI
>hire smartest people available
>smartest people immediately start building better AI to understand dangerous AI
>interesting
>we must understand capabilities to understand safety
>we must scale models to study alignment
>we must race ahead so less responsible actors don't get there first
>we must deploy systems to learn how deployment can go wrong
>we must build the thing quickly because building the thing quickly is dangerous
>outsider asks why the people most worried about AI apocalypse all work at AI companies
>complicated field
>company releases stronger model
>very concerned
>company begins training even stronger model
>extremely concerned
>company raises $14 billion
>concern reaches unprecedented levels
>need to influence government
>future is at stake
>normal democratic process too slow
>politicians don't understand exponential curves
>public doesn't understand x-risk
>experts must guide them
>who counts as expert
>people who understand x-risk
>who understands x-risk
>our friends
>someone objects that this seems politically convenient
>explain we're representing future generations
>future generations unavailable for comment
>develop concept of value lock-in
>terrifying possibility that one ideology controls civilization forever
>therefore extremely important that civilization adopts correct values before lock-in
>whose values
>let's circle back
>begin with impartial morality
>end with small group of people deciding what quadrillions of hypothetical beings would want
>beautiful arc
>meanwhile actual humans keep doing annoying things
>voting wrong
>having parochial attachments
>loving family more than strangers
>caring about local community
>getting upset when told their suffering is cosmically negligible
>evolutionary biases everywhere
>explain that moral intuition cannot be trusted
>except intuition that future digital people count
>and intuition that extinction is uniquely bad
>and intuition that our probability estimates are sane
>and intuition that our institutional choices improve the future
>those intuitions survived peer review
>someone donates $5k to local homeless shelter
>inefficient
>could have funded 0.0000000000003% of an AI governance researcher
>think of all the simulated people you just killed
>okay maybe don't phrase it that way publicly
>PR team says "future generations deserve a voice"
>much better
>journalist asks what longtermism means
>say "future people matter"
>everyone agrees
>great
>journalist asks what follows from that
>well technically we should redirect enormous resources toward low-probability interventions affecting astronomical futures
>journalist raises eyebrow
>return to "future people matter"
>motte has entered the chat
>critic: of course future people matter
>me: glad we agree
>critic: I don't agree that your institute knows how to help them
>me: why do you hate our grandchildren
>eventually notice uncomfortable implication
>if future value dominates everything
>then helping people today mostly matters through effects on future
>education matters because future institutions
>health matters because future productivity
>democracy matters because future trajectory
>human beings slowly become instrumental variables in their own moral philosophy
>see starving child
>feel compassion
>check spreadsheet
>child's direct welfare contribution negligible
>but perhaps childhood nutrition improves national institutional quality
>compassion restored
>tell myself this is impartial altruism
>one day assistant asks obvious question
>"how do you know your intervention actually improves the far future?"
>silence
>open spreadsheet
>increase column width
>add confidence interval
>assistant asks again
>"no, I mean how do you know the sign is positive?"
>stare into cosmic light cone
>10^50 people staring back
>none of them exist
>none of them can tell me
>none of them can falsify my assumptions
>realize I have invented the perfect constituency
>infinitely important
>completely silent
>and always represented by me
I finally decided to try out omarchy. Support for the keyboard did not work quite right so I hooked up a robotic arm and it LLM-generated a driver based on the aptic feedback. It also added support for my standing desk and for fidgeting, while it was at it.
Claudio Criscione retweeted
Excellent OpEd in the FT by Mario Draghi arguing that (1) without higher productivity Europe cannot sustain our social model; (2) that AI is our best possibility to do that; (3) that dependence on US and China makes this hard for sovereignty.
He proposes building up European compute, using our data advantage, and pooling corporate demand to finance it.
ft.com/content/f054f927-b512…
