
🦅 The changelog says "bug fixes." The diff says "security patch." We track CVE-less fixes so defenders don't fly blind. New drop every Thursday. @78_lab
Joined June 2026
- Tweets168
- Following2
- Followers74
- Likes2


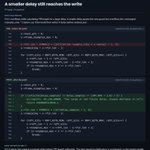
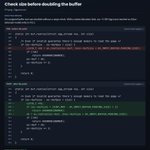
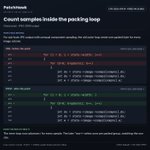
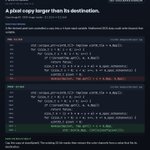
7-Zip 26.04 read two bytes past an 8-byte heap buffer while listing a crafted NTFS image. It printed those bytes as the volume version: "File System = NTFS 0.0". 26.05 skips the short attribute before reading.
Release diff: github.com/ip7z/7zip/compare…
PatchHawk flagged NtfsHandler.cpp in the 26.04→26.05 diff. In Docker, 26.04’s ASan build hits the over-read in every run; 26.05 lists cleanly; a 12-byte control parses as NTFS 3.1 on both. No matching CVE or GHSA found as of Oct 28.
PoC: github.com/78ResearchLab/Pat…
PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab

libpng 1.6.58 has a use-after-free in an unusual read path. A crafted PNG can make libpng read freed memory if an app calls png_read_end() after png_read_info() but before reading any image rows. Version 1.6.59 fixes it.
Advisory: github.com/pnggroup/libpng/s…

ALT CVE-2026-46675 in libpng. Two stacked code panels show the compressed-text release path. In 1.6.58, it only sets zowner to zero. In 1.6.59, it calls png_inflate_detach_buffers first. The error check above and the end of the block remain visible. For a crafted PNG and a read-end call before any image rows, the old path could use a pointer to freed data.
PatchHawk flagged pngrutil.c in the diff. We ran the same PNG through libpng’s public API on both releases. ASan caught a one-byte read from freed memory in 1.6.58. The 1.6.59 run ended with a handled parser error and no ASan finding.
PoC: github.com/78ResearchLab/Pat…
PatchHawk scans release diffs for security fixes. For selected cases, we share the input, Docker steps, and before/after logs so you can check our work: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more patch notes backed by code. #PatchHawk #78ResearchLab
Firefox 151.0.3 includes Mozilla's fix. On Linux, Firefox uses the system FreeType library, so updating Firefox doesn't update that library. PatchHawk compared the releases. We matched the change to this CVE and ran the Docker test ourselves. mozilla.org/en-US/security/a…

PatchHawk looks for security fixes in software updates. For selected cases, we share the code change and steps to reproduce the bug: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained through code. #PatchHawk #78ResearchLab
The PoC is now public: github.com/78ResearchLab/Pat…
It includes the 345-byte JXL input, Docker reproduction scripts, 0.11.1/0.11.2 djxl logs, and the Valgrind trace. The README states the tested 32-bit scope and limitations.
PatchHawk finds security-relevant fixes in release diffs. Selected PoCs include write-ups, repro steps, and pre/post comparisons: github.com/78ResearchLab/Pat…
Follow @patchhawk_ for more fixes explained with real code and verifiable PoCs. #PatchHawk #78ResearchLab