
Web3 Security Researcher | #2 on Code4rena 90-days leaderboard (in Dec 23) | @zenith256 Auditor, @PashovAuditGrp Auditor
Joined March 2022
- Tweets854
- Following379
- Followers2K
- Likes4.2K





Pinned Tweet
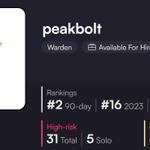
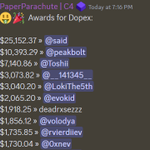
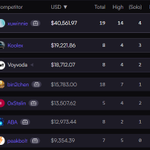
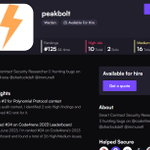
With the year ending, here's my C4 stats for 2023.
Thanks @code4rena for the opportunity!
It has been a rewarding experience while securing the web3 ecosystem.
I am ready to achieve more for web3 security in 2024!
#Code4renaWrapped

peakbolt retweeted

Code4rena will run audit contests for free, as public goods.
100% of funds from sponsors will go directly to auditors and judges. We won't take any cut.
Why?
1. Competitions are commodities.
They're CRUD apps. Why should builders pay premium for a website just to submit bugs? Especially smaller teams without VC funding.
2. Everyone deserves competitions.
We tell all our clients to get a competition after their audit. That's because competitions simulate real world conditions, where there's thousands of eyes on a protocol. We want to make competitions as affordable as possible so everyone can get one.
3. It benefits our wardens.
In 2021, we invented the competition format. We're still the platform with the largest auditor pool (10,000+ registered). Not only should builders have access to the best security talent, we believe auditors should have opportunities to work with great projects. Opening up our platform benefits our wardens.
How will you afford this?
Zellic is a profitable business. We make money doing traditional private audits through Zellic and Zenith. This benefits us because: (1) our clients are more secure after they run contests, and (2) Code4rena is a talent pipeline for Zenith.
Will you stop maintaining the platform?
Of course not. Since we acquired Code4rena, we've shipped several features and have several more already underway. C4 has a dedicated dev team that we're fully committed to.
Besides, many of our clients at Zellic use C4. We're incentivized to make sure the platform works well. It's just that now we're allowing everyone to benefit from our investments in Code4rena.
In conclusion:
Run a contest on Code4rena! We won't take a cut, your prizes will go directly to wardens and judges.
For full details, check out our blog post here: zellic.io/blog/code4rena-fre…

peakbolt retweeted
To demonstrate @burraSec's expertise, we’re offering a free full-day security review/consultation for projects integrating with LayerZero or Arbitrum—whether you’re already deployed or still in development.
We’ll thoroughly review:
LayerZero: Configuration (DVNs, Executor, and overall integration), functionality (LzRead, OFTs, vanilla OApps, and more).
Arbitrum: Native bridge or token bridge integrations, use of retryable tickets, or custom Orbit chains (e.g., custom gas tokens, USDC bridge standard).
DM me to schedule your review!

💡I’ve been asked numerous times to provide a checklist for auditing a LayerZero integration.
⚡️You asked, so here it is: github.com/windhustler/Inter…
🧠 I’ve dumped everything I could think of that can go wrong and more.
@g_vladika spent years building and breaking the core Arbitrum protocol and he’s contributed to the Arbitrum checklist.
CCIP checklist is still WIP.
I want this to become the go-to place while auditing protocols with cross-chain components.
We’re going to be adding Axelar, Wormhole, Stargate, LiFi, Across, and more.
If you’ve been auditing cross-chain protocols and found quirks or integration bugs, reach out or contribute via PR.
⭐️ If you find the checklist useful, I’d appreciate a retweet and star on GitHub to raise awareness.

Congrats on the launch @zenith256 @bytes032 ! 🔥

peakbolt retweeted

Introducing Zenith: an auditing firm that delivers good, affordable audits ASAP.
Teams want to ship this week, not next month. And without critical bugs.
We pick a team of top auditors and manage the audit. It's hassle-free.
No more waiting: we can start at a moment's notice.

Glad to see SR being rewarded in the ZKSync airdrop. Do check it out!

ZKSync airdrop has audit contests as one of the eligibility criteria
Ya'll might want to check
blog.zknation.io/zk-token/

peakbolt retweeted
Introducing Code4rena Pro League 🏆
⭐ All-star auditors
🔒 Custom security services
🥇 The best security talent including @cmichelio, @samczsun, @hellocccz, @IAm0x52, @xuwinniexu, @zachobront, and more!
Read more: code4rena.com/blog/introduci…
Excellent point by @cergyk1337. Also, We as SRs need to understand that audit firms and contest platforms complements each other in the same way. It's not a zero-sum game.

It only goes to show the strength of the @sherlockdefi model, even when an experienced SR slips up, community offers a safety net to the protocol.
Also for more context I helped to shed light during escalations on the only high issue found in the protocol and reported by @zigtur (amazing SR btw). It ended up not being rewarded due to judging technicalities
Overall this contest sees a win-win situation for all parties IMO, no need to FUD :)
1
19
1,601
peakbolt retweeted

In November, I submitted a critical bug to Cronos (@cronosapp) which they downplayed and have since been kicked off Immunefi. Here's some info about the bug and an example of how projects can simply not pay a fair amount.
Report: gist.github.com/fatherGoose1…
tl;dr:
- It's a simple staking contract where you stake your TONIC and receive xTonic at the current exchange rate.
- The vulnerability lies in a function called performConversionForERC20() which allows anyone to convert other tokens held by the contract into TONIC.
- This function is vulnerable to reentrancy because the caller sets an arbitrary swap path and can inject a malicious token in the middle to gain control of execution.
- The contract determines the estimated amount of TONIC that should be received by the swap, and any extra goes to the caller as a reward.
- But since there is reentrancy, the caller can also STAKE their TONIC prior to the above function completion.
- The caller's stake is honored AND they are transferred back their TONIC, essentially receiving free staked tokens.
Caveat:
There is a 10 day unstaking delay. So the exploiter would not be able to actually convert the staked tokens back into TONIC until the cooldown period had passed.
What Cronos said:
Thank you for reporting this issue.
The team has verified that the exploit described can indeed work. From our side, we have safeguards in place to mitigate these risks; such as a 10 days delay period for the xTonic minted. As such, there is a low possibility of the exploit realising; as the issue will be rectified before the exploiter can launder the gotten funds.
However, we do appreciate your effort in identifying this issue and plan to update the contract to eliminate the risk entirely. In addition, we are happy to reward you with USD1,600 as a token of appreciation.
Actions:
Cronos fixed the vulnerability immediately, before even responding to the report.
My thoughts:
Obvious lowball. Cronos's max bounty was $250,000 and they offered $1,600. I understand the technicality with this attack, and would have agreed to a payout less than the max, but the payout would have to accurately represent the value of this report.
Mediation:
Immunefi mediated twice and confirmed that this report deserved the max bounty. Immunefi told Cronos that a simple unstaking delay is not an adequate means of protection.
Cronos claimed:
"We have implemented a robust monitoring framework, consisting of internal systems, protocols, and strategic third-party partnerships, which promptly respond to any anomalies within our smart contracts. This is the standard of any big organization, and we refrain from disclosing further specifics to maintain the integrity of our security protocols."
When Immunefi asked them to provide any information regarding their automated detection and mitigation processes, Cronos would not comply.
Result:
Cronos was kicked off Immunefi.
Final thoughts from Django:
'Tis the life of a bug hunter.

This is a huge leap for web3 security. Congrats @bytes032 !

Officially announcing FindAudit v1.0
The first permissionless P2P security marketplace
The only place where protocols can get access to 100's of quotes from security providers.
Completely free.

1
3
606
The one tool I cannot live without is Solidity Visual Developer by tintinweb. Definitely at least 2X my auditing speed with it. Thanks @nicht_tintin !
Listen in to my recent talk on @opensensepw , where I shared my personal insights on how I levelled up my auditing skills and improved my performance within a few months!

Determined to elevate your auditing game? 🎯 Join @peak_bolt as we unpack the secrets to mastering the craft, from mastering code correctness to thinking up intricate attack vectors. Tune in as @peak_bolt unravels the path to success.
youtube.com/watch?v=5I-MP6JJ…


peakbolt retweeted

To every SR spreading FUD about contests not getting enough coverage next couple of weeks.
I invite every single one of you to prove your claim and catch solo highs.
If you can't do it, respectfully, shut up and stop spreading FUD.


Thanks to @PashovAuditGrp, which gives me opportunities to perform team audits on interesting projects with talented auditors and learn from them!
Here's an audit report we did recently.

Pashov Audit Group's first smart contract security team audit report has just been published, 10 more coming🫡
This month-long audit has ~25 Critical/High/Medium findings and we did have 2 guest auditors. Worth a read✌️
github.com/pashov/audits/blo…

3
27
1,331
What makes one more suited to be a bug bounty hunter than an auditor? And vice versa?
I'm inclined to believe there are some underlying factors that determines it even though both have overlapping skill sets.
7
21
2,831
Excited to join @DegenShaker and his blue team @SapphireWeb3Sec!

Announcing the addition of @peak_bolt to the Sapphire Dynasty team. Currently #2 on the 90 Day @code4rena leaderboard with 5 Solo highs and Top-5 for 5 contests.
Impressive.
Protocols that utilize C4's Blue Team package can rest assured they have certified leaders of industry protecting their operations.
We've also set up a dedicated X page for our team at @SapphireWeb3Sec. Appreciate a repost and follow.
Always interested in hearing from Security researchers interested in developing their growth and potential collaborations.

10
775