
Long-time Postgres. Writing about data, agents, and the incentives that break systems. United States and Brazil, in both languages. Reliability over slogans.
Lehi, UT
Joined February 2010
- Tweets3.1K
- Following1.6K
- Followers583
- Likes20K


In Postgres 18 (and unreleased 19) every NOT NULL column gets a row in pg_constraint. Every ATTACH PARTITION scans all of it.
An empty ATTACH took 0.78 ms with 195 rows. With ˜1 million rows, it took 64.5 ms. The fix is an index on pg_constraint.confrelid, committed only for PG 20, not 18 or 19.
1
3
120


Postgres update releases today fixes 52 (!!) security vulnerabilities.
Many of them let a user who can already run SQL execute code as the OS user that runs the database. That's typically postgres, which owns the database files, often run and expire backups, etc.
Some matter even if you never log in as a database user. If you use pg_restore on backup (custom, directory, tar) it can run code as the OS user that launched it. If a logical replication subscription is owned by a superuser a compromised publisher can write to the subscriber's system catalogs, which can run code as the operating system user on that subscriber.
BTW, this is also the LAST update for Postgres 14, which is now EOLd. If you are still on it, install 14.25 today and plan the major-version upgrade.
Lukas wrote a nice blog about the fixes at pganalyze.com/blog/5mins-pos…

56


Managed Postgres requires an authenticated user.
A low-privilege login is all any customer on those services gets (no superuser). CVE-2026-6460 an 8.8 fixed yesterday goes from that login role to running code as the OS user.
Mehmet Ince's proof of concept only needs temporary objects, which every role can create by default. He ported it to almost every managed provider hje knew, none unaffected.
Times are exciting and scary.

The release notes credit AI security teams at OpenAI and Anthropic, some alongside human researchers, on 30 of these 52 vulnerabilities.
In the agent era, if you leave a published Postgres fix uninstalled you are no longer waiting out a slow, expert-only exploit cycle.
26
Announcement: postgresql.org/about/news/po…
Security info with CVEs addressed: postgresql.org/support/secur…

24
One of the reasons I love being an engineer. Being used to that mindset also means one must recognize that is not the case in most other places, including relationships. One needs to navigate those differences.

I fucking love working with engineers man.
While a lot of stuff in engineering is a judgement call, a lot of it isn’t.
And I just love that engineering practice and culture never hides that.
Literally every other vocation has some element of face saving behavior when proven wrong in public.
And so many good engineering cultures are like
> the answer is 100
> no actually it’s 200
> oh you’re right I’m wrong
And then people go on with the right information.
It’s truly insane how common in some vocations someone can call the sky green in a meeting and either nobody will correct them on it or they won’t admit it and “take it offline and circle back” without ever admitting fault.
And the biggest thing is that so many engineering leaders will get corrected by subordinates.
That’s really fucking rare out there.
In other vocations corrections so often go strictly down the org chart.
Lots of companies have it all and get everything right. Engineering lead companies often do.
But so many people out only complain about “engineer” or “engineering brain” and it’s literally just people who won’t let you say random false shit constantly.
44

In July, Goldman’s CIO described traders and bankers building tools with AI and handing them to one of the bank's 12,000 engineers to polish.
By October internal guidance restricted traders and bankers from using Claude Code and GitHub.
Writing the code was the cheap part. Review and ownership land on someone else and are NOT cheap.
2
1
61
Claude Code's "Yes, and don't ask again" can save the exact command you approved, password included, in .claude/settings.local.json.
Apiiro found 379 database passwords among the secrets in public copies of that file. A password after PGPASSWORD= doesn't match a known key format.
If the password lives in ~/.pgpass, the command you approve never contains it.
47


Claude Code put the account email into the model's context so @author tags would stop inventing names.
But when the model wrote a curl call for a site that asked for a contact, it reused that email in the User-Agent. The receiving site can read the header even if you never typed an address into a form.
Once the model can see your email, it can include it in any tool calls without your consent.
Even though a privacy mod shipped in 2.1.317, what other privacy-leaking things are lurking in the shadows?
2
57
Escândalo bancário no Paraguai:
- Santiago Peña, presidente, renunciou.
- Em menos de 72h, todos os diretores e o dono estão presos, e o dinheiro já está sendo devolvido para 98% dos correntistas.
Escândalo bancário no Brasil:
- Juízes envolvidos da suprema corte julgam normalmente, e decidem sobre o próprio processo que os involve.
- Só um ou outro preso
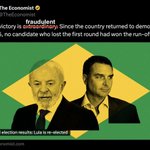
- Presidente com grandes indícios de envolvimento é “reeleito”
Paraguai deu aula de como reagir a um escândalo.
Brasil deu aula de roubalheira e bagunça institucional.
WTF

I'm not even sounding the claxon for this it's just horrible.
Any text > 256chars is a valid root password, holy shit
sshhole.com/

3
49