

A long random password gives you root - sounds like a joke, but it's an integer overflow, a real security failure.
What stands out:
• The bug isn't in OpenSSH itself, but in how the underlying library handles boundary cases. Supply-chain security isn't just "what software do you run," it's what environment it runs in.
• AI rediscovers bugs within hours, so the old "keep it secret" window is shrinking. Patching has to move faster.
• For teams running servers: disable password login by default, use keys or certificates, and keep SSH exposure minimal.
The biggest risk isn’t the sophisticated attack. It’s the basic flaw you assumed was already closed.

The bug is like a joke.
On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀
Readers added context they thought people might want to know
Exploitation requires specific conditions, not just typing a long string anywhere on Alpine: sshd built without PAM, password auth enabled, a target account with a '*' password field, and another local account with $5$/$6$ hashes. Root login also must be explicitly permitted. alpinelinux.org/posts/2026-11-… openssh.org/releasenotes.h…
3
415
Respect to @Binance for publishing this postmortem. The whole industry can learn from it.
Key lessons I took away:
1️⃣ Job interviews are now an attack vector. "Take-home assignments" and unverified dev tools belong in an isolated sandbox, never on a work machine.
2️⃣ Internal AI tools are attack surface too. Scope their access as strictly as you would an employee's.
3️⃣ High-privilege credentials shouldn't live on laptops. Deploy permissions should be short-lived and need multiple approvers.
4️⃣ Pausing withdrawals doesn't revoke on-chain authorizations that are already live. Have a runbook for revoking them in an emergency, and drill it before you need it.
Security isn’t one company’s problem. We get stronger by sharing!


9
419
⚠️ Running nodes on Ubuntu? A critical Linux kernel bug lets hackers take over your server remotely, no password needed. Ubuntu hasn't shipped a fix yet.
Until the patch lands:
• Close any ports you don't need
• Temporarily disable MPTCP
• Keep your keys off node machines
Patch and reboot as soon as Ubuntu releases the fix.
‼️ Ubuntu and Red Hat still have no fix for a Linux kernel flaw that Anthropic says its unreleased AI model turned into a remote root exploit.
The bug, CVE-2026-98432, is a use-after-free in the IPv4 TCP handshake, rated 9.8 out of 10.
The exploit needs no credentials and targets servers with a multipath TCP listener, which Go 1.24 and later open by default.
The fix reached stable kernels on 11 October and Debian has shipped it. Ubuntu still marks every release from 16.04 to 26.10 vulnerable.
Red Hat now rates it Critical but has no patched kernel for RHEL 8, 9 or 10.
Anthropic has not released the exploit. By its count, it takes 48 minutes to leak a kernel pointer and five more to run commands as root.


6
325
DNS hijacking is underrated in Web3. Take over the registrar and you control the domain, valid TLS cert and padlock included 🔒
Registry lock, hardware-key 2FA and DNS change alerts AREN’T optional.
For users: check what you sign, not just where you sign it.

Our official website, flap.sh , is currently affected by a DNS hijacking incident and is redirecting to an unauthorized website. Please do not visit the site, connect your wallet, or sign any transactions until further notice. We are actively working to restore it and will provide an update once it is safe to use again.
安全提醒:我们的官网 flap.sh 目前遭遇 DNS 劫持并被指向未经授权的网站。请暂时不要访问官网、连接钱包或进行任何签名操作。团队正在紧急处理,恢复后我们会第一时间通知大家。请以官方社交媒体发布的信息为准。

5
202
Even the hacker trackers get hacked.
The real headline: "offensive agentic techniques." AI agents never sleep, never get tired, and probe every gap at machine speed.
Security can't be a checklist anymore. Defense has to be just as autonomous as the attack.
‼️ Chainalysis, the firm that tracks crypto hackers, was hacked itself.
It told customers in an email seen by ICD that an attacker using "offensive agentic techniques" accessed users' names, emails and role labels.
It says this has nothing to do with the $6.3B Binance heist.


8
332
Tough moments reveal true strength. Full transparency and full user protection.
Standing with Binance 💛
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

1
6
155
欢迎报名,敬请期待!


2
9
367
iPhone Duo is here, and @TrustWallet is ready📱
A new large-screen design is coming soon, with smoother interactions and better trading experience.
Stay tuned 👀

NSA telling orgs to take systems offline is rare. These two bugs (CVE-2026-109618 / CVE-2026-109619) live in PHP’s core memory management, not app code.
OOM-triggered use-after-free + stale global state across requests. On mod_php the attack can fire before any application code runs - unauthenticated RCE to the filesystem or database.
Upgrade to the recommended versions and then restart your workers. If you can’t, take them offline is the right call.
Stay Safe!

2
6
399
Under the Hood of Engineering @TrustWallet #1: Problem Solving Mindset
One of our engineers asked me: "Hey Ron, how do I level up? Do I just take on as many tasks as possible?"
No. Engineering at Trust Wallet was never about task execution. It's about problem solving.
In many places, engineers are simply handed tasks and expected to execute them. That's not how we work here.
Here's how we work:
- Understand the real problem, not just the ticket
- Step back, zoom out and see the bigger picture
- Debate ideas as a team until the best design wins
- Build it to scale, because millions of people rely on Trust Wallet
- Divide and conquer, and ship it together
Over the past few months, this approach has shipped real milestones:
🔔 Revamped Notification Service ← price alerts and transaction status reach your devices much faster
⛓️ Revamped Blockchain Indexer ← balances, transaction history and status update quickly and accurately
📊 New Market Data Platform ← token prices, charts and other token data stay consistent and real-time across the app
And more to come...
The data lays it bare.
The cabal isn’t a conspiracy theory - it’s a quantifiable cluster of coordinated wallets that enter at the moment the decision is made. Everyone else, including AI agents, only sees the on-chain result after the fact. Better models and faster reactions still mean reacting to a move that’s already priced.
The edge is positional, not algorithmic. Trade carefully!

The Audit Of The Memecoin Casino
Since late August we have recorded every trade on every pump fun and Stonk launch on Solana. Not a sample. All of it: 384 million swaps from 7.7 million wallets across more than a million pools, every bonding curve and every pool that follows it. That is over 56 GB of data and 820 million rows of market history, and it grows by 18 to 25 million trades, up to a million wallets and more than 60,000 new launches every day.
We measured each coin minute by minute. We scored every entry by what the coin did next. We trained neural nets on the result, then went wallet by wallet looking for the people who actually win.
The question was simple: can anyone see the big move coming before it happens?
The short answer is no. The long answer is worse than no, because the data does not just fail to find an edge for you. It shows, in detail, who holds the edge, how they use it, and what they do with you.
Start with a coin that has actually caught a bid: real volume, real buyers, the kind of thing that shows up on your screener. From any given moment, about one in ten of those doubles within the next 24 hours. The rest bleed, and the bleeding is not gentle.
Now take a wallet's first buy into a live coin. Every first buy, 22.8 million of them over a two-week window. In 17% of those entries the coin doubles before it drops 40%. Trade that mechanically, double or stop, and you lose about 19% per attempt after costs.
Call that the house hold. A slot machine keeps 5 to 10%. This keeps 19%, per pull, before any skill or selection is applied.
The reason is the shape of the payoff. A 2× pays you 100%. The failures do not cost you 10%; they cost you 50%, 80%, 95%. To break even you have to be right far more often than the game allows.
The cabal is real, and we can see it
CT calls it the cabal. The data calls it a cluster: a set of wallets whose first buys land within a minute of each other, on the same brand-new coins, over and over. We do not find them by name or PFP. They fall out of the trade stream all on their own.
They are there. Swarms of 450, 1,400 and 2,000 wallets that hit hundreds of launches a week, moving in within the first minute or two of a coin's life. Smaller, tighter groups of 7 to 50 wallets that pick their spots. Across daily refreshes the count has run from 9 groups to 33, with members rotating in and out as wallets burn and fresh ones take their place.
They are not guessing. The coins the big swarms pile into double 28 to 46% of the time, three to four times the base rate. Their own entries, across every coin they touch, run 50 to 60% to a 2× before a 40% drop, against 17% for everyone else.
That is what an edge looks like in this market. It belongs to a few hundred wallets, and it is applied to tens of thousands of launches with industrial regularity.
Copying them loses too
The obvious retort: find the cabal, copy the cabal. We did exactly that. A machine watches every launch every minute and flags the moment a known group piles in. Then we traded every flag the way a fast human could: in two minutes behind the group, double or stop out at −40%, out after a day.
Following the big swarms lost 41% per coin across 93 coins. The median result was −95%. Not because they were wrong; their coins doubled 28% of the time. Two minutes behind them is simply already the top of the move. They bought at launch. You bought the candle they are selling into.
Following only the groups with a positive track record still lost 11% per coin. Following one good wallet on its own lost 20% per trade in our back-tests. The single pocket that came out ahead, a handful of small, tight groups, made about 10% per coin over 16 coins. That is a few days of trades and nothing anyone should bet a bankroll on.
The cabal's edge is not information you can borrow. It is position. By the time their trade is visible on-chain, the thing that made it profitable is gone.
The best model we could build still loses
We also tried the honest version: no cabal, just prediction. Dozens of signals per coin every minute, price, flow, liquidity, holder behaviour, bot share, fed into neural nets trained on our own history and tested on days they had never seen.
It works, in the sense a quant would recognize. The top of its ranking doubles 26% of the time against a 10% base rate. Two and a half times better than chance.
It also loses money every single day. 771 picks over eight days; every day negative; −11% per pick on the same double-or-stop rule; the median pick down 45%; 55% stopped out within 24 hours.
The ranking is real and the P&L is still red. The losers are deeper than the winners are tall, and nothing observable at the five-minute mark separates the coin that keeps going from the one that reverses. That is the part worth meditating on: a model 2.5× better than chance odds is still a losing model.
Why nobody sees it coming
The reason is simple, and it should change how you look at every chart. A meme coin moves because a few people decide to move it: the operator holding the supply, the caller with an audience, the wallet group with the bankroll. That decision is made off-chain. The chain only shows you its execution, the swaps, the volume, the new holders, and by then the first leg is done.
Everything a trader looks at, from a screener to a chart to a wallet tracker, is a photograph of a decision that has already been made. The data is enormous and almost all of it is the crowd reacting. The informative part, a few hundred wallets' intent, is visible only at the instant it executes, and the people executing it are the ones selling to you a few minutes later.
Add 60,000 launches a day, and the future 100× at minute one is indistinguishable from the 59,999 that die. The casino does not need to hide the cards because it deals them faster than anyone can read and analyze them.
Conclusion
After spending thousands of dollars in API credits, VPS costs, Claude credits, etc the goal was simple: find alpha - if it exists - in order to be able to monetize it.
Instead, all we were able to prove is what we all have suspected all along - the meme coin casino is almost entirely cabal driven.
🫡 From the depths —
The White Whale 🐋

5
369
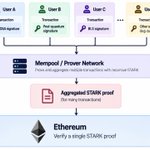
EIP-8288 maximalism is the real architectural shift.
Heavy cryptography moves client-side → STARK it → aggregate. Ethereum stops doing the work and only verifies the result. No more precompiles, lean chain.
But then proof generation & aggregation become critical infrastructure - potentially as important as validators and block builders.
Is proving latency the next bottleneck?


Ultimately, precompiles and EVM are both the wrong place to put most cryptography support into Ethereum. The reason is that precompiles and EVM both operate on data that has to be included into the ethereum chain somehow, which realistically means included in a block as calldata. That space is limited - even with PeerDAS and blocks-in-blobs, there's a practical cap of ~8 MB/s before it starts getting uncomfortable.
Remember: it's not a blockchain. It's a cryptographic world computer. Any data/computation that does not need to be in the "main thread" of data/execution should not be put into the main thread.
Instead, the correct solution is... EIP-8288 maximalism.
If you have any heavy computation that's self-contained, compute it and STARK it client-side (this is quickly getting faster and faster, even on phones), and push the STARK through the EIP-8288 recursive aggregation mechanism. The chain sees the fact that the computation was done and what the result is; it never needs to see the actual data and computation.
This way everyone can use whatever cryptography they want, the Ethereum chain can be lean, and we never need to add more precompiles again.
8
344
We cut the app size significantly by systematically removing legacy code, unused stacks, and unnecessary dependencies accumulated over the years.
A smaller binary brings direct, measurable gains:
- Faster download and update times, especially on slower networks or metered connections
- Lower storage footprint, which matters for users with limited device space
- Reduced install friction - users are more likely to complete the download when the package is significantly smaller
- Smaller attack surface and less code to load at startup, which can help with cold start and overall memory pressure
Doing this kind of dependency cleanup and dead-code removal while the app stays in production is non-trivial, but the user-facing improvements are clear.
We’re continuing to push further! @TrustWallet
app size is down by ~200 MB, and we’re aiming to trim it even further.
a lot of behind-the-scenes work, like making jet engine changes in-flight (eth merge energy, but frontend).
over the last 9 years, we've accumulated legacy code, unwanted stacks, and unnecessary dependencies that we never prioritized fixing, making the app bulky; we’re cutting that weight for real.
kudos to our based devs, tremendous work!


1
10
374
这些看起来都是“理所当然”的体验优化,但背后是技术团队持续在性能、交互流畅度、数据实时性和多语言/多场景适配上做深耕。
老用户觉得“本该就有”的功能,恰恰说明产品在不断向“无感好用”靠拢 - 我们从底层性能、数据架构到用户触点反复打磨,力争把 @TrustWallet 做成真正的 “指尖好产品”:打开快、操作顺、信息准,不管牛市熊市,都能成为大家日常最顺手的工具。

