

security @zksecurityXYZ & AI @zkaol, Assistant Professor @ucl - PhD @imperialcollege
London, England
Joined November 2021
- Tweets260
- Following276
- Followers849
- Likes1.1K





Pinned Tweet
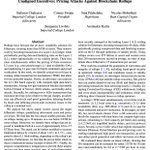
Excited to share our latest work on ZKPs security: "SoK: What don’t we know? Understanding Security Vulnerabilities in SNARKs" (w/ @0xSerious, @infosecual, @cryptodavidw, @MMJahanara, @convoluted_code).
URL: arxiv.org/pdf/2402.15293.pdf

Stefanos Chaliasos retweeted

zkSecurity audits formal verifications, the line is this way ⬇️

Who verifies the formal verification?
Read about how we audited @TachyonZcash's Ironwood formalization and about common pitfalls for formal verification in general.
blog.zksecurity.xyz/posts/au…
Stefanos Chaliasos retweeted
We hired @zksecurityXYZ to audit Ironwood's formal verification. Rather than looking for security bugs, they tried to *add* bugs to see if the formal verification could catch them!
Here's our summary, along with the report:
zakura.com/engineering/adver…

Stefanos Chaliasos retweeted

Who verifies the formal verification?
Read about how we audited @TachyonZcash's Ironwood formalization and about common pitfalls for formal verification in general.
blog.zksecurity.xyz/posts/au…
Stefanos Chaliasos retweeted

Very proud of this work and honoured that it is receiving an Outstanding Paper Award at TCC'26! H/t to my co-authors and huge thanks to @zksecurityXYZ for the support
FRI is a fundamental protocol yet few people confidently say they understand the security proof. This ends today

Congratulations to @0xAlbertG (Nethermind), @nico_mnbl (zkSecurity), and Benedikt Wagner (Ethereum Foundation) on winning one of three Outstanding Paper Awards at TCC 2026, the Theory of Cryptography Conference, for "A Simplified Round-by-round Soundness Proof of FRI."
FRI sits at the core of most STARK-based proof systems, including Starknet's. Its existing soundness proofs are long and hard to check. This paper gives a much simpler one, which is a step toward formally verifying the systems built on it. eprint.iacr.org/2025/1993

Stefanos Chaliasos retweeted

been telling people for a while @nico_mnbl has become one of the experts in the field and they should watch his work - if you don't follow him, highly recommend

Very proud of this work and honoured that it is receiving an Outstanding Paper Award at TCC'26! H/t to my co-authors and huge thanks to @zksecurityXYZ for the support
FRI is a fundamental protocol yet few people confidently say they understand the security proof. This ends today
Stefanos Chaliasos retweeted
we introduce categories of Fiat-Shamir bug in this post blog.zksecurity.xyz/posts/fi…

Stefanos Chaliasos retweeted
The Year Finding and Exploiting Bugs Became Cheap, and What to Do About It
blog.zksecurity.xyz/posts/th…

Stefanos Chaliasos retweeted

Recently talked about zk.golf, LLM-as-compilers, and how writing zk circuits can be extremely cheap!
youtube.com/watch?v=9BSzHnkM…
Stefanos Chaliasos retweeted
We’re happy to support the proximity prize challenge efforts, now with machine-verifiability!
better.codes currently hosts two challenges, to improve what we know about the security bounds of proximity gaps. Since the challenges are expressed in Lean, every accepted result carries a strong guarantee, in the same style as zk.golf.
This follows the series of efforts in the industry and in our team to utilize verifiability for fearless optimization.
Starting from a security bits baseline of 53 (lower bound) and 128 (upper bound), AIs (and people too) will collaborate to improve the state of the art, and hopefully interesting ideas that can advance science will rise out of it!

Stefanos Chaliasos retweeted
vibe cryptographing? do it right! explore some ways AI is being used to optimize cryptography
blog.zksecurity.xyz/posts/op…
Stefanos Chaliasos retweeted
We just released zkvmBlast: a zkVM-agnostic differential fuzzer for RISC-V zkVMs.
One program, run across SP1, RISC0, OpenVM, Pico, Zisk and Airbender plus a reference simulator. Every disagreement is a bug lead.
Partially funded by the @ethereumfndn
Stefanos Chaliasos retweeted

zk-skills by @zksecurityXYZ was just added to pashov/ai-web3-security🤝
Bravo to the zkSecurity team for shipping this👏
github.com/pashov/ai-web3-se…

Stefanos Chaliasos retweeted
We just released zk-skills: open-source security skills for AI coding agents, starting with circom-auditor, a first line of defense for finding vulnerabilities in Circom circuits.
Partially funded through the Ethereum Security QF round (@Giveth). Big thanks to @TheDAOfund, @quantstamp & @wintermute_t for leading this round
🧵
Stefanos Chaliasos retweeted
Excited to share I’ve joined @zksecurityXYZ 😃
I’ve known the amazing team for years, and I’m happy to be part of this team that has been involved in securing and creating important parts of cryptographic infrastructure across the industry
Grateful to the inspiring @stefancoh, @alexhevans, @angeris and the rest of the team for the time together in @BainCapCrypto, and all the awesome founders I got to know and work with during my time there
Reach out to me with anything related to security, cryptography, formal verification, distributed systems, protocols or otherwise need help with!

Stefanos Chaliasos retweeted
Warning to cryptography projects running in production, a massive amount of bugs are being reported and/or exploited in the wild. Basically every time we run zkao on the exploited project it ends up finding the bugs. Run a scan now rather than later. zkao.io
Stefanos Chaliasos retweeted

Kudos to @zksecurityXYZ for building zk.golf !👏
Porting some of the optimizations proposed for challenges 5 and 6 into @gnark_team 's circuits yields some impressive results! -50% constraints for ECRECOVER precompile circuit, which directly benefits @LineaBuild🔥

Stefanos Chaliasos retweeted

1/ Zero-day discovery just went from an elite human craft to a cheap, automatable commodity. DARPA's own AI Cyber Challenge proves it: detection rates jumped from 37% to 86% in a single year.
Stefanos Chaliasos retweeted
AI meets Cryptography 3: What AI Found in Bron Labs's bron-crypto
blog.zksecurity.xyz/posts/br…