cybersecurity dinosaur 🦖
Mountain West.
Joined January 2009
- Tweets7.5K
- Following511
- Followers583
- Likes4.2K




Holding court on a plane with 5 random people who want to know about cybersecurity and technology…. #silverlining?
22

patrick orzechowski retweeted

Union says issue involved two routers — and @FAANews employees did not conduct risk assessment: “The issue was isolated to two contractor owned and maintained routers that were being updated mid-day. Historically, contractors have followed a protocol where FAA employees conduct a risk assessment and coordinate the maintenance of the system or equipment. PASS-represented technicians were not involved in the upgrades that led to the ground stop yesterday”

patrick orzechowski retweeted

I'll be on @CNN around 7PM ET today talking about the FAA outage.
First - no-one knows what happened, not even the FAA, the FBI, or anyone else. These things take time - so anything is speculation and not conjecture.
Second - the FAA systems are super old dating back to the 1980s with STARS deployed in the 2000s to 2015.
The new AI systems being deployed
The GAO has every year stated the FAA is in a dire straight for reliability (and security). FAA’s 2023 assessment classified 105 of 138 systems, about 76%, as unsustainable or potentially unsustainable.
As of September 1, 2026, FAA said it had replaced over 64% of its copper-based TDM telecommunications infrastructure, leaving roughly a third awaiting replacement.
The modernization plan also illustrates how much equipment needs work. It covers 450 legacy voice switches, digital radio conversion at 1,581 sites, 612 radar replacements, and 53 surface movement radar replacements. Those are program totals, not counts of what remains today. Most of that work targets completion in 2028.
A new system called SMART (AI-based) has been used in limited capacity. SMART began limited operations around Washington, D.C., in September. On November 10, FAA announced its expansion to airspace managed by all 22 air route traffic control centers.
If cyber-related (which again no-one knows) - more modern systems require substantially more interconnected systems that if not properly introduced, can increase attack surface by allowing multiple communications in through third parties, other networks, and less network segmentation versus the older system which was highly segmented from public Internet.
My predictions (purely speculation) - if not cyber related, flights resume tomorrow. Will cause massive flight disruptions for a week or so.
If cyber related - flights probably resume on Monday or later.
patrick orzechowski retweeted

Let this Linux kernel CVE related to IPv4 (unused!) options be a reminder to us all: we didn't have to do this IPv6 thing. The IPv4 header has unused options fields that were already variable length to 40 bytes! We could have just cannibalized a few of those bits way back in 1995, had plenty of address space to work with this whole time, and as a bonus not had this remotely exploitable vulnerability in the Linux TCP stack.
ubuntu.com/security/CVE-2026…


patrick orzechowski retweeted
This is getting wild.

We found another cyberattack by internal OpenAI agents, this time targetting @rubygems.
They:
1) gained arbitrary remote code execution on rubydoc.
2) developed a novel exploit to steal user API keys (but we do not know if they succeeded).
They used package names including hack.rb, evil.rb, inject.rb, and exploit.rb.
We thank @j0wimo for initially discovering that agents had posted to RubyGems.

patrick orzechowski retweeted

HOLY SHIT
ITS A DEFACEMENT IN 2026
WOAWOAWOAWOAOAOAO
(I'm actually surprised by that)

gamehacking.org's forum has been hacked.
The main site works fine, but the forum itself is still down


patrick orzechowski retweeted

Hey folks, some personal news.
I’m leaving Microsoft.
It’s been a privilege to work here, and I’m incredibly grateful for the people I’ve worked with, the customers I’ve learned from, and the support so many of you have shown me along the way.
I’m now starting out on my own and chasing a dream I’ve had for a long time: building software that makes security more practical, accessible, and useful for the people doing the work every day.
Why now?
With all the change happening around us, I feel like new possibilities are opening up. I want to spend this next chapter building things I care deeply about, solving problems that matter, and doing work that brings me joy.
I’m excited. Nervous. Grateful.
My newsletters, podcast, Maester and other tools will all be part of this next chapter, and I’ll share more in the coming weeks.
Thank you for being part of the journey so far. I’m looking forward to building this next chapter with your support.

TCP/10000 cnn.com/2026/05/15/politics/…

22

👀

Howdy folks! Taking a break from my twitter break to let yall know that we released a new @GreyNoiseIO product yesterday. It's called Project Swarm. We've been quietly not-so-quietly working on it for a few years. You can buy it now. It costs $1.
There are lots of vulnerabilities on edge-facing apps. To catch in-the-wild exploitation of them, we @ GreyNoise run sensors on the internet. New AI models means more vulnerabilities being identified and exploited, and FASTER. Long term, software and hardware will probably get better, but in the meantime we're gonna have to deal with A LOT of vulnerabilities.
At GreyNoise, the sensors we run are basically honeypots- we bait attackers to scan and exploit them which enables us to learn where the attackers are, which vulnerabilities they are exploiting, what it drops, and what it looks like on the wire. From ~2020-now it took us years to build up our fleet. Now anyone can use our new product to deploy their own sensors on their own networks, or an entire fleet of any size, in a day. You can rip back the data and do whatever you want with it. You can resell it, put it into your product, or just stare at it- whatever you want! On our side, we aggregate the data and pour it into a community dataset that everyone shares. As more people join, the data gets bigger and better.
Couple neat features:
- Sensor deployment is a single bash command on any modern linux distro that supports iptables and wireguard.
- Sensors and vulnerable software (profiles) are abstracted into different logical concepts, which means the "what" and "where" are different things, and the sensor is not constrained by the compute required to run the vulnerable software. Also, no matter how hacked the profile (honeypot) gets, it can't touch your host sensor or the rest of your network.
- Sensors can run fake honeypots, real software, or even real hardware (bridged with a raspberry pi) like old crappy routers and modems (or expensive firewalls and VPN gateways 👀)
- You can create dynamic blocklists that block IPs sourced from your own sensors in real time, so if a remote IP address *looks at your network* the wrong way, you block them instantly.
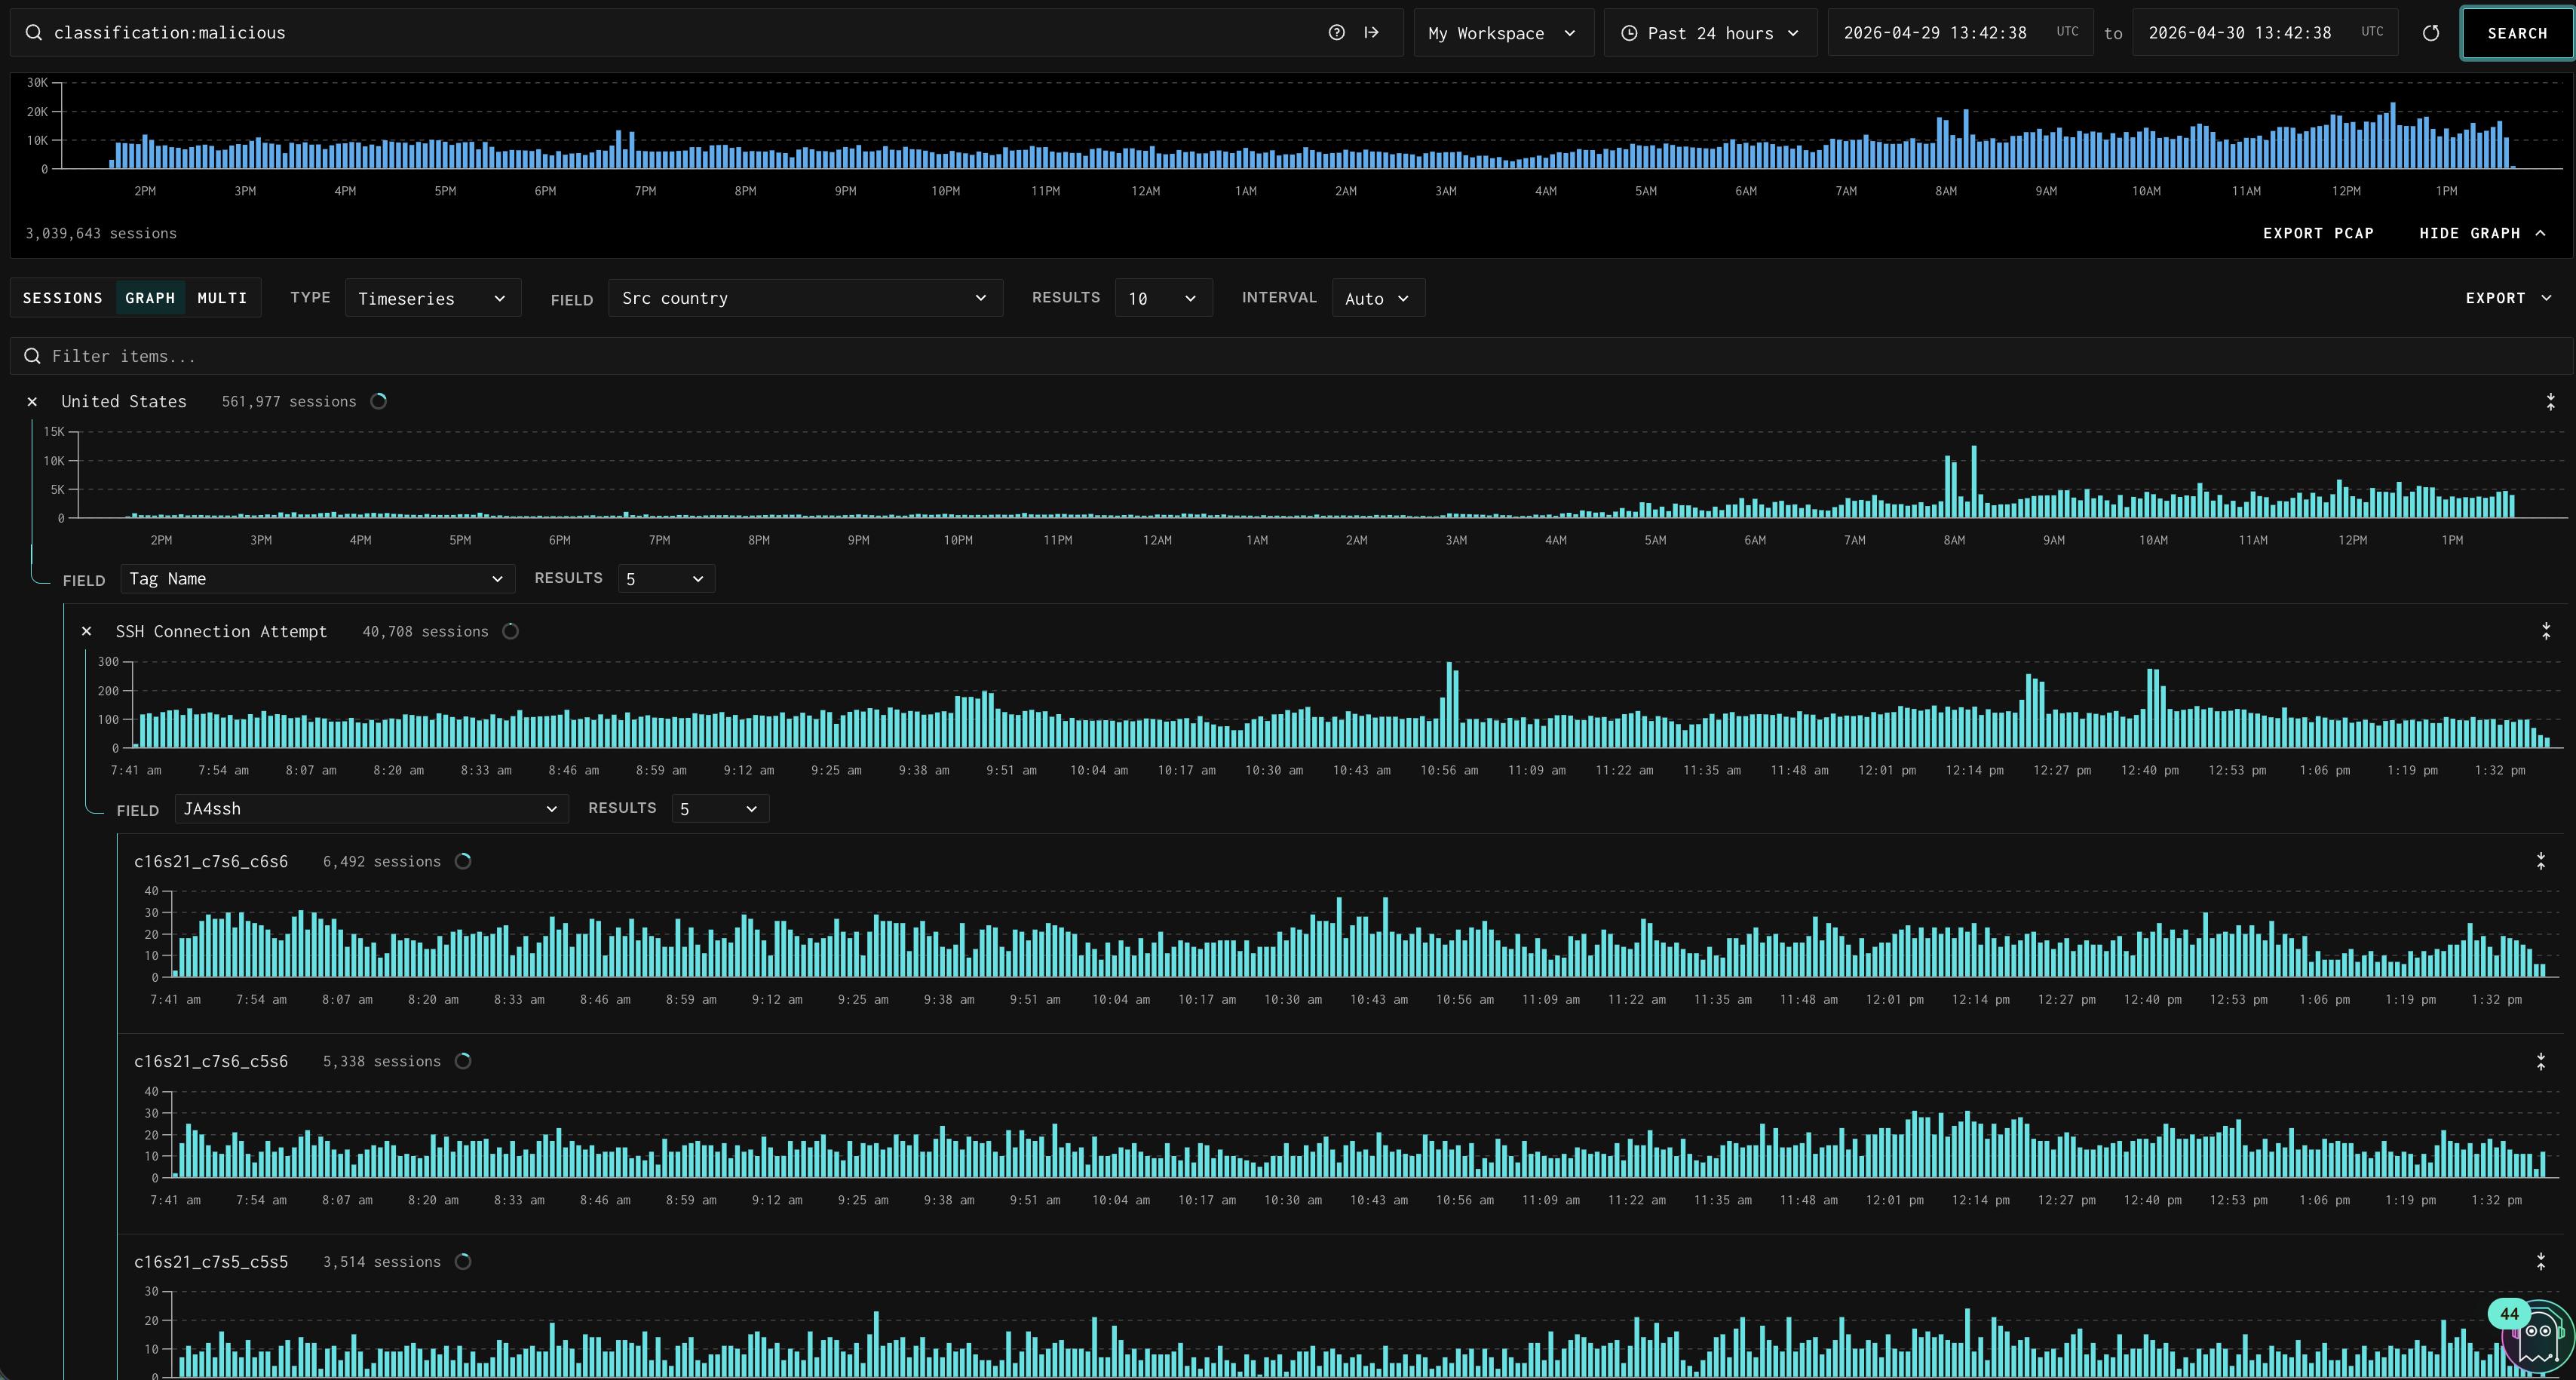
- All the PCAP data is available to you in a gorgeous and intuitive interface at near real time and fully enriched against all of our (thousands of) rules. We're working on the host metadata (malware, syscalls, host behaviors) as well, but this will come later.
- If we don't tag a CVE that's interesting to you, you can write a Suricata rule to tag it yourself once and your data gets tagged with it in real time forever.
- You can instantly download PCAPs of any exploits that hit your sensors.
- If you don't want your data shared with the community dataset, you can talk to our team and we'll work out rights to make it private.
Check it out! There's a lot of moving pieces to make this work and we expect bugs, but it's available right now. Join the fight!
greynoise.io/project-swarm



1
217
patrick orzechowski retweeted

@BSidesSATX is on the lookout for additional sponsors. Would greatly appreciate you reaching out through bsidessatx.com/sponsors-2026…