




Pinned Tweet
🚀 Syhunt is bringing next-generation, on-device AI to application security!
Join us at Security Leaders Brazil 2026 for an exclusive preview of NX, our new AI-native and AI-augmented security product line.
📍 São Paulo | October 21–22
🔗 Learn more: syhunt.com/en/?n=News.2026-N…

Syhunt Hybrid 7.2.1 responds to Black October with DAST coverage for 207 additional CVEs and expanded SAST detection.
🔗 Learn more: syhunt.com/en

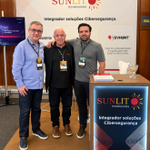
Thanks to everyone who stopped by Sunlit's stand at the Security Leaders Brazil conference to learn about the upcoming Syhunt Hybrid NX product line!
Pictured: Paulo Roberto dos Santos, Antonio Carlos Scola, and Cauã Pastore.
We were there to showcase the upcoming Syhunt Hybrid NX product line, which combines deterministic code security testing with multiple AI engines.
Learn more at syhunt.ai

Syhunt retweeted

🚨 First PHP, now Ruby...
Memory corruption vulnerabilities in Ruby's regex engine (Onigmo) could lead to RCE in applications that compile regular expressions from untrusted user input.
Not just ReDoS. These flaws are also behind the recent GitLab RCE alerts. So... update Ruby!
ruby-lang.org/en/news/2026/1…
#ruby #rubylang #rails #rubyonrails #cybersecurity

Syhunt retweeted
🚨 CONFIRMED: PHP has officially acknowledged another RCE vulnerability, CVE-2026-115560, affecting specific session configurations even after the October 21 patches.
A separate issue, not a bypass of the original fixes. A patch is planned.
We've updated our defensive toolkit:
github.com/syhunt/php2shell-…
#php #cybersecurity

Syhunt retweeted
We've updated our php2shell-protection toolkit with new findings on post-patch PHP security risks, additional hardening recommendations, and expanded credits to @acd421 for his research.
No exploit code or PoC links. The focus remains on defense.
#php #cybercurity
github.com/syhunt/php2shell-…
Syhunt retweeted
🚨 UPDATE: A public PoC demonstrates RCE on PHP 8.5.12, even after the October 21 security patches.
The attack is separate from the patched php2shell CVEs and requires specific session configurations and application weaknesses.
Our earlier concerns about PHP session handling remain relevant.
We've updated php2shell-protection with additional hardening guidance.
#php #cybercurity
github.com/syhunt/php2shell-…
Security teams aren't getting much sleep tonight.
nitter.cf/FelipeDaragon/status/2…

As if PHP2Shell wasn't enough for one day... now GitLab. 😅
🚨 CRITICAL GITLAB ALERT (CVSS 10.0)
CVE-2026-110264 could allow unauthenticated RCE on self-managed GitLab servers.
⚠️ Potentially affects 12 years of releases, dating back to 2014.
Patches available. Update immediately!
docs.gitlab.com/releases/pat…
#gitlab #cybersecurity
Patch immediately, but continue monitoring emerging research. The reported crash warrants investigation, not a premature declaration that PHP 8.5.12 remains remotely exploitable.
nitter.cf/FelipeDaragon/status/2…
🚨 UPDATE: PHP 8.5.12 may still be vulnerable to php2shell!
Researchers are reporting a successful double-free trigger on the newly patched release.
⚠️ The official fixes may be incomplete. A crash alone doesn't confirm RCE, but this deserves urgent investigation.
Don't assume you're safe just because you've patched.
#php4shell #php #cybersecurity
nitter.cf/_annieversary/status/2…
Syhunt retweeted
🚨 UPDATE: PHP 8.5.12 may still be vulnerable to php2shell!
Researchers are reporting a successful double-free trigger on the newly patched release.
⚠️ The official fixes may be incomplete. A crash alone doesn't confirm RCE, but this deserves urgent investigation.
Don't assume you're safe just because you've patched.
#php4shell #php #cybersecurity
nitter.cf/_annieversary/status/2…

chat. chat... its not funny anymore

Readers added context they thought people might want to know
The original post has since been edited to specify that this was about an unrelated vulnerability that the user had discovered, not the recently patched vulnerability.
fedi.katze.sh/@elise/1174793…
Syhunt retweeted
🚨 UPDATE: PHP's official advisory confirms the php2shell vulnerabilities and session upload-progress attack path, but not that multipart blocking provides complete protection.
We've updated our repo with official findings and additional hardening measures. Patching remains essential.
github.com/syhunt/php2shell-…
#php #Cybersecurity #php2shell
Syhunt retweeted

ありがたい!が、環境によっては注意が必要。
php2shellの暫定策として「multipart/form-dataのPOSTをApacheで止める」ルールを入れるなら、判定をPHPと同じ切り方に揃えないと漏れる。
PHPはContent-Typeを「;」「,」「空白」のどれでも区切り、小文字にしてから multipart/form-data と比べる(main/SAPI.c)。syhunt/php2shell-protection の初版の正規表現はカンマを見ておらず、公開から約2時間後の修正で [;,[:space:]] になった。READMEは効果の限界まで正直に書いてある。使うなら修正後の版を。
自分の環境に当てはめて引っかかったのは3点。
・AllowOverride None だと .htaccess は読まれない。vhostに書く
・<If> の %{CONTENT_TYPE} はレスポンス側。リクエストは %{HTTP:Content-Type}
・同梱の checkblock.php はHostヘッダ宛にPOSTするので本番に残さない
2件目の根本原因はまだ公式に出ていない。multipart以外の経路があるかは、修正版の差分で確かめてください。
github.com/syhunt/php2shell-…
We've released php2shell-protection, an emergency Apache mitigation and testing toolkit for CVE-2026-109618 / CVE-2026-109619.
⚠️ Not based on official vulnerability details. This is a precautionary measure based on information circulating in the security community and zero-day PoC material we've obtained and reviewed.
It blocks multipart POST requests before they reach PHP. Not a substitute for patching.
github.com/syhunt/php2shell-…
#php #Cybersecurity
Syhunt retweeted

For those mitigating remember this is still primitive mitigations the ultimate is updating as soon as its released. Some parts were Redacted for safety to the ecosystem as a whole. These primitive mitigations still give you a head start on what attackers likely already recreated.
We just released an emergency mitigation and testing toolkit for CVE-2026-109618 & CVE-2026-109619.
This is a precautionary, community-driven effort based on preliminary info and privately reviewed zero-day PoC material, not official vuln. guidance
#php
nitter.cf/FelipeDaragon/status/2…
We've released php2shell-protection, an emergency Apache mitigation and testing toolkit for CVE-2026-109618 / CVE-2026-109619.
⚠️ Not based on official vulnerability details. This is a precautionary measure based on information circulating in the security community and zero-day PoC material we've obtained and reviewed.
It blocks multipart POST requests before they reach PHP. Not a substitute for patching.
github.com/syhunt/php2shell-…
#php #Cybersecurity
"Our support team has determined there was no violation and has restored your account to full functionality." Oh, okay...
Syhunt retweeted

Proud to have partnered with Syhunt in developing its next-generation on-device AI technologies, including proprietary AI models, a breakthrough Symbiotic AI security engine, and AI-powered vulnerability analysis
nitter.cf/syhunt/status/21097467…

🚀 Syhunt is bringing next-generation, on-device AI to application security!
Join us at Security Leaders Brazil 2026 for an exclusive preview of NX, our new AI-native and AI-augmented security product line.
📍 São Paulo | October 21–22
🔗 Learn more: syhunt.com/en/?n=News.2026-N…


DaragonTech started out as Syhunt's AI research division and is now an independent company.
Proud to see what it's shipping.
github.com/DaragonTech/LibLa… #OpenSource

Syhunt retweeted

welcome LibLayaX ✨🚀

LibLayaX 1.0.15 is out: an open-source alternative to the Jev API. It runs Laya decision models locally, from any language, on CPU or GPU.
New:
- a model in one .tar file
- GPU under Wine, Apple Silicon included
github.com/DaragonTech/LibLa…
#OpenSource #AI #ML #LocalAI #Jev