

Malware Analyst/Vuln Hunting
Kazakhstan
Joined June 2019
- Tweets2.8K
- Following407
- Followers851
- Likes6.8K





Neogram retweeted

Cool project for AI/vibe reverse engineering .net apps built on top of libxsql and inspired by IDASQL and GhidraSQL by Rakan AlDuwaysan.
Give your AI agent this tool and see it RE smoothly.
github.com/rkn47/dnspysql

Neogram retweeted

some new pics of iOS 7.1.2 on a smasnug J1 2016
source code here:
uniloader - github.com/kOtusin/uniloader
xnu - github.com/kOtusin/xnu-j1xlt…


Neogram retweeted

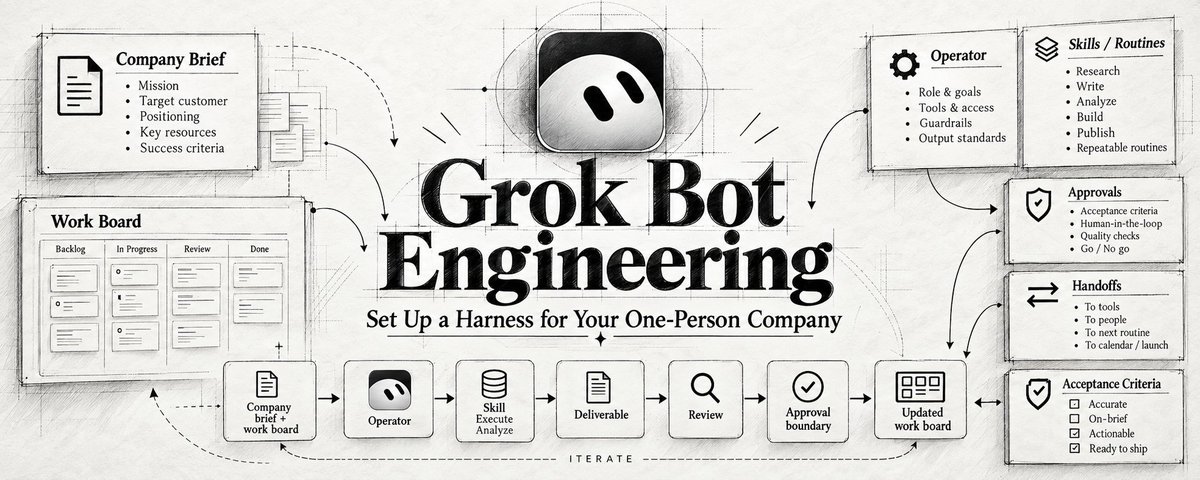
This is f*cking insane. SpaceXAI engineer Lauren Tan:
"There's no point spawning 110 agents if you can't trust the output of one"
"Without a verification skill, you're the one checking everything - and you become the bottleneck"
In a 1-hour talk, she explains how she went from reviewing every output to shipping 1,000 PRs in a month
Watch Every Step → Verify → Skills → Evals → Auto-Merge
Trust in agents isn't a feeling - it's infrastructure you build
Worth more than most $2,000 AI coding bootcamps
Bookmark it and watch tonight


Neogram retweeted

blog.talosintelligence.com/b…
@TalosSecurity identified UAT-6275 (TAG-193 by Recorded Future) activity targeting government organizations across the Commonwealth of Independent States (CIS). Recovered artifacts show additional interest in water resources and energy. This focus is consistent with intelligence collection and may reflect the regional effects of the Russia–Ukraine war.


Neogram retweeted
If you update WinDbg, you might notice a few changes :) There's now an official MCP server for the debugger.
devblogs.microsoft.com/perfo…

Neogram retweeted

A little over a week since launch, OrcaSAQ-2 Cyber 27B is among the most trending models globally on Hugging Face. Again.
15.7GB.
262K context.
94.4% Top-1 fidelity.
Built for cyber.
We believe it’s the most capable cyber model in its size class (<16GB).
Small enough to run locally. Strong enough to matter.
Try it out: huggingface.co/orcarouter/Or…


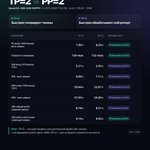
Today we’re announcing OrcaSAQ-2 27B
High-fidelity mixed-precision Qwen3.8 for long-horizon agents.
55.59 → 12.06 GB — 78.3% smaller / 4.61×
3.21 bpw · 93.2% Top-1 agreement
70.0 SWE-bench Verified
58.4 Terminal-Bench 2.1
262K context
A 27B model for coding, terminal, browser, security and multi-tool agents — in a footprint you can actually deploy.
SOTA agentic capability density among similarly sized models we evaluated.
huggingface.co/orcarouter/Or…

Neogram retweeted

🇷🇺

🕵️♂️Our team analyzed data leaked from the Russian research institute Spetsvuzavtomatika last May that exposed a broad research and development program for automated cyber-enabled intelligence collection. Read the investigation 👇
dti.domaintools.com/research…
#Russia #Cybersecurity

Neogram retweeted

While sweeping open directories on @etugenio, I came across a server in the US🇺🇸 on PEG TECH's network with port 8888 exposed. It wasn't a victim, but rather a box where a Chinese🇨🇳 speaking operator had left their entire offensive arsenal exposed to the internet. At the center of it was an AI-driven pentest framework.
The operator calls it "Sinian." It organizes each attack technique into its own SKILL.md playbook, while sinian_pipeline.py chains them together into an autonomous attack pipeline. The same environment also hosts a plugin-based webshell C2 with modules for lateral movement, database dumping, SOCKS proxying, persistence, and log timestomping.
The targets include Chinese payment and virtual-goods platforms such as tokenpay, dujiaoka, acg-faka, and epay, whose source trees were exposed through publicly accessible .git repositories. The attacks appear to rely on a ThinkPHP deserialization chain. Tooling targeting Shanghai health-card and Guangxi police-certificate systems also suggests that the operation extends into account-opening and real-name verification fraud. Stolen data is exfiltrated to a Telegram bot.
Host: app.etugen.io/trashpile/104.…
Content: Sinian AI pentest toolkit + webshell C2 + qingmeng-backdoor
Exfiltration: Telegram bot
Framework: CyberStrikeAI
Exploits: CVE-2024-44902 - CVE-2025-63888 - phpggc
Targets: tokenpay - dujiaoka - acg-faka - epay
Fraud tooling: shanghai_health_card.py - guangxi_police_cert.py
ATT&CK: T1059.004/.006 · T1552.003 · T1530 · Webshell
#CTI #opendir #usa #china #war #hack #webshell


Neogram retweeted

Malware family identification is hard, especially when samples are packed, encrypted or poorly classified. FlowCarp can help identify the correct malware family and reduce alert overlap.
netresec.com/?b=2692109

Neogram retweeted

Windows Exploitation Techniques: Dangling COM Object Registrations projectzero.google/2026/09/w…


