
Father of 2 Perpetual Student He/Him
Joined April 2017
- Tweets653
- Following551
- Followers278
- Likes442
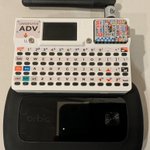






I've grabbed a Philanthropist badge the last 4/5 years because I can't go to summer camp anymore. I was wondering what was up, and I'm bummed, but can't hate since the track was so real 🤣

Badge mog your peers with the last @ANDnXOR DC34 Philanthropist Badge.
Max aura.
Zero Cool.
One remains.
And.
Thank you everyone so far for helping make the @5n4ck3y CTF happen at @defcon again. We couldn't pull this off alone.
We love you.
shop.andnxor.com/products/an…


Just opened mine, this thing is so baller, gonna need a permanent spot on my desk.

A few people have received their badges.
They're probably so overwhelmed by the sheer chaos and blinding beauty they’ve lost the ability to tweet.
Or they’re still rebooting. Emotionally.
#mainedoesnotexist #mattdamon


I love hearing passion @ #ThruntCon, @DrunkBinary CTI Stories back to back with @nohackme talking real vs fake rap beefs.


Thrunthog retweeted

Stairwell's comprehensive analysis helps ensure that users instantly know if they're impacted by the #xzbackdoor — down to the when and where — or confidently confirm they're not. Grab IOCs, a #YARA rule, and learn how Stairwell users are a step ahead: stairwell.com/resources/thre…

Thrunthog retweeted
Three days later, lets catch up together on the #XZBackdoor in #XZUtils .
Current understanding (2024-04-01) is the malicious code creates a backdoor for remote code execution.
1 / 5🧵
For those looking to get straight to RE: github.com/karcherm/xz-malwa…


reddit.com/r/sysadmin/commen…
And there goes the weekend

Seeing passion is watching Drive to Survive and @danielricciardo giant smile when Christian says "welcome back"
Thrunthog retweeted
Stairwell closely monitors news for #security events that could potentially impact customers and the world at large. Among rumors of a breach at #AnyDesk, we started proactively working to develop #YARA rules and hunting methods.
Get them here: stairwell.com/resources/proa…

Thrunthog retweeted
🕵️♂️ The silent torrent of VileRAT
Get an in-depth, technical look at #VileRAT, a sophisticated Python-based malware believed to be the work of the #Evilnum threat group.
Read our latest #threatresearch report here: stairwell.com/resources/tech…

Thrunthog retweeted

Ruining Ransomware Redux -- today's not just about DOJ v. ALPHV -- here's the recording of the Stairwell threat team's disruption of a Kuiper ransomware gang affiliate.

Last week, @saintX and @silascutler joined up for a chat on #Kuiper #ransomware, detailing how they operate, what's so interesting about this new group, and how to get your hands on #decryption keys.
Watch the full discussion here: stairwell.com/resources/kuip…
Thrunthog retweeted
The Stairwell research team acquired a copy of a server believed to be used by the devs of #Kuiper #ransomware, which includes source code, decryption keys, control tooling, and exfiltrated data, providing us with a comprehensive view. Get the full report: stairwell.com/resources/kuip…