

Computer security and privacy, lately focused on traffic analysis. Researcher at @kaucs, member @torproject, member @dfri_se. I mostly like and retweet.
Karlstad, Sweden
Joined October 2009
- Tweets1.1K
- Following1K
- Followers304
- Likes12.5K
Pinned Tweet
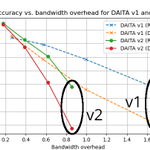
Posted some technical details on DAITA v1 and v2 defenses together with @mullvadnet to celebrate the broad deployment of v2 🚀

ALT DAITA v2 provides the same level of protection as v1 but with half the average bandwidth overhead
2
2
226

Klockrent: #ChatControl är som att tvinga människor att sitta på bilbältet. Tekniskt sett är bältet där fortfarande, men poängen försvinner liksom...

It "doesn't break encryption" in the same way that forcing people to sit in front of their car safety belt rather than strapping it around them doesn't break the strength of the belt.
1
3
201
Good take. Having cost associated with surveilling people in a democracy is a feature, not a bug. Criminals will adapt, leaving us worse off. Even if you think this won't be abused in the EU, the EU is speedrunning mass-surveillance infrastructure for a large chunk of the globe..

The "chat control" law is a big step for EU
A big step, towards an Orwellian totalitarian ideology
Essentially forbidding the use of end-to-end encrypted communication will have many consequences
It won't do much to fight crime, since criminals will use secure communication channels regardless of what the law requires
It will, however, make it much easier for OTHER nation states as well as cyber crime groups, to do mass surveillance against regular and law abiding citizens of your nation, including people in a position of power in politics as well as business
It's ludicrously naive to believe that such powerful capabilities for mass surveillance will not be targeted and successfully compromised by your adversaries
It is similarly naive to believe that such mass surveillance capabilities will never be abused "internally" by political leaders, business leaders as well as just random IT staff in the various tech companies that are responsible for implementing and managing the access to this capability
Protecting against the "bad guys", as well as national security threats, is important. Leveraging offensive technology in order to do so in a targeted manner (and at a cost, automatically contributing to limiting the use to cases that matter) is sometimes necessary
Introducing capabilities for mass surveillance at scale is a completely different story, however. Saying that this is not the "intended" use of the capability in question means nothing
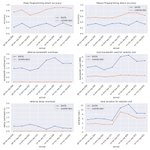
I evaluated using the first eight production servers from @mullvadnet running the new DAITA feature as a Windows user. The results are below.

1
3
106
Whenever I see differential privacy being used, I read it as some group of people being "differentially f***ed". This is a great thread on how some tools from our community are used for privacy washing. Cannot see the forest for all the trees, textbook example.

The critical point here is that the resulting models are a *massive* privacy threat to users. Your data might not reveal your embarrassing or deeply private preferences. But the resulting model might be able to determine exactly what you like. Its existence destroys your privacy.
1
81
This press conference speech by Josep Borrell captures the humanity of the ongoing war so well.
newsroom.consilium.europa.eu…
67
I run a default bridge and a middle/guard relay for @torproject at @KAU since many years with little friction. Happy to contribute to a better Internet both in research and practice, improving cybersecurity for all. Hoping to expand our contributions in the future 🧅🚀

Universities are the perfect place to run a Tor relay. Let's get more universities to do it. eff.org/deeplinks/2023/08/an…

Underskattar vilken shit show Telekom-stacken är mot Signal. Det finns problem kring trafikanalys i Signal av kvalificerade aktörer men det måste ställas mot att 14-åring med mammas kreditkort kan dra SIM-swap+massiva antaganden att mobilnätet är gjort för annat än att bli ägt
This Post is from an account that no longer exists. Learn more
380
Earlier this week I started my vacation project with the goal of learning Rust. It's a beautiful language and I've been surprised by how smooth it has been. This video aptly captures part of why.

1
4
Yes, Tor is made for this. If point 1 is a problem, consider requesting a bridge in Tor Browser. Not perfect by any means, but an improvement over a persistently known IP connection to a VPN. If Tor not an option, use @mullvadnet .

Forget which VPN providers you can trust from a business standpoint. Assume Russian intelligence is monitoring network traffic at a telco level and can see:
1. Who is connecting to VPN servers from inside of Ukraine
2. Many VPN exit nodes
@campuscodi is right - use Tor
3
Told earlier today that I can't buy students coffee+cake for the first in-person colloquium with two international guests in two years... Just not allowed. God forbid they get a ~3€ gift! An admin is now double-checking with another admin...
We can’t even buy pizza for our grad students anymore using gift funds, unless we eat it 100 miles away. I understand why so many of my colleagues are leaving for industry.
1
Feeling privileged: just got my second Moderna shot. Amazing what society can accomplish 🙂 here's to contributing back! 🍻
3
Want to do a PhD around cybersecurity and network measurements of DNS? Look no further for a great position together with @stiftelsen . Loads of flexibility for the direction, e.g., why not around @DNSPrivacyProj ?
kau.varbi.com/en/what:job/jo…

Please apply for a fun opportunity with an excellent industry partner in the area and good working conditions for research studies studyinsweden.se/plan-your-s…
This Post is from an account that no longer exists. Learn more
A really solid thread worth reflecting over. Fun academic exercise is to map to venues and look for gaps.

More and more folks want to hire privacy engineers. This is great! You almost certainly need them! But, just like security, privacy engineering is a whole field.
So for the folks who want to hire or become a privacy engineer, a rundown of the current rough types I see. (Big🧵)
1
The highlight of this year for me research-wise:
blog.torproject.org/new-low-… work with @real_rgdd, funded by @stiftelsen and @KKStiftelsen
We just started a new project on correlation attacks on Tor funded by @IIS! Project page and a short introduction to traffic analysis attacks on anonymity networks here: pylls.github.io/CAT/ @kaucs @torproject
Tackar och bockar! nitter.cf/stiftelsen/status/9966…

Vi delar ut 1,4 miljoner kronor till fem nya teknikprojekt! Bland annat till Pjodd som jobbar för fri internetåtkomst i Malmö, en teknisk lösning för att skydda internetanvändares personliga integritet och förbättringar av anonymitetstjänsten Tor: iis.se/press/pressmeddelande…
