

not around here anymore lol. previous statements may not represent me correctly anymore
it/its | she/her
Joined November 2018
- Tweets42K
- Following3.3K
- Followers2K
- Likes102K




hi @starlabs_sg! first, congrats on the shell on issues.chromium.org/issues/5…!
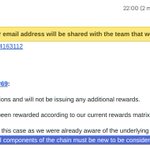
heartbreaking news: google likely wont pay you the fullchain bonus that you're hoping for :(
we're in the same boat: pvr upstream known but unpatched bug w/ angle bypass. they dont wanna pay for that
1/2
if you wanna take a look at how my chain like that worked: issues.chromium.org/issues/5…
also, as the thread says, this is not explicitly stated in the rules but they still refuse to pay out. if you wanna get in contact to try to do something about this feel free to dm though! 2/2

lexi <img src=x onerror=alert(1)> retweeted
Illinois Senate: Kirk (R), Giannoulias (D) Still Neck-and-Neck... www.rasmussenreports.com/illinois
lexi <img src=x onerror=alert(1)> retweeted

Kirk Street Suspect: ESCAMBIA - He was shot in the neck while trying to protect his home now deputies say th... http://tinyurl.com/3ytggdc
lexi <img src=x onerror=alert(1)> retweeted

@cubsncards @BullsBlogger LOL! I didn’t even notice Hinrich! Watch that neck, Kirk!
using cuckbrowser.com on cucklinux.com 💪


reported a chrome fullchain (web -> shell) on pixel 10 to google. got a 9.6 cve (cve-2026-87464) and a fix in chrome.
now they bend the rules and refuse to pay the fullchain bonus bc one of the vulns in the chain was an unpatched nday. total payout: $2.5k. despite cve + shell :|
update: appealed the decision and they denied it because of this "rule".
"Demonstrations of exploits against an active release of a Stable or Beta build of Chrome" is what it says in the rules at bughunters.google.com/about/…. nothing about everything being new. they just made that up

lexi <img src=x onerror=alert(1)> retweeted
i asked personally and got a signed response!!! pastebin.com/UdPZ2DYx