

The ETH must flow
🚀
Joined March 2018
- Tweets5.4K
- Following1.4K
- Followers1.6K
- Likes63.2K




Culgin.eth | Justmy2.gwei retweeted

Calling contracts across chains with EEZ just got a lot easier: there’s now an EEZ tab in @EthereumRemix 🎉
Deploy your contract, give it a cross-chain proxy, and call it from the other chain like it lives right there. Your L1 and rollup contracts can call each other in the same transaction!
Culgin.eth | Justmy2.gwei retweeted

Next Spring @GnosisChain will relaunch as an Ethereum Economic Zone.
It will be the first of a new kind of rollup. Still with app-chain cost, speed, and scalability, but also synchronously composing with @ethereum.
We're calling on protocols and applications to see what that unlocks for you. Check out the demos that @etheconomiczone just shared (in QT).
For us, it's been a journey. And now we're coming home.
It's time to make it EEZ.

We don't want to keep anyone waiting, so here is a very quick cut of today's live demos from @eduadiez and @tw_tter . Plus a little bonus footage on demo 2.
We hope you're as excited as we are.
Full recording to follow.
nitter.cf/etheconomiczone/status…
Culgin.eth | Justmy2.gwei retweeted

No regulated bank has ever been this transparent
And Binance did this voluntarily

Tremendous public service from Binance to publish this.
Take your time to read it. Make all your engineers read it. In fact, anyone you know who works in tech, have them read it.
This was the largest single heist in human history, $6B+, and it happened through mundane channels.
The Internet is now going to be full of AI-accelerated social engineering toxic sludge, and it's your job to be hypervigilant. Build your infrastructure in a way that assumes it will get compromised. Make sure you have AI-powered monitoring 24/7 and a "shut it all down" killswitch in case you ever need to go nuclear. The stakes are too high to be scrambling in the moment the way it seems Binance was during this attack.
Culgin.eth | Justmy2.gwei retweeted

TLDR: If DPRK are reading this, they should be saying "time for round 2".
Takeaways:
- critical infra engineers are free to download arbitrary software on work laptops.
- the day-to-day work setup can connect to billion dollar signing environments.
- no human oversight or physical confirmation for moving 10-figs of value / EIP-7702 code change.
- various AI vibe-based tools running in corp environments doing god knows what except serving as a remote compromise surface, framed as a good thing btw.
- none of the above labelled as the problem.
- instead, reads as blaming employees for falling for social engineering, and anti-virus not catching the malware. This is a dog-ate-my-homework level excuse deployed after a nuclear-failure level event.
Sincerely hoping binance have more reloads available to cover the next losses too. Reaching exchange hot wallets will never be near impossible, but it should not be this easy either.


Sometimes people wonder why it's always crypto exchanges/companies getting hacked. The truth is every company can get hacked but if the flow of funds can't be seen onchain, they are often just covered up

ZachXBT: French Bank Crédit Mutuel Arkéa Allegedly Lost Over $133M in Crypto Theft
On-chain investigator ZachXBT disclosed on November 4 that the financial institution allegedly affected by a crypto theft exceeding $133 million is Crédit Mutuel Arkéa, a French banking group with approximately $235 billion in assets. ZachXBT previously reported that an EU-based entity was suspected of losing more than $106 million from multiple centralized exchange accounts on November 1. The suspected attacker withdrew funds in USDC and USDT before swapping assets into ETH and privacy coin XMR and transferring funds across multiple blockchains.


The biggest exchange heist in history but no user lost any funds, price action held support, and the worst-case scenario didn't materialize.
If such a major incident can't nuke the market, what makes bears think their November doom thesis will?
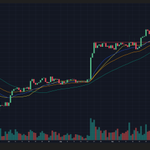
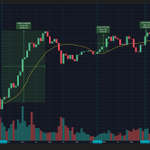
There are certainly some similarities between now and Mar 2023 on the 3-day chart.
What if?🤔
ethereum:native


ethereum:native just closed the monthly. While some are panicking over a bearish engulfing candle, I see a clean test of the 12M SMA and 0.618 Fib holding as support.
October wasn’t nearly as bad as bears predicted, so naturally the goalposts move to November.
Let them cope. Bullish on ethereum:native 🐂


Culgin.eth | Justmy2.gwei retweeted

The scale of the danger North Korea poses to crypto has become impossible to ignore.
This is the story of the investigators exposing North Korean operatives working inside the industry.
You think you know who your developer is.
But do you?
🎬 Introducing THE DEVELOPER.
Culgin.eth | Justmy2.gwei retweeted
这次币安被黑,不是 EIP-7702 本身的锅,
它只是被用上了。
它是被黑客用来更高效地执行这次攻击的工具之一,
不过,不是被黑的原因。
黑客利用了 EIP-7702 的委托能力,
让扫款操作更顺畅、更批量、更原子化。
不过,
真正让资金被转走的,还是签名权限被拿到了(热钱包被攻破、内部签名通道被入侵等)。
具体一点来说,
从链上看,
攻击者提交了 50 个由 Binance 14 私钥签过的 EIP-7702 授权,覆盖连续的 nonce。
其中一个命中了当时的 live nonce,
把热钱包的代码委托给了攻击者事先部署的扫款合约。
随后一笔交易就把 ETH + 63 种代币(含 16.15 亿 USDT)一次性扫走。
不过,如果没有 Binance 14 的有效签名,EIP-7702 根本用不上。
这也是为什么比特币侧同样被洗(比特币没有 7702),
被黑原因目前看,指向签名系统/热钱包密钥通道被突破(可能是 HSM/MPC/内部签名接口被渗透,不一定是明文私钥被完整偷走)。


Wild to know one compromised laptop can result in such a massive breach
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…

Culgin.eth | Justmy2.gwei retweeted

Quick notes on 7702 to dispel fud and keep your funds safe.
First thing first -- 7702 itself isn't broken. Don't panic if you are using a wallet that supports 7702 (MetaMask, Uniswap, Ambire, etc.).
To recap, 7702 is an account abstraction EIP that allows an EOA to sign a special message, called a "7702 authorization," that would insert a smart contract into the account, which enables the account to do powerful things like transaction batching, e.g. doing "approve" and "transfer" in one transaction so you can swap on Uniswap with one click.
But unfortunately the same feature also allows a hacker to efficiently move all your tokens in one single transaction. In the Binance hack, the hacker moved ETH, USDT, and 62 other tokens in one transaction, whereas without 7702 they'd have had to send one transaction per token. In this particular case, many of those transactions would've failed because Binance was still using the hacked wallet for withdrawals, so all transactions sent by the hacker would've had to compete with the legit transactions for nonces. So using 7702 did help the hacker steal as much funds as possible, as quickly as possible. Ouch!
However, in order for the hacker to use 7702, they must have either 1) had access to the private key, or 2) tricked Binance into signing a 7702 authorization. The latter is very unlikely, as it's hard to imagine Binance being so incompetent as to expose an endpoint for signing 7702 authorizations or (even worse) for signing raw messages which the hacker could've repurposed for 7702 authorizations. But I can't rule that out until the official postmortem.
What does all this mean for you?
- If you are a wallet developer, do NOT, under any circumstances, expose a way for third parties to request 7702 authorizations. This is just handing your users a giant footgun to shoot themselves with. No wallets I know of do this, so don't worry if you are a user.
- If you are a user, use a well-known wallet. 7702 does let wallet developers screw up in more ways than before, so use only well-known wallets whose developers' competence you can trust.
- If you are a company (e.g. an exchange) operating hot wallets, do NOT, under any circumstances, expose an endpoint (even if it's an internal endpoint) for signing 7702 authorizations or raw messages.
As a contributor to AA, I feel partially responsible for hacks like this, since by increasing the power of accounts, we've indeed also empowered hackers (not unlike how any new technology empowers both the good guys and the bad guys). That said, it's important to note that 7702 was only a transitional EIP, and "endgame AA" such as Frame Transactions (EIP-8141) would allow wallet owners to set up their wallets much more securely. For example, if Frame Transactions were available today, Binance could've:
- Set up their wallets as multisig contracts only (not EOAs).
- Set up "post conditions" for their `transfer()` functions, so that even if the multisig got hacked, the contract itself would perform sanity checks such as "no transfers of more than 1000 ETH without additional signers."
In short, the endgame of Ethereum UX is one with both optimal security and optimal UX, and users never have to trade off between the two. But we still have a long way to go until we get there. Back to work!
Culgin.eth | Justmy2.gwei retweeted

Seeing rumors blaming EIP7702 for the Binance hack.
From what I can see EIP7702 was just used to preform the hack efficiently but was NOT the root cause.
Good for Ethlabs and therefore good for $ETH

Today, more people are backing Ethlabs.
Ethereum co-founder @MihaiAlisie joins as an anchor funder, @payward and @gattacahq join as contributors, and 19 new supporters from the Ethereum community are now backing our mission.
Thousands of people across the world have spent years building Ethereum and holding $ETH, we aim to honor their commitment by becoming an open, accessible, and user-focused organization that supports the development of both this unstoppable network and its immutable asset.
We care deeply about what makes Ethereum special: its credible neutrality, security, censorship resistance and openness. We also believe that Ethereum's potential is only realized when people use it at scale and when it remains the natural place to innovate, issue assets, hold + settle value, and be the home to a digital future its users can own.
A big thank you to our initial anchor funders @BitMNR, @Sharplink, and @ethereumJoseph; to everyone joining us today, to the countless people and organizations that make Ethereum possible, and to all who have supported our work so far.
There is an enormous amount left to do, and we are fortunate to have so many people who believe that it is worth doing.
Now back to work.
Funders: ethlabs.org/funding
Weekly updates: ethlabs.org/writings
