

NGO Director https://nitter.cf/t.co/534IpYYmta | Security Researcher
internet
Joined October 2020
- Tweets1K
- Following478
- Followers5.1K
- Likes2.5K



Pinned Tweet
CVE :- 2021-34506 , 2021-38641 , 2021-38642
CVE-2021-38642
msrc.microsoft.com/update-gu…
CVE-2021-38642
msrc.microsoft.com/update-gu…
CVE-2021-34506
msrc.microsoft.com/update-gu…
@MrRajputHacker , @tirtha_mandal ,@Th3Pr0xyB0y
#bugbounty #MSRC #Microsoft #Cybersecurite #infosec #Security

ALT CVE :- 2021-34506 , 2021-38641 , 2021-38642 CVE-2021-38642 https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2021-38642 CVE-2021-38642 https://msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2021-38642 CVE-2021-34506 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2021-34506 @MrRajputHacker , @tirtha_mandal ,@Th3Pr0xyB0y #bugbounty #MSRC #Microsoft #Cybersecurite #infosec #Security
👾 The Great War Is Not Won By Money, Power, Or Networks... It Is Won By Strategy, Expertise, And Determination.
Shivam Kumar Singh retweeted

I can refer for a Senior iOS Developer role.
If you’ve got 5+ years of iOS experience and want a referral, DM me your resume.
No spam, just genuinely trying to help good engineers get seen.
Shivam Kumar Singh retweeted

Once we have completed our review for security vulnerabilities, we will make the entire codebase of 𝕏 open source, with no exceptions.
Moreover, we will invite third party reviewers to examine the system that is running to confirm that the open source code is what is running.
Trust through total transparency is the only thing that should be believed.
Shivam Kumar Singh retweeted

Alleged GitHub internal source code and ~4,000 private repositories are reportedly being offered for sale on a dark web forum by the threat group “TeamPCP.”
The leaked screenshots appear to reference GitHub Actions, enterprise APIs, billing systems, repository security tooling,

To fix triage delays, platforms should add smart limits: priority after 10 reports, fast-track for new hunters, and flag AI spam based on valid/report ratio Hunter profile.
@Hacker0x01 @Bugcrowd
This Post is from an account that no longer exists. Learn more
Trust the device = Game over.


Hacking the #EU #AgeVerification app in under 2 minutes.
During setup, the app asks you to create a PIN. After entry, the app *encrypts* it and saves it in the shared_prefs directory.
1. It shouldn't be encrypted at all - that's a really poor design.
2. It's not cryptographically tied to the vault which contains the identity data.
So, an attacker can simply remove the PinEnc/PinIV values from the shared_prefs file and restart the app.
After choosing a different PIN, the app presents credentials created under the old profile and let's the attacker present them as valid.
Other issues:
1. Rate limiting is an incrementing number in the same config file. Just reset it to 0 and keep trying.
2. "UseBiometricAuth" is a boolean, also in the same file. Set it to false and it just skips that step.
Seriously @vonderleyen - this product will be the catalyst for an enormous breach at some point. It's just a matter of time.

The biometric authentication of the #EU #AgeVerification app can be easily bypass too...
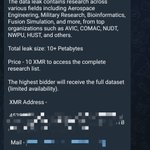
China Got Hacked 🇨🇳
Sample is out, 10PB claimed.
Where did he store it? God knows…
Or maybe he never did - just selling panel access.
~/Welcome to modern cyber warfare.
#CyberSecurity #ThreatIntelligence #DataBreach #Darkweb #InfoSec #DigitalSecurity #CyberDefense


Shivam Kumar Singh retweeted

🚀 Excited to share the most inspiring work I’ve been part of this year:
"Learning to Reason without External Rewards"
TL;DR: We show that LLMs can learn complex reasoning without access to ground-truth answers, simply by optimizing their own internal sense of confidence. 1/n

Shivam Kumar Singh retweeted

01110100 01101111 01110101 01100011 01101000 00100000 01100111 01110010 01100001 01110011 01110011 00100000 01101001 01100110 00100000 01111001 01101111 01110101 00100000 01100011 01100001 01101110 00100000 01110010 01100101 01100001 01100100 00100000 01110100 01101000 01101001 01110011
Shivam Kumar Singh retweeted

I’ve been facing a serious, recurring safety issue with my @VolkswagenIndia virtus car from the very first day of delivery. Despite multiple complaints and service visits, nothing has been fixed and now it has caused a major highway accident. Sharing everything here 👇
Today, humans create AI. One day, humans will create ways to destroy it.
Money is flowing into building smarter machines and soon, it will flow into controlling and dismantling them.
It’s the circle of innovation: every creation brings its own counterforce.
Once, people learned not to share personal details on WhatsApp or social media.
Soon, people will learn not to share everything with AI.
We keep teaching machines to think but maybe it’s time to teach ourselves to trust wisely.
#AI #Future #Technology #DigitalAwareness
Shivam Kumar Singh retweeted
🇷🇺 Russian Authorities Arrest 3 Developers of Meduza Stealer Malware
In a rare move, Russian police have arrested three IT experts behind the Meduza Stealer malware. Authorities raided their homes after the malware was linked to an attack on a Russian regional organization.
Shivam Kumar Singh retweeted

Great to speak with India PM @narendramodi @OfficialINDIAai to share our plans for the first-ever Google AI hub in Visakhapatnam, a landmark development.
This hub combines gigawatt-scale compute capacity, a new international subsea gateway, and large-scale energy infrastructure. Through it we will bring our industry-leading technology to enterprises and users in India, accelerating AI innovation and driving growth across the country.
Shivam Kumar Singh retweeted

I don't belive this is accurate (way too high).
I also don't think it matters.
What matters is how many people we can help, and by how much.
Make a world a little bit better than before I arrived.


Shivam Kumar Singh retweeted

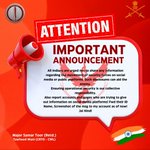
#OperationSindoor on the games field.
Outcome is the same - India wins!
Congrats to our cricketers.
I think HackerOne should create a role in the company Job profile called 'Hacker Success,' similar to a Business Customer Success role.
It's really disappointing to see great community contributors like @YShahinzadeh and @h4x0r_dz get banned.

@Hacker0x01 is now banning people without explanation or providing how the terms and conditions were violated. While other platforms are advancing, H1 revolutionary new vision is to track hackers on social media, make assumptions and ban them without a real proof.

