

Security Solutions Engineer | Agentic AI security. Building @securegraph_AI
lagos nigeria
Joined December 2014
- Tweets10.4K
- Following2.5K
- Followers1.5K
- Likes72.7K




Pinned Tweet
Weirdly, I want to buy a warehouse, set it up with internet access via starlink, and make people access it for free, as long as you have a verifiable project you are working on.


P.H.A.N.T.O.M F.O.R.T retweeted

"If the pipeline cannot prove it, the pipeline does not ship it." Chaim Mazal, CISO, GitLab.
Why security belongs in the pipeline: blog.phantixlabs.com/posts/t…

P.H.A.N.T.O.M F.O.R.T retweeted
Risky actions wait for a second person. Findings are proven before they reach you. Fixes are retested.
25 beta places, free, no card: platform.phantixlabs.com/reg…

P.H.A.N.T.O.M F.O.R.T retweeted
One annual pentest covers about 15 days of the year. Roughly 350 go unwatched.
Why security has to move into the pipeline: blog.phantixlabs.com/posts/t…

P.H.A.N.T.O.M F.O.R.T retweeted
A yearly pentest watches about 15 days. The product changes on the other 350.
Keep the deep test. Add a check on every change: blog.phantixlabs.com/posts/t…

Most teams run one pentest a year. Useful, and a sample: about 15 days of coverage. The product changes on the other 350.
Our write-up: blog.phantixlabs.com/posts/t…

P.H.A.N.T.O.M F.O.R.T retweeted
The SecureGraph beta is open: 25 places, free, no card.
Register, tick Join the beta, then connect your security database. That is when your place is confirmed.
platform.phantixlabs.com/reg…


After years of delulu.
I will be getting an iPhone for this codebase audit.
The current has forced my feet after all, and I am having to go with the flow.
P.H.A.N.T.O.M F.O.R.T retweeted
To the security lead at a lean team: your product changes every week. Your security should keep up.
The SecureGraph beta has 25 places. Free, no card: platform.phantixlabs.com/reg…
The SecureGraph beta is open, with 25 places.
platform.phantixlabs.com/reg…
The SecureGraph beta is open. 25 places, free, no card.
A place is confirmed when you connect your security database, so the places go to teams who actually run it.
platform.phantixlabs.com/reg…

P.H.A.N.T.O.M F.O.R.T retweeted
Software ships faster than ever, but most pentest reports still describe January. SecureGraph tests continuously, proves each finding before you see it, and holds every risky agent step for a human.
phantixlabs.com

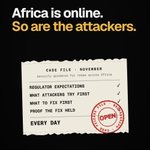
Africa is online. So are the attackers.
Every day this November, SecureGraph opens the case file: what regulators expect, what attackers try first, and how to prove the fix held.
phantixlabs.com

P.H.A.N.T.O.M F.O.R.T retweeted
To close the month: you cannot protect what you cannot see. Keep a list of everything you own, with an owner for each. SecureGraph will find it, test it and prove every fix. Launching soon.
#CybersecurityAwarenessMonth #CyberSecurity #Africa


For a whole month I was writing conditional statements, after stacking multiple yamls.
The hard part is the LLM now making decisions mid turn and deviating from all these just to arrive at a split second solution using less tool than provided.

