

Access Role Holder of @ConcreteXYZ Contributor of @fhenix
Joined March 2025
- Tweets4K
- Following574
- Followers449
- Likes5.5K




Pinned Tweet
@fhenix goes beyond encrypted computation by rethinking key custody and decryption. With Intel TDX, remote attestation, Shamir Secret Sharing, and future Threshold MPC, it aims to reduce single-party trust and build a more secure foundation for confidential DeFi.
@deivonchain
🤖 Made with AI

Suma Begum retweeted

me: ai wont change a logo because of its safety policies
some random 7th grader after reading the @GoogleCloudSec report: got it, so we make the ai read security patches and write exploits
cloud.google.com/blog/topics…
tl dr: google found a tool used by attackers that compares software updates, looks for the vulnerabilities they fix and automatically tries to exploit them before everyone updates
Suma Begum retweeted

Atlas is 6 feet 2 inches tall and weighs 198 pounds. Most people at CoRL didn't realize how big that is until they were standing next to it.
Here's what else we noticed at the @BostonDynamics booth:
Suma Begum retweeted

Exactly this is the point most people miss when they talk about privacy on chain. Institutions do not need secrecy for its own sake. They need control. They need to be able to move size without broadcasting intent to the whole market, and then prove what happened when compliance asks. That is the impossible tradeoff that has kept serious capital on the sidelines for years. Fully public works for transparency but it leaks alpha. Every position becomes visible. Every rebalance becomes a signal. Competitors can front run you. Counterparties can price against you. It is not a level playing field, it is an open book that punishes size. Fully private solves the leak but creates a new problem. If no one can verify anything, how do you pass an audit. How do you show regulators, investors, or partners that the numbers are real. Privacy without proof is a dead end for any regulated fund, bank, or treasury. Dual mode is elegant because it refuses to choose. One token. One pool of liquidity. One integration for builders. Private by default when you are executing, public when you need to disclose. You get discretion during the trade and accountability after it. No split liquidity. For liquidity providers this matters too. Depth stays unified, pricing stays tighter, and builders only integrate once. This is how privacy becomes infrastructure, not a niche feature. Institutions adopt what gives them safety and compliance together at scale. @fhenix

Suma Begum retweeted

Blockchain's next evolution won't be defined by transparency alone. Privacy will matter just as much.
This is where @Fhenix is working on something meaningful.
On traditional public blockchains, balances and transactions are visible to everyone. But real financial systems need room for confidentiality.
With Fully Homomorphic Encryption (FHE), Fhenix enables computations directly on encrypted data without exposing the underlying information.
Its Dual-Mode Tokens take this concept further, allowing users to switch between public and confidential balances while maintaining the same asset, liquidity, and DeFi composability.
What makes this approach interesting is that privacy doesn't have to mean isolation from the broader blockchain ecosystem.
Transparency for verification. Privacy for execution.
That's an important direction for the next generation of Web3, and Fhenix is helping build it. @Asterix54907294 @deivonchain
🤝 Paid partnership · 🤖 Made with AI

Suma Begum retweeted

Today ⏳ - 7pm UTC
@arbitrum × @fhenix live on space 🚀
Real knows real for the OGs
Explore @fhenix product -> genesis.fhenix.io
Bring your questions on space.


Suma Begum retweeted

There’s a beautiful word in Japanese 🇯🇵
奇跡 (きせき)
Kiseki – Miracle.
Sometimes, miracles aren't grand or extraordinary. They can be a little bee resting among flower petals, a ray of sunshine slipping through a window, or a peaceful moment we happen to stumble upon.🌷🍂☘️🍁🍃
Life is always full of little wonders. We just need to slow down enough to notice them. 🌸🐝♡


Anyone else learning Japanese so you can visit Japan 🇯🇵 one day without needing Google Translate? 😂
At the very least, I hope I’ll be able to confidently order a cup of coffee! ☕️
For me, the hardest part of learning Japanese is probably Kanji. They look so beautiful, but memorizing them is a whole different challenge! 🥹📚
Let’s keep going, fellow Japanese learners! 🌸

Suma Begum retweeted

A warm fire, a peaceful night, and a little friend to cuddle with. 🐱🔥❤️
Sometimes, happiness is just this simple.
Good night, everyone. Sweet dreams! 🌙✨
Thank you all so much for your kindness and support today. ❤️
See you tomorrow! I hope I can continue to count on your kindness and support.
🐾🐾🐾🥰🍀🙏🙏🫶🫶🫶🐾🐾🐾

Suma Begum retweeted

The Missing Infrastructure Behind Physical AI: Why PrismaX Matters
The robotics industry has made impressive progress in hardware and artificial intelligence.
Humanoid robots can walk, manipulate objects, and perform increasingly complex tasks. But one major challenge remains:
How do robots actually learn to operate in the real world?
A powerful robot is not automatically an intelligent robot.
Physical environments are unpredictable. Objects have different shapes, surfaces, weights, and positions. Real-world tasks require more than visual recognition; robots need practical experience and the ability to adapt.
This is where PrismaXai takes a different approach.
Instead of focusing only on building robotic hardware, PrismaX is developing the data infrastructure behind Physical AI.
Its approach connects three important elements:
1. Teleoperation
Human operators remotely control robot arms and humanoids, demonstrating how physical tasks should be performed. These demonstrations become valuable training data.
2. Egocentric Data
First-person recordings capture how humans interact with everyday environments. This gives AI researchers another perspective for teaching machines real-world skills.
3. Robotics Data Infrastructure
PrismaX brings together collected demonstrations, quality evaluation, and accessible datasets to support teams developing Vision-Language-Action models and robotics foundation models.
The scale is also worth watching:
- 5,000 hours of monthly collection capacity.
- 1,700+ deployed scenarios.
- 120,000+ episodes delivered.
- More than $1 million paid to contributors.
The bigger picture is interesting.
Robotics needs more than advanced machines. It needs diverse experiences, reliable demonstrations, and high-quality training data.
PrismaX is working on that missing layer.
Because the future of robotics won't depend only on how robots are built, but also on how effectively they learn.
🤝 Paid partnership · 🤖 Made with AI

Suma Begum retweeted

How Primus Could Make the Internet Verifiable Without Exposing User Data
The internet generates massive amounts of data, but verifying its authenticity without compromising privacy remains a challenge.
Web3 applications often depend on external sources, APIs, and oracles to access real-world information. However, sharing complete records can expose sensitive user data.
This is where primus_labs brings an interesting approach.
1. zkTLS: Making Web2 Data Verifiable
Primus uses zkTLS to connect Web2 information with Web3 applications through cryptographic proofs.
Users can prove specific claims, such as exchange trading volume, financial eligibility, or account ownership, without unnecessarily exposing complete records.
2. zkFHE: Privacy-Preserving Computation
Primus also explores zkFHE, combining Zero-Knowledge Proofs with Fully Homomorphic Encryption.
FHE enables computations on encrypted data, while zero-knowledge proofs help verify claims without revealing unnecessary information.
Together, these technologies aim to make private information useful and verifiable.
3. What Could This Unlock?
- DeFi: Privacy-preserving financial verification.
- Identity: Proving credentials without exposing personal records.
- AI: Accessing trustworthy external information.
- Reputation: Building trust through verifiable proofs.
The Bigger Vision
The future of digital trust shouldn't require exposing personal information.
Primus is exploring how zkTLS and zkFHE can make verification more private and practical.
Prove more. Reveal less. That's the future of digital trust.
🤝 Paid partnership

Suma Begum retweeted

A secure Bitcoin network does not automatically make every Bitcoin-based financial application under it secure.
@utexocom is building infrastructure to bring existing USDT liquidity onto Bitcoin through RGB, with its Mint infrastructure connecting external networks to Bitcoin.
But bringing USDT across these networks involves more than just making the asset transferable. From the moment USDT is deposited and locked on its source network to the minting, validation and eventual redemption of its Bitcoin-based representation, every stage depends on secure infrastructure.
The contracts managing the assets, the signing mechanisms authorising operations and the systems validating transactions must all work as intended.
So who is checking each layer at Utexo ? That's where @0xorio and @ValkyriSecurity step in.
🔹Oxorio
Oxorio audited the Utexo Bridge's smart contracts, enclave signer and burn signer. The reports are now public, with the findings documented, and according to Utexo, most of the security findings were fixed and the rest acknowledged.
🔹Valkyri Security
Unlike Oxorio, Valkyri is a long-term partner for ongoing reviews across the wider stack, covering smart contracts, TEEs and Web2 components, including the AWS Nitro Enclaves behind minting.
When real dollar liquidity moves between networks like in the case of Utexo, every system involved becomes part of the trust users place in the infrastructure. That's why Utexo has long-term independent scrutiny on the contracts, the signers and the layers around them.
@marvelboyHaRSH

Suma Begum retweeted

They call me a monster, but I was once a prince. 👑
The Devil's kiss gave birth to two serpents upon my shoulders. 🐍
They feed on human brains 💀 — the source of human thought, ambition, and greed.
Now I sit upon the throne.
I am the Serpent King — Zahhak. And I am watching.

Suma Begum retweeted

When Encryption Changes Smart Contract Security
Most smart contract security models are built around one assumption: a contract can read its own state.
But what happens when even the contract cannot see the balances, transaction amounts, or financial conditions it needs to process?
This is where @fhenix introduces a fundamentally different security challenge through Fully Homomorphic Encryption (FHE) and its CoFHE infrastructure.
Traditional Solidity relies heavily on visible conditions:
"require(balance >= amount);"
If someone tries to transfer more than their available balance, the transaction reverts.
But confidential computation changes this entire approach.
1. Privacy changes how failures must work.
In an encrypted environment, a contract cannot directly inspect an encrypted balance or determine whether a secret condition is true.
Even a transaction failure can become an information leak. If a transfer reverts specifically because someone has insufficient funds, that public outcome could reveal sensitive financial information.
Fhenix addresses this through encrypted conditional computation, allowing the contract to evaluate possible outcomes without exposing which condition was satisfied.
2. A successful transaction does not always mean a successful transfer.
This is one of the most interesting differences.
In conventional ERC-20 systems, a successful transfer generally means the requested operation was completed.
With confidential transfers, the transaction can execute without revealing whether the full amount was actually transferred.
That means developers must carefully design encrypted accounting, track actual transferred amounts, and ensure that credits, debits, and outstanding obligations remain consistent.
Security is no longer just about preventing invalid transactions. It is also about maintaining correct financial relationships without exposing private information.
3. An encrypted handle is not authorization.
This is perhaps the most overlooked security issue.
In CoFHE, encrypted values are represented through handles. A handle identifies an encrypted value, but possessing it does not automatically grant permission to access or use that value.
Imagine Alice's encrypted balance handle becomes visible through an event.
If another user can submit that handle to a poorly designed function without proper authorization, they might manipulate computations involving Alice's balance and potentially extract information through an account they control.
The encryption itself has not been broken. The vulnerability exists in access control and application logic.
This is why encrypted handles must be treated as references, not proof of ownership.
4. Security must be designed differently from the beginning.
Fhenix's collaboration with Consensys Diligence examined these challenges across confidential tokens, encrypted vault shares, OTC trading, and sealed-bid auctions.
The bigger lesson is that confidential smart contracts need more than traditional Solidity auditing.
Developers must rethink execution logic, failure handling, authorization, and financial accounting.
With CoFHE, computation can happen on encrypted data while the EVM maintains the verifiable structure of contract execution.
That creates opportunities for financial applications where balances, bids, and trading strategies remain private without sacrificing programmable onchain logic.
My takeaway:
Encryption protects information, but it does not automatically protect application logic.
The next generation of secure smart contracts will need to prove not only that data remains confidential, but also that every operation involving that data is properly authorized and financially correct.
That's the deeper security shift Fhenix is bringing to confidential DeFi.
Privacy is powerful. Privacy with correct security architecture is what makes it usable.
@deivonchain
@Asterix54907294
@0xkeksgiven
🤖 Made with AI

Suma Begum retweeted

Smart contract events can expose more than transactions, revealing trading strategies, financial relationships and user behavior. @fhenix uses FHE to keep sensitive data encrypted during computation while supporting programmable blockchain functionality without requiring complete
🤖 Made with AI

Suma Begum retweeted
Inside CoFHE Architecture: How Fhenix Makes Encrypted Computation Possible. Most blockchains have a transparency problem. Smart contracts can execute complex operations, but sensitive information is usually exposed during execution.
@fhenix is approaching this challenge differently through CoFHE, its Fully Homomorphic Encryption (FHE) coprocessor. But what actually happens behind the architecture?
Let's break it down.
1. On-chain layer: FHE.sol
Developers integrate Fhenix through a Solidity library.
Smart contracts can request encrypted operations without exposing the underlying values.
2. Task Manager and ACL
The Task Manager receives computation requests, checks permissions and creates handles representing encrypted results.
The Access Control Layer (ACL) determines who can access or use specific encrypted values.
3. Off-chain FHE Engine
This is where the actual encrypted computation happens,The Engine processes ciphertexts without accessing the original plaintext or holding the decryption key.
4. Commitment Registry
Each computation result is associated with a cryptographic commitment.
This creates a verifiable connection between the encrypted result and its onchain handle.
5. Threshold Decryption Network
When an authorized user requests a result, the decryption system coordinates access to key shares.
The goal is to prevent any single operator from independently controlling the decryption key.
6. Developer SDK
The cofhe/sdk handles client-side encryption, proof generation, access permits and decryption workflows.
Developers can integrate confidential functionality without building the entire cryptographic infrastructure themselves.
Why does this architecture matter?
CoFHE separates blockchain execution from encrypted computation while connecting both through verifiable handles and permission controls.
This creates opportunities for:
→ Confidential DeFi
→ Private trading strategies
→ Encrypted financial applications
→ Confidential token transfers
→ Privacy-preserving smart contracts
The bigger vision is simple:
Smart contracts should be able to compute on information without needing to see it.
That's the infrastructure Fhenix is building with CoFHE.
@Asterix54907294
@deivonchain @0xkeksgiven
🤝 Paid partnership

Suma Begum retweeted
Privacy deserves a creative touch
My artwork for @primus_labs represents a future where digital trust meets privacy.
With zkTLS and zkFHE, Primus is exploring ways to verify information, protect sensitive data, and bring privacy-preserving technology into Web3.
Verify more. Reveal less.
Building a more private internet, one innovation at a time.
Robotics intelligence doesn't emerge from models alone. It grows through a continuous loop: humans demonstrate, robots generate real-world data, and AI learns to become more autonomous. That's the infrastructure PrismaX is building for Physical AI.
@PrismaXai

Suma Begum retweeted
Transaction Privacy Is Not Enough. Blockchain Needs State Privacy.
Most blockchain privacy discussions focus on one question: Can we hide transaction details?
But there is a bigger question worth exploring: Can we keep the underlying application state confidential, even while smart contracts continue executing?
These are two different privacy challenges.
1. Transaction Privacy: Protecting What Happens
Transaction privacy focuses on limiting the information exposed when users interact with a blockchain. Depending on the implementation, this can protect information such as:
- Transaction amounts
- Sender and recipient details
- Financial activity
- Sensitive transaction inputs
The goal is to prevent unnecessary exposure of individual activities.
But hiding transaction details doesn't automatically make the entire application private.
2. State Privacy: Protecting What Exists
Blockchain state represents the information maintained by smart contracts. Think about a lending protocol. Even if a transaction is hidden, sensitive information about collateral, balances, credit positions, or financial strategies could still become visible through application state or related data. This creates another privacy challenge. Users need more than confidential transactions. They need applications capable of processing sensitive information without exposing it.
3. Where Fhenix Enters the Picture
This is where @fhenix deserves attention.Fhenix brings Fully Homomorphic Encryption (FHE) into smart contract environments.
FHE allows computations to be performed directly on encrypted data without first decrypting the underlying information. Through its confidential computing approach, Fhenix aims to help developers build applications where sensitive inputs and data can remain encrypted during computation.
Its CoFHE infrastructure also explores bringing confidential computation to EVM environments.
4. Why This Difference Matters
Consider what confidential state could enable:
→ Lending protocols that protect sensitive financial positions.
→ Governance systems that keep individual votes confidential.
→ Trading applications that reduce exposure of private strategies.
→ Applications that process sensitive information without revealing it to everyone.
These possibilities require more than hiding transaction histories. They require confidentiality throughout application execution.
5. The Bigger Picture
Public blockchains made transparency a fundamental feature. But transparency should not mean exposing every piece of user information. Transaction privacy protects individual interactions.
State privacy addresses the deeper challenge of protecting information maintained and processed by applications. The next evolution of blockchain privacy isn't simply hiding what users do. It's protecting the information applications need to function. That's the direction Fhenix is exploring with Fully Homomorphic Encryption.
The future of blockchain should allow computation without demanding complete visibility.
@Asterix54907294 @deivonchain @0xkeksgiven
🤝 Paid partnership · 🤖 Made with AI

Suma Begum retweeted
The next battle for USDT on Bitcoin is distribution, not issuance.
Getting USDT onto Bitcoin is one good milestone, no doubt about that. But making it accessible through wallets, trading platforms and applications that people already use in the BTC-fi ecosystem is another. Without those connections, even a working asset infrastructure has limited reach.
@utexocom knows this and is working on both sides of the equation. Here's how:
🔹Tether's Wallet Development Kit (WDK)
WDK gives developers the tools to build self-custodial wallets. Utexo has contributed RGB modules that WDK-based wallet developers can integrate to support Bitcoin-based assets.
In practical terms, a team building a wallet doesn't have to develop all the RGB functionality from scratch. It can simply use the existing on-chain RGB module to manage and transfer assets, with a separate RGB Lightning module, currently in beta, for Lightning transfers.
🔹UniSat
UniSat gives Utexo a route into an existing Bitcoin-native wallet and trading ecosystem.
The planned rollout starts with wallet and explorer support, followed by USDT trading on UniHexa, with financial services beyond trading planned after that. UniSat has already reported successful test minting, confidential transfers and redemption on Bitcoin Signet.
These are two different pieces of the stablecoin distribution puzzle in Bitcoin finance. WDK helps developers bring RGB asset support into their wallets without building from scratch, while UniSat could give users a familiar place to hold, transfer and eventually trade USDT on Bitcoin.
For Utexo, the work doesn't end when USDT can be minted on Bitcoin. Wallet integrations and trading venues are what can turn that technical capability into something people can seamlessly use every day.
Utexo is building issuance and distribution together, which is what turns USDT on Bitcoin into a working network.
@marvelboyHaRSH

Suma Begum retweeted
The Hidden Cost of AI Isn't Compute. It's Data Movement.
AI infrastructure is evolving rapidly, but one problem often gets overlooked: keeping data accessible wherever compute happens.
A powerful GPU is not productive when its workload is waiting for datasets to move, sync, or download from another environment.
This is where @shelbyserves is building something interesting.
Shelby, developed by Aptos Labs and Jump Crypto, is designed as decentralized hot storage for AI, agents, and distributed computing.
Its architecture focuses on three important ideas:
1. One Address, Global Access
Instead of repeatedly copying datasets between regions, Shelby aims to keep the same data accessible across supported locations as compute moves.
2. Performance Meets Verification
S3-compatible storage, low-latency reads, and cryptographic verification combine familiar developer workflows with verifiable data access.
3. Real Workloads, Not Just Promises
Shelby's Private Beta has brought real use cases from Teepin (enterprise AI), Pictor Network (distributed rendering), and PathPulse AI (spatial intelligence).
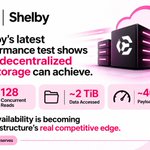
The November 10 performance update is particularly interesting: one gateway handled 128 concurrent reads, approximately 2 TiB of data, and around 46 Gbps of payload throughput.
The bigger opportunity isn't simply storing more data. It's reducing the friction between data and compute.
Token incentives and future rewards are worth watching, but confirmed distribution details should come before any assumptions about an airdrop.
My takeaway: The next generation of AI infrastructure won't be defined by GPUs alone. The data layer connecting those GPUs could be just as important.
@shelbyserves
@affinity_matrix

Suma Begum retweeted
Most people discuss FHE as the future of blockchain privacy.
But there is a problem few people discuss:
Can encrypted computation become fast enough for real financial activity?
This is where @primus_labs deserves attention.
Fully Homomorphic Encryption allows applications to process encrypted information without exposing the underlying data. However, traditional gate-by-gate evaluation creates a serious computational bottleneck.
Every operation can increase ciphertext noise, requiring bootstrapping to refresh it.
For large computations, thousands of small gates can mean thousands of expensive operations.
Primus is approaching this challenge through AutoHoG.
Instead of evaluating every simple Boolean gate separately, AutoHoG automatically generates custom homomorphic gates that combine multiple inputs and outputs.
It also analyzes larger circuits, identifies mergeable subcircuits and optimizes their evaluation.
The reported results are interesting:
• Up to 5.7x lower latency across selected circuit benchmarks.
• Around 90ms for a fully encrypted 64-bit confidential transfer.
• More than 210 transfers per second using eight NVIDIA RTX 5090 GPUs.
Another important detail is deterministic integer computation, helping independent nodes produce byte-identical ciphertext results.
Why does this matter?
Because confidential finance needs more than encryption.
It needs performance, consistency and practical scalability.
If encrypted operations become efficient enough, applications could support private payments, confidential lending and institutional financial workflows without exposing sensitive information.
Primus is exploring an important question:
What if privacy could become a normal part of financial infrastructure rather than an expensive additional feature?
@primus_labs
s.kaito.ai/2trAVAx
Let's go together.
@xxiang_xie @bitvickyzh
