

Gaming | Open-source developer & revolutionary thinker | Analyzing geopolitical & tech structures | Locked in My Room Planning the Revolution
In my Room
Joined November 2011
- Tweets3.8K
- Following459
- Followers366
- Likes5.4K
Finally it drops….

Title Update v1.2.0 introduces our first gameplay adjustments for #FC27. Including changes to 95 Depth, fullback positioning, and more. Alongside key updates for Career Mode, FUT, and The Grounds.
Read the full Pitch Notes here: x.ea.com/6r7pvk0xW9y4


28


Eddie retweeted

We'll be dropping our next FUT Developer Notes Wednesday 11th, discussing Evolutions, SBCs, Rewards, and more.
Following the Developer Notes, the team will be hosting a live Discord Developer Q&A on Friday 13th at 4PM GMT to address community topics in the @EASPORTSFC Discord.
Join here: discord.com/invite/easportsf…

Eddie retweeted

The bug is like a joke.
On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀

‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password.
The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours.
It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY".
Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.


Eddie retweeted

how is this shit allowed

Some news: I’m joining OpenAI to lead product management for Core Products!
I have a lot of respect for OpenAI for showing the world that scaling works, for bringing AI to over a billion people, and for believing great products are core to the mission.
I’m excited to work with @thsottiaux, an incredible PM team, and everyone across OpenAI. Together, we’ll build agents that have your back and your team’s, and keep you in control, so you get more time for the people and work you love.
Lots to learn, and lots to build. Please keep your feedback coming!
Eddie retweeted

Some news: I’m joining OpenAI to lead product management for Core Products!
I have a lot of respect for OpenAI for showing the world that scaling works, for bringing AI to over a billion people, and for believing great products are core to the mission.
I’m excited to work with @thsottiaux, an incredible PM team, and everyone across OpenAI. Together, we’ll build agents that have your back and your team’s, and keep you in control, so you get more time for the people and work you love.
Lots to learn, and lots to build. Please keep your feedback coming!
Eddie retweeted

Your router can be hacked without an attacker ever guessing your Wi-Fi password.
That's because your Wi-Fi password isn't the only way to gain access to a router.
Here's how attackers can exploit other weaknesses to take control of it.
Eddie retweeted
Fixes are available for CVE-2026-109518, a High severity vulnerability in APT, the package manager used in Debian, Ubuntu, and derivative Linux distributions. The CVE has a CVSS 4.0 score of 7.7.
Remediation details are available on our blog.
ubuntu.com/blog/apt-vulnerab…

Eddie retweeted

BREAKING: 🇺🇸 Google is now paying employees in 5 more countries to quit as AI spending costs keep rising.
Staff in Canada, France, Germany, Japan and Switzerland are being offered one month's pay for every year worked to leave.
The only teams left out are Google Cloud and DeepMind, its AI unit.
Just last week, Microsoft offered the same kind of deal to 60,000 employees, about a quarter of its entire workforce.
Big Tech is cutting staff to pay for AI, with Google, Microsoft, Amazon and Meta on track to spend $735 billion this year, mostly on data centers and chips.


Eddie retweeted

1/ CVE-2026-98432, the remote Linux TCP bug: I reproduced it after just a few hours with a local LLM 🤯.
Here's the plain-English version of the bug & how it works ⬇️
(Obv. not sharing the exact exploit, but it's trivial to make)
Eddie retweeted
Fixes available in -proposed pocket for CVE-2026-98432. Read the blog for more details: ubuntu.com/blog/fixes-availa…

Eddie retweeted

With the recent wave of vulnerability disclosures, it’s a good time to take a closer look at your own code.
Turn your coding agent into a team of security auditors with the open-source skill that seeded Cloudflare’s vulnerability discovery harness.
The 6 phase approach:
1. Map the codebase
2. Hunt for vulnerabilities
3. Challenge each candidate
4. Record the findings
5. Verify the findings
6. Report what’s confirmed, rejected, or still needs validation
Start your hunt here:
github.com/cloudflare/securi…

Eddie retweeted

Need an app? Built.
Need a website? Built.
Need payments? Built.
Need all of it? Let's talk.
Building tech that works, from Harare.
vetech.co.zw
WhatsApp : +263787980222
Email: [email protected]
Eddie retweeted

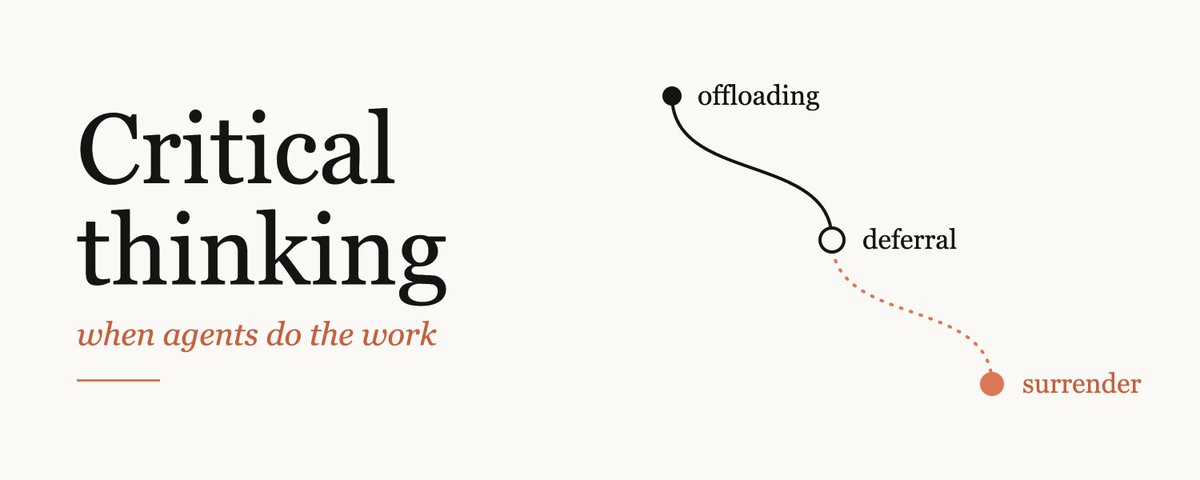
HOLY: Anthropic's Claude Code engineer Addy Osmani is warning about a brutal AI paradox: the more coding you hand to agents, the more you risk losing the very skills needed to supervise them.
He calls it "cognitive surrender." AI-generated code looks pristine, tests pass, and engineers start approving work they no longer understand.
Anthropic's own research warns: "supervising Claude requires the very coding skills that may atrophy from AI overuse."
Osmani makes a striking observation: "When you're producing more than you can stand behind, you're no longer reviewing. You're hoping."




Eddie retweeted

Pattern recognition is one of the most underrated forms of intelligence. The ability to connect seemingly unrelated events, identify recurring behaviours, and anticipate outcomes before they happen gives you an advantage that raw intelligence alone cannot.
Once you recognise the pattern, you stop being surprised by the outcome.
