


The next >5% $BTC movement will bankrupt @papertrade_xyz
Trades on papertrade are synthetic, against the House, unlike a CEX where every trade is coupled with a opposide trade and de-risked with ADL mechanism.
3
4
456
yannickcrypto retweeted

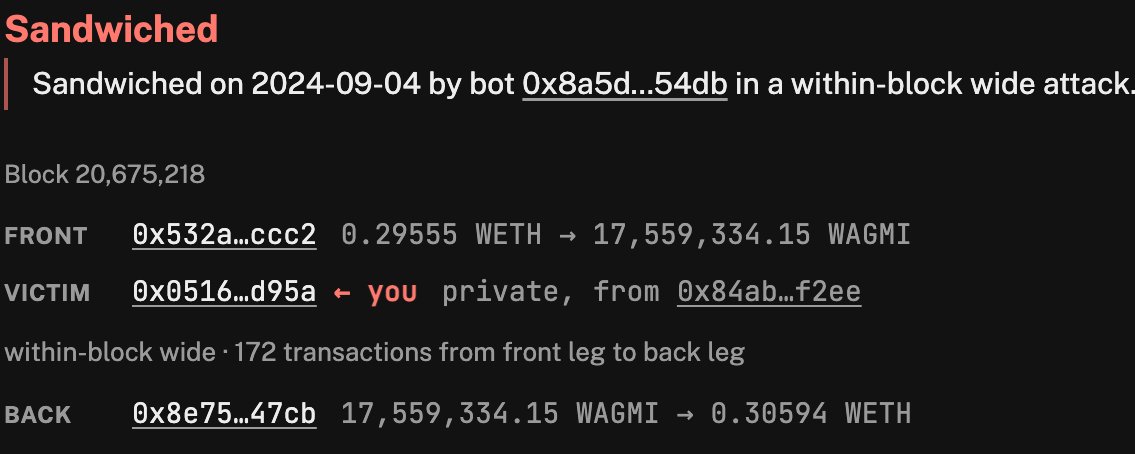
Your MEV protection may not work as you expect. We discuss our latest paper on protected order flow sandwich attacks and release an explorer to check if your protected transaction was sandwiched, and how.
yannickcrypto retweeted

🚨 New paper alert 🚨
No Place to Hide: An Analysis on Protected Order Flow Sandwich Attacks
w/ Ozan Solmaz @boez95 @ChristofTorres
Bots watch every pending trade in Ethereum's public mempool and sandwich the ones worth attacking. Hence the nickname: the dark forest. In response, Ethereum and other chains built protections, from private RPCs to mechanisms native to the chain, that shield trades from these bots. We call this protected order flow.
How well are these users actually protected? We measured it in a three-year study of sandwich attacks by persistent bots against protected order flow on Ethereum, Solana, Tron, Base, Arbitrum, and Monad. The protections on these chains range from private RPCs on Ethereum and private submission to a centralized sequencer on Base and Arbitrum, to first-come-first-served ordering in Tron's public mempool and local mempools on Solana and Monad. Local mempools were never meant as a full front-running prevention, but they do limit who sees a trade before it lands.
On four of the six chains, we observe protected order flow sandwich attacks: 28.0M attacks on Solana, 38,567 on Tron, 30,607 on Ethereum plus 2,576 more through reorged blocks, and 1,889 on Base.
We trace each chain's exposure and find that it sits in various places along a transaction’s path.
🟠 Ethereum: OFAs can expose enough information to make private trades sandwichable, especially when the same transaction reaches multiple OFAs or when searchers receive full transaction details. Reorged blocks also expose private transactions. We find transactions that were private and untouched in a block that got reorged, and then sandwiched on the canonical chain.
🟠 Solana: transactions are sent to the upcoming leaders, and early on we find that a few leaders carry far more attacks in their blocks than their share of blocks, i.e., they are likely the exposure source for these transactions. From 2025 that fades, but we see that victims concentrate around a few apps.
🟠 Tron: we presume that bots win latency races in the public mempool, so the first-come-first-served ordering in block building does not fully prevent sandwiches.
🟠 Base: we see two different kind of exposure. One lines up with a documented RPC bug that exposed pending transactions. The other has attackers preying on victims who trade on a predictable schedule, if the vicim does the same trade every couple of blocks, the attacker can front-run them without observing the pending trade.
Protected order flow sandwiches look very different from public mempool sandwiches. The attacker's transactions often land in a different block than the victim's, and unlike in the public mempool, their success is not guaranteed. These attackers simply don't act with the same certainty.
The dark forest may have shrunk, but we show there's an even darker corner of it, where users who think they're protected still get front-run. Protection has to hold at every layer, from the app to the RPC to the block producer. Encrypted mempools and TEE-based designs can help, by keeping transaction contents out of attackers' reach until inclusion. But even they might not be enough on their own without privacy, for example if the victim is too predictable.
Link: arxiv.org/abs/2609.28115
🤖 Made with AI

I sold 100% of my crypto assets at around $74k-$75k, BTC, ETH, SOL and some other alts, i believe we will see 40k this year and this was the last god given chance to exit.
$52 milion payout to Compound foundation.. voted FOR by Compound foundation.. @Compound_xyz the best DECENTRAL project out there <3

9
1,068
Is Michael sellor laundering funds?
Who noticed that @saylor ALWAYS buy the pico top or since the 32 BTC sell ALWAYS sell the pico bottom.
That cant be a coincide, we want to see the OTC sales, exact dates, premium, benefitor.
What if saylor is buying from himself with huge premium and sell now to himself back with huge premium and the stock holder and creditor have to pay it.
850000 BTC money laundering?

yannickcrypto retweeted

The founder of ENS is about to vote himself control of a half billion dollar treasury
ENS has a governance emergency and is voting to move the DAO treasury into the FOUNDATION
The foundation is controlled by ENSLabs. Nick Johnson’s company
The problem is NICK.ETH holds 3.3m voting power and there is no group on that board that can outvote him
So when the vote comes, it passes. Not because the community agreed but because most of it left
Five years ago Nick said ENS was Ethereum infrastructure and too important to sit with a single entity. That’s why it became a DAO
Now the DAO is voting to undo that in public for half a billion dollars
The craziest part is that it’s being signed this week and the vote has ONLY 20k views and 12 replies


DAOs are so dead that I see nobody noticed or discussed this proposal that @ENS_DAO essentially dissolves itself and transfers control of the entire treasury (almost half a billion in ENS + stables) to the ENS foundation.

yannickcrypto retweeted

the latest tornado cash proposal 67 is _malicious_: https://bafybeie5hxovqc4ifcnrnhvmjbefxgeix6oqvzaspyytdxiyscji22v5pu[.]ipfs[.]inbrowser[.]link/governance/67
decompilation of the proposal: app.dedaub.com/ethereum/addr…
the try to set the governance address to a vanity address that looks almost like the governance address:
- spoofed version: `0x5EFDa50f22D34F272c7077689d6ABc42F15E285f`
- real governance address: `0x5efda50f22d34F262c29268506C5Fa42cB56A1Ce`
same for the staking governance proxy:
- spoofed version `0x2fc93484614a34f7dbf98d7f7e997f6424e54a32`
- real staking address: `0x2FC93484614a34f26F7970CBB94615bA109BB4bf`
furthermore, worth mentioning the function `nullifyBalance` checks against the spoofed governance address above; so whoever controls that vanity address can zero out any relayer's balance at will.
this is a governance attack on Tornado Cash and i ask all TORN tokenholders to reject this proposal


1/ A suspicious DAO proposal on Tornado Cash was created ~8hrs ago. Summoning @pcaversaccio (and everyone else curious) for an independent opinion!
Details in the thread below👇


It happend, jaredfromsubway.eth lost $7 million dollar in a hack and the reason is simple.
For Uniswap pools you have to transfer the token to the contract and then call mint().
But RingSwap wants you to approve the pool and call mint(), it then calls transerFrom.
The problem, since SELFDESTRUCT got nerfed you cant re-deploy a new contrct with CREATE2 anymore, thats what we used to update our Mev Bots.
So Jared couldnt add checks to see if the allowance got consumed.
His only option was to deploy a new contract but he decided to be sloppy and keep his 2 million transaction count on etherscan, over a protocol that gives him $100 net profit a day.


IOST
1INCH
ADA
CRV
POWR
MANA
ARK
LSK
ENS
AVAX
Buy now, TP at ema200 1d, thank me later, this is financial advice.