


yannickcrypto retweeted

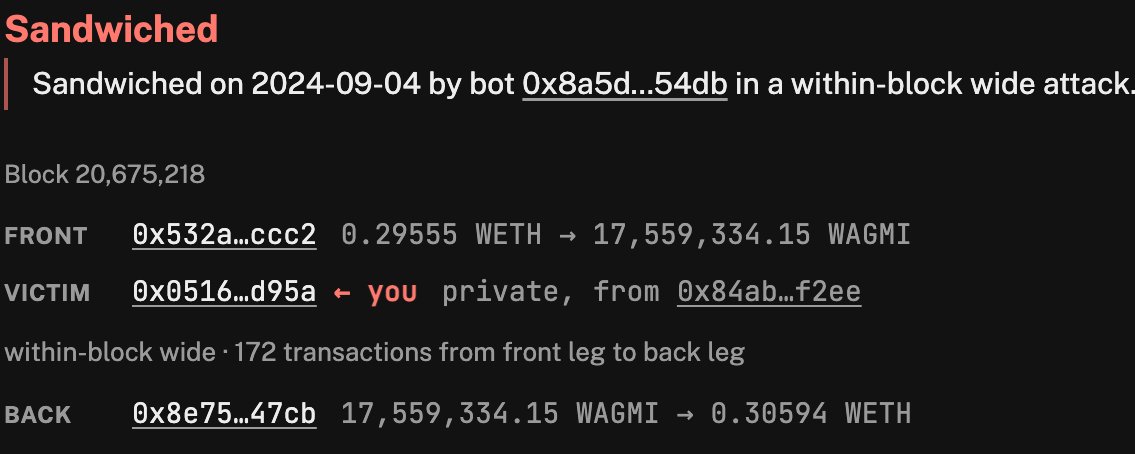
Your MEV protection may not work as you expect. We discuss our latest paper on protected order flow sandwich attacks and release an explorer to check if your protected transaction was sandwiched, and how.
yannickcrypto retweeted

🚨 New paper alert 🚨
No Place to Hide: An Analysis on Protected Order Flow Sandwich Attacks
w/ Ozan Solmaz @boez95 @ChristofTorres
Bots watch every pending trade in Ethereum's public mempool and sandwich the ones worth attacking. Hence the nickname: the dark forest. In response, Ethereum and other chains built protections, from private RPCs to mechanisms native to the chain, that shield trades from these bots. We call this protected order flow.
How well are these users actually protected? We measured it in a three-year study of sandwich attacks by persistent bots against protected order flow on Ethereum, Solana, Tron, Base, Arbitrum, and Monad. The protections on these chains range from private RPCs on Ethereum and private submission to a centralized sequencer on Base and Arbitrum, to first-come-first-served ordering in Tron's public mempool and local mempools on Solana and Monad. Local mempools were never meant as a full front-running prevention, but they do limit who sees a trade before it lands.
On four of the six chains, we observe protected order flow sandwich attacks: 28.0M attacks on Solana, 38,567 on Tron, 30,607 on Ethereum plus 2,576 more through reorged blocks, and 1,889 on Base.
We trace each chain's exposure and find that it sits in various places along a transaction’s path.
🟠 Ethereum: OFAs can expose enough information to make private trades sandwichable, especially when the same transaction reaches multiple OFAs or when searchers receive full transaction details. Reorged blocks also expose private transactions. We find transactions that were private and untouched in a block that got reorged, and then sandwiched on the canonical chain.
🟠 Solana: transactions are sent to the upcoming leaders, and early on we find that a few leaders carry far more attacks in their blocks than their share of blocks, i.e., they are likely the exposure source for these transactions. From 2025 that fades, but we see that victims concentrate around a few apps.
🟠 Tron: we presume that bots win latency races in the public mempool, so the first-come-first-served ordering in block building does not fully prevent sandwiches.
🟠 Base: we see two different kind of exposure. One lines up with a documented RPC bug that exposed pending transactions. The other has attackers preying on victims who trade on a predictable schedule, if the vicim does the same trade every couple of blocks, the attacker can front-run them without observing the pending trade.
Protected order flow sandwiches look very different from public mempool sandwiches. The attacker's transactions often land in a different block than the victim's, and unlike in the public mempool, their success is not guaranteed. These attackers simply don't act with the same certainty.
The dark forest may have shrunk, but we show there's an even darker corner of it, where users who think they're protected still get front-run. Protection has to hold at every layer, from the app to the RPC to the block producer. Encrypted mempools and TEE-based designs can help, by keeping transaction contents out of attackers' reach until inclusion. But even they might not be enough on their own without privacy, for example if the victim is too predictable.
Link: arxiv.org/abs/2609.28115
🤖 Made with AI

yannickcrypto retweeted

The founder of ENS is about to vote himself control of a half billion dollar treasury
ENS has a governance emergency and is voting to move the DAO treasury into the FOUNDATION
The foundation is controlled by ENSLabs. Nick Johnson’s company
The problem is NICK.ETH holds 3.3m voting power and there is no group on that board that can outvote him
So when the vote comes, it passes. Not because the community agreed but because most of it left
Five years ago Nick said ENS was Ethereum infrastructure and too important to sit with a single entity. That’s why it became a DAO
Now the DAO is voting to undo that in public for half a billion dollars
The craziest part is that it’s being signed this week and the vote has ONLY 20k views and 12 replies


DAOs are so dead that I see nobody noticed or discussed this proposal that @ENS_DAO essentially dissolves itself and transfers control of the entire treasury (almost half a billion in ENS + stables) to the ENS foundation.

yannickcrypto retweeted

the latest tornado cash proposal 67 is _malicious_: https://bafybeie5hxovqc4ifcnrnhvmjbefxgeix6oqvzaspyytdxiyscji22v5pu[.]ipfs[.]inbrowser[.]link/governance/67
decompilation of the proposal: app.dedaub.com/ethereum/addr…
the try to set the governance address to a vanity address that looks almost like the governance address:
- spoofed version: `0x5EFDa50f22D34F272c7077689d6ABc42F15E285f`
- real governance address: `0x5efda50f22d34F262c29268506C5Fa42cB56A1Ce`
same for the staking governance proxy:
- spoofed version `0x2fc93484614a34f7dbf98d7f7e997f6424e54a32`
- real staking address: `0x2FC93484614a34f26F7970CBB94615bA109BB4bf`
furthermore, worth mentioning the function `nullifyBalance` checks against the spoofed governance address above; so whoever controls that vanity address can zero out any relayer's balance at will.
this is a governance attack on Tornado Cash and i ask all TORN tokenholders to reject this proposal


1/ A suspicious DAO proposal on Tornado Cash was created ~8hrs ago. Summoning @pcaversaccio (and everyone else curious) for an independent opinion!
Details in the thread below👇


yannickcrypto retweeted

I Saved Injective's $500M. They Pay Me $50K.
I like hunting bugs on @immunefi . I'm decent at it.
- #1 — Attackathon | Stacks
- #2 — Attackathon | Stacks II
- #1 — Attackathon | XRPL Lending Protocol
- 1 Critical and 1 High from bug bounties (not counting this one)
Life was good. Then I found a Critical vulnerability in @injective .
This vulnerability allowed any user to directly drain any account on the chain. No special permissions needed. Over $500M in on-chain assets were at risk.
I reported it through Immunefi. The next day, a mainnet upgrade to fix the bug went to governance vote. The Injective team clearly understood the severity.
Then — silence. For 3 months. No follow up. No technical discussion. Nothing.
A few days ago, they notified me of their decision: $50K. The maximum payout for a Critical vulnerability in their bug bounty program is $500K. I disputed it. Silence again. No explanation for the reduced payout. No explanation for the 3 month ghost. No conversation at all. To be clear: the $50K has not been paid either.
I've seen others share bad experiences with bug bounty payouts recently. I never thought it would happen to me. I can't force them to do the right thing. But I won't let this be forgotten.
I will dedicate 10% of all my future bug bounty earnings to making sure this story stays visible — until Injective pays what I deserve.
Full Technical Report: github.com/injective-wall-of…

yannickcrypto retweeted
An alleged dev named Bruce Lee botched a proxy upgrade and froze over $20M in POL.
The ETHSecurity Telegram Community turned it into a comedy roast, but the project remains unknown, the contract unlabeled on @arkham and clueless users won’t find this funny.
Who Got Rugged?



yannickcrypto retweeted

SDNY and @HSISanDiego seize cryptocurrency worth approximately $31 million related to April 2021 hack of Uranium Finance. If you believe you have been a victim of this hack, please contact [email protected].
yannickcrypto retweeted

Exclusive: @DeFiTuna Blows Whistle on M3M3's $200M Market Manipulation Scheme
✍️ @0xSheldon
solanafloor.com/news/defi-tu…

yannickcrypto retweeted

🚨 BREAKING: The NYSE has filed a proposal to allow staking for Grayscale’s Ethereum ETF.


yannickcrypto retweeted

Yo Am I the only one who saw this during the fight? Is it me or @blknoiz06 and @BenArmstrongsX made out passionately?
yannickcrypto retweeted

👏 Thanks to efforts of @YannickCrypto, we recovered 36,800 $POT
We are grateful for @YannickCrypto's contribution to web3 security and rewarded them. We look forward to closer cooperation with them to create a better web3 & metaverse space.
1/2
yannickcrypto retweeted

On February 27th, @discord unjustly perma-banned me and several others for having a Moderator role in a server called POLI (All-Sides Politics).
Most of us have been Discord users since at least 2017. We all were in good standing with no reports against us.
-->THREAD

yannickcrypto retweeted

25.7 eth was sitting waiting for somebody to take it for ~1hour, just build custom block and set coinbase address and block hash and there's your free $30k... owner withdrew shortly after he found out though etherscan.io/address/0x92ffa…

yannickcrypto retweeted

Same Jared Grey who contacted a ton of CT ppl to promote his NFT scam? Sus behavior


Hey @SushiSwap how it comes you elect @JaredGrey, a scammer and con artist, as the new CEO?
Here some details about Grey:
yannickcrypto retweeted

He was a big part of Encore / evault.finance too. Absolute serial scammer.

