

@aacle_
Account based inIndia
About this account
- Account based in
- India
- Connected via
- India Android App
Account-level information from X, not a live location or the device used for a specific post.
Building @Vulncure ⚡| Helping founders fix vulnerabilities before hackers find them. Talk to me about: Bug Bounties, LLM Security & React.
Joined June 2017
- Tweets4K
- Following291
- Followers49.6K
- Likes3.5K




Pinned Tweet
Starting Claude For Bug Bounty - # Series
I’m starting from absolute zero and showing beginners how to actually use Claude for:
→ Recon
→ Burp Suite
→ API testing
→ XSS
→ IDOR
→ JS analysis
→ Finding bugs
→ Writing solid reports
I’ll show what Claude is doing, why it works, and how to verify the findings yourself.
first part coming soon. 👀


Abhishek retweeted

I got $90,000 for a RCE in Google.
simonkoeck.com/writeups/goog…


Abhishek retweeted

I just spent the last 6 hours with two different models to exploit an XSS and I think I finally figured it out
all of this to get a dupe?
Abhishek retweeted

Telegram Desktop: one-click account takeover via IPC injection
beaksec.github.io/posts/tele…
Abhishek retweeted

A Google API key is not always just a Low or Informational finding.
The Story of Submitting some P1s in the last months by the same method
Sometimes the real impact is in what you can do with it.
For example, with Firebase / Google Identity Toolkit, a leaked key may allow account creation directly through the API:
curl -sk -X POST \
"identitytoolkit.googleapis.c…" \
-H "Content-Type: application/json" \
-d '{"email":"youremail@company.com","password":"Test12345!","returnSecureToken":true}'
Now imagine the application trusts users based on the email domain and does not properly verify ownership.
In that case, you may be able to create an account using an organization email, receive a valid auth token, and access parts of the application that were supposed to be limited to internal users.
At that point, this is no longer about an "exposed Google API key".
The impact can become unauthorized registration, authentication bypass, internal access, sensitive data exposure, or even full access to the application depending on how the backend handles authorization.
So before marking a Google API key as Low, always check what the key actually allows you to do.
The key itself may be Low. The impact behind it may not be.
#bugbountytips #bugbountytip #infosec #Bugbounty


HackerOne actually did this 💀😂
giving a whole separate badge 🏅 to researchers who Submit AI Sloop Reports


You must read this too... 👇
Top 43 AI Security Skills, MCP Servers & GitHub Repos
medium.com/@Aacle/top-43-ai-…

Every 3rd person I see on my feed is posting about the $ bounty they earned from bug bounty hunting.
That’s honestly crazy. 🔥
Another example that AI in CYBERSECURITY is really crussing SECURITY TESTERS in FINDING SECURITY VULNERABILITIES MANUALLY in these days
❗❗

📢 PSA for open-source bug hunters
We are temporarily no longer accepting OSS VRP product vulnerability submissions. This does not impact OSS VRP supply chain reports, or any outstanding reports. As an alternative, we encourage you to find impact across our other VRP programs and submit there instead, or pursue the Patch Rewards Program.
Why is this happening? This pause is due to a significant rise in automated submissions, the vast majority of which are not valid. We will continue to reformat and work on this aspect of the OSS VRP and commit to giving an update in Q1 2027.
bughunters.google.com/about/…

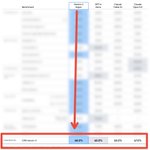
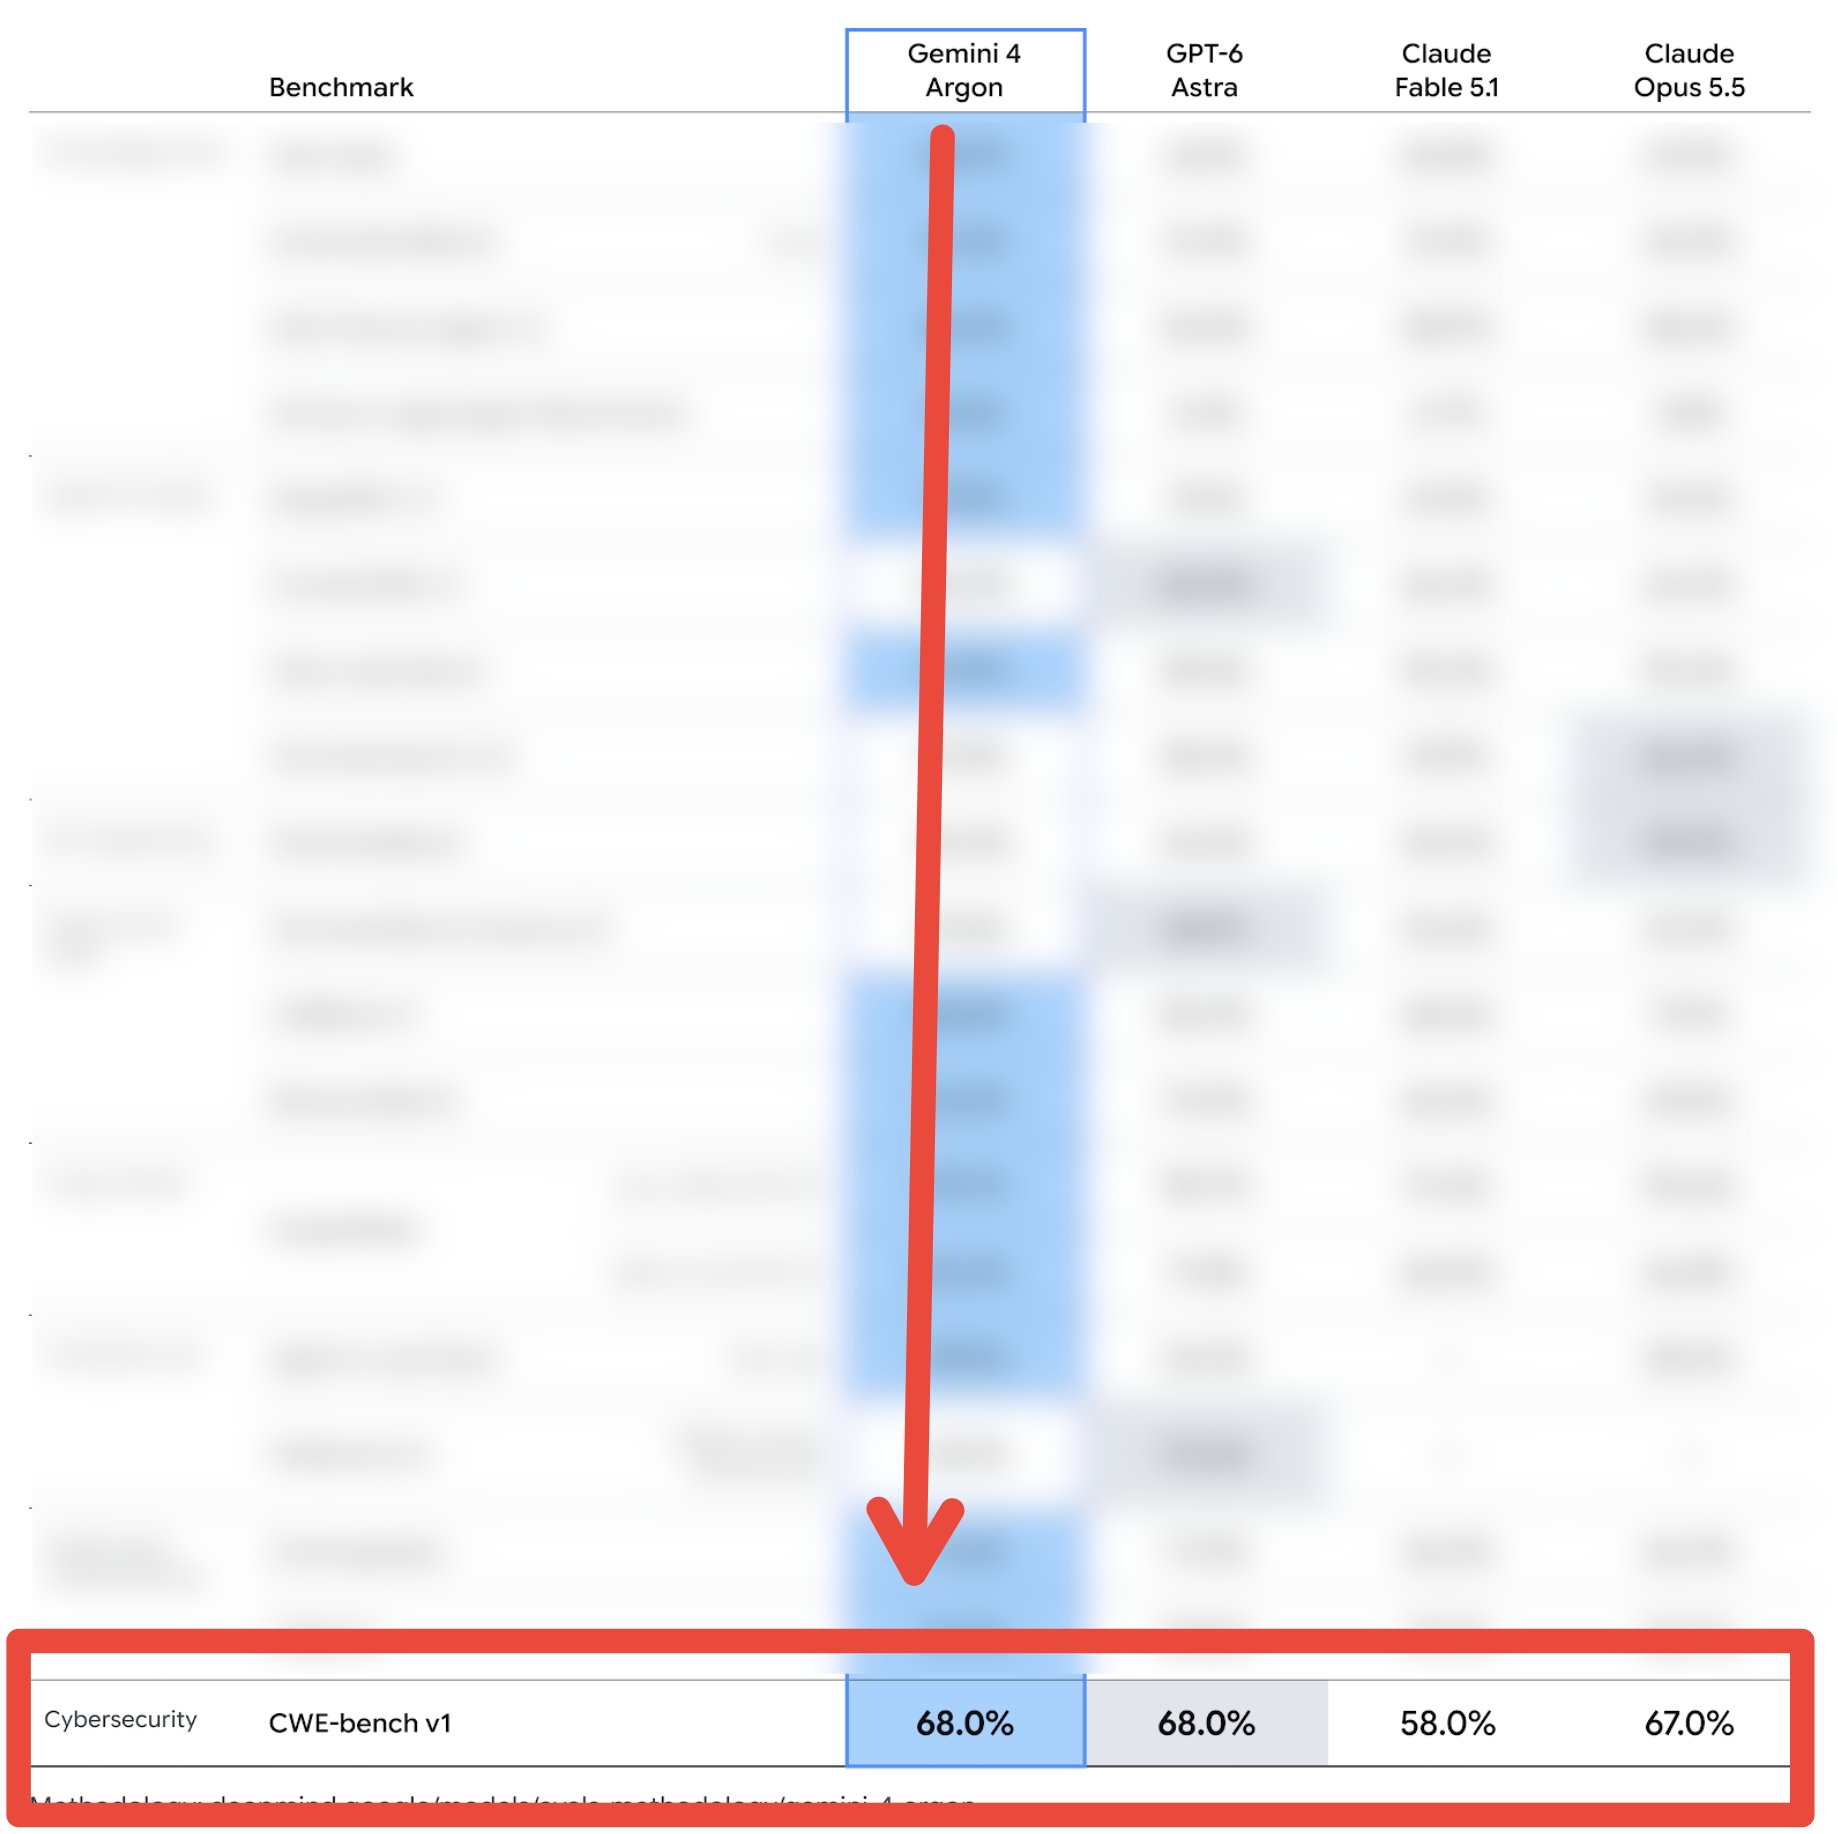
🔥 Gemini 4 hype is starting.
“Best in cybersecurity.”
Then you check the numbers:
CWE-bench v1 → 68%
Same score as GPT-6 Astra.
Interesting. but the bench marks could also be benchmaxed !!
🚨 400 hunters are staring at the login page.
Meanwhile, that tiny features like Export to CSV button has barely anyone testing it.
That’s where things get interesting & you shoud look features like where you could examine that having less testers on crowded bug bounty programs 👀
Every boring feature is a fresh attack surface:
→ 📄 Export / PDF generation → SSRF, template injection
→ 📧 Email digests → IDOR on recipient IDs
→ 📁 File previews → path traversal via filenames
The features nobody uses are often the ones nobody tests.
And that’s exactly the point. 🎯
✅ One thing I always check when testing rate limits:
Does the app normalize the identity, or just compare the raw string?
For example, Gmail can treat these as the same mailbox:
➜ victim@gmail.com
➜ USER@gmail.com (Gmail ignores case)
➜ v.i.c.t.i.m@gmail.com (Gmail ignores dots)
➜ victim@googlemail.com (same mailbox)
➜ victim+1@gmail.com (plus-tag)
But a poorly designed limiter might see 5 different strings and create 5 different rate-limit buckets.
Abhishek retweeted
r/bugbounty now deletes this question as a repeat topic:
"is manual hunting still worth it?"
asked so many times it counts as spam. the platforms won't answer it either.
so i tried to build an answer from the numbers. it's worse, and better, than you think:
medium.com/@Aacle/is-manual-…

RocketChat's main login was fully secure.
Then a microservice re-implemented the same login flow and the copy was missing one await.
Your auth is only as strong as the worst copy of it.
I wrote up how three small bugs chained into "log in as anyone"
medium.com/@Aacle/one-missin…

I rarely promote tools, but Better Shot deserves it.
github.com/KartikLabhshetwar…
Use every day on my Mac for screenshots, annotations, OCR, color picking, screen recording, video edits, zooms, captions, blur/pixelate, and sharing.
Free + open source.
Huge shoutout to @code_kartik for building this 🙌

LFI filter bypass via emojis
/𝘥𝘰𝘸𝘯𝘭𝘰𝘢𝘥.𝘱𝘩𝘱?𝘧𝘪𝘭𝘦=../../../𝘦𝘵𝘤/𝘱𝘢𝘴𝘴𝘸𝘥 → 404
/𝘥𝘰𝘸𝘯𝘭𝘰𝘢𝘥.𝘱𝘩𝘱?𝘧𝘪𝘭𝘦=⬅️/⬅️/⬅️/𝘦𝘵𝘤/𝘱𝘢𝘴𝘴𝘸𝘥 → 200
the filter blocks the literal ../ sequence. the emoji variant gets through
source: nitter.cf/0xConda/status/2101647…