

CTO, co-founder @ManifestCyber. Former @CISAGov, @DefenseDigital. Fellow @AspenPolicyHub. Leading @0x4Sight. Hack the Planet. Views are my own.
Joined July 2011
- Tweets391
- Following357
- Followers414
- Likes1.2K





Daniel Bardenstein retweeted

In line with our Cybersecurity Strategic Plan and our focus on measuring risk reduction, we are measuring national progress in the adoption of CPGs and associated progress in addressing key risks. Read the details in our latest blog: go.dhs.gov/oCt

Daniel Bardenstein retweeted

AI Supply Chain Security is top of mind for most organizations nowadays. Join me in a conversation about AI/ML Bill of Materials with @allanfriedman, Sr. Technical Advisor at @CISACyber and @bardenstein, Co-founder and CTO @ManifestCyber on Thursday at 11am EDT.
manifestcyber.com/mlbom-webi…
#CyberSecurity #ArtificialIntelligence

Daniel Bardenstein retweeted

Daniel Bardenstein, CTO of @ManifestCyber, joins us on 30 November for the AI Security Summit, hosted by OASIS Open and @Cisco.
@bardenstein will discuss AI transparency: the machine learning bill of materials (#MLBOM aka #AIBOM).
Register (free): aisecuritysummit.org/

Indeed! All the more reason to check out the webinar we're hosting on ML bills of material (MLBOMs) on 11/9 with @allanfriedman and @santosomar !
Details below!
manifestcyber.com/mlbom-webi…
#sbom #aibom #ai #ml #genai #llm #supplychain #slsa

ML is growing and this is fertile ground for attackers to exploit the AI supply chain. How do we protect it? Turns out, we can use the same tools as the traditional software (sigstore, SLSA,etc.)
security.googleblog.com/2023…

So proud to know the newest member of cDc, who couldn’t be a more deserving inductee.
Keep rocking @hexplates !

The @ONCD #DEFCON31 badges were so cool that I had to try to win one by solving the hidden puzzle. With some help and much effort, I finally broke the code 👨💻
Kudos to @RoRoRah and @cybertestpilot for their amazing work, and ONCD for making it all happen.
H/t @DEFCONPolicy
Daniel Bardenstein retweeted
Outstanding work by @manifestcyber now supporting @OASISopen CSAF!
#CyberSecurity #supplychainsecurity #sbom #vex
manifestcyber.com/blog/the-p…
Tune in to this panel at 11am ET today to learn about the path to secure software development!
webinars.securityboulevard.c…
#sbom #vex #nist #securesoftware #appsec

Excited to share that I'll be speaking at @defcon at the @DEFCONPolicy alongside Chris Butera from CISA and Cassie Crossley from Schneider Electric to talk about Secure By Design and the future, tension, and implications for government and software vendors!
Daniel Bardenstein retweeted

Cross-Sector Cybersecurity Performance Goals (CPGs) can help all organizations, regardless of size or industry, prioritize the steps they need to take to mitigate risk of potential threats from sophisticated cyber threat actors. Learn more: cisa.gov/cpg

Daniel Bardenstein retweeted

We're incredibly honored and excited to be part of this fantastic SVIP cohort to push forward all things #sbom.
Can't wait to get started!

Excited for the announcement of @dhsscitech SVIP awardees for SW Supply Chain Tools and #SBOM. We're looking forward to working with these great teams.
@AppCensusInc @chainguard_dev @deepbits_tech @manifestcyber @ScribeSecurity @testifysec & Veramine
dhs.gov/science-and-technolo…

The team and I can't wait to jump into this forward-thinking, collaborative program to help promote tools that will help #SBOM adoption - and software transparency - globally.
💪 #knowwhatyouremadeof
Excited for the announcement of @dhsscitech SVIP awardees for SW Supply Chain Tools and #SBOM. We're looking forward to working with these great teams.
@AppCensusInc @chainguard_dev @deepbits_tech @manifestcyber @ScribeSecurity @testifysec & Veramine
dhs.gov/science-and-technolo…
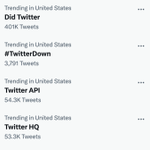
A story in a picture (assuming it actually loads given the current circumstances)
"Did #Twitter (HQ) just let their own API go down?!"

Lest we forget - solving this problem goes farther than product liability laws (though that would have tremendous impact).
We also need to start teaching CS students how to code securely (e.g. with memory safe languages). 1/

Very excited to hear @CISAJen going after a hard but critical problem: holding software suppliers responsible for insecure code.
washingtonpost.com/politics/…
Very excited to hear @CISAJen going after a hard but critical problem: holding software suppliers responsible for insecure code.
washingtonpost.com/politics/…
Great #sbom win about how organizations can (and are actively!) using SBOMs to buy more secure products and understand #softwaresupplychain risk before they deploy software into their networks.
Honored to be part of @manifestcyber !
linkedin.com/feed/update/urn…


Come find me this week at #S4x23 to catch up on ICS security and chat about #SBOM's and @manifestcyber .
See you all in Miami!