

{ "name": "Corey J. Ball", "author": "Hacking APIs", "creator": "https://nitter.cf/t.co/y3EHBlzHvJ", "is_admin": true }
Grants Pass, OR
Joined May 2020
- Tweets1.4K
- Following872
- Followers14.2K
- Likes4.4K





hAPI_hacker retweeted

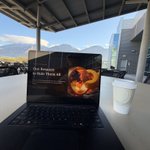
Even though I’m currently unemployed & still looking for work I’m trying to stay busy! I’m happy to say my latest project is completed!
JaysonEStreet.com
has been turned into Street_OS! 😊
I think the transformation from my old one to this is amazing!!! 🤩


hAPI_hacker retweeted

In a single year, AI has rewritten the security priority list for CISOs.
Attackers are moving faster. Bain estimates AI compresses a typical cyberattack from about four weeks to about 18 hours, and models keep getting better at finding and exploiting weaknesses.
There's also more to protect, with employees shipping apps they couldn't have built a year ago and agents getting access to source code, documents, and production systems.
In a survey of 100 CISOs at companies with 1,000+ employees, all seven of the most-selected 2027 priorities involve AI.
The biggest jumps since 2026:
- Internal AI agent security (+28 pts)
- AI SOC (+26 pts)
- AI offensive security (+24 pts)
- AI code security (+23 pts)
- AI vulnerability remediation (+22 pts)
Last year's staples:
- Exposure & vulnerability management (-21 pts)
- SIEM / security data (-18 pts)
- Privileged access management (-18 pts)
From a16z's @OwenColby and @steph_zhang on The New Security Agenda: a16z.news/p/the-new-security…


hAPI_hacker retweeted

UPDATE: Specific mitigation guidance for the recently identified PHP critical vulnerabilities is now available. Secure your servers today. Guidance and technical steps here: nsa.gov/Press-Room/Press-Rel…


Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Patch away everyone! PHP patches are out now: lnkd.in/gtHWuu5G
PHP2Shell Resources:
Cloudflare is helping: lnkd.in/geU8VZig
NSA Cyber is saying if you cannot patch it, take it offline until you can patch: lnkd.in/gZGkQCcC
Wiz PHP2Shell RCE Research: lnkd.in/gzv3tSN7
Don't take it from me even the Prime Minister of Japan, Sanae Takaichi, says to patch!

hAPI_hacker retweeted

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X


hAPI_hacker retweeted
🚨 PHP2Shell detection is now available in Burp Suite Professional & Burp Suite DAST.
Most of the web is powered by PHP, which means most of the web is vulnerable to these critical unauthenticated remote code execution flaws (CVE-2026-109618 / 109619). You can already detect it in Burp Suite using:
🟧 ActiveScan++ v2.0.13 (portswigger.net/bappstore/31…)
🟧 Bambda scan checks (github.com/PortSwigger/bambd…)
🟧 BChecks (github.com/PortSwigger/bchec…)
Start scanning for the vulnerability now → portswigger.net/bappstore/31…

hAPI_hacker retweeted

phucking patch
php.net/archive/2026.php#202…
github.com/php/php-src/secur…
github.com/php/php-src/secur…


hAPI_hacker retweeted
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
hAPI_hacker retweeted
Your next security skill starts with a good book.
Save 30% on hacking and security books with code STAYSHARP through October 9.
Print books include the free ebook. Sale excludes preorders.
nostarch.com/catalog/securit…

ALT No Starch Press Cybersecurity Awareness Month sale graphic. Sharpen your defenses with 30% off cybersecurity books using code STAYSHARP through October 9. Excludes preorders. Featured books are Foundations of Cybersecurity, 2nd Edition; Practical AI Security; Cybersecurity for Small Networks; Designing Secure Software; Cybersecurity Tabletop Exercises; and Practical Purple Teaming.
hAPI_hacker retweeted
Huge shoutout to @hAPI_hacker for gifting me an ASCP voucher back in April 🙏
I just passed my ASCP exam! 🎉
Your generosity goes a long way Thank you!

hAPI_hacker retweeted

It takes a while to build the confidence, but there's no future where you're manually reviewing every line of agent code. Not much acceleration in that. You need adversarial agent reviews, you need automated testing, and maybe you spot check. That's it. From prompt to production!

hAPI_hacker retweeted

Absolutely incredible research by @garethheyes
One email, two readers.
:before and :after inject text into the page. An AI browser reading the message does not see that text.
opacity:0.00000001 does the reverse. The victim cannot read the element, but the AI browser can.
Read CSS:the bomb inside your inbox by Gareth to learn more 👇
portswigger.net/research/css…

hAPI_hacker retweeted

In less than 24 months there will be a clip of a high profile CRO explaining this reality to a (much smaller) room of sales reps.

hAPI_hacker retweeted


🌉 Sept. 24: Join us at our next Agents & APIs SF Dev Meetup featuring:
👉 @mlhassett, Sr. Developer Advocate, @canva
👉 @binsquares, founder, @smolmachines (YC P26)
👉 @poojamakes, Sr. Developer Advocate Enterprise Adoption, @astropods_
👉 @anandPa94, founder, @tryscope_app (YC P26)
Sign up here: luma.com/Sept-SF-Agents-APIS…

hAPI_hacker retweeted

Attacker vs. Defender AI Advantage
danielmiessler.com/blog/atta…

hAPI_hacker retweeted

Think you're late to AI security? The field is just starting.....
Sat down with my friend Jason Haddix (@Jhaddix) the guy who literally defined AI pentesting methodology, to show you how to become an AI hacker/pentester from scratch!
Watch the full video here --->
youtu.be/_yfiUQSbdPY?si=qUEv…
hAPI_hacker retweeted

One slot left at apisec|CON. CFP closes midnight PT today.
Oct 21. Single track, ~7 talks.
Theme is exploitability — chains you've actually walked, not CVSS scores you've read.
If you've got the talk, send it:
conf.apisecuniversity.com/
@hAPI_hacker @apisecu
