

bitcoiner | @btcillustrated supported by @btrustteam & @bitcoin_devs
Joined August 2014
- Tweets278
- Following914
- Followers760
- Likes5.5K





jrakibi retweeted

Quantum Computing 101
A Bitcoin Security Consortium report, in collaboration with Presidio Bitcoin.

jrakibi retweeted

SHA-256 is not broken, but its security margin lost 1 more round this year:
Last week I found a collision attack on reduced 39-round that improves prior art by over 30 bits and the first differential attack on that round better than generic search on @yukonresearch Hashsmash board.
The attack rests on the same method as prior art ePrint 2026/1120 with new insights that first 2 state words could remain free, allowing a critical condition at step 16 rebuilt as a claw-search problem rather than a probabilistic filter. Took days of watching SAT logs, burning cores and arguing with Claude on what's possible to get a result close to generic search.
Since my initial submission, other hashsmash participants sraiw, @cyberaxe, @privacymage, @lamb356_ and @geeknik pushed it down by over 6.5 bits, currently estimated at 118.15 bits. The tree of submissions is hard to follow, so I put the construction, insights and numbers into a blog and am working on detailed technical report.
It's fascinating to see an initial structural observation develop into an improvement in the reduced-round collision frontier within days. AI is now a real aid in cryptanalysis and open collaboration speeds it up.

jrakibi retweeted

hey guys, so this was a little harder but these two messages collide for 38-step SHA-256:
m1 = 33ee28ac5f8ef994c787777c079d17e11198d1beb527c8554bfeff014ab531951cf31bd2bbfc637e122da4f948e6e447d5a6b8b6ea9e7af5aac1aeabeeaceb0dbd07668b833fe88e689ffe8da52259da14b9855eee5138ba88355f4806d5cf5d161c50014c6b7d7e0e7eb888747559fc990a7af69dd8e59f57d7f6a3c0fbd03b
m2 = 33ee28ac5f8ef994c787777c079d17e11198d1beb527c8554bfeff014ab531951cf31bd2bbfc637e122da4f948e6e447d5a6b8b6ea9e7af5aac1aeabeeaceb0dbd07668b833fe88e689ffe8da52259da14b9855eee5138ba88355f4838b3d19d161c4ffd4c6b7d7e0e813888747559fc990a7af69dd8e59f57d7f6a3c0fbd03f

jrakibi retweeted

We published a paper (eprint.iacr.org/2026/2626) about exact definitions of bit-security. We noticed that depending on how you account the adversary's work we have slightly (but noticeable) different security of Hash-based schemes. Be careful with your Lean-proofs and statements :)
jrakibi retweeted

Two months ago, alongside @Coinbase and @danboneh, we co-hosted a post-quantum workshop for cryptographers, protocol engineers, hardware wallet manufacturers, and institutional voices working on Bitcoin’s preparedness for a CRQC.
Today, we’re sharing transcripts from the event and a blog post summarizing the discussions: lclhost.org/blog/quantum-wor…
A special thank you to our speakers and session leaders: @danboneh, @asanso, @LindellYehuda, Pieter Wuille, @conduition_io, @n1ckler, @P3b7_, and Justin of Localhost, everyone who traveled to attend, and the @MARAFoundation_ for sponsoring our post-event dinner.
We hope this workshop leads to more in-person opportunities to study Bitcoin’s Post-Quantum Problem (PQP).
Finally, thank you to @btctranscripts for hosting the transcripts of every talk and session: btctranscripts.com/quantum-w…


jrakibi retweeted

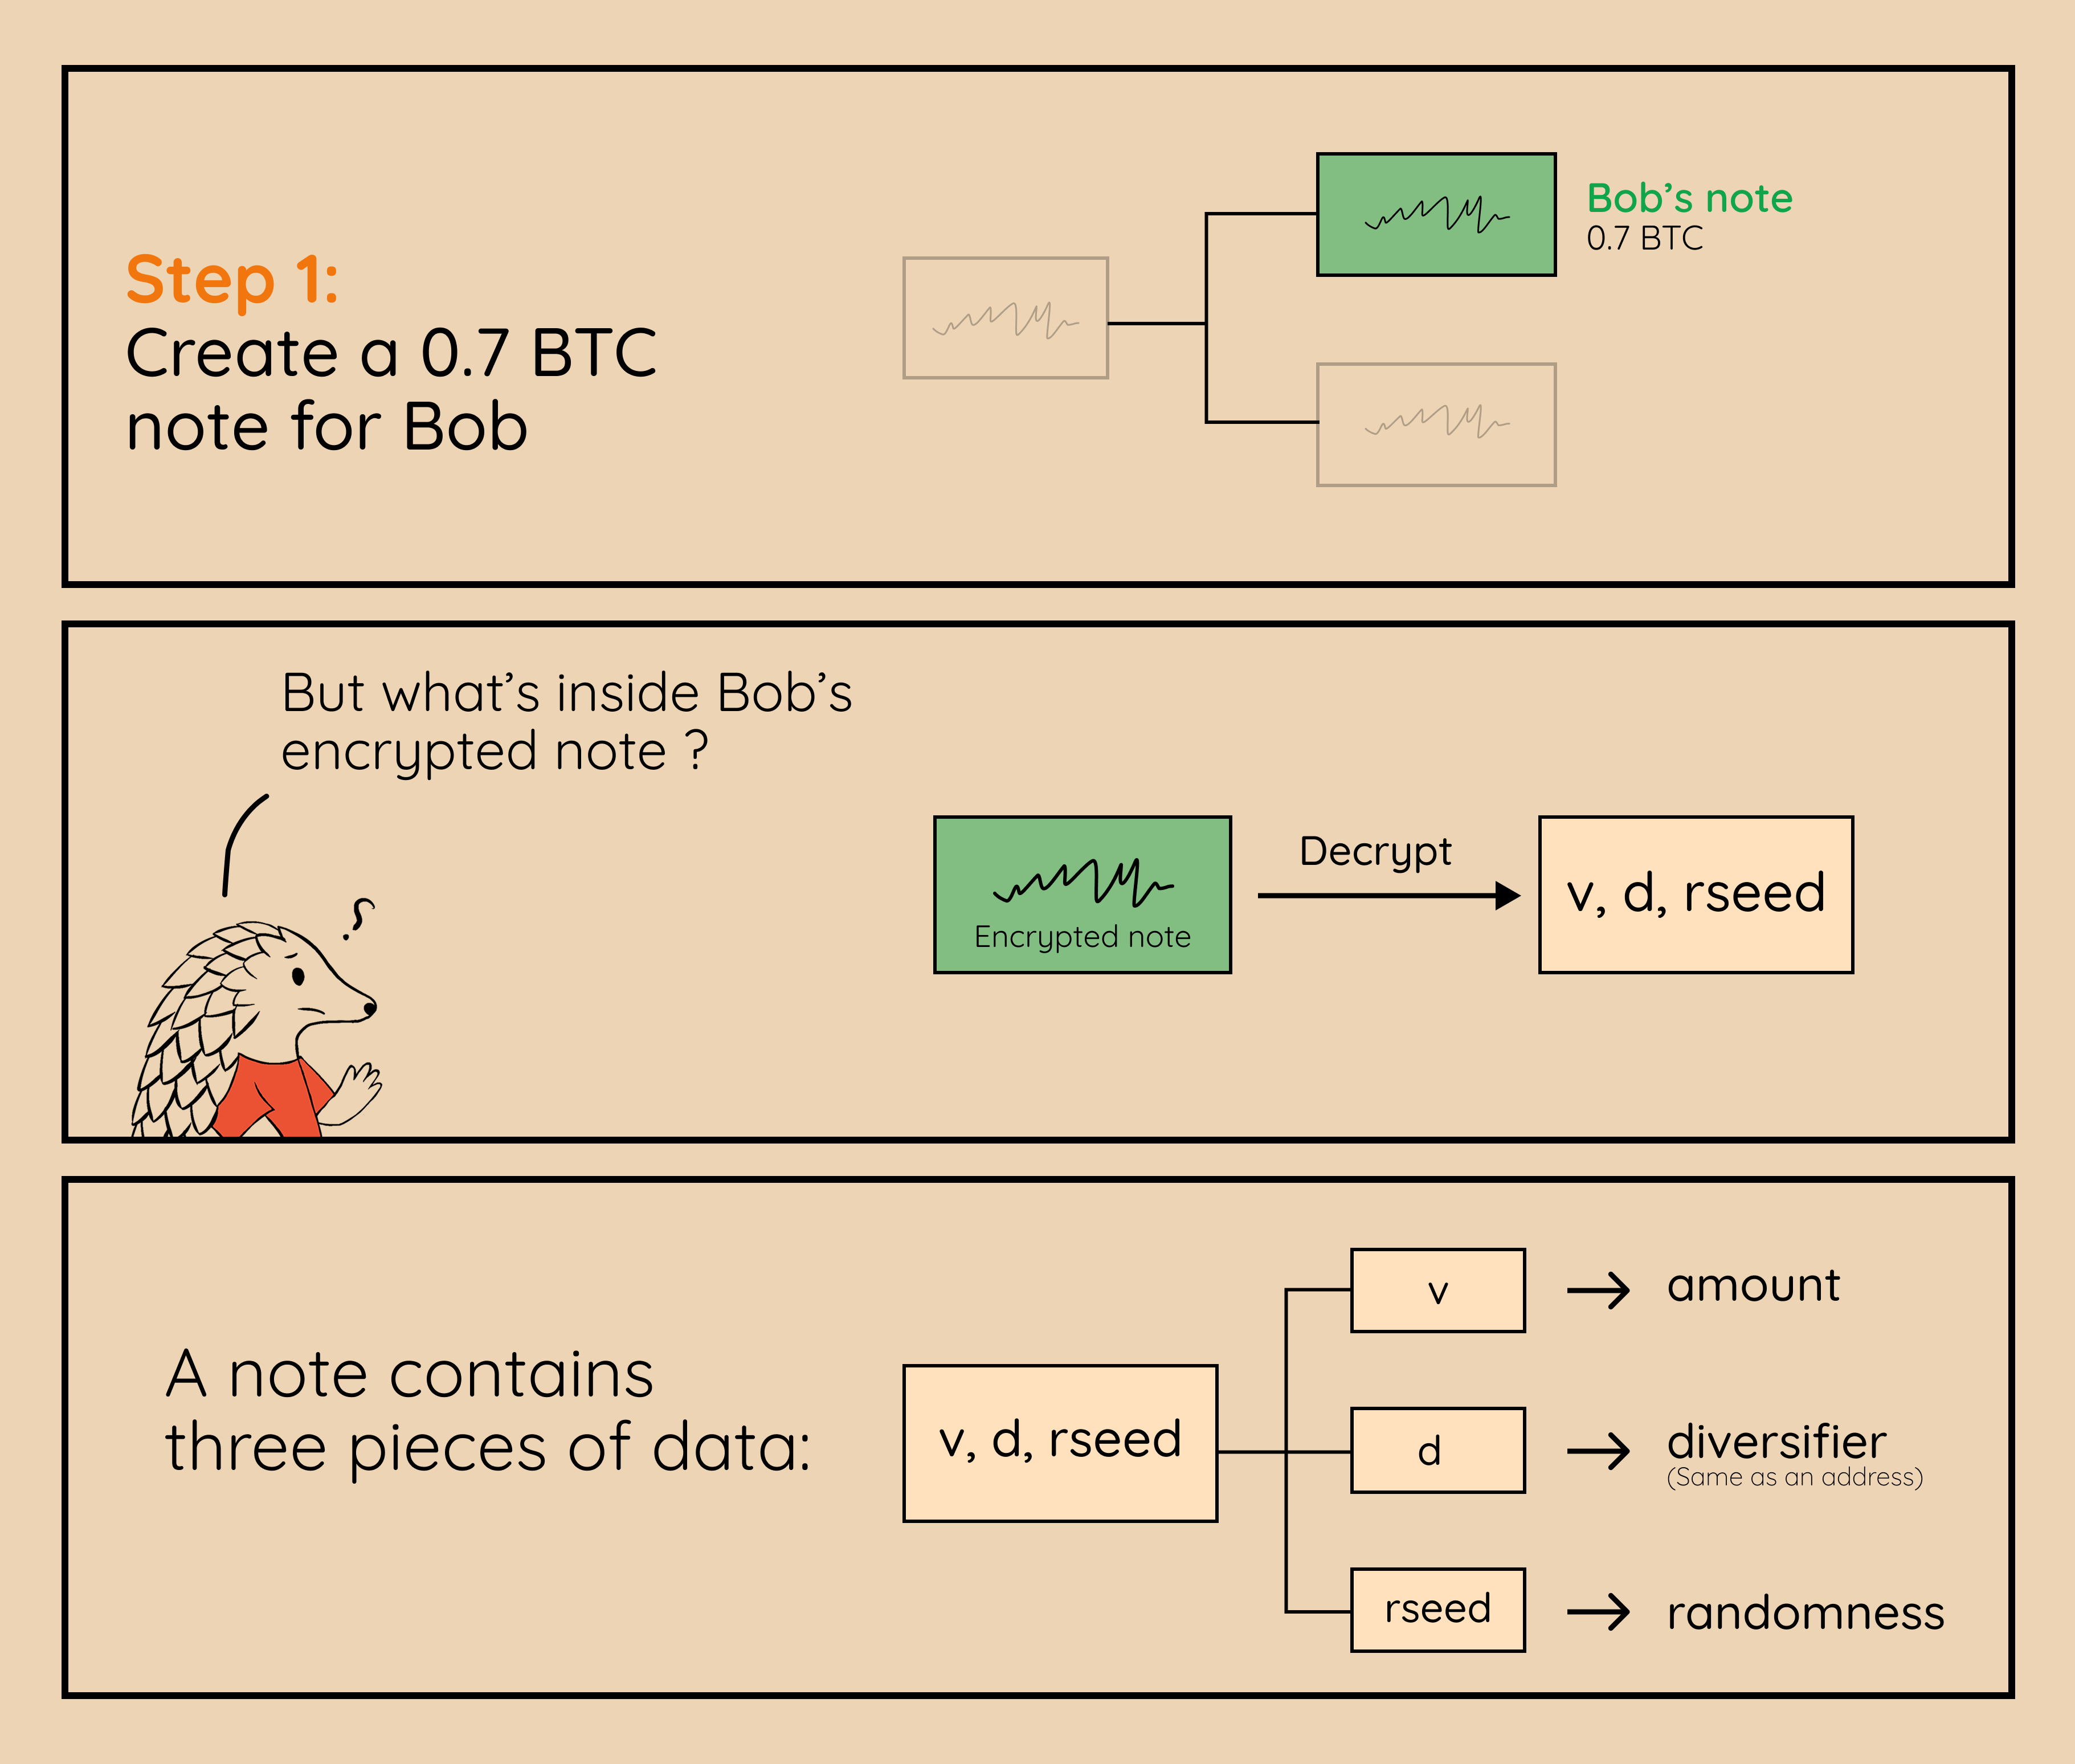
I'm glad to share that our book on zero-knowledge protocols now has a full chapter on post-quantum zero-knowledge proving systems with over 100 pages!
It covers lattice-based Σ-protocols, LaBRADOR, and ZK-STARKs, with all the necessary prerequisites included.
Link below 👇




jrakibi retweeted
A high level overview of how funding works in bitcoin open-source. View article

jrakibi retweeted

There is a critical vulnerability being actively exploited on BTCPay Server, which can result in the loss of funds.
Please update your BTCPayServer to 2.4.2 by going to Admin Dashboard -> Server -> Maintenance -> Update & verify the 2.4.2 version string in the footer.
If you are unable to update right away, turn off your BTCPay Server to prevent unauthorized access until you can update.
jrakibi retweeted

This is stealer code from that threat actor.
pastebin.com/UDxCq74Y
jrakibi retweeted

Jesus, I can confirm it downloads and executes an infostealer writen in python 2800 lines of code that searches for wallet seeds, private keys and passwords, browser cookies, exchange sessions hijack, GitHub, Gitlab tokens, cloud credential files, ssh private keys.

⚠️ This repo gained many stars in 24h. DO NOT RUN IT.
It claims to reproduce the vulnerable COLDCARD RNG, but an LLM-assisted review found a dependency that downloads and executes an infostealer that searches for wallet seeds, private keys and passwords.
github.com/domaup/coldcard-p…
jrakibi retweeted

Diabolical
⚠️ This repo gained many stars in 24h. DO NOT RUN IT.
It claims to reproduce the vulnerable COLDCARD RNG, but an LLM-assisted review found a dependency that downloads and executes an infostealer that searches for wallet seeds, private keys and passwords.
github.com/domaup/coldcard-p…
⚠️ This repo gained many stars in 24h. DO NOT RUN IT.
It claims to reproduce the vulnerable COLDCARD RNG, but an LLM-assisted review found a dependency that downloads and executes an infostealer that searches for wallet seeds, private keys and passwords.
github.com/domaup/coldcard-p…
Another red flag: the GitHub account was created on June 4, 2026, and coldcard-poc was its first repo, created on Aug 4
github.com/domaup
1
5
831