

Christian. Killer Grizz, Threat Intel & Thrunter. Hack things w/ @bsides_nova. @DEFCON Contests Dept Lead & Black Badge DC32. GSE #344. (VIEWS ARE MY OWN).
Boston, MA
Joined June 2017
- Tweets16K
- Following2.8K
- Followers6.6K
- Likes38.3K




Pinned Tweet
Pinning this thread of #CTI tips and lessons learned. I'll add to it at random times.
#threatintel
nitter.cf/klrgrz/status/12860843…

Andy Piazza retweeted

BREAKING: Employers worldwide are pulling back on AI as they navigate a flood of errors and low-quality work that sap employee time, raise privacy and security risks, and drive up costs, per the Guardian.
Andy Piazza retweeted

#BSidesNoVA conference starts tomorrow!
October 30th: Workshops and Happy Hour
October 31st: Talks and Villages
Workshop tickets are available until tomorrow, so get yours ASAP!
Conference Schedule: bsidesnova-2026.sessionize.c…
Tickets: eventbrite.com/e/bsidesnova-…

Andy Piazza retweeted

If you're a threat Intel pro that's been laid off and you want to come to @CYBERWARCON I have a ticket for you. Hit me up.
Andy Piazza retweeted
If you’re headed to #BSidesNOVA this weekend, @Junior_Baines is talking about Chinese implants in the supply chain on 10/31! Jake computers real good, you won’t wanna miss it 🎉
bsidesnova-2026.sessionize.c…


If you’re not a software vendor, you shouldn’t worry about 0days. Have a plan (that’s tested) to rapidly patch / mitigate 0days, but you shouldn’t worry about them. That’s the vendors’ problem. You have enough risk to focus on, don’t borrow trouble that you can’t own.

It might surprise many to find out I essentially never think about 0days, despite my job. The hyper-complexity of environments is a far greater challenge, and also something you can't really explain to someone outside of the profession without a mental model of it. Yes you can just walk up to the prime minister with a shotgun.
I don’t know who needs to hear this: but this is NOT what we meant by calling October Cybersecurity Awareness Month. Can we go back to cookie cutter “guest speaker” all hands and lame corporate memes about security? I’m tired of Hard Mode Awareness Month.



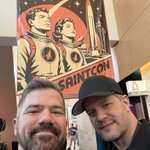
Just a couple of dudes in black tshirts at a hacker conference. @Grifter801 @SAINTCON

Andy Piazza retweeted
Just starting out or trying to switch careers to #cybersecurity?
#BSidesNoVA conference has you covered on Oct 31st with Career Village!
Get your resume reviewed!
Learn how to get started in offensive security!
Conf Schedule bsidesnova-2026.sessionize.c…
Tickets eventbrite.com/e/bsidesnova-…


If you’re around @saintcon this week, say hi!! I’m the hacker in the black shirt with tattoos. Won’t be hard to find at all.
Andy Piazza retweeted
Welcome back @PhiaLLC, returning gold sponsor of #BSidesNoVA!
Learn how phia blends cyber, intelligence and technology expertise with passion and commitment at phiatech.com
BSides Conference Schedule: bsidesnova-2026.sessionize.c…
Tickets: eventbrite.com/e/bsidesnova-…


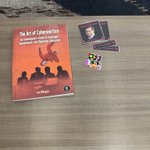
Getting ready to teach my #CTI101 workshop at @SAINTCON today. I had to make sure the students left with some goodies so I brought along the some friends: @_JohnHammond and @Jon__DiMaggio as student handouts is definitely a first 🤣


Andy Piazza retweeted

The way frontier labs have restricted access to cyber capabilities makes no sense. If you're considered a "defender" you're not allowed access to the "offensive" versions of the models (the ones that can do development/validation of malware and exploits).
So for example, if you want to build some sample malware to test a detection system, nope.
Or if there's a major crisis due to a critical vulnerability in PHP and you need to rapidly triage fake exploits to see if there are any real ones floating around so you can warn people, nope.
Want to build a remote code exploit to make sure the detection rules you plan on proposing to the clients actually work? Hard nope.
You gotta call your red team friend and wait for them to do your job for you, because "defender" are only allowed to play in the sandbox with the children.
Not an expert, but I think that the ability to triage in-the-wild exploits during a major crisis affecting 40 million systems is possible maybe important.
And then they want to ban abliterated open weight models, which half of the people are only using because frontier labs will only give them access to lobotomized models.