

Building & securing innovative solutions at the intersection of AI, blockchain, Web3. 🛠️🚀 Security Researcher | Engineer with a passion for cutting-edge tech.
Joined February 2009
- Tweets1.4K
- Following311
- Followers228
- Likes2.6K





Sensitive reports shouldn't go to unverified AI.
Built at NEAR HACKATHON: PrivateTriage checks TEE attestation before disclosure and verifies the model-signed response.
Demo: mickeyjoes.github.io/near-pr…
Code: github.com/mickeyjoes/near-p…
@NEARProtocol #NEARHackathon
66
Built at NEAR HACKATHON: Pursewarden limits AI-agent spending on-chain.
8 concurrent requests. Protected: 5 NEAR. Our deliberately broken control: 17 NEAR.
Demo: pursewarden.com
Code: github.com/mickeyjoes/pursew…
@NEARProtocol #NEARHackathon
69

I received a Competition Bronze Medal in the AI Agent Security - Multi-Step Tool Attacks Competition! #kaggle #bronzemedal - kaggle.com/certification/com…

Reached level 10 on @Hacker0x01 💪
You did it: Level 10! You’ve reached 2,000 points, joined an elite group of hackers in the program, and helped define what excellence looks like. Your current score is 2010!

2
61

🔥

Top 3 researchers this week:
🥇 @Maybach_hunter
🥈 hc
🥉@mickeyjoes
Stay sharp! 🔥
Want your handle here? Join active programs: hackenproof.com/programs

1
62

Mickey J retweeted

5 weeks ago i wrote: "20 reports, 1 paid, one stuck 2 months." said the industry had a payout problem and went silent. spent every night in vendor code, chasing bugs nobody else did. today: 7 paid, #1 hacker of the week on @hackenproof as @redvision (me). we fucking earned this.


That's right!
The best Critical vulnerability is the one found before anyone can exploit it.
In August alone, HackenProof researchers had 259 Critical vulnerabilities paid out.
That’s a sharp increase from the previous two months – bringing the total to 326 Critical vulnerabilities identified throughout the summer.
Across HackenProof programs, researchers uncover critical security risks before they can impact users and businesses.
Secure Your Product with HackenProof→ hackenproof.com/contacts

37
Apparently I’ve burned through 66.5 BILLION tokens across ChatGPT + Codex 🤯😂
Just found the profile page and had absolutely no clue.
Codex has definitely been putting in some hours. 😅
Anyone got me beat?

1
59
Mickey J retweeted
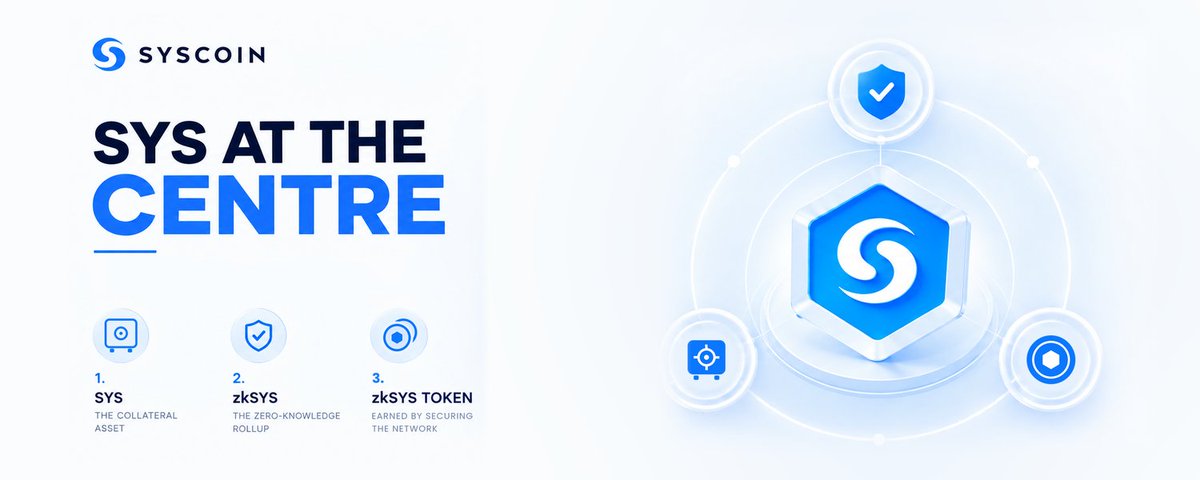
Quantum computers could eventually break the digital signatures most blockchains use today. Syscoin is already designing around that risk.
Think of every Sentry Node having its own quantum-safe digital stamp. Before the network accepts something, it would collect 801 stamps from several independent groups of nodes.
That full proof is only about 3.6MB, roughly the size of a photo, and can be checked in parallel in around 1 millisecond.
Syscoin’s 2.5-minute blocks, Bitcoin merge-mining and finality every five blocks give the network enough room to handle these larger, safer proofs. The same hash-based technology can also support the data layer behind zkSYS.
In simple terms: thousands of independent nodes can prove they agree without relying on one shared key, while staying secure against future quantum computers.
Most blockchains may need to bolt this on later. Syscoin is designing for it now.

Working on SLH DSA based sentry nodes. Removing the DKG and MPC replacing it with direct signatures, and a 3.6mb commitment of 801 signatures which validate in 1ms (parallel). A global key will replace the BLS owner key with a FIPS 205 SLH-DSA-128s (7856 bytes). At around 3k SNs this is less than 24mb. A merklized tree of subkeys are created under C11 (SPHINCS-) which is 3976 bytes and 2^14 signature budget. Much faster to sign, and gives the 3.6mb commitment with 801sigs. Why 801? Because you have 4 quorums of 400 nodes, while each quorum you want 267/400 safety (33% liveness), distributed over 4 quorums and 3 out of 4 need to sign. 267*3=801. This will only work on @syscoin because it is purposefully slow at 2.5m block times, auxpow with @bitcoin and we finalize every 5 blocks. This gives adequate buffer for the bandwidth overhead. The DA layer is also hash based (keccak or blake2s), which feeds zkSYS (zkVM layer) for speed and convenience. Lastly once we figure out which direction BTC is going (likely shrimp/shrinc/sphincs), we can complete utxo PQ, once EOAs on eth figure out which way (hopefully hash based), we will finish EVM PQ. The reason we need the safe large sigs is because we reuse addresses with sentry nodes across validator usages, and although hash based snarks are becoming viable, they still open new games and attacks and I prefer safety first with 128+ bit PQ security at minimum.
Mickey J retweeted

We did it, finally... Codex & ChatGPT desktop, now on Linux.
Thanks for waiting and you can cancel that MacBook order if you got impatient. It’s that good.
👀
Moved to @HackenProof leaderboard rank #55 🚀
hackenproof.com/hackers/mick…

2
113
Mickey J retweeted
More opensource goodness. We have just released a CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities in your code. Scan repositories, review changes, track findings over time, and run security checks in CI.
github.com/openai/codex-secu…


