

Helping You Secure AI Apps and Infrastructure · Ambassador @SpaceXAI · BJJ 🟪
APAC
Joined April 2021
- Tweets9.2K
- Following977
- Followers2.3K
- Likes7.2K





Keith Vaughan retweeted

tldr: when it comes to cyber defense, there are things you can control, and things you cannot.

being able to communicate ideas is becoming far more high value than it ever has been, especially with ai slop drowning the internet.
it's feels like a muscle - i've been writing for years on socials but never really talking on video outside of random tv appearances, sitting down talking to a camera in an empty room feels way more awkward than that.
here's my brain dump on cyber & ai in response to the whole php apocalypse we just went through (and are probably still experiencing)
in this video i cover:
- why cyber is like chess with infinite pieces, and why defenders start at a disadvantage
- why most of the php conversation focused on patching, and what got missed
- practical layers you could have put in place before any patch existed: hiding server banners, waf rules, web server controls, restricting access to trusted clients, php directive changes
- why memory corruption exploits almost always leave logs, and how to watch for them
- assuming breach and running endpoint detection on your internet-facing servers
- checking whether someone got in before you patched
(need to practice talking faster - set playback to 1.25x for better experience)

Keith Vaughan retweeted

Agentic money laundering

Our investigators are observing never-seen-before laundering patterns with the stolen funds from the Binance exploit. Thousands of transactions in a short period suggest that the attackers are using automation to obscure the trail of funds. Rather than simply moving funds onward, they repeatedly circulate them among addresses, often sending funds back to addresses involved earlier in the sequence.
Read more: chainalysis.com/blog/binance…

Everyone is talking about the using abliterated models.
Using them scan their own systems for security vulnerabilities, but we also need to start thinking about where that LLM runs. What's being logged and who is behind that API.
Near Protocol released something today which is interesting.
But add the potential for harm of OpenRouter or similar being compromised and the world is looking pretty fierce.

Hey everyone, just double check.

Cursor users: check your Claude Code extension.
Cursor confirms a trojanized Anthropic.claude-code v2.1.313 in its extension marketplace on 29 October, 09:27 to 20:35 UTC. It estimates up to 5,000 affected users and identifies macOS ARM64 and Windows x64 builds.
Loading the extension executes malicious code that collects host information and attempts to install a persistent SSH backdoor.
Cursor says SSH access would fail on most hosts due to bugs and insufficient privileges. That limits remote access; it doesn’t undo malicious code execution. Credentials and repositories accessible to that account are potentially at risk.
The package has been removed and the C2 taken offline. Uninstalling the extension may still leave persistence behind.
If this version ran, investigate the host, remove persistence and rotate accessible credentials from a clean system. Updating the extension alone doesn’t prove the machine is clean.
The vendor-confirmed distribution channel is Cursor’s marketplace. Microsoft VS Code uses a separate store. These reports don’t establish a compromised Microsoft Marketplace or malicious npm release.
My recommendation: turn off automatic extension updates completely - for yourself and for your developers. With supply chain attacks like this, I don’t think the benefit of another feature or a minor UI fix justifies automatically accepting every new release onto developer machines.
Update manually when something stops working, when a bug is actually getting in your way, or when a relevant security fix needs to be applied. Otherwise, leave a working extension alone.
Cursor advisory and cleanup instructions:
cursor.com/blog/claude-code-…
Technical analysis:
opensourcemalware.com/blog/t…


show version | include vibecode

This is INSANE. Cisco’s president Jeetu Patel has given a 27-year-old engineer unlimited AI tokens to try to rewrite 98% of the company’s legacy code within 24 months, Fortune reports.
Padmanabhan Krishnamurthy thinks he can do it with a two-person team. He has just four weeks to prove the approach.


Keith Vaughan retweeted
New Date: Saturday 31st Oct // Ho Chi Minh City 🥥
Workshop focussed on adapting the strategies and frameworks used by enterprise FDE teams and applying them to helping small to medium business deploy AI.
10-12am @ HOFF Specialty, Vo Thi Sau
🤖 Made with AI


Why am I making brainrot in IG?
Because I need to find winning content I can push with ad spend.
Learn the algorithm will help me know which content I can ramp with ads.

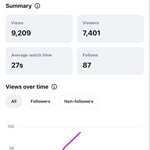
Week two of the instagram experiment.
Finally blew above 100 followers and had a video approach 10k.
The video felt too simple, but I guess that’s the signal.
#AISecurity

Keith Vaughan retweeted
nothing is safe.
binance hack = $5.7B lost 😳

fuuuuuuck
coindesk.com/business/2026/1…
Binance loses $5.7 billion in largest crypto hack to date

Week two of the instagram experiment.
Finally blew above 100 followers and had a video approach 10k.
The video felt too simple, but I guess that’s the signal.
#AISecurity
Here at sumosign.app we are ready for this future. Agents will buy and spend. On their own and for their human. And at times they will contract and deal with humans autonomously.


Guy go check this out, never liked Discord

Never have a heavy suitcase.

The biggest mistake tourists make in Japan is dragging a fifty-pound suitcase up and down subway stairs.
Watch how Japanese travelers board the bullet train. They walk on with a cup of green tea, a small shoulder bag, and both hands free.
Where is their luggage? It is already in the next city, waiting for them.
In Japan, the system is called Takkyubin, recognizable everywhere by a logo of a mother black cat carrying her kitten gently in her mouth.
When you check out of your hotel in Tokyo at eight in the morning, you hand your heavy suitcase to the front desk, fill out a tiny slip, and pay about twenty dollars. You can even send it straight from the corner convenience store.
Then you spend the entire day wandering through mountain temples or eating street food with nothing on your back.
When you walk into your traditional inn in Kyoto that evening, your suitcase is already standing neatly in your room, wiped clean, with the handle turned toward you.
In fifty years of handling millions of bags a year, lost luggage is virtually unheard of.
A society runs smoothly when you can hand your belongings to a stranger at a convenience store and know they will beat you to your hotel.


Wow Palo Alto watch out!

Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

🙈

While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected.
Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions.
Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent.
But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models?
We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem.
Read the full report: cohere.com/blog/concerning-b…
