

The TruffleHog company We find credentials, with open source https://nitter.cf/t.co/7CnEqo1inq https://nitter.cf/t.co/8vZxthRRXX
Joined January 2019
- Tweets491
- Following1
- Followers5.1K
- Likes278





🔍 Search your Slack for “AKIA”.
Your AWS keys live in a vault with rotation, policy, and an audit trail. The copy pasted into a thread during an 11pm build fix has none of that. It works just as well. 🔑
Deleting the message isn’t revoking the secret.
👉 trufflesecurity.com/blog/the…

Truffle Security is collaborating with Google Cloud to make exposed secrets easier to act on.
TruffleHog Enterprise finds and verifies them. GCP Analyze maps the identity, permissions, and resources behind them, then re-verifies after rotation.
trufflesecurity.com/blog/tru…

There's going to be a lot more secrets revoked in the coming months.

🚨 New investigation: Socket found malicious LiteLLM workflows running 11 days before the attack, targeting 20 secrets including GitHub, cloud, and AI credentials.
After our disclosure, LiteLLM linked a stolen token to approval of the malicious release.
socket.dev/blog/litellm-atta…

A stolen AI API key can pay for more than free inference.
Attackers can query a teacher model, save its responses, and use that data to train a smaller student model. Your credential becomes part of their model-building pipeline. 🔑🤖
trufflesecurity.com/blog/mod…

🧩 A supply chain attack doesn’t need a malicious dependency.
In the Trivy incident, compromised credentials let attackers publish malicious releases and manipulate GitHub Actions tags. 🔑
Finding the token is step one. Verify that the access is actually gone.
trufflesecurity.com/blog/the…

Told you scanning GitHub alone wasn't enough. 🤷
Turns out, there's surprisingly little overlap between the secrets we find across different sources. Here's what our data shows 👇
Any of the numbers surprise you?

Think scanning GitHub alone is good enough?
Our research team scans nearly 2 petabytes of data every month across repositories, packages, apps, container images, and more. Because secrets don't just live in your GitHub repo. And if you're only looking there, you might be missing what's shipping in your final product 😶🌫️

🧊 AWS quarantine isn’t revocation.
We found 929 leaked AWS keys carrying AWS’s compromised-key quarantine policy. Some were flagged 3+ years ago. Every one still authenticated.
Quarantine limits permissions. Revoke and verify.
trufflesecurity.com/blog/aws…
#AWS #CloudSecurity

🪣 S3 buckets hold a lot more than secrets.
TruffleHog Enterprise can now scope scans by object-key prefix and extension before download.
🔐 The October release also adds OAuth2 auth for custom verification and more reliable Jira and Confluence scans.
Read: trufflesecurity.com/blog/foc…

Deleted the secret from your repo? Cool. Your coding tool might still have a copy.
We found 2,148 distinct secrets in Claude files and 603 in Replit files. They showed up in settings, saved conversations, and worktrees.
Deleting it from source is only part of the cleanup.

Cleanup on aisle commit. Before your next commit, check these files for secrets 👇
.claude/settings.local.json
.claude/settings.json
.codex/auth.json
.cursor/mcp.json
.vscode/mcp.json
.vscode/settings.json
.vscode/cline_mcp_settings.json
.idea/dataSources.xml
.idea/copilotDiffState.xml
.idea/CopilotChatHistory.xml
opencode.json
opencode.jsonc
.replit
For saved states:
.codex/shell_snapshots/.sh
.vscode-server/data/logs//ahp/*.jsonl
A short-lived key is only safer if the replacement stays secret.
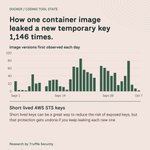
From Sept. 1 to Oct. 7, one container image leaked a newly issued AWS STS key 1,146 times 🫠
This is the first in a series on how coding tool state can turn credential rotation into repeated exposure.

🧪 An AI agent didn’t need a zero-day to enter two companies’ systems. In a cyber eval, Gemini found leaked credentials in public repositories and used them to log in.
🛑 It stopped after recognizing the targets were real. The failure mode wasn’t new.
trufflesecurity.com/blog/lea…

🔑 A credential can be governed when issued and unmanaged the moment it’s copied.
The original sits in a vault. The copy survives in Git history, Slack, a CI artifact or an agent config.
Downstream systems trust both.
Read the blog: trufflesecurity.com/blog/one…
🤖 Made with AI

🎥 We’ll go deeper in our upcoming webinar with Matt Brady: event.on24.com/wcc/r/5443805…
Finding a leaked credential doesn’t remove its access. 🔑
We found 543,699 live credentials across 224M public GitHub repos used in AI training. The median had been exposed for 2+ years.
After remediation, retest the credential to confirm the access is gone. ✅
trufflesecurity.com/blog/why…
🤖 Made with AI

We scanned 224M public GitHub repos used to train AI models and found:
🔑 543,699 credentials still live when tested
⏱️ Half exposed for 2+ years
😬 The oldest had been public since 2009
Finding leaked credentials isn’t the hard part. Revoking them is.
trufflesecurity.com/blog/git…

👀

Cyber is having a moment
Across 21 major software companies, including Apple, AWS, Microsoft, and Google:
- Reported critical vulnerabilities never cleared 100 per month in four years
- Since spring they've jumped to over 600 per month
Charts of the Week: a16z.news/p/chart-of-the-wee…

AI worms don’t need superintelligence. 🪱
The pieces already exist: hacking, propagation, and full model-stack replication have all worked in controlled experiments. 🧪
Dylan Ayrey predicts operational AI worms could arrive within 6–12 months. ⏳
trufflesecurity.com/blog/ai-…
