

Senior FDE at Microsoft. @Arsenal fan Tweets, or Xeets are mine
Melbourne, Victoria
Joined October 2010
- Tweets15.2K
- Following703
- Followers1.4K
- Likes19.6K



Will Velida 🇺🇦 retweeted

"It's crazy how there's so many major hacks all of a sudden"
- people who started paying attention to cybersecurity 3 weeks ago.
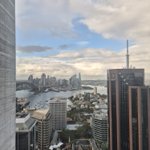
Summer in Melbourne is just around the corner. Few more weeks of the wintery, springy, autumn weather we usually get.

Experimenting with using git worktrees with parallel coding agents in @github Copilot app. I've had success with tmux and Orca in the past, so this should be interesting.


Will Velida 🇺🇦 retweeted

I find the discourse around Microsoft offering a buyout to 60k employees and the whole "Day in the life of a SWE at Microsoft" videos.
Ya'll saying some silly stuff like "these people don't do anything but waste time, eat food and get in the way of real employees"
My brother in christ, you're in the middle of the work day, on X dot com the everything app shit talking other people not being productive. Get a grip on your own reality.
Will Velida 🇺🇦 retweeted

We'd like to invite you to try out #squad 2.0 preview. we don't have in all the package managers yet, but, if you're keen to try it out you can download the installers from our release page here: github.com/bradygaster/squad…


Just arrived at API Days Melbourne. I'll be talking about applying the @owasp Top 10 for Agents at 4:50 in Room 103. If you care about agentic security, make sure you attend my talk!

We're seeing more cases of bad actors using open source pen test software and agents to attack systems at machine speed. While we should take this seriously, there are cases despite using agents, they still aren't successful. Is vibe-hacking a thing now? norforge.com/blog/inside_cai…

Will Velida 🇺🇦 retweeted

Offense and defense now share the same intern, and it has no loyalty to either side.

There are so many challenges when it comes to security in multi-agentic architectures. Super interesting area right now.


New edition of Last Week in Agent Security! It wasn't just PHP causing headaches. We also had agents using Cairn and ARTEX causing havoc, hackers hunting for LLM endpoints, MCP servers, and AI Gateways, and more LiteLLM, OpenCode and Meta problems: willvelida.com/posts/last-we…

Will Velida 🇺🇦 retweeted

A poisoned invoice reaches one agent. Its output feeds another. Soon the failure has spread across the workflow. @WillVelida explains cascading failures in agentic systems on RunAs Radio. runasradio.com/Shows/Show/10…

Will Velida 🇺🇦 retweeted

🚨 PHP2Shell attackers accessed MFA secrets and password hashes at a European government entity in just 2 hours.
That's not all.
→ Signs of agentic AI use in post-exploitation activity
→ Suspected Lazarus-linked operators scanning 216 targets worldwide
Full details ↓ thehackernews.com/2026/10/ph…

Critical RCE flaw in OpenCode that affects users on Windows and WSL that allows attacker-controlled remote MCP servers to execute code during MCP auth. Anomaly say that since user-configured MCPs are outside their trust boundary, no CVE has been published: thehackernews.com/2026/10/op…

Will Velida 🇺🇦 retweeted
excited to be speaking at #ndcporto next month! i’ll be showing all the latest goodness we’re shipping in #squad 2.0!
ndcporto.com/agenda/from-cod…

Will Velida 🇺🇦 retweeted
🚨 LiteLLM reveals the root cause of its supply chain attack.
A master key leaked on GitHub in May was never revoked, allowing attackers to access its Agent Platform, steal a GitHub owner token, and publish a malicious PyPI release in October.
Read: thehackernews.com/2026/10/le…

Will Velida 🇺🇦 retweeted

"Sorry we didn't get back to you yet, we've been too busy on Twitter and trying to keep our investors happy"
Unbelievable statement from eMudhra!
bugzilla.mozilla.org/show_bu…
